I click “accept the cookies” almost every time. I just personally don’t feel it’s worth the effort and cost to try to avoid it.
What “dark pattern cookie trick” are you worried about? I just can’t come up with a scenario where it will actually harm me in any way. All the examples I have heard are either completely implausible, don’t actually seem that bad to me, or are things that are trivially easy to do even without any cookies.
Now, I am not going around giving my real email out to random sites, though, although even that doesn’t strike me as particularly dangerous. I already get infinite spam, and I am sure there are millions of other ways to get my email address… it is supposed to be something you give out, after all.
I just don’t think it is something that is worth stressing out about and fighting against. Maybe I am actually naive, but I just have not yet been convinced I should actually care.
the effort and cost to download an ad-blocker that automatically removes the prompt to accept/deny entirely is practically zero and the amount of clicks you'd save yourself would quickly exceed the clicks it took to install the blocker.
> I just don’t think it is something that is worth stressing out about and fighting against. Maybe I am actually naive
It seems like you are, but that's just how our brains work. We're very bad at judging long term and abstract risks, especially when the consequences and their connection to the cause are intentionally kept unclear. For example, when people's cars started collecting data on their driving habits and selling that data to insurance companies a lot of people saw their insurance rates go up, but none of the insurance companies said that it was because of the data collected from their cars. I'd be willing to bet the data being collected by tracking your browsing history has already been screwing you over in various aspects of your life, online and offline, but you won't be told when it happens or why.
Ok, can you give me a plausible example of what that harm could be? This seems in line with the exact thing I said in my comment; every time I ask how it could harm me, I am given vague statements about tracking and data. Charging me more if they think I can afford it is surely a thing to worry about, but there are so many ways to do that without tracking that I already need to take actions to defend against that (comparison shopping, price history tools, etc).
I am not saying I don’t think companies can take data they have access to and use it to extract more value from me… I am saying I don’t thing opting out of cookies is going to do much to change that, for better or worse.
There are countless ways the data collected about you can be used against you. Companies are using this data for everything from setting prices, to deciding which policies they'll apply to you, what services they'll offer or deny you, even shit as trivial as deciding how long they should leave you on hold when you call them on the phone. It's been used to deny people housing, or employment. It's even resulted in innocent people being arrested and investigated by law enforcement. This guy (https://www.nbcnews.com/news/us-news/google-tracked-his-bike...) wasn't worried about Google tracking everywhere he went until he had to get his parents to clean out their savings to pay for a lawyer in order to prove his innocence.
AI is only going to make it easier for companies to leverage the massive amounts of data they've collected against us. Companies have been trying to get consumers to accept discriminatory pricing practices this data enables for a very long time (https://link.springer.com/article/10.1057/s41272-019-00224-3) and it looks like they're starting to wear us down. Digital price tags are becoming increasingly common. So are demands that consumers scan QR codes to get prices. Prices don't have to be set so high that they become unaffordable to you, they can just slowly eat away at more and more of your earnings.
The system is set up so that you will never know when or how the data being collected about you is used against you, but every company is looking to leverage that data to their advantage every chance they get. I get that it's easy to feel defeated and think "My ISP already sells my browsing history, Google chrome already collects all by browsing history, so who cares if I let 30 other random companies collect it too by accepting their tracking cookies on every website I visit?" but those companies collecting your data care very much and it's not because they have your best interests in mind. They aren't going through all the trouble to track you across every website you visit because it doesn't matter. Taking a few basic steps to help protect yourself is just the smart thing to do, especially when it's something as simple as using an ad blocker or an add-on to auto-reject the countless "Can we track you" requests.
Maybe not, but does that matter when they use an advertising profile to make your life hell before determining you're not in the problem group? Will they even bother to check? They already have been hassling and detaining citizens on similar sloppy suspicions around immigration.
Even if you're a perfect aryan and think you're safe from the current regime... will the next one have the same notion of perfect?
For less-often used, e.g., non-English language sites, these often leave a site in an unusable state, e.g., non-scrollable. I often have to go into the developer tools to fix a site manually, sometimes hunting for the element to fix if it's not body or html.
It's only zero if you don't need to interact with sites that break when you're running an adblocker. I run an ad-blocker nearly continuously, but there are all sorts of sites where I have to disable it in order to use the actual functionality of the site (and these are frequently sites I _have_ to interact with).
Conspiracy theories are gossip for men.
The data collected about us online is extensively used against us both online and offline. The multi-billion dollar industry around collecting and selling every scrap of data about you and your personal life didn't spring up because nobody was making money from it.
To your point about the actual harm, I've come to see it as a kind of ecological problem. Wasting energy and sending more trash to a landfill doesn't harm me individually, at least not immediately. But it does harm in aggregate, and it is probably directly related to other general harms, like overall health outcomes, efficiency, energy costs, etc.
No, accepting cookies by itself may not do much to me, but the broader surveillance and attention economy that relies on such apathy certainly has.
In theory, the government doesn't need the ad exchanges which have very lossy information. They have access to the ISPs and cell service providers, etc, with a warrant. Dictatorships like China and Russia don't need ad network data to be police states, they just use the core phone, internet and computer data.
But in this case, the US gov are using the insecure private data as a run-around to the warrant process. This is definitely unfortunate, and I think laws should be amended to prevent this workaround.
On the contrary, the ads become worse, since they become better at trying to get me to buy some crap I don't need.
The more irrelevant to my profile they are, the better.
> It basically just powers product discovery in a giant global marketplace.
That is also incomplete. See how profiling led to ICE finding people - and ICE has a proven track record of executing US citizens. That is also a fact. It does not mean profiling led to the death of the people here, 1:1, but it meant that it is a contributing factor to the build-up of government troops killing people (which is very similar of Europe 1930s by the way).
https://www.transportforireland.ie/getting-around/by-taxi/dr...
---
Additionally, in plenty of European Countries, it's pretty common to write your name on your address: https://c8.alamy.com/comp/B01RP4/personal-name-plates-at-blo...
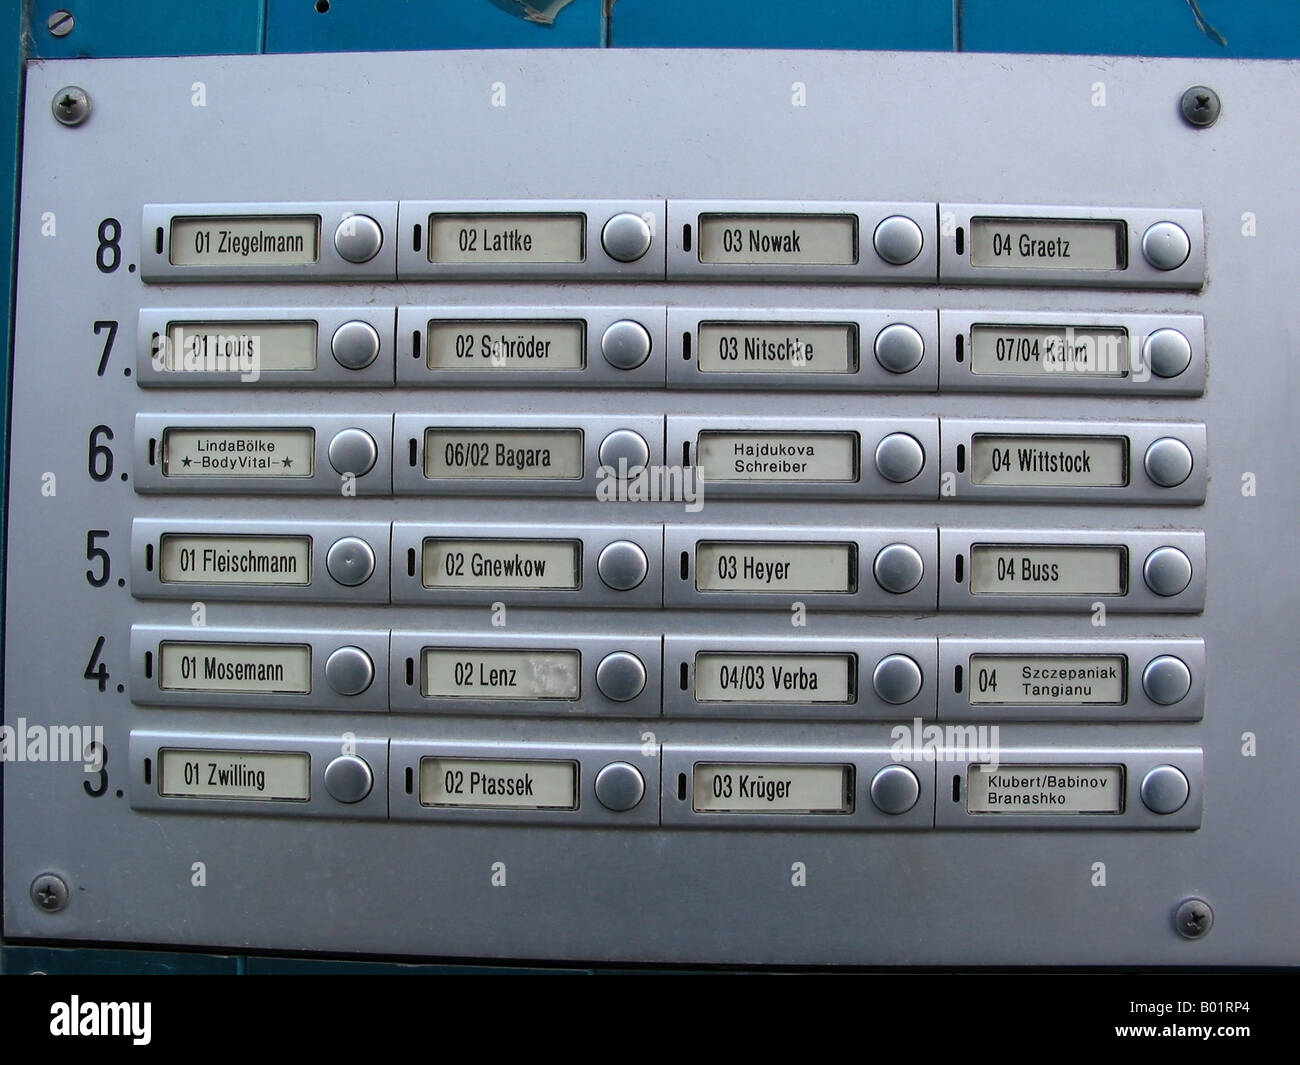
Writing it down would give more information to everyone else at all times.
What about video games? They only have utility in pleasure and the sedentary lifestyle associated with over-playing them is extremely harmful.
Sounds to me like you have some random things you decided you don't like and want to ban ads for them, not that you've done any thinking about utility (other than as a bad attempt at rationalizing your anti-some things campaign).
I thought this was just ignorance.
Then I checked the profile. They ”have lots of experience with digital advertising “
“It is difficult to get a man to understand something, when his salary depends on his not understanding it”
Why should I give up my data to any private entity?
If their business model depends on ads, then I say it should die.
People already pay for things like Kagi to try to get out from under the mountains of SEO adspam. I have to pay in time and aggravation to stay sane in the face of ever escalating tactics to shove ads in my face and manipulate my online behavior. So I don't think a smaller web would be a bad thing.
But I don't see that as likely to happen anyway; companies have found out that advertising and data harvesting is far more profitable, and governments have found the same to be very useful for exercising control.
I, as an individual, am not going to have any effect on a business if I opt out or not. No business decision is going to be made because I opt out.
You might argue that it will matter if enough of us do it. Sure, that is true... but again, it won't matter if I do it or not. If N number of people opting out is enough to ruin the business model, then N-1 is surely enough as well. There is a 0% chance that I am the one who finally causes the system to collapse.
I do use an ad blocker, and never click on ads. I feel like that action has a bigger return on investment than no clicking the cookie banner.
If having more information about me allows the website to charge more to show me an ad, and I never click any ads, then I am hopefully helping decrease the return advertisers get by using personal information.
It may be you don't believe in democracy at all, and that's fair, but consumer action is the only way you can affect business decisions, by joining the decision-cohort you agree with more. Joining the opposite cohort because it's less work represents that you're okay with things continuing in that direction.
That said, I agree with the work it takes to navigate cookie banners being excessive (hence dark pattern), which is why my default browser config = ublock + consent-o-matic [1]
> It may be you don't believe in democracy at all, and that's fair, but consumer action is the only way you can affect business decisions, by joining the decision-cohort you agree with more. Joining the opposite cohort because it's less work represents that you're okay with things continuing in that direction.
I actually believe even less in 'voting with your wallet' than in actual voting, for all the same reasons except the cost of 'voting' in this case is even higher (choosing an individually suboptimal option with my wallet hurts me directly even more than the cost of voting in an election does... e.g. choosing to pay more to avoid major corporations costs me every time I shop) I personally think the only way to avoid companies destroying the common good for profit is to price in the destruction to make it explicit (e.g. carbon taxes, pollution taxes, etc).
If I ever decide that it is no longer worth voting then I will probably leave the country under the expectation that other people like me giving up on voting are doing it for roughly the same reasons.
About voting with your wallet, I agree that it'd be best if companies actually had to pay for those externalities you mentioned. If you have spare money to spend, you can view not choosing the cheapest option as supporting or donating. That's what I sometimes do when e.g. buying locally instead of ordering from somewhere far for cheaper. I can get local faster and it's more convenient, so there's lazyness, but thinking about it as supporting helps me rationalize it further (and it is true). I don't think it really hurts me more than buying something else that I don't strictly need. I see indirect value in trying to uphold things I like.
Cooperation to the detriment of the individual in the animal world is exactly the same phenomenon in a much simpler system. That is widely and repeatedly evolved so we know for a fact that the game theory works out in a vacuum (ie without human cultural factors).
Any high trust cultural behavior is similar.
- Biology gives us the instinct to cooperate and the capacity for empathy.
- Capitalism provides the mechanism to scale that cooperation to millions of strangers.
- Institutions (laws/culture) provide the rules that prevent the "vacuum" from devolving into a state where the strongest exploit the weakest (which is actually what happens in nature when policing fails).
Therefore, in a capitalistic society, cooperation to the detriment of the individual (e.g., paying taxes, following labor safety rules) is not just a biological imperative; it is a social contract enforced by culture to allow the complex system to function. Without the cultural layer, the biological layer alone is insufficient to sustain a modern economy.
I do not think this should be analysed from the perspective of an individual but from the perspective of being part of a collective.
Individually we are pathetic naked monkeys, collectively we are mighty
That may be true, particularly in the short term, but you might be hurting everyone else including yourself in the long term. Opening your wallet sends a signal to the receiving business to keep doing what they're doing, even if we all know it's bad.
There's also a cultural aspect to consider. It's normalized to not think of anything other than cost. That's why we have CAFOs, toxic plastic children's toys, landfills full of junk, etc... Pricing in the destruction might help, but at some point our culture needs to change. Outside of the occasional voting, we're all pretty powerless to enact top-down change like taxes and regulations, but we can all build culture.
That is exactly my point, though. The signal from my personal transactions isn't going to be enough to change anything. It will be drowned out by everyone else.
Of course, you are right that if enough people closed their wallet, then the business would have to change. However, that is STILL true even if I keep my wallet open. If N people stopping their shopping at a store would cause it to close/change its practices, then surely N-1 people stopping their shopping would also cause it to change. I could still keep shopping their, get the benefits while they last, and then switch once it finally goes out of business.
Of course, you might reasonably say, "Well, if everyone thought like you, then the change would never happen!" True, but my decision does not change anyone else's decision. The other people won't even know my choice, it isn't going to make other people boycott.
You could argue that people will listen to what I say, and I could influence them. That is true, but that is again independent of whether I actually 'vote with my wallet' or not. The influence I have on other people is the same whether I tell them not to shop there and I also don't shop there, or if I tell them not to shop there but secretly shop there myself.
Obviously there is some other morality at play here, but it isn't as simple as invoking the direct signal I am sending by choosing to shop somewhere or not.
Is it effective? Probably not in the short term, at least for the intended purposes, but secondary effects like personal growth, satisfaction, and social dynamics might be realized.
And I think this is great. Often our convictions aren't, and those are what make us interesting! I also think it's interesting how/why we rationalize our irrational behaviors! For example, I generally feel the same way as you about voting, but I don't like living as (in my mind, at least) a defeatist. Also, I feel that if I didn't vote then I have no right to complain or have an opinion about the things I didn't vote on. So I go vote for those reasons.
But it isn't because my individual vote actually matters.
If you only pay attention to national elections sure. Tons of local and state elections come down to a couple hundred votes all the time.
I guess if your position really is votes don't count unless its the one to tip the scale no one would be debating you because its irrelevant. Maybe lead with that.
> Your argument is basically well voting doesn't matter so we should have a dictatorship instead of democracy
I am actually not saying that at all, which is what makes this a paradox. I think democracy is important and that getting an accurate determination of the will of the people is important... but it still doesn't make sense, from a pure game theory perspective, to vote in an election.
It isn't REALLY a paradox, because both things are true - voting is a good way to get a representative sample, and a single vote isn't going to change that sample very much.
In many ways, this is just basic statistics, and we experience this every single election night - elections are called WELL in advance of every single vote being counted, because we already know with statistics what the result will be. Now, there are a few examples of this going wrong, but those are mostly times where the rush to call an election makes people call it when the statistics say there is still a reasonable chance for a comeback.
Honestly, it if was up to me, elections should be determined by a random sample. Randomly select N citizens from the country to be the voters that year, and use that result. If N is sized correctly, you will get the same result you would with an actual election, and we don't have to have everyone waste their time voting.
This would never happen, of course, and I honestly can kind of understand why; the results aren't the only thing that is important, feeling connected to the process and that your voice matters also is important. It is a bit of a agreed upon delusion, though.
I mean, insomuch as any action I take is a consumer action, because I am a consumer, this is true. That's why Luigi'ing is a consumer action.
But 'vote with your wallet' is an illusion; you have no way of informing an entity why you are rejecting their service if you simply don't patronize them. On a ballot you're actively choosing another over them. As a consumer, you're otherwise 'invisible' to them.
Walking past Target out of rejection of their politics, for example, is no different to them than the person next to you walking by because they don't need anything from them at that moment (and realistically, they would probably prefer to just switch you for said politically/privacy-un-conscious person). It's still good to stick to your morals, but that alone isn't actually 'consumer action' in the way you mean it.
It requires a coordinated, public messaging campaign that a group is boycotting actively to have any impact on a business. Your individual action of not clicking on Accept Cookies does nothing to influence businesses.
We spent money on goods/services we choose, and receiving money is a very strong signal to a business. Not spending money is an extremely weak signal.
Opposites.
>We don't vote for a policy (although that is a common misconception.) The collective power of voting is often voting against a person/party : voting them out.
Few people get coffee to support union labor but knowing that a coffee shop is actively antagonistic toward unionization may cause you to choose a different shop. The collective power of voting with your dollar is to 'vote in' businesses. The businesses not receiving votes must change or find themselves voted out. Much like politicians, businesses can also look at where the money-votes are going.
If you aren't worried about the US government having this, it's a sign of significant privilege and safety a lot of others don't have.
It's not possible to be a ghost, but it is possible to reduce your surface area in these systems, which is what I focus on. Denying tracking cookies is a single tool in this quite large toolbox.
Its highly unlikely your vote will swing an election.
If you want easy things to do use cookie blocking extensions.
Which is why those things need laws to create any meaningful change.
These are all related to the collective action problem (https://en.wikipedia.org/wiki/Collective_action_problem). This is why we have regulations and rules and laws about things like pollution, because we CAN'T rely on everyone wanting to live in a clean world to make everyone not pollute.
My own personal bend is that I do not want to be sold anything and I want anonymity where possible. We’re constantly being advertised to. Anything small action that I can take to deter that, or make the ads less personalized/interesting/distracting to me, is worth it. Even if I also will never knowingly click an ad.
It’s probably largely a control thing psychologically. With cookie banners specifically, I also don’t want to concede to dark patterns which make accepting easier than rejecting.
You can always choose this no matter what ads they show you. In some ways, choosing to not be sold AFTER being shown ads might be more effective at shutting down that behavior than simply avoiding the ads entirely; forcing the company to pay to show you the ad that you ignore is costlier to them than simply not being able to show you the ad at all.
Right, but this is not solely about cookies or blocking ads. You also leave behind data which helps create a profile. AI is mass-creating profiles of everyone. Not everyone will have the same pattern, but information space is finite and they get more and more data about you over time. You may think this is not relevant for your use cases, but can you make this as prediction in the future?
I'm not a revolutionary taking up arms I'm a voter and a citizen in disagreement. Unless I am seen and counted, then being any of those things is worthless as well.
There is no value in hiding from the system while the system goes to hell and attacks everyone else.
That's not up to you to decide. It's up to whomever is in power and has the ability to label you as such.
See: US ICE telling people filming that they're domestic terrorists because they are filming.
See: the poem "first they came..." which happens every time
- CBP has admitted to buying location/advertising data from brokers to use in helping locate people to arrest
- Phishing and identity theft can be made easier due to cookies... security researchers have even demonstrated 2FA bypass techniques based on it
- Price discrimination - Consumer Reports found that flight prices can fluctuate based on your cookies. Sometimes they would even raise the price if you kept searching for routes, as an indication that you were in a hurry, thus likely willing to pay extra.
- Healthcare discrimination - Companies have been found to raise healthcare prices or deny coverage due to cookie data aggregated via brokers where external sites tracked a person's health conditions based on what pages they visited (examples: fertility, cancer and mental health support groups)
- AI models or automated systems using cookie data to predict housing stability, creditworthiness, and employment risk without ever seeing your resume or credit report directly
- ProPublica found that Facebook was allowing advertisers to target their housing ads based on specific age/race groups stored in cookies
- Some recruiting firms have used cookies to infer personality traits and political leanings. Your employment application could be rejected or deprioritized based on that
- Based on the previous examples, I think it is not a far-fetched idea that websites and services could deny you access altogether based on data revealed by a combination of things like your browser fingerprint + brokered cookie data, such as political affiliation, estimated income, race/gender, health situation, etc. Imagine for example, not being able to order pizza because you badmouthed their favorite president online.
It's also harder to change your mind later and go delete a bunch of specific cookies to opt out when you could have just said no from the beginning.
https://abrahamjuliot.github.io/creepjs/
And yes it often results in endless captcha loops.
Only Tor Browser can reliably fight with it.
Also, that EFF site only checks against other people who visited the same site, so the results are skewed IMO. The other comment that links to creepjs is what I consider the best available open source tool.
You don't have to compare your fingerprint with other visitors. Just have a look at the detailed information to understand which things reveal your identity the most.
Would be nice if there was some other solution, like maybe encrypting the browser profile and then requiring a pin/password/biometric/something to unlock it on each start.
Many sites I use force email or SMS-based 2FA, sometimes in addition to "security questions" and/or have other multiple steps of authorization (like captchas) required; it's often not just a simple username/password for me.
Now multiply that by 25 different sites. Not happening.
Then don't. No need to be sad about it.
> I, as an individual, am not going to have any effect on a business if I opt out or not. No business decision is going to be made because I opt out.
I do it more from a point of view of principal. I don't want following around the Internet by all and sundry who care to, any more than I want to be followed down a dar alley, for followed into Tesco by someone yelling “hey, Dave, I saw you went to the pub last night, my shop has some cheap spirits” or “hey, Dave, I saw you but a network switch the other week, do you want another one?”.
I also resist anything wrapped in many layers of dark patterns, and that describes almost all current ad tech.
> You might argue that it will matter if enough of us do it. Sure, that is true... but again, it won't matter if I do it or not. If N number of people opting out is enough to ruin the business model, then N-1 is surely enough as well. There is a 0% chance that I am the one who finally causes the system to collapse.
If your stats knowledge and reasoning accept that, then I've got an infinite compression scheme for you. It can compress anything including compressed anythings!
You are jumping between two factors of large numbers haphazardly from sentence fragment to sentence fragment, and the logic isn't following you. At some point N-1 might make a difference, and you could be that -1.
> I do use an ad blocker, and never click on ads.
To use your argument on tracking: but many people don't, so why do you bother? What makes you think you could be the +1/-1 here but not there? And by blocking ads you are blocking a fair portion of the tracking, in fact that is why I block ads much more than the ads themselves. I don't run sponsorblock for the other side of the same reason: that doesn't affect tracking at all.
> If having more information about me allows the website to charge more to show me an ad, and I never click any ads, then I am hopefully helping decrease the return advertisers get by using personal information.
And when the database eventually leaks, many others will have the extra information about you.
And again: by blocking the ads using most ad blockers (obs not all work the same ways) you are blocking at least some tracking.
--------
But again, if you don't want to block tracking, don't. No need to be sad that we've not convinced you with our arguments as to why we try to block it. I know other devs who take your attitude (that is simply isn't worth their effort), and many others who take mine or similar (when it isn't worth the effort, the information or product behind the mountain of “legitimate interest” checkboxes isn't worth the effort either so I'll just move on). Our threat and principal models can be different from ours without either of us being bothered by the other's choices here.
Saying you don't see an individual motive here to do anything just says that you don't see how interconnected everyone is in modern society.
Arguably, clicking on the ad but never buying would have a stronger negative affect. The advertiser pays for your click but gets no return...
I use an adblocker too.
there's a reason I don't walk around naked either. it wouldn't hurt me, but I don't need that kind of exposure for no upside
You're going to be presented with ads and preyed on by marketing no matter what. The "made up story about who you are" is just even more imaginary the less they know about you. You'll simply be presented with less-targeted ads.
The only times I've stopped, or tried to deny it is with the recent thing I've seen from some sites that say "accept cookies or pay money". I think that is scummy, and against what these regulations require, so I'll usually just close the site in that case.
Oh and to address the point from the main article, I think I'm unfortunately beholden to more companies, but would strongly prefer to not verify my identity, because I have little to no trust in the companies to safeguard my actual personal data. (rather than inferred cookie tracking data, which they can have imo).
One click usually gives random foreign corpos the right to your data across a multitude of platforms, the right to identify you across data sets, and to permanently link your device identifiers to you, for ”fraud detection” on a site which sells nothing.
Clicking on accept or deny on those notices makes no real difference, since the ”partners” and ”vendors” usually enshrine their core data activities into the ”legitimate interest” category, which has no opt-out.
I still have the same question… how is my life going to be made worse by that happening?
All of your data starts affecting everything your data is used for.
You may get worse rates for a mortgage, or not get one at all. You may be denied insurance or insurance claims. Cherry-picked details of your online activities may be used against you in a court of law, if you ever find yourself in one for any reason (think custody).
These are the very mild examples from a somewhat functional society. In the other end of the spectrum, where societal breakdown is imminent, you have things like getting disappeared, thrown in a concentration camp, executed on your own front yard.
I just don't think blocking cookies meaningfully protects anything that I want to hide. I feel like it is putting gloves on while you walk around naked, it isn't doing anything to protect your privacy.
> You may get worse rates for a mortgage, or not get one at all.
That is an interesting example, because getting a mortgage is going to require me to voluntarily give ALL my personal information to the company giving me the loan, and they will absolutely use all of that to determine if I get a better or worse rate. I am literally giving them my entire financial history, they don't need to try to piece it together using my browsing history.
Also, shouldn't mortgage companies determine rates based on personal information about you? How else should they manage risk? It would be awful for our society if banks were forced to give loans out at flat rates for everyone. There would be zero incentive to pay back loans, because they can't use you not paying it back to decide not to give you more money in the future. If banks had to give everyone the same rate, they would stop lending money entirely. There would be no way to avoid losing it all, why would you do that? No, we WANT loans to be based on personal information, because that is what allows us to have control over our own financial reputation.
> Cherry-picked details of your online activities may be used against you in a court of law, if you ever find yourself in one for any reason (think custody).
This one seems very nebulous, and a very unlikely and low risk. Courts can do discovery; they can obtain much more personal information than cookie based online tracking data. I can't see how this would be worth considering.
> These are the very mild examples from a somewhat functional society. In the other end of the spectrum, where societal breakdown is imminent, you have things like getting disappeared, thrown in a concentration camp, executed on your own front yard.
If this happens, browsing history is going to be the least of our worries. They might throw you into a camp because you DON'T have any browsing history and that is suspicious. If there is no rule of law, you can't expect plausible deniability to help with anything. If we get to that point, they are going to have a lot more than ad tracking data to work with. The added risk seems negligible.
Ignore at your own peril, and enjoy risk with no benefit.
Also, gig workers get paid less when in a poor financial position. Harassed, detained when crossing borders.
These are the start, not the end.
They'll get it one way or another
With IP tracking, you don't really need cookies much anymore
I just always the most left button, as this is usually "cancel" or "deny" - not alwys right,though :-D LOL
Its not always clear what the desired outcome is here. The dark pattern could have nothing to do with the tracking most folks worry about. We like our phones more than our laptops because we touch the screens for example. The dark pattern here could simply be you use the site more because you do more actions there driving you to waste time and view ads. Who knows.
It's disheartening that so many people still do this (and not accepting has rarely ever required enormous efforts, to begin with).
There was a time where the Internet was the wild west and you could've easily been personally targeted and exploited. Businesses sold your data to whoever.
Even today, if you decide to accept all cookies, you're safer than what you used to be.
Rejecting the non-essential cookies puts you in the safest spot from bad actors.
> There was a time where the Internet was the wild west and you could've easily been personally targeted and exploited. Businesses sold your data to whoever.
Yes, I remember when the internet was a much more dangerous place, in all sorts of ways. Browsers were not as secure, network security was not very robust. Most things were plain text. Hell, my friends and I used to run ettercap in our college dorm, because the entire dorm LAN was unprotected from ARP spoofing. Everything was sent in plain text, we would capture email passwords, AIM passwords, etc. We would play pranks on each other where we would spoof AIM messages to different people pretending we were someone else on the dorm floor.
I think some of the regulations have helped the internet be safer, but the tech is really what has changed.
The data trail you are creating is much more personal and invasive than you want to imagine, and in the wrong hands it could be used to devastating effect.
You are. Tracking is extremely dangerous to the society.
Before Shiftkey offers a nurse a shift, it purchases that worker's credit history from a data-broker. Specifically, it pays to find out how much credit-card debt the nurse is carrying, and whether it is overdue.
The more desperate the nurse's financial straits are, the lower the wage on offer. Because the more desperate you are, the less it'll take to get get you to come and do the gruntwork of caring for the sick, the elderly, and the dying
You’re not missing anything about what’s likely to happen to you personally. What you’re missing is the manner in which rights shape your life and your society even when you don’t exercise them, and sometimes even when nobody is currently exercising them, and that significant harm can be built out of a vast number of smaller harms that aren’t individually that bad.
Moral of the story is: If you want me to see your content, and maybe spend money, don't cover up your content.
Especially if you're not EU-based and not subject to GDPR, stop listening to the laws of some foreign country that doesn't control you.
I am fanatically following my rule "one email per website". Obviously, they all route to the same inbox. Initial motivation was to see who leaks my address and simply block it. However, the separation helped me out tremendously more than I ever expected (at the very least I believe so).
I'm originally from a country with a highly oppressive regime. Years ago I signed up for financial support to a political opposition leader. Things weren't as bad and it felt safe enough at the time. They had my email, of course.
Eventually opposition systems were compromised, and the full donor list became public. The regime's response: they cross-referenced it against emails registered on government services. For quite a few whose addresses matched, police officers paid a visit — looking for grounds to fine them, pressure them, etc.
My alias for that site existed nowhere else. No match, no visit. Definitely an experience I was more than happy to avoid.
I'm not out to convince you since my reasons are unlikely to apply to you. There are some of us who want privacy for privacy's sake. We respect the social boundaries of other people, and find those who don't respect our social boundaries creepy. We don't much care one way or the other if those people are out to exploit us or to harm us. It is the act itself that we consider violating.
But to me, what is mind blowing, is when one day you accept the cookies on random e-commerce or review website about vacuum cleaner, and then later when you browse news or look at videos, there is suddenly a constant stream of advertisement for vacuum cleaners, everywhere.
"We kill people based on metadata"
It's really alarming, actually. I run the cyber security training & phishing simulations at my work, and it's the younger employees that struggle the most. It's like they just assume that everything on the web is trustworthy.
It's not hard to see why though. They grew up with app stores & locked down devices. No concept of a file or file system, no concept of software outside of the curated store & webapps. People that never had to take responsibility for their own digital safety because "someone else" (Google, Apple) always did it for them.
> It's not hard to see why though. They grew up with app stores & locked down devices.
When we create a safer world, people’s defense mechanisms naturally atrophy or are never developed in the first place.
We might be safer in terms of vulnerabilities, root exploits, RCEs, etc. but the internet is still full of malware, scams are still just as rampant. Vigilance is still very much required, but is no longer taught.
Look at all the malware available on the Play Store. The curation does nothing but create an illusion of safety.
That stuff is still there if you look for it, but it's not on your social media feeds or in any of the apps provided through app stores.
This accounted for most of the risks on the wild west internet, but the worst case scenario of permanently losing data or having to reinstall Windows was actually rarer than it was made out to be imho.
These days the common risks are the same, except they're no longer risks - all of those have been built into the fabric of everyday internet usage and criminals have been replaced by businesses. It's like the cliche about Vegas being better when it was run by the mob.
Hell, cellphones these days ship with spyware pre-installed. Samsung being the one of the worst for filling their phones with their own apps which spy on you constantly.
Believing you are more under threat from sophisticated government hackers rather than unsecured IOT devices, unvetted npm packages or hijacked download links is just LARPing for people who want to sound more important than they actually are IMO.
In terms of cybersecurity, I see it as "security first" culture means people rely on the system to keep them safe. "Safety third" (or security third) emphasizes that everyone should already know they are operating in a risky and dangerous environment and take security as a personal responsibility.
It's just a reminder that no one cares about your life more than you do, so stay vigilant and take personal responsibility.
edit just realized I didn't actually answer your question on the first and second priorities.
I suppose First would be the reason the system exists in the first place (buy something online, for example). Second would be the user experience of doing the thing. Security should help you take calculated risks rather than prevent you from taking any risks at all.
When I got filtering on observe-only mode I saw users were getting up to a dozen phishing emails every day.
We quickly did a hard simulated phishing test and most users opened the email but zero users clicked through.
Two years later, after we had excellent email filtering in place, our simulated phishing test had a 30% fail rate.
Take from that what you will!
It was also drilled into me that the default state of anything on the internet is to be untrusted and potentially harmful.
It also helped that you could actually tinker with things, and there were plenty of foot guns around to drill that lesson home.
Somewhere along the way that message got lost and didn't get communicated to the young ones, and I'm not even that old (38).
I think almost every Android user has thise concepts.
But on the trustworthy web assumption, I agree. The only effective remedy is a personal calamity.
(fwiw it's been a while since iOS also have those concepts)
No other prior generation comes close.
Compare them to people growing up in the 1980s. The average person at that time was overwhelmingly oblivious to computing very broadly, their grasp of a "file" as a concept would have been close to non-existent. That was just 40 years ago.
In the mid 1980s a mere 10% of US households had home computers. And that was a high mark globally, it was drastically lower in nearly every other country (closer to zero in eg China, India at that time). The number of people routinely using office PCs was still extremely low.
Today young people have a computer in their hand for hours each day, and they knowingly manage files throughout the day.
My kids will know way less about filesystems than I do, because I had to learn DOS commands to navigate around the operating system if I wanted to play computer games, which led to a lifelong interest in how computers actually work at a level they can (and, so far, do) happily ignore.
While it is possible to interact with the local file system on a school Chromebook, it’s certainly not the default. School interactions with Chromebooks seem to consist of logging with highly secure passwords like “strawberry” and using Google Docs. And playing games with heavy PvP components and paid DLC (paid by parents whose kids beg for it, not by schools) that call themselves “educational” because they interject math problems needed to use those juicy spells, make no effort whatsoever to teach anything, but produce a nicely formatted report correlating scores to numbered elements of the Common Core standards.
As a non-Apple user, this is not something that happened to me. I literally have a "Files" app on my Android phone and my laptop/desktop.
In my files app i see "downloads" "images", "videos", "apps", "starred", "safe folder". In "images" i see pictures tagged "downloads", "camera", "DCIM", "screenshots" and one odd "2024-12-03_description_here" that I clearly names myself but don't remember doing that.
I have no clue how that maps to a physical phone filesystem, even though I know it's there. I'm sure teenagers don't know that too.
Yes there has been a Files app on iOS devices for well over a decade
Yes, which gets autosynced to my immich instance
https://www.youtube.com/watch?v=tnPAhVxsPHE
> Your iPhone is Lying to You About Files...
> And you might be thinking, finally, we have the real directory structure of all the folders inside of the iOS device. But that's actually just another illusion. Now the files manager is using guess what? A SQLite database. So it's more just like a generic lookup table inside of that so that we can preserve the sandboxing of the untrusted files for the application. So what it's doing is it's it's creating this kind of fake directory structure and then if you try to go to an associated file, it's doing a lookup into the SQLite database to find the real location of the actual file.
Same same, but different...
I get that it's supposedly about security, but this is not the only secure way. It is however the most convenient secure way for Apple, as now the only simple method of backing up and syncing files through all those isolated containers is iCloud.
And easily get sold add-on services. How many people hit the 5GB iCloud limit for backups and just pay without stopping to think that it might be possible to do local backups to your computer and you don't really have to pay for extra storage?
Just hit them with the scary language "You are at risk of losing your photos forever if you don't pay!" because that concept of "Oh, photos are just files in a directory and I can copy those anywhere I want" doesn't exist. To many, those photos are part of the gallery app, not a separate file from it and since that app only runs on the phone, surely it must not be possible to copy them anywhere unless I pay for the storage.
No, they do not. First, simply using something does not mean you understand it at all. Secondly, because the devices they've become the most accustomed to work very hard to hide all those details from the user.
They know app silos, not file system hierarchy. Ask a teenager where a file is on their phone and the will tell you the name of an app. Ask them how to copy it somewhere else, and they'll use the share sheet and send it to another app.
High adoption doesn't equate to high literacy.
To be fair, at least Android and presumably iOS grant apps by default no access to your files in modern versions.
The only way to get, e. G., an attachment downloaded via Thunderbird to a PC or another app is the share dialogue. A user does not access to the isolated app storage by default on an unrooted Android phone. For better or worse the young user is actually making the right choice here for their platform.
(This is also why making a backup of an Android phone is a nightmare when you aren't using a first party option. ADB is sometimes able to bypass it)
Note taking apps are a prime example of this, using a proprietary localdb for notes, inside of app storage you can't access, forcing you to transact with your own data exclusively through the app (and whatever subscriptions or upcharges that come with it). We've trained out the idea that these could just be local text files in a directory you can access and do with what you want.
I've watched discussions around open file formats fade away into obscurity along with the rise of mobile, and now we have to fight on whether we should be so graciously allowed to install software on the devices we own or not.
Not everyone needs to be a computer science student, but some basic level of curiosity or education around how tech works should be required in school, at the very least a warning message of "Your data isn't safe if it's not under your control."
But have you considered that a meaningful number of users actually want functionality that plain text simply can’t provide?
I understand files and file systems, I’ve worked in IT for decades, mostly in open source. I still choose a non plaintext note solution because it delivers capabilities that plain text cannot, especially across devices.
As long as the data can be exported to open formats, why would I voluntarily limit the value and functionality my tools can provide?
That's exactly the point!
The file system is hidden from modern users. Kids brought up on this now have no idea or concept of where their data resides.
It's just not commonly used for the reason the other person mentioned (share buttons between apps that are file type aware)
Unfortunately, they don't.
They might have had a computer in their hand for hours each day, but they barely know anything about it. The ones who do tend to be those who grew up playing on PC, as opposed to console or mobile, because the latter - despite falling under the "digital natives" aegis - are really shockingly ignorant of even basic concepts.
I learned to code on a Sinclair ZX Spectrum machine!
"Those were the days, next n" ( https://m.youtube.com/watch?v=-d8UfQn3BEg&list=RD-d8UfQn3BEg... )
I totally disagree!!! Yes, everyone works with computer, phone, tablet, whatever, nowdays!
But does generation z "knows" about what a computer is?
Absolutely not!!!
While tech has advanced and graduated IT personal know more than previous generations (obviously!), all the rest, while they do know how to do their jobs, they know nothing about computers!!! They are pretty much like everyone else that didn't know what a computer was in generations x and previous!!!
However, contrary to previous generations, because they do interact with the tech, they represent a higher security risc for them and for others!
... Because they know nothing about it!!!
It's like giving a box of matches to a neanderthal in the middle of the woods...
Almost everyone in the "Gen x and previous" that interacted with the tech, did know what they were doing (past the initial learning phase)!!!
This does not happen after gen x!
It's a comparison between
Gen Y and Gen Z
and NOT Gen X and Gen Z!
It's people born after 1995 that are completely unprepared! Worst: they almost all tend to think they are prepared and that they even know more about it than previous gens (and because tech has evolved they actually accomplish more, but unfortunately they understand a LOT LESS about the underlyings of it!!! Naturally, there are exceptions! Few, however!)
I was in kind of a hurry and messed it up!!! (however, I do tend to think of Y as a transitional generation where late borns - think 92 or after - won't actually remember much of theirs "last analog generation")
So, I do agree with you!
I've tried to edit it but I'm no longer allowed to!
Thank you for pointing out my mistake!
Also, I'm kind of amazed you do remember the analog days! Being born in 87 makes you aware of it around 92 or 93! Past 95 things start to flip and after 00 all hell broke loose (what's analog again?!)!
Most people don't old up much to their 13yo memories! Keep that up! It really makes a difference "today"!
Still it does depend where you live in! This "generations" timeline work well in US cities! But if you change country or if you don't live in a city that timeline doesn't hold up that well! Tech arrives latter and the ways of life get altered later! That's why many people tend to identify more with the previous generations! Specially if you're born on a generation edge!
Yeah... scientists try to put all in one simple bag but the truth ain't that simple!
> Yeah, I have a particular rant about this with respect to older generations believing "kids these days know computers." [...] they mistake confidence for competence, and the younger consumers are more confident poking around because they grew up with superior idiot-proofing. The better results are because they dare to fiddle until it works, not because they know what's wrong.
You nailed it! Simple and short!
GREAT COMMENT!!!
I couldn't think of a better way to put it!
Well done!!!
Ahahah
This argument is like saying you understand nutrition because you eat food every day and haven't died yet.
To the sibling comments: don't "accept the cookies" and then delete them.
- - -
I'm super angry at what the web has become, especially at the OS browser community. There is 0 browser (that I know of) that can access the web safely and conveniently. Atm I use Firefox with uBlock which blocks the cookie banners, but Firefox's extension model is broken, and every single extension provides 100% access to my websites to whoever controls the extension. I don't like it.
We need a browser with a safe extension model.
- - -
edit: I guess using 2 Firefox profiles, one with uBlock and one with my google/facebook/bank/amazon/etc accounts solves the threat posed by uBlock and extensions. I still don't like it.
But there are couple of things I find subpar:
You can’t import/export a list of website permissions. For a couple of extensions I’d like to say “you have access to every website, except this narrow list” and be able to edit that list and share it between extensions.
On iOS, the only way to explicitly deny website access in an extension’s permissions is to first allow it, then change the configuration to deny. This is bonkers. As per the example above, to allow an extension access to everything except a narrow list of websites is to first allow access to all of them.
Finally, these permissions do not sync between macOS and iOS, which increases the maintenance burden.
¹ Private being the equivalent to incognito.
What makes it worse is that a substantial portion of users block web trackers through an adblocker. However on phones, unless you have a rooted phone or use some DNS-based blocker, all these analytics get uploaded without restraint.
Atm I use Firefox with uBlock which blocks the cookie banners, but Firefox's extension model is broken, and every single extension provides 100% access to my websites to whoever controls the extension. I don't like it.
Some browsers (e.g. Vanadium, Vivaldi) have a built-in adblocker, so you have to trust one party less.
Why are you using that malware? Is a "nice wallpaper" worth the security risks? Really?
Browsers should provide a filtering option before they makes a request.
IMO a lot of no-brainer options are missing from personal computers. Like the ability to start a program with restricted access to files, network or OS calls (on Windows and on Linux). Browsers should provide the ability to inspect, and filter network access, run custom javascript on websites, etc.
But the tricky part is that "reading files" is done all the time in ways you might not think of as "reading files". For example loading dynamic libraries involves reading files. Making network connections involves reading files (resolv.conf, hosts). Formatting text for a specific locale involves reading files. Working out the timezone involves reading files.
Even just echoing "hello" to the terminal involves reading files:
  $ strace echo hello 2>&1 | grep ^open
  openat(AT_FDCWD, "/etc/ld.so.cache", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/lib/x86_64-linux-gnu/libselinux.so.1", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/lib/x86_64-linux-gnu/libgcc_s.so.1", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/lib/x86_64-linux-gnu/libm.so.6", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/lib/x86_64-linux-gnu/libc.so.6", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/lib/x86_64-linux-gnu/libpcre2-8.so.0", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/proc/filesystems", O_RDONLY|O_CLOEXEC) = 3
  openat(AT_FDCWD, "/proc/self/maps", O_RDONLY|O_CLOEXEC) = 3
openat(AT_FDCWD, "/usr/lib/cargo/bin/coreutils/echo/en-US.ftl", O_RDONLY|O_CLOEXEC) = -1 ENOTDIR (Not a directory)Bubblewrap allows you to do that on Linux.
But the browser also has 100% access to all of the websites. The browser is software that works for you. You control the browser.
Who but yourself do you imagine controls your extensions?
Oh really? Then why do my browsers keep moving things?
- Read-only access to cross-tab web site content
- Ability to modify web site content
- Ability to access the network
They can always "access the network" in that the extension developer can push static updates for things like ad block lists or security updates.
It might be possible to have "read only" cross-tab access include automation APIs like keyboard + mouse, with user prompting to prevent data exfiltration.
However, I'm just suggesting a modest improvement to browser extension security (that doesn't completely break ad blockers like Chrome's approach).
In practice, I run an ad blocker, and just trust that it won't exfiltrate bank passwords and stuff. Imagine the blast radius for a successful and undetected UBlock Origin supply chain attack!
My "pick one" approach (ad blockers would pick the middle option) would mean that comparable supply chain attacks would also need to include a sandbox zero day in the web browser.
At some point, you have to implicitly trust someone unless you audit every line of code (or write it yourself) and build everything from source that you run.
But there are other uses cases, like cloud2butt.
I'm not the person who wants to redesign the browser extension ecosystem, but I can build Firefox from scratch and review the source code if I want, unlike Safari.
Once again, I'm not the one who said they would like to design a new browser extension framework, but I have created custom versions of Firefox that have all ability to phone home removed and modified extension support. So not verifying every single line of code, but making fairly substantial changes in the direction the parent poster wanted to go in.
I'm interested in a conversation about that, not you pestering me about whatever issue I seem to have triggered within you that resulted in your interjections in this conversation.
You didn’t say this?
> At some point, you have to implicitly trust someone
A model so I trust my OS and my browser, and I don't have to trust anyone else, that is, they can't harm me.
Or do you want the browser to enforce permissions on extensions so you can lock them down as well as auditing them?
https://codeberg.org/konform-browser/source/releases
https://techhub.social/@konform
Shared today on Show HN but seems to be drowning in deluge of LLMs...
https://news.ycombinator.com/item?id=47227369
> every single extension provides 100% access to my websites to whoever controls the extension
That feels a like a bit of overstatement and depends on what addons you use and how you install them... CSPs at least make it possible to restrict such things by policy (assuming user has been exposed to it and parsed it...). https://developer.mozilla.org/en-US/docs/Mozilla/Add-ons/Web... MV3 introduced further restrictions and controls regarding addon capabilities. While I agree the UI and UX around this could be much better, it's not all hopeless. The underlying pieces are mostly there.
While the fundamental addon execution security model in Konform Browser is inherited from upstream, for core addons like uBO you can improve the supply-chain security situation by loading it under "system scope" and disable addon updates in the browser itself. So while we don't (yet) improve on the runtime aspects you speak of, at least for now we can tighten up the supply-chain side to minimize risk of bad code running in the first place.
Literally `apt-get install webext-ublock-origin-firefox`.
"Enterprise policy files" can be used to change Firefox behavior and tweak security model around addon loading. A little explanation and reference of how it works if you want to do the same in other FF build or for other addons: https://codeberg.org/konform-browser/source#bundled-extensio...
Any particular addon you think is missing from the list there and should also be packaged and easily available? Maybe will be able to improve some of the security-UI/UX here too down the line. I'd be keen to hear your take on how this should be done better!
Regarding what addons can and do leak about you to the outside... I think you may also take interest in FF Bug 1405971. We ship a patch for that which can hopefully be upstreamed Soon (tm).
I don't even think it would be even a blip on the radar now.
It really is depressing how much ground we've given.
My local library is run by the county government, so of course the government can see the checkouts, they are the ones I check the book out from. But they restrict checkout information from others. For example, a parent can see the checkouts of their own children, but not after they turn 13.
Perhaps you're talking about subpoenas? Checking some other libraries I see SF Public Library has some discussion about that, but they delete books from your checkout history once they are returned. https://sfpl.org/about-us/confidentiality-and-usa-patriot-ac...
...I mean I suppose you still can but still, it's not as obvious anymore and people's mobile phone numbers are unlisted by default and not publicly linked to an address..
Because of this, I found it odd that the regulation allows displaying the accept cookies button. Instead, it should be rejecting cookies by default and a separate flow to accept tracking cookies (e.g. via account settings page)
"Use Chrome"
"Crazy"
Or, completely normal behavior. Are you suggesting that people should live in a shed in the woods like the Unabomber?
Terrifying.
It’s naive to think that cookies are the only tool used for tracking, but they are the most powerful tool for web based tracking.
Sorry mate, the GDPR is there for a bloody good reason; and legit companies obey the law.
But at least we have cookie banners everywhere.
The GDPR does outlaw unnecessary collection of personal data without explicit opt-in consent. It's baffling you appear ignorant of this.
So you can pretend that the law is effective or you can admit that all it gave the world were cookie banners.
Blame the parasitic ad-tech industry for their existence. Not the lawmakers who protect all our privacy.
That being said, it was very early regulation in this field, and more recent approaches are already better, e.g., GDPR, DMA.
Accept everything, the end the session.
That said even with throwaway relay emails I don't sign up to much
There is a similar story with Ford and how they build pavement everywhere and taught the young population that roads are for cars. Now we have to drive for 10 minutes to get from one shop on the plaza to another shop on the different plaza.
https://en.wikipedia.org/wiki/Roman_roads_in_Britannia
Unless you mean something else, but Paris was paving roads in the 1750s, a lifetime before even the hobby-horse Draisine was invented:
https://en.wikipedia.org/wiki/Macadam#Pierre-Marie-J%C3%A9r%...
On that page it's mentioned that Macadam (predecessor to tarmac) was used in the USA in 1823 on a stretch of road of 10 miles which took stagecoaches 5 hours to pass in the winter before it was Macadamized, suggesting quite a desire for better roads a century before safety bicycles with chains were invented.
Then 'History of the bicycle' says:
"On the new macadam paved boulevards of Paris it was easy riding ... the "bone-shaker" enjoyed only a brief period of popularity in the United States, which ended by 1870. here is debate among bicycle historians about why it failed in the United States, but one explanation is that American road surfaces were much worse than European ones, and riding the machine on these roads was simply too difficult."
https://en.wikipedia.org/wiki/History_of_the_bicycle#1860s_a...
Although apparently it was a thing in the USA: https://en.wikipedia.org/wiki/Good_Roads_Movement
"The Good Roads Movement occurred in the United States between the late 1870s and the 1920s... a coalition between farmers' organizations groups and bicyclists' organizations .. Early organizers cited Europe where road construction and maintenance was supported by national and local governments."
But now instead, my 11 year old's Roblox thinks she is 18 because she wore glasses in their age verification webcam tool. And it can't be changed unless she uploads a passport, which I will never allow.
Please, gov.uk introduce a gov ID verification service? I could trust that, -ish, I have worked with public sector clients several times...
This is truly crazy. Random companies interacting on this level with children is far from ideal.
> Please, gov.uk introduce a gov ID verification service? I could trust that, -ish, I have worked with public sector clients several times...
I don't like the idea of governments collecting this sort of data either.
FWIW I'm 43 and grew up on the dark parts of the internet.
In the US it's not rare to link accounts through phone numbers that are required in web forms and store memberships.
In Chile they started asking for your National Id with so many stupid pretexts that people got conditioned into just giving it away. It wasn't like this 10yrs ago. I'd rather have membership numbers.
It's technically public information, so collecting Ids is legal, but it's also a universal primary key within the country that allows merging any user-related table you run into.
Retail says it's just to associate it with receipts in case you need that later, but I'd rather just get a photo of the printed receipt for later than rely on them to find my receipt. Supermarkets, Drug stores, and petrol stations tie it to (possible) discounts or points at check-out, which is price discrimination and it's illegal, but we are in our way to get surge pricing as soon as the new US bootlicker president begins his period next week.
In the early aughts I was sitting in on privacy discussions that reluctantly acknowledged that regardless of what we do online, surveys showed you could offer someone at the mall a free Snickers and they'd fill out the whole form.
The perceived cost to the individual of divulging their personal data is near zero; dangling nearly any incentive in front of them will induce them to let it go. And that's not a new phenomenon.
Definitely in 2026 kids should be getting tons of education in public school about how to safely browse the internet, both for personal data privacy and for safety against stalking, doxxing, grooming etc in the same way millenials were grilled about source checking internet resources like Wikipedia.
It's almost like forcing (almost) every website to add these cookie banners has desensitised people to what they're actually saying.
I just click "Accept all" on every cookie banner, life it too short to figure out which checkboxes and dark patterns I have to avoid on each site to not hand over some data...that is than later on just tracked in the backend ("server to server tracking"). Or sold by my credit card company, or tracked by me hovering over some video on YouTube. With the amount of data available unselecting some check boxes on a website just doesn't make a difference.
if there's anything remotely good with GDPR is the requirement to companies to disclose known data breaches
all the rest of it is a terrible idea and only serves to nag people and legitimise the darkest of patterns
the regulation should be there to disallow companies from asking certain information, everything else regarding tracking is self-defeating as it's 1) seldom enforceable 2) hardly binding in any meaningful way 3) pushing people to concentrate their services where they have already surrendered their data 4) legitimising of dark patterns
this new and blatant step towards digital id is a hill i intend to die on, I will not comply and I will do everything in my power so that others don't have to and are even punished for doing so
> "all the rest of it is a terrible idea"
Having a legal right to ask a company for a copy of all the data they have on you is terrible?
Having a right to ask a company to correct errors in data about you, or delete data about you, that's terrible?
A company having to tell you what they intend do with data about you and stick to it for the threat of a big fine, that's bad?
there are bits, but the total package is cancer
> "i completely reject it, because people seem to believe it's there to protect any rights"
Under "Your rights" section on the UK government website you can see that it grants you rights, so people have good reason to believe that: https://www.gov.uk/data-protection
How does it nag people? How does it legitimise dark patterns? What is in it regarding tracking? How does it push people to concentrate their services in a bad way? The GDPR is not just for websites, it's for all dealings with companies.
you are soft in the head if you believe that, there's no argument to be had
How does the conditioning start?
> not value their personal data
Okay, but in practice how much do they do with it that isn't ad placements?
We've collectively long ago crossed over from privacy to convenience, and there's no going back. You and some of us here on HN (myself included) are the outliers.
Set your browser to block 3rd party cookies, add privacy badger and ublock origin. It will have more effect than clicking "reject"
I click "don't send me mail" every time I buy something. Every place I buy from still sends me spam at some point. There are no negative repercussions for them beyond whatever infinitessimal thing me clicking the "report as spam" button does
Same thing with age verification. My kids all have devices that are managed through parental systems like Google Family Link and Microsoft Family Safety. It would be straightforward to have a header for "user is an adult" or not, and to have a standard API for "this site is requesting metadata that you haven't said to automatically make available without permission. Do you want to send it? Y/N [ ]checkbox use this for all sites.
The only time we should even be talking about full identity verification is on user-submitted content, and even then that should be up to the site (with the commensurate legal liability of hosting anonymous slop).
That is wrong. You definitely ARE the target too - perhaps not the primary one but you are part of the cohesive whole. Why would you think that Facebook sniffs for offline data about which doctors people visit? These are not accidents.
The internet has maliciously complied with most if not all regulation applied to it which is where the new mass of banners and interstitials come from but the ultimate effect is to just beat the user into submission. See the EU cookie mandate and GDPR for how badly that turned out in terms of UX (even though the accountability is well in force under the hood, so the bad UX compliance failed and those sites are just screwing themselves).
In this way, Google was initially a hero but is now just another American Big Tech entity that is too big to fail and can do whatever it wants along with Meta and Amazon, and in fact now TikTok's US entity.
Yeah, people will sell these tokens online, but that's not the end of the world. People have bought liquor for minors who sit around the corner from the liquor store since forever. It's still a reasonable comporomise
Surely I don't use the web based services which require a login everyday in my main main browser.
But e-mail address is a hard pass, mostly on the amount of work than the anything else.
Maybe it’s a little bit overkill but I set it all up once and only have to whitelist sites every once in a while so it’s not really an annoyance. Besides, I’m not 100% sure now but I’d say that just using uBlock is enough (if properly configured) to prevent cookie-based tracking so my setup is definitely over-engineered.
I have seen (young) parents who are more addicted to this sort of careless internet use than their kids
It will take some years before the cycle is broken
Future generations will not be conditioned the same as prior ones
Perhaps "age verification" as a wake-up call could mark the beginning of the transition
Either your trust website to not be shady, or not. That button click is not a formal agreement.
I really think this cookie consent concept should have been a browser functionality, so I can make my default choice for all sites and be done with it.
I'm the sort of person that either rejects the cookies, or will use another site entirely to avoid some weird dark-pattern cookie trickery. I don't like the idea of any particular service getting more information than they should.
Siting there I realized, we were not the real target. It is the young people that are growing up conditioned to press accept, enter any details asked of them, and to not value their personal data. Sadly, the damage is already done.