News for hackers. Stuff that matters.

ranger_danger

> if you have an attacker inside the network, it's already too late.

Disagree, I think it's still a good idea to try to mitigate e.g. root escalations via this bug from devices within your network as well, as they could become compromised at any moment via other means and then promote themselves to root.

"default deny incoming" would apply to the filter INPUT chain, and there are several other chains that run before that one (raw, conntrack, mangle, nat), so it's better to use an explicit iptables or nft rule targeting the earliest "raw PREROUTING" chain.

Do note that eBPF can still bypass netfilter entirely, as can containers, or any process using a separate network namespace.

It could be from a multi-part attack where someone combines an application-level RCE like php2shell, then sends the evil loopback packets to elevate to root.
eBPF programs can also bypass netfilter, as can different network namespaces (like as used by containers and some privsep/isolated software).
I also add the same rule for OUTPUT to prevent any misbehaving apps from trying to break things.

Red Hat also claims that netfilter is not enough: https://access.redhat.com/security/vulnerabilities/RHSB-2026...

> The following nftables table drops incoming IPv4 TCP packets that contain IP options, which reduces exposure to this vulnerability but cannot fully prevent it.

I know things like eBPF can technically bypass netfilter if someone tries hard enough, but I'm not sure if they're referring to any other ways to exploit this that a netfilter rule can't catch.

A system running multiple network namespaces might also not have the same mitigations applied inside all of them.

But yes I agree it seems strange that most posts/articles/etc. are not prominently giving out mitigation strategies.

Except I was able to use the PoC to exploit several of my "classic 443 machines" sitting on the internet, like millions of other servers out there.
Are you suggesting customer demand does not influence car manufacturers?
Are you suggesting consumers want cars they can't fix?

They may regret it when the battery dies and it's a $20k repair because they're actually structural components on those cars. Or a single $20 sensor dies that's part of a larger non-serviceable $5k component.

Sortof. There's no guarantee they wouldn't lose customers/revenue if everyone started buying BYDs or NIOs... they could decline to insure those cars at all due to the high repair cost, or not cover all of it, and that affects more than just themselves.
Disagree... they're a lot more integrated than other cars, meaning less parts in a way, which is cheaper to buy, but much more expensive to repair later.

Consumers want protection from cars they can't afford to fix.

Insurance companies want protection from costly warranty repairs.

Mechanics want protection from cheap highly-integrated gatekept parts that they can't work on, and/or won't get paid as much for.

I would say it's actually more complicated than that. Here is a good video that goes over the situation, and multiple perspectives on it: https://www.youtube.com/watch?v=Nim61oVLdwk

TL;DR They severely reduced the number of components by integrating parts into larger pieces. This trades upfront cost savings for longevity concerns and repair prices down the road.

One could argue the US wants to ban them solely because it undercuts other manufacturers, but there's more.

You can also argue it's not good for many other people, like:

- the average consumer (that expects a quality long-lasting product)

- the insurance companies that will be footing a lot of the repair bills

- independent repair shops that either won't get those jobs, cannot actually perform the work due to tech/service monopolies, or simply lose revenue because the work is shorter

Re:WTF Ubuntu? on Monday November 02, 2026 @02:02PM (#50341860)
> Ubuntu has not marked it critical.

Yes they have, and the article links directly to where they say so: https://ubuntu.com/security/CVE-2026-98432

I think the author probably assumes that after almost 3 weeks of the entire world going ape-shit over this, most people reading their post probably know about it already, or know how to find out more, so they didn't feel the need to elaborate.

> Why wait for Ubuntu at all?

There are many reasons... businesses often cannot go this route. But I don't see why it matters unless you're just trying to attack and discredit this person because you disagree with how they write their articles.

Why are you trying to farm out so much critical thinking to other people for you? It is easy to do a quick web search and find out everything one needs to know.

Re:WTF Ubuntu? on Monday November 02, 2026 @01:56PM (#50341774)
> running any sort of Go server like Caddy

It's so much worse than this, and there is a staggering amount of misinformation running rampant about this bug.

MPTCP is not a requirement, it can be exploited merely by sending specially crafted TCP packets with (any) IP options set. No special MPTCP support, web servers or any specific software listeners are even necessary at all to trigger it, just send the packets and boom.

I think the reason people assume MPTCP is a requirement is because that's what the PoC used... but MPTCP itself also doesn't even rely solely on IP options.

Ubuntu also does not even list a single mitigation strategy... at least RHEL did.

And like I said, any normal TCP packet that contains IP (not TCP) options can trigger the bug. I cannot emphasize enough how important and absolutely ridiculous this is.

Like the post says, this is big enough to get a massive amount of people to completely stop trusting Ubuntu entirely and jump ship.

Re:US boy names that became girl names and vice versa on Monday November 02, 2026 @01:46PM (#50341588)
Interesting, they sound exactly the same to me, and I cannot even think of how they might sound different to someone else. Care to explain?
Re:US boy names that became girl names and vice versa on Monday November 02, 2026 @01:14PM (#50341055)
What about Aaron -> Erin ?
Re:Decode kernel panic from QR Code photo on Monday November 02, 2026 @01:13AM (#50333653)
This is why I like to use Binary Eye, it never acts on anything automatically when scanning a code, you have to tell it to.
Re:TCP Use-After-Free: CVE-2026-98432 / CVSS 9.8 on Sunday November 01, 2026 @02:33PM (#50328870)
This is an RCE though...
Re:TCP Use-After-Free: CVE-2026-98432 / CVSS 9.8 on Sunday November 01, 2026 @02:32PM (#50328862)
This is misinformed and dangerous advice, MPTCP is not a requirement. You would need to block all TCP packets with any IP options set to fully mitigate this. Thankfully iptables/nft can do it.
Let me guess, a paper written by Mordechai Guri?

It's not even a contest anymore, that man is the heavyweight champ of air-gap security.

Re:Spooky C++ on Saturday October 31, 2026 @10:35PM (#50322240)
But it's not actually taken as a reference (with &) anywhere I see... and even if it's just internally referencing the (static) string, there shouldn't be any issue with that memory either right?
Re:Spooky C++ on Saturday October 31, 2026 @09:52PM (#50322056)
But if Sanitize has a return type of string_view, then returning the temporary variable should make a copy of it (or move it), right? And the string "foobarbazboo" is static so that's not being freed either.

And the while loop shouldn't even run at all since front() never equals ' '.

Re:Spooky C++ on Saturday October 31, 2026 @08:39PM (#50321677)
but when using it as a parameter it IS stored as a variable, just only within that function, right?
Re:Spooky C++ on Saturday October 31, 2026 @08:35PM (#50321659)
> For example, this only works because the string foobarbazboo is the same length as admin_id

12 != 8

I don't get it...

> As you can guess, this is an example of undefined behavior causing unintuitive results.

No I couldn't... and what undefined behavior where? They don't explain anything.

Important to note that it only helps against DDoS that originates within layer7 e.g. recursively downloading specific page URLs, especially many dynamic ones that are easy to slow down the entire webserver with, such as with git platforms.

Someone (or their botnet) sending a "real" DDoS of a few terabits/sec of layer3 traffic your way cannot be stopped by software running at a higher layer at all. Your only recourse there is playing a cat-and-mouse game of who can change IP addresses fast enough.

Re:C2PA's eMudhra Moment on Friday October 30, 2026 @05:19PM (#50310284)
> "refusing to elaborate on how exactly the failure occurred"

But in fact they did elaborate, even before the news stories broke:

https://bugzilla.mozilla.org/show_bug.cgi?id=2083449#c10

And again with the follow-up issue:
https://bugzilla.mozilla.org/show_bug.cgi?id=2085612#c3

Are you perhaps confusing a bailout with a buyout?
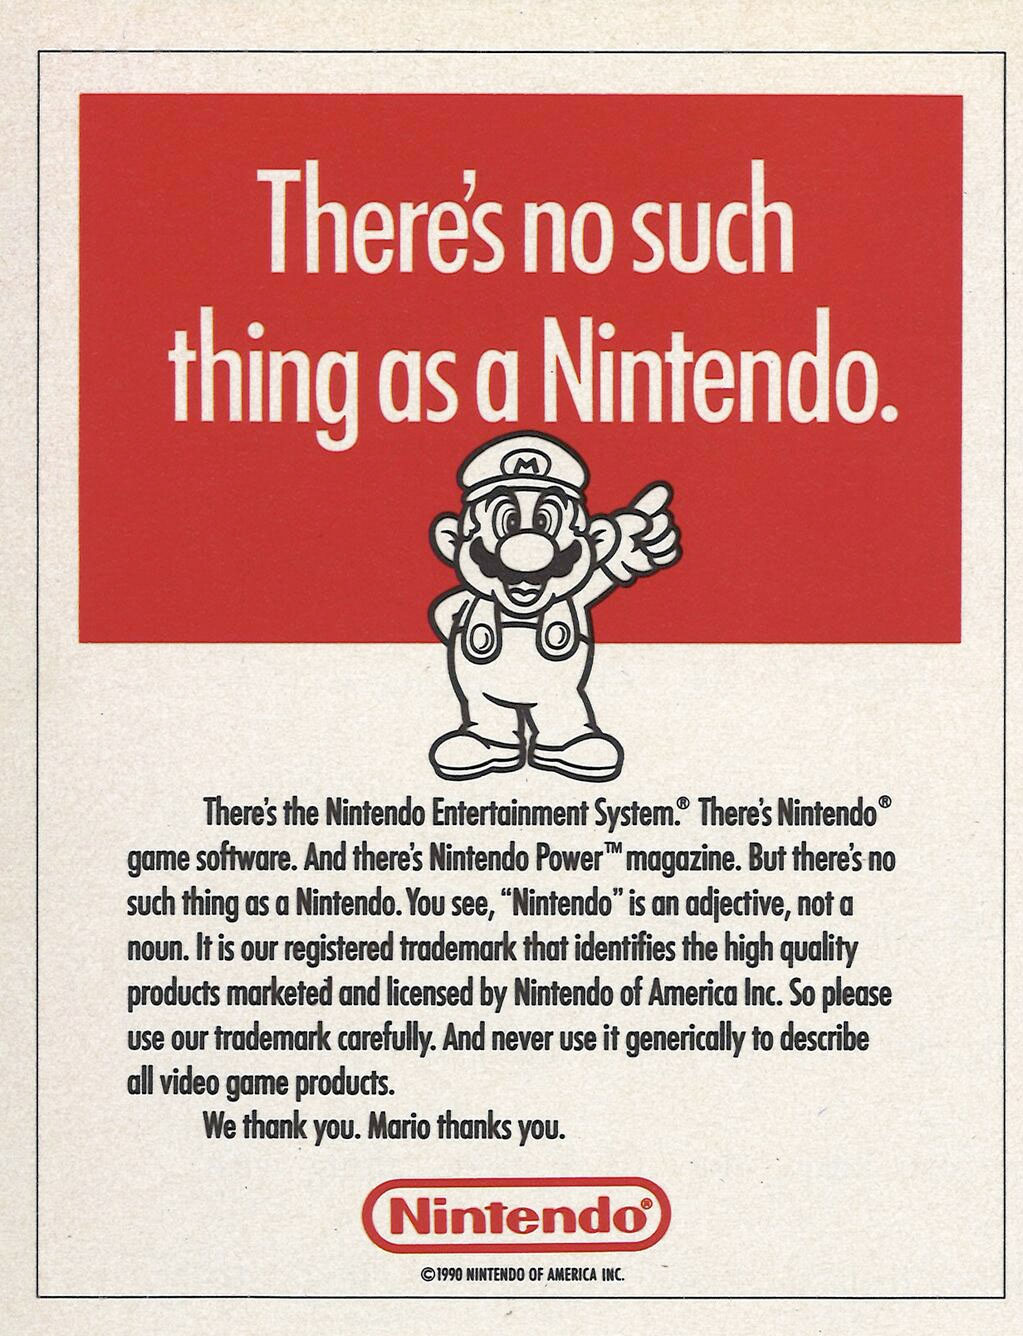
Re:Show HN: A working Nintendo in ~1GB of Qwen weights on Friday October 30, 2026 @01:24PM (#50307185)
They were really upset about it even back then: https://gcdnb.pbrd.co/images/9zn32PxVXM5w.jpg
Do you have a source for this claim?
Re:Zero click, silent, remote Android DoS on Thursday October 29, 2026 @10:52PM (#50299340)
Hi I saw your post on eMudhra "refusing to elaborate on how exactly the failure occurred", but in fact they elaborated before the news stories even broke:

https://bugzilla.mozilla.org/show_bug.cgi?id=2083449#c10

And again with the follow-up issue:

https://bugzilla.mozilla.org/show_bug.cgi?id=2085612#c3

Older »