News for hackers. Stuff that matters.
Re:New Mac ransomware spreading through piracy by cpach on Tuesday June 30, 2020 @06:56PM (#23695758)
I don’t understand how people dare to run executables downloaded from a pirate site...
Re:New Mac ransomware spreading through piracy by AnthonyMouse on Tuesday June 30, 2020 @07:14PM (#23695904)
> I don’t understand how people dare to run executables downloaded from a pirate site...

Pirate sites have reputations the same as anybody. The more reputable ones actively remove spam and malware.

So it's kind of like saying, I don't understand how people dare to run executables downloaded through the internet. Depends a lot on where on the internet you downloaded it.

Re:New Mac ransomware spreading through piracy by milesvp on Tuesday June 30, 2020 @07:23PM (#23695972)
Very much this. Decades ago, when I couldn’t justify the cost of software, I generally knew what places I could trust, and what places might be more sketchy, and what places were guaranteed to infect my system. The cracking scene was very competitive, and any place that messed with the final binary would get blacklisted, making it very hard to get zero day releases from various groups.

I have no idea what the landscape looks like today, and I’d be reluctant to run anything outside a vm, since I no longer know where the reputable sources are, but I’m sure there are still private trackers and discord servers where you could trust every link.

Re:New Mac ransomware spreading through piracy by sneak on Wednesday July 01, 2020 @09:29AM (#23701071)
There’s no such thing as a private Discord. It’s not end to end encrypted, and all Discord “servers” are actually just Discord hosting accounts (and hosted by Discord), so they can always read 100% of everything.

They happily ban users for sharing the wrong links, and have banned entire instances for discussing anticheating technology.

Re:New Mac ransomware spreading through piracy by Polylactic_acid on Tuesday June 30, 2020 @07:31PM (#23696036)
I'm on several private torrent sites and I still wont run software out of a VM. The problem is the users are trusted but unless they packaged the crack themselves they don't even know if there is malware bundled in. Its easy to verify that audio or a book is high quality but verifying software is next to impossible.
Re:New Mac ransomware spreading through piracy by austhrow743 on Tuesday June 30, 2020 @08:40PM (#23696478)
Software on private torrent sites comes straight from the scene, who treat their hobby pretty seriously.
Re:New Mac ransomware spreading through piracy by Cyph0n on Tuesday June 30, 2020 @08:45PM (#23696522)
Exactly. Scene groups are tight knit and very professional.
Re:New Mac ransomware spreading through piracy by techntoke on Wednesday July 01, 2020 @03:26AM (#23698759)
Unless you piss them off and become their target
Re:New Mac ransomware spreading through piracy by dewey on Wednesday July 01, 2020 @07:19AM (#23700225)
If it's not a 0day tracker they usually unpack the scene files and repackage them so you don't have the split archive files. It wouldn't be hard to slip something in in this process.
Re:New Mac ransomware spreading through piracy by philliphaydon on Tuesday June 30, 2020 @09:35PM (#23696794)
One of the things I miss in Windows 10 I don't have on Ubuntu is 'Windows Sandbox'. It's great for testing software out. It loads pretty much instantly.
Re:New Mac ransomware spreading through piracy by heavyset_go on Tuesday June 30, 2020 @11:22PM (#23697429)
Re:New Mac ransomware spreading through piracy by aj3 on Wednesday July 01, 2020 @07:22AM (#23700237)
There are so many ways to escape Firejail, that no one should seriously rely (solely) on it for security. Please, just use proper virtualization for trying shady software/suspected malware.
Re:New Mac ransomware spreading through piracy by panpanna on Wednesday July 01, 2020 @05:18AM (#23699517)
If you are going that route you are better of with LXC or Docker. IIRC LXC is part of the 20.04 install.

Or use Vagrant if you want better security.

Re:New Mac ransomware spreading through piracy by philliphaydon on Wednesday July 01, 2020 @12:34AM (#23697774)
Thanks!
Re:New Mac ransomware spreading through piracy by wsc981 on Wednesday July 01, 2020 @01:58AM (#23698217)
Is there such software for macOS?
Re:New Mac ransomware spreading through piracy by aj3 on Wednesday July 01, 2020 @07:20AM (#23700230)
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:25AM (#23699193)
I don’t think anyone has packaged this up, although the tools are there.
Re:New Mac ransomware spreading through piracy by leoh on Wednesday July 01, 2020 @02:44AM (#23698483)
This is 100%. I'm not sure, however, that I even trust PDFs these days. Somewhat paranoid there are zero days on libgen, etc.
Re:New Mac ransomware spreading through piracy by cpach on Wednesday July 01, 2020 @05:27AM (#23699580)
Sure, PDF is a bit hairy. But you also can choose to not use Acrobat Reader. If you use e.g. Preview (macOS) or Evince (Linux) then I would wager that it’s not exactly trivial to get remote code execution. (Most probably possible though, but it would probably take some work.)
Re:New Mac ransomware spreading through piracy by leoh on Monday July 06, 2020 @05:20PM (#23752882)
I think all clients are a bit questionable since it's such a complex format and because most clients are not written in safe languages. Although they're rarer, even Mac OS X's Preview.app has had CVEs.
Re:New Mac ransomware spreading through piracy by aj3 on Wednesday July 01, 2020 @07:28AM (#23700284)
Here's a tip: the safest way to open sketchy pdf is through PDF.js that's used in browsers as it relies on the same JS sandbox you use to browse net all day. Other than that - open documents in a VM (with reverting to the previous snapshot after viewing the file) or install Qubes where this is default behaviour.
Re:New Mac ransomware spreading through piracy by wolfgke on Wednesday July 01, 2020 @04:54AM (#23699369)
> Somewhat paranoid there are zero days on libgen, etc.

Do you have an alternative to trusting them?

Re:New Mac ransomware spreading through piracy by whitepoplar on Tuesday June 30, 2020 @07:23PM (#23695977)
Which are the most reputable sites?
Re:New Mac ransomware spreading through piracy by AnthonyMouse on Tuesday June 30, 2020 @07:25PM (#23695988)
If you're looking for free software the best site I know of is debian.org, though if you use Windows or Mac you might want to check out firefox.com, libreoffice.org and gimp.org.
Re:New Mac ransomware spreading through piracy by j88439h84 on Tuesday June 30, 2020 @07:33PM (#23696058)
I downloaded the free version of Word from libreoffice.org and it's much harder to use than the paid CD-ROM from Best Buy, so I think that's only a nerfed trial of Word. Same with the Photoshop from gimp.org.

The unpaid WinZip still works great though.

Re:New Mac ransomware spreading through piracy by manigandham on Wednesday July 01, 2020 @02:22AM (#23698363)
Just use 7-zip instead: https://www.7-zip.org/

Free, open-source, and much faster.

Re:New Mac ransomware spreading through piracy by aphroz on Tuesday June 30, 2020 @08:15PM (#23696346)
I realized there were a free WinZip just after I bought my WinRar license
Re:New Mac ransomware spreading through piracy by cpach on Wednesday July 01, 2020 @05:28AM (#23699590)
Winrar’s UI is quite a bit better though, isn’t it?
Re:New Mac ransomware spreading through piracy by grawprog on Tuesday June 30, 2020 @08:02PM (#23696253)
I dunno, I think they just took word 98 and changed the name, I mean it looks the same. It doesn't even have a ribbon. How am I supposed to find the icons I use to do things without it? There's some menus but they're full of text and kinda scary to be honest.
Re:New Mac ransomware spreading through piracy by forgotmypw17 on Tuesday June 30, 2020 @09:47PM (#23696849)
It only takes a few minutes of use and comparison to understand that today's LibreOffice doesn't even come close to touching the level of polish and user-friendliness of Word 98 (Mac) or Word 97 (Windows).
Re:New Mac ransomware spreading through piracy by grawprog on Wednesday July 01, 2020 @01:07AM (#23697935)
I'm guessing this whole section of the thread went over a few people's heads....hn always does have a bit of a problem detecting ironic sarcasm...
Re:New Mac ransomware spreading through piracy by forgotmypw17 on Wednesday July 01, 2020 @12:40PM (#23703463)
I wasn't being sarcastic. I still use Word 97 for writing, because in Word 97, it always takes me two keystrokes to save a new document (Ctrl+S, Enter), whlie in LibreOffice it is an exercise in frustration, because every new document is titled Untitled 1, and that causes a problem when I've already saved Untitled 1.

This is just one example of a basic feature, used on a regular basis, which has obviously been tested thoroughly by the Office 97 developers, but has seemingly barely received any attention from LibreOffice.

I use a very basic laptop, and through the wonders of virtualization have a Windows ME VM with Office 97 on it, and it runs just as fast as LibreOffice does natively, if not faster. In a VM, being used for an hour or two at a time, Win ME has no stability issues.

Win ME came with IE 5.5, and I eventually upgraded it to 6.0. Because I built my site to be compatible with both, I can easily copy and paste what I wrote into my blog. Office 97 and IE 6.0 support Unicode well enough that I can do all this in two different character sets.

I rarely print anything, and I'd probably still use LibreOffice for that. But if I really wanted to, I could probably figure out how to print, too.

The Win 9x series is remembered for being unstable and crashy, but I think it's also a marvel of engineering and UI design. And when you take away malware, random utilities, registry decay, hardware malfunctions, and so on, it's a comfortable, almost typewriter-like experience.

Re:New Mac ransomware spreading through piracy by grawprog on Wednesday July 01, 2020 @02:10PM (#23704574)
Whoops my bad. I was reading all the other comments here in response to this and I responded to yours. I can't disagree. Older versions of word were a lot more stable than newer versions.

About the Ctrl-s thing, maybe it's specific to windows, I use libre office on linux and have for years and Ctrl-s on a new document has always brought up the save-as dialog for me.

Either way, I'd rather use an older version of word or libreoffice over new versions of office.

I grew up using older windows, I don't really remember it being overly good or bad, it just kind of was. I remember lots of crashes, but used to do a lot of things I probably shouldn't have been and I do remember it working for everything I tried to do so I don't really have any complaints really. I don't really have any fond nostalgia either though to be honest.

I stopped using windows entirely outside work over a decade ago so none of it really matters all that much to me.

Re:New Mac ransomware spreading through piracy by forgotmypw17 on Wednesday July 01, 2020 @06:45PM (#23707717)
>About the Ctrl-s thing, maybe it's specific to windows, I use libre office on linux and have for years and Ctrl-s on a new document has always brought up the save-as dialog for me.

I'm using LibreOffice on Fedora, and I've used it on Mac and Windows too.

Yes, it brings up the Save As dialog, but the name is not pre-filled with an intelligent choice.

In Office 97, it typically pre-fills the suggested file name with the first line of the file. If that's not available, it tries to think of something else.

But never does it ever suggest a file name that is either invalid or would overwrite an existing file.

It ensures that the suggested filename is not too long, and doesn't contain unacceptable characters.

If there's already a file with the first name it thinks of, it appends a number, so that you don't accidentally overwrite an existing file.

In case you don't care about the filename, and just want to save the document, you are never forced to change the default, and it always works.

Many of my files begin with "I'm ..." and sometimes the best that Word 97 can come up with is "I7.doc".

Well, that "I7.doc" is a whole lot better than LibreOffice's "Untitled 1", which will overwrite the last "Untitled 1" it already had me save.

After how many years of development is LibreOffice still not smart enough to do any of these things?

Surely, LibreOffice today has been in development longer and by more people than Office 97 had been in '97?

What is the cause of this unfortunate circumstance?

Re:New Mac ransomware spreading through piracy by grawprog on Wednesday July 01, 2020 @08:22PM (#23708496)
>Yes, it brings up the Save As dialog, but the name is not pre-filled with an intelligent choice.

No, but it's usually helpfully preselected so a single keystroke, changes the name.

>Many of my files begin with "I'm ..." and sometimes the best that Word 97 can come up with is "I7.doc".

>Well, that "I7.doc" is a whole lot better than LibreOffice's "Untitled 1", which will overwrite the last "Untitled 1" it already had me save.

Personally, I dislike that feature of word because typically I do not want my files saved by the first thing i've written and yes I care about file names and take the time to name things sensibly and even put them in related folders.

Also, it should automatically detect an untitled1 and enumerate to untitled2 if untitled1 exists, again this is how it's always worked for me. So your file overwriting example seems a tad dubious to me.

I have to be honest, of all the gripes i've heard, this one's just a bit ridiculous. The save feature works exactly as it should. A program should allow me to choose a name for a file or choose a reasonable generic default, not decide what it thinks I want.

If I see an untitled1.doc around, I know I forgot to rename a file and I investigate, if I see I7.doc or a my name is.doc, I dunno what the hell it is. Maybe it's something I forgot to rename, maybe it's something I wrote before and forgot about, who knows?

Re:New Mac ransomware spreading through piracy by forgotmypw17 on Thursday July 02, 2020 @01:45PM (#23715904)
>Personally, I dislike that feature of word because typically I do not want my files saved by the first thing i've written and yes I care about file names and take the time to name things sensibly and even put them in related folders.

Then you can rename it?

>Also, it should automatically detect an untitled1 and enumerate to untitled2 if untitled1 exists, again this is how it's always worked for me. So your file overwriting example seems a tad dubious to me.

But it doesn't! That's what my complaint is about! Do you think I'm just making it up?

>I have to be honest, of all the gripes i've heard, this one's just a bit ridiculous. The save feature works exactly as it should. A program should allow me to choose a name for a file or choose a reasonable generic default, not decide what it thinks I want.

To me, this reads as, "I read your text, but I don't think your problem is real, because I think it should work differently."

I think you should do a deep examination into how you relate and communicate with people, because you spent this whole thread invalidating what I'm saying and telling me the problems I'm describing in detail are not real problems.

You've given me the impression of being an insensitive and careless person.

Re:New Mac ransomware spreading through piracy by notkaiho on Wednesday July 01, 2020 @02:49AM (#23698514)
And yet I've seen more than one thread comment say the humanities and media literacy are "not worth teaching"
Re:New Mac ransomware spreading through piracy by ImprovedSilence on Tuesday June 30, 2020 @10:57PM (#23697296)
yeah but their spreadsheet blows the pants off of whatever garbage macOS trys to pass off as an Excel replacement.
Re:New Mac ransomware spreading through piracy by stOneskull on Wednesday July 01, 2020 @06:25AM (#23699915)
the libreoffice spreadsheet is very good. i think it's psychic sometimes, knowing what i want to do.
Re:New Mac ransomware spreading through piracy by karoofish on Wednesday July 01, 2020 @03:25AM (#23698753)
macOS, being an operating system does not have spreadsheet. If you looking for a spreadsheet on macOS, Microsoft Office is available and provides Excel.
Re:New Mac ransomware spreading through piracy by AnthonyMouse on Wednesday July 01, 2020 @04:23AM (#23699183)
Re:New Mac ransomware spreading through piracy by vetinari on Wednesday July 01, 2020 @07:44AM (#23700378)
To be fair, Numbers/Pages/Keynote, as well as Garageband and iMovie are not a part of macOS. Yes, they come preinstalled with a new Mac, but if you do a clean installaction, they will be missing. You will have to reinstall them from App Store.
Re:New Mac ransomware spreading through piracy by jacobolus on Wednesday July 01, 2020 @02:20AM (#23698343)
And sadly, both Word 98 and Word 2019 (any platform) are still far behind Word 5.1 (Mac; 1992).
Re:New Mac ransomware spreading through piracy by phre4k on Tuesday June 30, 2020 @08:47PM (#23696530)
The tabbed ribbons are called Notebookbar in LibreOffice.
Re:New Mac ransomware spreading through piracy by grawprog on Tuesday June 30, 2020 @09:00PM (#23696623)
Notebookbar?? Now that's a silly name isn't it? Not at all catchy like 'ribbon'. Ribbon just rolls off your tongue. Just how am I supposed to explain to grandma what a notebookbar is??

I mean just look at these instructions

https://help.libreoffice.org/Common/Using_the_notebook_bar/v...

I can't make heads or tails of this...first I gotta switch layouts?? Then I gotta go to view and turn notebook bar mode on? Then i've gotta choose between tabbed, contextual groups or contextual single bar...nope no siree this is why piracy's just not for me.

These knockoffs are always so complicated, why can't they be simple like the official certified word? And shiny and jazzy lookin'? I know ya get what ya pay for, but how hard would it be to slap some bezels and rounded edges on there? Maybe some 3d transitions?

Re:New Mac ransomware spreading through piracy by rbrtl on Wednesday July 01, 2020 @05:04AM (#23699420)
Well it's open source, so if there are features you want you could contribute to the project.

And being open source, the project won't have the same luxuries in terms of user-testing and iterative improvement of things as trivial as a 'shiny' UI. Again, if you have the time, you could help them out.

Re:New Mac ransomware spreading through piracy by grawprog on Wednesday July 01, 2020 @10:06AM (#23701441)
Apparently my comments were just too believable....yes siree. Guess I shoulda known better.
Re:New Mac ransomware spreading through piracy by rbrtl on Thursday July 02, 2020 @05:42AM (#23711526)
Heh dammit. Dragged under by a troll.

Ah well: play stupid games, win stupid prizes.

Re:New Mac ransomware spreading through piracy by AnthonyMouse on Tuesday June 30, 2020 @07:37PM (#23696095)
It's because they distribute the versions that work offline instead of uploading all your personal information to the vendors. The free software distributors are very privacy conscious.
Re:New Mac ransomware spreading through piracy by somehnguy on Tuesday June 30, 2020 @08:13PM (#23696327)
How does being offline have absolutely anything to do with their terrible UI?
Re:New Mac ransomware spreading through piracy by AnthonyMouse on Tuesday June 30, 2020 @10:19PM (#23697031)
I know we're having a laugh directing the would-be pirates to where they can get "free software" from, but you already know the answer to your question, right?

Online proprietary software sells you to advertisers for money, or locks you into an ecosystem so they can sell you to other third parties, and they use some of that money to fund development.

With free software you either have to improve it yourself (the source code is on the internet) or give them money so they can hire someone to do it (they all have donation links). If you're dissatisfied with the user interface, have you tried doing the things that cause it to be improved?

Re:New Mac ransomware spreading through piracy by XMPPwocky on Wednesday July 01, 2020 @03:19AM (#23698707)
If you're unhappy that people don't like free software, have you tried donating more money and contributing more to those projects so that they'll improve and people will like them more?
Re:New Mac ransomware spreading through piracy by AnthonyMouse on Wednesday July 01, 2020 @04:16AM (#23699132)
Yes. The overall result was for the software to improve to such an extent that it now overwhelmingly dominates the markets for servers, embedded devices and utility programs (e.g. zip, encryption, file transfer) and is the basis for the most commonly used smartphone operating system and browser. It has also caused alternatives to Office and Photoshop, while not perfect, to exist.

Rome wasn't built in a day, as they say.

Re:New Mac ransomware spreading through piracy by somehnguy on Wednesday July 01, 2020 @04:20PM (#23706085)
Again, this has nothing to do with software being always online or not.

Great looking software existed long before the rise of everything being always online.

Re:New Mac ransomware spreading through piracy by AnthonyMouse on Wednesday July 01, 2020 @06:12PM (#23707401)
> Again, this has nothing to do with software being always online or not.

Only if by "nothing to do with" you ignore that it is the method by which development is funded.

> Great looking software existed long before the rise of everything being always online.

At which time you had to pay a lot of money for it. If everybody gave the same money to free software developers, they'd have plenty of resources to build interfaces that are more to your satisfaction.

Re:New Mac ransomware spreading through piracy by somehnguy on Thursday July 02, 2020 @01:44AM (#23710366)
Your entire premise is flawed imo.

>If everybody gave the same money to free software developers, they'd have plenty of resources to build interfaces that are more to your satisfaction.

You're just arguing to pay for software, but in a more roundabout way. And again, great looking software existed far before the popularity rise in always-online.

Re:New Mac ransomware spreading through piracy by ferzul on Wednesday July 01, 2020 @02:32AM (#23698416)
the why do i have to “download” my document in libreoffice if i want to keep it?
Re:New Mac ransomware spreading through piracy by RealStickman_ on Wednesday July 01, 2020 @02:45AM (#23698487)
Wouldn't getfedora.org be a better address than Debian as they don't include any proprietary software in their default repositories?
Re:New Mac ransomware spreading through piracy by rovr138 on Wednesday July 01, 2020 @03:04AM (#23698597)
The main issue being discussed here has to do with proprietary software...
Re:New Mac ransomware spreading through piracy by RealStickman_ on Wednesday July 01, 2020 @07:36AM (#23700332)
I took the "free software" to mean free as in freedom and not free as in beer. I think this is what the parent meant by mentioning various FOSS projects.
Re:New Mac ransomware spreading through piracy by 0000000000100 on Tuesday June 30, 2020 @11:05PM (#23697338)
This list is a pretty good place to start. https://github.com/Igglybuff/awesome-piracy
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:28AM (#23699205)
There’s an awesome list for everything these days…
Re:New Mac ransomware spreading through piracy by penagwin on Wednesday July 01, 2020 @01:10AM (#23697955)
I recommend the Github link that 100 gave, and also the various related subreddits.

You're unlikely to get a direct answer because... Well you don't talk about fight club. But if you watch the subreddits a bit you'll get a much better idea of where to start, how to get invites to private trackers, etc.

Re:New Mac ransomware spreading through piracy by pjmlp on Wednesday July 01, 2020 @02:54AM (#23698544)
Reputable piracy site, the irony, so now we also have digital pirates, buccaneers, and corsairs.
Re:New Mac ransomware spreading through piracy by cosmodisk on Wednesday July 01, 2020 @06:14AM (#23699869)
Not much of an irony as far as I can see. There are a lot of people out there who are willing to break some rules but not others and that applies to piracy sites as well. Some years ago some of the websites were really active on this and crappy torrents used to be downvoted to oblivion.
Re:New Mac ransomware spreading through piracy by HenryBemis on Wednesday July 01, 2020 @04:07AM (#23699070)
>..now..

I don't remember when PirateBay or other Warez sites first appeared, but they have been around for at least 20 years. I remember people were even using Blogspot to promote their wares/z with links to RG, FS, DF, etc.

I know and trust(?) the results of Virustotal, and I tell all my clients that when in doubt, drop that bad (?) boy in VT and let it scan it.

Re:New Mac ransomware spreading through piracy by parksy on Wednesday July 01, 2020 @06:02AM (#23699783)
Sorry if this seems tangential and anecdotal, it's just an interesting part of home computing history and I lived through a bit of it growing up in the 80s and 90s.

Way back when, we had usenet, telnet and gopher, and local BBS's would sometimes have a private stash of cough shareware.

Prior to usenet etc being easily accessible to people outside of educational institutions (the majority of the 80s), it was more common to share programs via "sneakernet" on floppy disk as well, these would often contain a text document that would say what other programs were available and some clues on how to obtain them, but usually it was just a viral spread among friends and acquaintances.

Cracked software would often include intro screens and trainers, the intros sometimes included animations and catchy music to showcase the elite skills of the cracking crew and build reputation, and often they improved the software so it would load more quickly, unlock hidden functionality, or give you infinite lives etc. This spawned the DemoScene, which still exists today unrelated to piracy but historically rooted in the 80s cracking scene.

Here's a compilation of crack intros from 86 to 89 - https://www.youtube.com/watch?v=SFqBkSJOYOQ (skip to 11:40 and you'll see an advert for "cleveland cracking service" with a phone number for an example of how stuff got around before internet was common)

Essentially even back in the 80s and 90s there were the serious crews trying to demonstrate their awesomeness and generate rep, and dumb kids like me naively sharing "free stuff" we were given on disks because we had no idea what things like copyright and licensing even were, let alone stopping to consider whether the stuff we were loading onto our machines had any malicious intentions.

So I'd say that the idea of building reputation and trust in regards to piracy "crews" has a long history going back even further than 20 years, well before the web was common in homes, and I'm at least aware of early to mid 80s cracktro / intro scene materials so perhaps ~35-40 years is a good guess?

Re:New Mac ransomware spreading through piracy by aj3 on Wednesday July 01, 2020 @07:17AM (#23700217)
> I tell all my clients that when in doubt, drop that bad (?) boy in VT and let it scan it.

Who are your clients? Are you aware that everything that's uploaded to VT becomes public? As in full file contents, not just metadata & scan results. There's no harm in uploading .exe's there, but you should at least warn them not to upload private documents.

Also, VT results are trash for anything new so "all green" doesn't necessarily mean you're safe to run stuff if it also happens to be the first time VT has seen the file. It's not even the VT's fault, AV's suck and everybody knows it. The value of VT is that once something gets detected people can go back in time and look for other incidents that had flown under the radar previously.

Re:New Mac ransomware spreading through piracy by HenryBemis on Wednesday July 01, 2020 @12:25PM (#23703276)
Thank you for writing this (for all to see). I suggest this for "funky" files, for files of unknown/uncertain origin. Not every company has a strong IT/Sec team, with dedicated process and awareness training so that staff can forward funky emails to someone. Also, many companies rely on little or no spam filtering (if Gmail catches it, well done.. if not.. grace for impact!)
Re:New Mac ransomware spreading through piracy by pjmlp on Wednesday July 01, 2020 @04:18AM (#23699149)
Yes they have, and I never trusted any of them.

Not running pirate software is the only valid path for security.

Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:26AM (#23699194)
Sometimes I trust pirated software more than the original thing I was trying to install ;)
Re:New Mac ransomware spreading through piracy by pjmlp on Wednesday July 01, 2020 @04:33AM (#23699240)
Depends, after all pirate software >= original contents.
Re:New Mac ransomware spreading through piracy by koheripbal on Wednesday July 01, 2020 @02:39PM (#23704888)
> The more reputable ones actively remove spam and malware...

...that aren't there own.

Re:New Mac ransomware spreading through piracy by csydas on Tuesday June 30, 2020 @07:17PM (#23695927)
You've never been a part of a trusted community before?

rutracker isn't some fly-by-night random tracker, it's a well established site in Russia, and the admins have been extremely communicative with users throughout virtually every governmental upset.

To add some context, try to imagine if the classic western trackers had prominent links like this, for example, what.cd.

Looking at the thread, the early posts correctly identified it as malware before the malwarebytes report, and even noted that the link itself violated the application post rules.

It's good for malwarebytes to report that this exists, but they're focusing on the wrong parts, imho.

The hash files to identify the affected file should have been the first part, then the explanation. A bit of google translate would have shown that already, rutracker users are calling to delete the thread.

Re:New Mac ransomware spreading through piracy by userbinator on Tuesday June 30, 2020 @07:37PM (#23696088)
but they're focusing on the wrong parts, imho

AV/anti-"malware" has always meant "pro-corporations/pro-copyright/pro-establishment", ever since they started detecting completely clean keygens and cracks as well as "hacking tools" and demoscene productions.

There is sometimes truth, like this article, but there is also a lot of FUD --- IMHO to herd users into giving up personal discretion and instead adopting centralised trust.

Re:New Mac ransomware spreading through piracy by boomlinde on Tuesday June 30, 2020 @08:09PM (#23696303)
> they started detecting completely clean keygens and cracks as well as "hacking tools" and demoscene productions.

AFAIK this is usually a side effect of self-unpacking compressed executables, as produced by EXE packers. They have a property that's been useful to malware authors: they obfuscate the code. To de-obfuscate, you have to unpack, which some anti-virus vendors actually do for executables produced by common compression tools like UPX. For certain types of demoscene productions, however, a popular tool like UPX won't do if you can shave another few bytes using a more obscure packer that AV software are unlikely to have unpackers for. Once malware authors start using those same packers you'll get false positives based on signatures that are likely common to all software using them.

Re:New Mac ransomware spreading through piracy by yjftsjthsd-h on Tuesday June 30, 2020 @10:55PM (#23697284)
No, because they're flagged as "hacking tools" explicitly -they're not being misidentified.
Re:New Mac ransomware spreading through piracy by AYBABTME on Wednesday July 01, 2020 @12:24AM (#23697726)
How do AV software identify these "signatures"? Does it look for known strings, or does it do something smarter with some sort of behavior matching?
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:29AM (#23699211)
Usually both. They check known malware signatures and also look for suspicious behavior.
Re:New Mac ransomware spreading through piracy by arkh on Wednesday July 01, 2020 @04:35AM (#23699254)
> what.cd

Little angel gone too soon.

Re:New Mac ransomware spreading through piracy by isatty on Wednesday July 01, 2020 @05:51AM (#23699717)
Red is pretty good.
Re:New Mac ransomware spreading through piracy by fredoliveira on Wednesday July 01, 2020 @05:59AM (#23699765)
The best thing about redacted (and what, and oink before it) for me really is access to people with amazing musical taste. Most music these days is accessible for free in one way or another, but the curation in some of the collages is truly priceless.
Re:New Mac ransomware spreading through piracy by golergka on Tuesday June 30, 2020 @07:44PM (#23696141)
Rutracker, or torrents.ru, has been full of malware-infected trash for the last 15 years. It's anything but a trusted community
Re:New Mac ransomware spreading through piracy by lovelyviking on Wednesday July 01, 2020 @04:32AM (#23699235)
>I don’t understand how people dare to run executables downloaded from a pirate site...

But do you understand people who dare to run executables from 'proper-company' site? It's closed source, you have no idea what you are running, isn't it? As long as it's not free software in terms of FSF there is not guarantee what so ever that it's not harmful or even worse intentionally harmful.

How about this one from SONY, that didn't even ask user to run? https://en.wikipedia.org/wiki/Sony_BMG_copy_protection_rootk...

or this one Amazon remotely deletes book from kindle: https://www.nytimes.com/2009/07/18/technology/companies/18am...

Re:New Mac ransomware spreading through piracy by black_puppydog on Wednesday July 01, 2020 @05:48AM (#23699700)
With companies, there's an incentive structure that usually makes it pretty obvious whether they have an interest to do really shady stuff on your PC. For "proper" companies that have established customer bases and a legit revenue model, they have an incentive to not screw everyone over and lose their trust. That's just good management. Of course, management often screws this up and then we get (justifiably) outraged HN posts.

For pirated software the incentive structures are also clear, and usually point towards "yeah if given the chance they'll take everything from my HDD and make a run for it."

I'm all for FOSS everything, but running a company-distributed binaries is very different from pirated ones, and I agree with GP that it baffles me someone would do the latter.

Re:New Mac ransomware spreading through piracy by lovelyviking on Wednesday July 01, 2020 @07:46AM (#23700387)
>For "proper" companies that have established customer bases and a legit revenue model, they have an incentive to not screw everyone over and lose their trust.

It also depends on what company means by "not screw everyone over" Right now many companies consider practices as 'OK' while I am coming from the times when most of those modern activities considered to be virus or malware. So for me it doesn't really matter whether you have malware installed by a virus or it's hidden deeply in EULA which you can't reject partially anyway.

Re:New Mac ransomware spreading through piracy by black_puppydog on Wednesday July 01, 2020 @08:00AM (#23700452)
Oh I'm not trying to defend these practices in the least. But at least there is some mechanism (public outrage) there to make them think about it. That these mechanisms seem to fail and we need proper regulation is a different matter. Also in a lot of cases it's not really clear which tangible monetary benefit companies get from spying on their customers. Many cases seem to be managerial paranoia (Just in case the customers pirate!) or "because we can."

Pirating and re-packaging software for torrent is also a non-negligible amount of work, and with no revenue stream besides bundling the apps with malware. So it's quite a different incentive structure still.

Re:New Mac ransomware spreading through piracy by enzo1982 on Wednesday July 01, 2020 @05:46AM (#23699690)
> But do you understand people who dare to run executables from 'proper-company' site? It's closed source, you have no idea what you are running, isn't it? As long as it's not free software in terms of FSF there is not guarantee what so ever that it's not harmful or even worse intentionally harmful.

You'll have to trust somebody at some point.

Do you trust the company who designed your Ethernet chip? Do you trust the person who wrote the firmware for it? If not, go and design your own network chip. Otherwise, there's no guarantee it won't spy on you.

You'll also want to write your own compiler that you'll then use to build the operating system you intend to run. You won't just go download some Linux .iso to install, would you? After all, there's no guarantee it's not been manipulated by those who offer it on their website.

Re:New Mac ransomware spreading through piracy by lovelyviking on Wednesday July 01, 2020 @06:14AM (#23699865)
>You'll have to trust somebody at some point.

No, I do not have to. I can choose to, but I don't have to! That is the core of the issue.If I 'have to' then I don't. I prefer checking and facts, not delusions.

>Do you trust the company who designed your Ethernet chip?

No, I don't and we shouldn't. I evaluate chances and we should track network activity with diff. hardware on diff. chipsets from diff. manufacturers.

>Do you trust the person who wrote the firmware for it?

No, I don't and we shouldn't as it's insane to do so.

>If not, go and design your own network chip.

There are other means to overcome this: encryption. But yes, you right, we should make open source network chip. Agree. I certainly plan to design it.

>Otherwise, there's no guarantee it won't spy on you. That is correct, I agree with you.

>You'll also want to write your own compiler.

Yes, that is correct. I want and I am writing it right now. There is also an option of GNU c/c++ compiler available (GCC) https://gcc.gnu.org

>that you'll then use to build the operating system you intend to run.

This is how you build a proper GNU/Linux system worth some degree of your trust.

>You won't just go download some Linux .iso to install, would you? After all, there's no guarantee it's not been manipulated by those who offer it on their website.

Exactly. Or it can be modified on the way, while you download it. For the later you can check hash sums published by a site who respects user freedom and cares about own reputation.

>You'll have to trust somebody at some point.

Again I do not have to, but I can choose to trust with some degree to Richard Stallman and people sharing his views. https://www.youtube.com/watch?v=n9YDz-Iwgyw

I have some trouble trusting FSF since he was removed from the position due to false accusations for saying (!) just saying things, which he actually didn't say if you read carefully. Speak about respect of freedom of speech.

https://www.youtube.com/watch?v=7UbQ1kc1vQU

To trust the system we should have trust worthy components with open sourced designs starting from CPU and every chip installed and ending with each software running. That is the only way!

Re:New Mac ransomware spreading through piracy by raesene9 on Wednesday July 01, 2020 @05:34AM (#23699630)
There's no guarantees what you're getting even if it's open source, unless you read and understand the source code :)

The set of computer users who a) have the knowledge to do security code review and b) have the time to review the programs they run is, I would expect, fairly small.

Re:New Mac ransomware spreading through piracy by maayank on Wednesday July 01, 2020 @05:49AM (#23699709)
> There's no guarantees what you're getting even if it's open source, unless you read and understand the source code :)

Obligatory reference to Reflections on trusting trust [1]

[1] https://dl.acm.org/doi/10.1145/358198.358210

Re:New Mac ransomware spreading through piracy by lovelyviking on Wednesday July 01, 2020 @05:52AM (#23699723)
>The set of computer users who a) have the knowledge to do security code review and b) have the time to review the programs they run is, I would expect, fairly small.

Even a small number of those who understands can make a huge noise, because if comment is well grounded, it spreads exponentially by people who do not need to understand all the details.

And frankly how much those who understand you really need for each project? The thing is, if you are worried you can always look, which is not the case if you have nowhere to look.

Also expert is not always required just to see there is no brutal obvious harm intent, which covers a lot of cases

Re:New Mac ransomware spreading through piracy by raesene9 on Wednesday July 01, 2020 @08:21AM (#23700575)
There are a number of cases, even with just bugs, which won't be deliberately hidden (unlike malicious software) where critical security issues have gone unnoticed in major open source software packages for year (e.g. shellshock).

Then you have the fact that if it's deliberately malicious things can be hidden such that even experienced code reviewers (who are not plentiful) could be fooled. A good example of this is the underhanded C contest http://www.underhanded-c.org/_page_id_2.html .

Sure an open source user may catch malicious behaviour, but then security researchers find malicious behaviour in closed source software pretty regularly via reverse engineering or binary analysis.

This isn't an anti-open source thing, it's a reflection that open source often isn't much of a signal of safety, unless further work has been done and continues to be done on a regular basis.

Re:New Mac ransomware spreading through piracy by hengheng on Wednesday July 01, 2020 @05:38AM (#23699646)
Still a reputation to lose, generally speaking.

I have also never seen anybody who made this argument verify their free software by looking at sources before compiling.

Re:New Mac ransomware spreading through piracy by cpach on Wednesday July 01, 2020 @05:52AM (#23699721)
Exactly. Even if I would use only 100% FOSS software, I would not have the time to read all the source code of the whole stack, from the device drivers to the kernel and up to the source code of the web browser, etc etc.
Re:New Mac ransomware spreading through piracy by gjs278 on Wednesday July 01, 2020 @05:52AM (#23699724)
and neither of those are ransomware. do you understand the difference?
Re:New Mac ransomware spreading through piracy by lovelyviking on Wednesday July 01, 2020 @06:44AM (#23700027)
>do you understand the difference?

Let's take a File System for a second as example. If you wrote your personal data on some disk drive and then to read this drive you need let's say Mac/Win because it's a closed format. And Mac/Win cost money. How it differs from ransomware then? Sure you have more time to decide, usually more than 3 days and it costs a bit less, but is it much of a difference there? Probaly a choice to start using it, but is it really a choice? In many cases it's not really. So back to your point, I understand it, but do you?

Re:New Mac ransomware spreading through piracy by qppo on Tuesday June 30, 2020 @07:02PM (#23695798)
It's how kids get into multimedia content creation using real tools without paying real money
Re:New Mac ransomware spreading through piracy by lintroller on Tuesday June 30, 2020 @07:11PM (#23695884)
It's how I did. Now I'm a professional frontend developer with adequate Adobe skills and a license paid for by the company that frequently come in handy on the job.
Re:New Mac ransomware spreading through piracy by userbinator on Tuesday June 30, 2020 @07:38PM (#23696102)
license paid for by the company that frequently come in handy on the job.

...and now you know why Adobe products are so easy to pirate. Young pirates turn into loyal product users and customers.

Re:New Mac ransomware spreading through piracy by the_af on Tuesday June 30, 2020 @08:10PM (#23696307)
Didn't this also use to be the case with MS Windows and MS Office? I always thought they were so easy to crack, and Microsoft was so prone to turn a blind eye to pirate copies at home, because this led to employees familiar with their products at the office. And they did go after pirated software at the office.
Re:New Mac ransomware spreading through piracy by phre4k on Tuesday June 30, 2020 @08:50PM (#23696561)
It's almost as if pirating software for home users doesn't have the negative impact the big corporations would make you believe.
Re:New Mac ransomware spreading through piracy by user5994461 on Wednesday July 01, 2020 @07:05AM (#23700144)
Microsoft gives everything for free to students, except office.

Check with your university. This shall includes hundreds of software, all editions of Windows both 32 bits and 64bits, as well as all editions of Visual Studio Ultimate, plus databases and other tools.

Re:New Mac ransomware spreading through piracy by the_af on Wednesday July 01, 2020 @08:56AM (#23700801)
Yes, in later years, through my university this turned out to be the case. But it wasn't the case at first in my country.
Re:New Mac ransomware spreading through piracy by mschuster91 on Wednesday July 01, 2020 @05:40AM (#23699656)
They were easy to pirate up until CS6, nothing more than a keygen (or pregenerated key) and a couple blocks in /etc/hosts.

After that they really cracked down on piracy, and at the same time offer the CC subscription decently cheap (50$ a month) that honestly the risk of malware isn't worth it any more.

Re:New Mac ransomware spreading through piracy by user5994461 on Wednesday July 01, 2020 @07:08AM (#23700159)
So one can pay $700 a year to Adobe or pay 1-2 month of student rent for that year. I'd say Adobe is pushing hard for piracy trying to get blood from a stone (students).
Re:New Mac ransomware spreading through piracy by dylan604 on Wednesday July 01, 2020 @11:02AM (#23702133)
$50/month is the full price for the most complete bundle. Adobe has a student price at a lower rate that I can't be bothered to look up just as you couldn't be bother to look up before making your comment.
Re:New Mac ransomware spreading through piracy by mschuster91 on Wednesday July 01, 2020 @12:27PM (#23703289)
And even the 50$ - that's about the price of getting wasted once a month which most students can afford. The key difference between CS and CC is that you don't have to up-front hundreds/thousands of dollars.
Re:New Mac ransomware spreading through piracy by dmix on Tuesday June 30, 2020 @07:45PM (#23696147)
More like they eventually join mid-size plus companies which Adobe tracks down to make them pay for their photoshop (if they detect it on a company network they will reach out). Or they simply just pay for it because they can and/or are professional/law abiding people.

Adobe doesn't spend copyright enforcement time on individuals much.

Re:New Mac ransomware spreading through piracy by bredren on Tuesday June 30, 2020 @07:32PM (#23696042)
Me too. I distinctly remember the warez group editing the startup image of PS 6, which had the code name Venus in Furs. Apparently that was 20 years ago!

Anyhow, I know that much of my early software license transgressions resulted in actual software licenses.

Re:New Mac ransomware spreading through piracy by 488643689 on Wednesday July 01, 2020 @05:06AM (#23699438)
This is a hidden downside of having proprietary defacto monopolies in tech. As long as the Adobe suite is the default in digital content creation, piracy is the default gateway to that profession. I don't care about Adobe's loss, as they pretty much encourage the status quo, I do however care about all the people risking their digital life's integrity for this. Since it's "this is how you do it", many non-tech people are not even aware of the potential fallout. It's the same for even more problematic scenarios, e.g. students using cracked Matlab, SPSS, ... executables to crunch real study data at home.

Yes, digital responsibility is ignored by those using cracked software, but really you can't ignore factual constraints and the economic situation, when talking about who's to blame.

Re:New Mac ransomware spreading through piracy by dylan604 on Tuesday June 30, 2020 @07:36PM (#23696087)
The grandparents used alt.binary.* to get software
Re:New Mac ransomware spreading through piracy by ogre_codes on Tuesday June 30, 2020 @07:54PM (#23696201)
Ouch... a little too close to the truth here.
Re:New Mac ransomware spreading through piracy by dnh44 on Tuesday June 30, 2020 @10:08PM (#23696957)
That’s still going strong actually and a really convenient way to download things.
Re:New Mac ransomware spreading through piracy by rimliu on Wednesday July 01, 2020 @03:37AM (#23698856)
It was really true back in the day, not so now. You can get e.g. Davinci Resolve for free and it as real of a tool as it gets.
Re:New Mac ransomware spreading through piracy by coldtea on Wednesday July 01, 2020 @02:50AM (#23698525)
Beats paying for the software they can't afford, and it causes no issue 99% of the time...

It's a cost/benefit analysis... Billions of people in the developing world rely on pirated software, for one...

Heck, even in large parts of Europe, at some point there would be much fewer graphic designers today e.g. if they couldn't pirate Photoshop when they were young and non-pro (and no, Gimp wouldn't be of much use, they want to learn on the industry standard)...

Re:New Mac ransomware spreading through piracy by usrusr on Wednesday July 01, 2020 @05:27AM (#23699585)
> Billions of people in the developing world rely on pirated software, for one...

And it shows in their systems. I know a few people with extensive travel experience in Africa and most of them, despite being decidedly non-technical, came back with essentially the same story: "if you absolutely have to bring a laptop, don't ever connect it to something that has a data line"

Re:New Mac ransomware spreading through piracy by GekkePrutser on Wednesday July 01, 2020 @04:07AM (#23699068)
I agree Creative Suite is way too expensive (at one point it was 3000 euros!)

But for students Adobe was basically giving it away :) I remember getting a CD for 15 guilders at the time at the university. Which was around 5 euros.

Re:New Mac ransomware spreading through piracy by jonathanstrange on Wednesday July 01, 2020 @04:35AM (#23699258)
Back in the days when I couldn't afford proprietary software and didn't use Linux yet, I often downloaded torrents even for free software because the download was 20 times faster and you didn't have to fill out web forms and give away one of your throw-away email addresses to get the content. The crackers also often fixed bugs the developers refused to fix and removed annoying nag screens.

To be honest, when I had to upgrade my Windows machine last year, I really regretted the fact that I've gone fully legit with VST plugins. It took me more than a week to deregister and reregister all the horrible proprietary DRM schemes those companies are using. That would have taken less than a day if I had used cracked versions.

Re:New Mac ransomware spreading through piracy by usrusr on Wednesday July 01, 2020 @05:04AM (#23699422)
VST are particularly nasty for a reason though, because when they have a signature sound widespread usage by freeloaders will actively ruin that sound for those who paid. Exclusivity is a feature, the inverse of network effect.

Is there something like a "steam for VST"? Maybe it should exist, to ease the DRM pain for legitimate customers.

Re:New Mac ransomware spreading through piracy by coldtea on Wednesday July 01, 2020 @08:23AM (#23700585)
>VST are particularly nasty for a reason though, because when they have a signature sound widespread usage by freeloaders will actively ruin that sound for those who paid.

Nobody really cares if you use the same presets. There were countless top-10 hits with the same handful of DX7, M1, JV-1080, etc presets.

Nowadays, there are so many VSTs and they have so many presets, that nobody can keep track anyway, even if you do use their presets.

And of course you can always program your own patches on most VSTs, alter presets with layers of effects, etc...

Re:New Mac ransomware spreading through piracy by jonathanstrange on Wednesday July 01, 2020 @09:10AM (#23700921)
That's definitely something studios all over the world would greatly benefit from. Right now, they're just trying to never ever change the machine that runs those plugins unless they absolutely must.

Although there are a few larger DRM "alliances", for some reason manufacturers have not yet been able to agree on a common DRM and package management system. Currently every larger company and a number of smaller ones want to push their own plugin management system.

VSTs are a mess anyway, there are only few hosts who are able to scan all of them correctly without crashing (and these do it by separating the process that crashes from the rest of the host).

Re:New Mac ransomware spreading through piracy by mnjn on Wednesday July 01, 2020 @05:46AM (#23699687)
Kind of! Check out Splice[0]

[0] https://splice.com/

Re:New Mac ransomware spreading through piracy by mahathu on Wednesday July 01, 2020 @06:26AM (#23699925)
I doubt 99% of casual listeners would recognize a VST in a song they like or even know what a VST is. I can kinda see where you're coming from, but I wouldn't go as far as to say the sound gets ruined (or even devalued) for those who paid, just because more users use a certain effect.
Re:New Mac ransomware spreading through piracy by baddox on Tuesday June 30, 2020 @07:18PM (#23695935)
I don't pirate much any more, but in high school and college I was very much a digital hoarder. I ran plenty of pirated software and from what I remember never had any problems whatsoever with malicious software (that I was aware of). Of course you need to know what you're doing, same as downloading software from anywhere else.
Re:New Mac ransomware spreading through piracy by Polylactic_acid on Tuesday June 30, 2020 @07:33PM (#23696059)
> Of course you need to know what you're doing

No one knows what they are doing. Unless you are decompiling and reverse engineering the whole thing you are mostly just blindly trusting its safe. Even on trusted sites people share stuff from other sites not knowing its infected.

Re:New Mac ransomware spreading through piracy by boomlinde on Tuesday June 30, 2020 @08:14PM (#23696337)
There's something to be said for the sites that only shared scene releases from groups with a reputation to protect. Maybe in the future, trusted groups can cryptographically sign their releases to avoid tampering and minimize the amount of trust necessary.
Re:New Mac ransomware spreading through piracy by mfjordvald on Wednesday July 01, 2020 @02:23PM (#23704715)
They have been for decades! Most scene releases that are packed will include an SFV file that contains the checksums of each of the package files so that you can check the file integrity.

Obviously those can be repacked and faked so you'd have to check multiple sources to ensure you get a genuine release, but yeah the scene groups are as usual way ahead of everyone else.

Re:New Mac ransomware spreading through piracy by boomlinde on Thursday July 02, 2020 @05:15AM (#23711391)
I meant signatures, not checksums. A signature chain would avoid the repackaging problem if the signer's public key was distributed out-of-band. Groups and distributors alike could add their own signatures to create multiple possible trust boundaries.

I think the scene groups are a traditional bunch that in some respects are years behind because of it. I remember in maybe 2005 I'd still download releases that were split into floppy sized RAR files. Possibly, this tradition carried on for so long because the scene was so keen to shame groups that didn't package like everyone else. I don't know how it is now but I'm hoping they got over splitting releases.

Re:New Mac ransomware spreading through piracy by the_af on Tuesday June 30, 2020 @08:14PM (#23696338)
My guess is that the OP means knowing where you download from. In a way it's like the fabled "web of trust". Reputable warez groups didn't distribute software with viruses.

Like the OP, back in the day I used to have plenty of pirated software (mostly games) and never had a problem with viruses (at least, not that I knew or had any noticeable effects). The threat complexity is probably way worse these days and I wouldn't risk it. Plus, of course, I support games by paying for them :)

Re:New Mac ransomware spreading through piracy by arsome on Wednesday July 01, 2020 @03:09AM (#23698637)
I mean, the RuTracker thread identified it as malicious long before this report ever came out. A few people running sandbox tools, firewalls and host based IDS tools will catch pretty much all malware quickly based on behavior alone.

I used to swear by Outpost Firewall as it was able to do things like detect applications adding to startup, injecting into other processes, gaining raw disk access, reading your browser profile for passwords, communicating with any unexpected hosts, etc. This is enough to rapidly identify most malware packaged with pirated software immediately. This isn't some advanced targeted attack, it's a script kiddie packing ransomware, password dumpers like iStealer, RATs like DarkComet, etc. The kind of thing these tools are designed to detect.

Re:New Mac ransomware spreading through piracy by skinnymuch on Wednesday July 01, 2020 @05:01AM (#23699411)
I skimmed the blog post. It seems disingenuous to not say the original thread already people saying it is [shitty] malware.

I’m on my phone so can’t search better, but couldn’t find it at rutracker from a quick search. Not sure if it will be available via some archive.

Re:New Mac ransomware spreading through piracy by beagle3 on Wednesday July 01, 2020 @03:44AM (#23698906)
It’s important to realize that’s true also when you’ve paid for the software and got it directly from the source:

Sony has a root kit included, Zoom had a web server that could be exploited (at least) to then on your camera.

That’s just off the top of my head.

Re:New Mac ransomware spreading through piracy by amelius on Wednesday July 01, 2020 @04:13AM (#23699113)
It's also true most of the time when using open source software.
Re:New Mac ransomware spreading through piracy by beagle3 on Wednesday July 01, 2020 @05:49AM (#23699708)
“Most” Depends if you weight by installs, sources, or packages.

I don’t remember malware on Debian, Ubuntu, Fedora or Arch’s repository (put there by maintainers like the examples I gave above, or by a hack). And definitely not Gentoo.

But you are right. The bottom line is, you shouldn’t trust that which you cannot verify; but with open source, you have much more ability to verify (but it’s not a panacea - you run to many lines of code to verify yourself, it’s not clear anyone trustworthy verified it all, and there also the “reflections on trusting trust” argument)

Re:New Mac ransomware spreading through piracy by baddox on Tuesday June 30, 2020 @10:00PM (#23696914)
Sure. All I meant is you cannot just download and install anything and everything without using your judgement.
Re:New Mac ransomware spreading through piracy by Polylactic_acid on Tuesday June 30, 2020 @11:43PM (#23697535)
My judgement says not to execute programs I can't read the source to or hold the publisher legally accountable for.
Re:New Mac ransomware spreading through piracy by skinnymuch on Wednesday July 01, 2020 @05:04AM (#23699423)
But you don’t read the source to most things, no? Nor do most people.

Isn’t that why things like heartbleed took two years before being found out? I presume some people using the vulnerable OpenSSL versions felt similar to you.

Re:New Mac ransomware spreading through piracy by Polylactic_acid on Wednesday July 01, 2020 @07:23PM (#23708029)
Being open source does not ensure software is bug free but its highly highly likely to not be malicious. Usually malware authors don't actually write software, they tack it on to other peoples software or write stuff that doesn't do anything useful at all. Not once have I ever heard of malware making its way in to the debian repos.

The worst I have seen is xscreensaver embedding a message in the code to complain about the old version a year after release.

Re:New Mac ransomware spreading through piracy by sukilot on Tuesday June 30, 2020 @08:24PM (#23696393)
How old are you? Malware is much worse nowadays thanks to Bitcoin monetization and more networked sensitive data.
Re:New Mac ransomware spreading through piracy by jon-wood on Wednesday July 01, 2020 @09:06AM (#23700892)
The world has changed pretty substantially from my teenage days when I'd happily run pirated software. Back in the day viruses and malware would either screw with your computer in amusing and reversible ways (so long as you had a good backup), or spam you with popup ads. Maybe they'd relay spam mail for a while until you noticed your internet connection was useless and run a virus scan.

The damage malware can do now is so much deeper - encrypting all your files, which then gets synchronised out through the tool you were using for backups automatically, before holding them to ransom. Then it turns your light bulbs into DDoS nodes to spread that to people across the internet, and probably you won't notice because you're on a fast enough connection for that to fly under the radar.

Re:New Mac ransomware spreading through piracy by usrusr on Wednesday July 01, 2020 @05:13AM (#23699477)
I don't know when you went through your youthful piracy phase, but I know that when I did, malware was still mostly a shits'n'giggles affair. Worst case you'd get nudged a little closer to that long overdue clean slate reinstall. That landscape has changed dramatically, it's an industry now.
Re:New Mac ransomware spreading through piracy by Karunamon on Tuesday June 30, 2020 @07:16PM (#23695918)
I'd trust the average pirate to not crap all over my computer a lot more than I'd trust the average corporate software release nowadays. The former actually has to care about their reputation...
Re:New Mac ransomware spreading through piracy by WrtCdEvrydy on Tuesday June 30, 2020 @07:00PM (#23695791)
Depends on the site, some repacks are probably nicer than the average DRM dump from ubisoft.
Re:New Mac ransomware spreading through piracy by y2bd on Tuesday June 30, 2020 @07:04PM (#23695820)
Similarly, a cracked version of Photoshop probably installs less junk than a legal version of Photoshop.
Re:New Mac ransomware spreading through piracy by foobiekr on Wednesday July 01, 2020 @01:34AM (#23698087)
It's a wonder it isn't spreading through open source packages.

There is a de-drm tool that I used to use which packages some other open source. For whatever reason, I always assume people who package up software are careful about what they're packaging up, but no, as it turned out this project is not careful at all. It shouldn't have been surprising but it was.

(I ended up writing my own tool. I de-drm on principle; I don't mind buying stuff, I am deeply offended when that stuff vanishes out from under me because of deliberate obsolescence and/or shutdown. Buying DRM-free is not always an option.)

Re:New Mac ransomware spreading through piracy by magicseth on Wednesday July 01, 2020 @01:43AM (#23698136)
Do you have a solution for ebook dedrm? I've been struggling to automate my flow recently!

edit: fix the autocorrect

Re:New Mac ransomware spreading through piracy by foobiekr on Friday July 03, 2020 @02:36AM (#23721580)
Apprentice Elf. Though it appears to be broken on Catalina. I will need to have a look at it, I think, when I get a chance.
Re:New Mac ransomware spreading through piracy by jbverschoor on Wednesday July 01, 2020 @02:17AM (#23698328)
We simply need better sandboxing, and on by default. In a way it’s also usable for normal people.

Mac has the sandbox runner, with a configuration file. However it’s deprecated, and difficult to create.

Also, not even Facebook signs all their apps.

It’s funny, bc everybody is kicking and yelling against the AppStore, and the process. But it’s the only thing protecting everybody from misuse

Re:New Mac ransomware spreading through piracy by skinnymuch on Wednesday July 01, 2020 @05:09AM (#23699463)
iOS App Store? Were there any [major] issues with jailbroken iPhones running cracked apps? Especially before when jailbreaking and pirating iOS apps was a bigger portion of users and culture.

It was and is a small number of people regardless. I’m not sure if that’s going to be the “reason” nothing happened. If so, it doesn’t seem like that can conclude protection from misuse.

Re:New Mac ransomware spreading through piracy by rvz on Tuesday June 30, 2020 @07:13PM (#23695898)
From the standpoint of malware writers, the users are one Office 20XX or Adobe CC 20XX away to installing the latest 'free trial' until they search for that fake keygen.exe or 'cracked full version' and it starts encrypting their work.

Adobe and Microsoft are the most targeted by malware writers unsurprisingly.

Re:New Mac ransomware spreading through piracy by harikb on Wednesday July 01, 2020 @01:53AM (#23698190)
Not only that, Little Snitch of all things. I can understand if people downloaded pirated a game or word or photoshop (before they went all cloud). Little snitch is literally for the ones who are paranoid about these things in the first place
Re:New Mac ransomware spreading through piracy by Topgamer7 on Tuesday June 30, 2020 @08:35PM (#23696451)
I knew a dude who loved to click on ads. All of them. He thought it was fun to see all the garbage people try to peddle to you. Even after I explained to him that ads can be sketchy and lead to you collecting malware.
Re:New Mac ransomware spreading through piracy by nisten on Wednesday July 01, 2020 @04:14AM (#23699115)
You could say the same thing about every business that has installed Zoom.
Re:New Mac ransomware spreading through piracy by mratsim on Wednesday July 01, 2020 @08:38AM (#23700671)
Zoom is free so you're the product.
Re:New Mac ransomware spreading through piracy by nisten on Thursday July 02, 2020 @02:34PM (#23716462)
No it's not, the business product had the exact same spyware-like behaviour issues acting up after you'd uninstall it on MacOS. They had to push an entire mac security update just for that fix.
Re:New Mac ransomware spreading through piracy by GekkePrutser on Wednesday July 01, 2020 @04:04AM (#23699045)
In particular, I don't understand how people use pirated security software (which Little Snitch basically is). If you're going to have to trust something, it's that.
Re:New Mac ransomware spreading through piracy by waheoo on Wednesday July 01, 2020 @03:34AM (#23698825)
You mean like a batch file with a vlc shortcut icon. I accidentally run those all the time. My eyesight sucks and win10 accessibility is dogshit.

Ive done similar on mac too.

Re:New Mac ransomware spreading through piracy by bobbylarrybobby on Tuesday June 30, 2020 @07:21PM (#23695956)
It's not just that it was an executable. The real issue is that Little Snitch is distributed as a pkg (not that that's the developers' fault, as there's no way to implement the app's functionality with just a simple app). But distributing it as a pkg that requires installation with an admin password is how the malware takes hold of a user's computer. AFAIK it is always safe to open an app you download from the web (although the app may not respect your privacy).
Re:New Mac ransomware spreading through piracy by saagarjha on Tuesday June 30, 2020 @07:22PM (#23695961)
> The real issue is that Little Snitch is distributed as a pkg (not that that's the developers' fault, as there's no way to implement the app's functionality with just a simple app).

In Big Sur, it might be.

> AFAIK it is always safe to open an app you download from the web (although the app may not respect your privacy).

Apps can still encrypt your disk this way.

Re:New Mac ransomware spreading through piracy by bobbylarrybobby on Tuesday June 30, 2020 @07:28PM (#23696011)
Does apple not throw up a permission dialog whenever an app tries to access just about any part of your filesystem? Like this:

https://nektony.com/wp-content/uploads/2019/11/grant-acces-d...
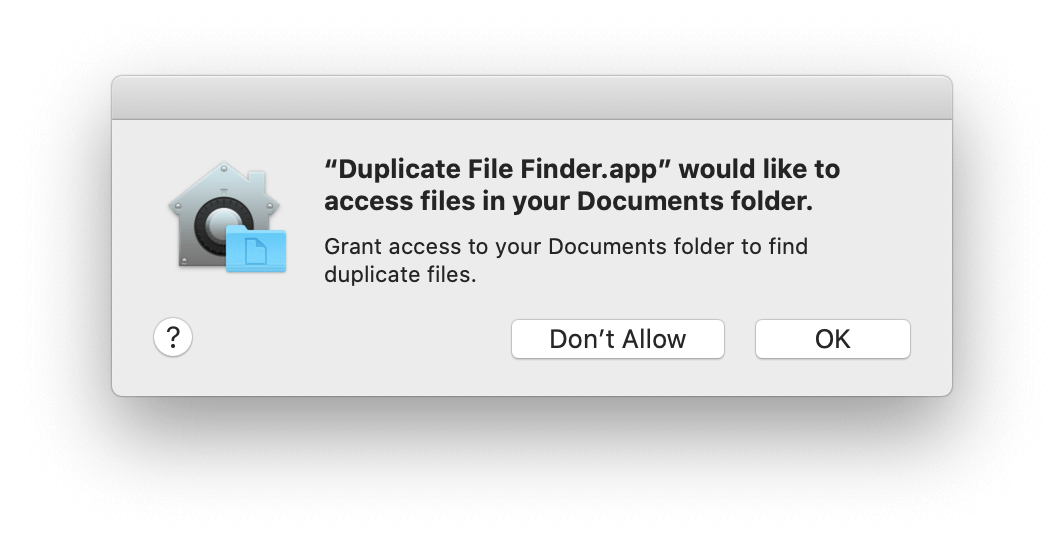
I could be wrong, maybe it's only for certain kinds of apps.

Re:New Mac ransomware spreading through piracy by comex on Wednesday July 01, 2020 @12:49AM (#23697839)
That’s for all apps, but only for specific parts of the filesystem, so there’s still plenty of room for apps to cause havoc by messing with everything else.

This is separate from the older sandboxing feature that’s designed to fully isolate apps from the rest of the system, which is mandatory for Mac App Store apps but opt-in for other apps.

Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:32AM (#23699233)
Mandatory for new Mac App Store apps
Re:New Mac ransomware spreading through piracy by michaelmrose on Tuesday June 30, 2020 @09:29PM (#23696773)
>FAIK it is always safe to open an app you download from the web

No its not various ways to break out of sandboxes exist.

Re:New Mac ransomware spreading through piracy by Wowfunhappy on Tuesday June 30, 2020 @10:58PM (#23697299)
And you don't even know that the app is sandboxed!
Re:New Mac ransomware spreading through piracy by fortran77 on Tuesday June 30, 2020 @11:34PM (#23697498)
The real issue is people are trying to steal it and getting fooled by a malicious site.
Re:New Mac ransomware spreading through piracy by c-c-c-c-c on Wednesday July 01, 2020 @02:09AM (#23698273)
Download the program from the developer and run the keygen in a VM and copy over the license.
Re:New Mac ransomware spreading through piracy by whywhywhywhy on Wednesday July 01, 2020 @10:04AM (#23701420)
Very few keygens these days, there used to be a 100% safe way of getting the full Adobe Suite back in the CS6 days.

Now everything is subscription based fully you have to replace the license system within most major software.

So I'm told.

Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:31AM (#23699227)
If they give you the keygen…
Re:New Mac ransomware spreading through piracy by stOneskull on Wednesday July 01, 2020 @05:52AM (#23699726)
it is getting like that. it's been mostly good up til the present time. you know, there are 'scenes', trusted crackers and communities, users giving 'thumbs up' etc. but this ransomware trend is a bit scary.
Re:New Mac ransomware spreading through piracy by wolfgke on Wednesday July 01, 2020 @04:52AM (#23699359)
Because they simply cannot afford the software, they often do not have an alternative.
Re:New Mac ransomware spreading through piracy by coronadisaster on Wednesday July 01, 2020 @07:11AM (#23700177)
Probably not much riskier then using the mobile app stores if you have a good source.
Re:New Mac ransomware spreading through piracy by piratearrrggg on Tuesday June 30, 2020 @08:16PM (#23696354)
I've been pirating since I was 11 years old. I have never once gotten a virus or malware. I have, however, gotten a virus from a random website that popped up on the front page of google.
Re:New Mac ransomware spreading through piracy by ipsum2 on Tuesday June 30, 2020 @07:00PM (#23695790)
some people like to live dangerously.
Re:New Mac ransomware spreading through piracy by earthscienceman on Tuesday June 30, 2020 @07:29PM (#23696020)
Or. Like the world we live in, there's massive inequality and some people just don't have "I comment on hackernews" levels of money
Re:New Mac ransomware spreading through piracy by spideymans on Tuesday June 30, 2020 @10:54PM (#23697282)
If you're gonna pirate, at least do a checksum or something.
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:32AM (#23699236)
Against what?
Re:New Mac ransomware spreading through piracy by jonathanstrange on Wednesday July 01, 2020 @04:51AM (#23699352)
Against the cracked copy, of course, to make sure the DRM really has been removed. You don't want to get nasty surprises and accidentally install PACE or another Sony rootkit...
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @05:06AM (#23699439)
How would you know if he cracked copy you’re comparing against didn’t already have something nasty in it?
Re:New Mac ransomware spreading through piracy by jonathanstrange on Wednesday July 01, 2020 @09:06AM (#23700886)
You wouldn't, I was joking. Sorry, I shouldn't have done thas, I was in "Reddit mode" and forgot that discussions are more sincere on HN.
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @01:39PM (#23704206)
Ha, I didn't catch the joke. Guess it seemed too much like genuine advice…
Re:New Mac ransomware spreading through piracy by mratsim on Wednesday July 01, 2020 @08:39AM (#23700679)
checksum can tell you if there is a difference but not what caused it.
Re:New Mac ransomware spreading through piracy by brnt on Wednesday July 01, 2020 @03:57AM (#23698990)
I don’t understand how people dare to run executables downloaded from app stores..
Re:New Mac ransomware spreading through piracy by eckza on Tuesday June 30, 2020 @07:07PM (#23695849)
Re:New Mac ransomware spreading through piracy by saagarjha on Tuesday June 30, 2020 @07:15PM (#23695910)
Not just children.
Re:New Mac ransomware spreading through piracy by imtringued on Wednesday July 01, 2020 @05:18AM (#23699515)
They ought to be punishmed by forcing them to play Cataclysm DDA without the wiki.
Re:New Mac ransomware spreading through piracy by pacamara619 on Tuesday June 30, 2020 @07:52PM (#23696187)
I don’t understand how people dare to run anything but free and open-source software. Proprietary software tends to have malicious features. The point is with a proprietary program, when the users don't have the source code, we can never tell. So you must consider every proprietary program as potential malware.
Re:New Mac ransomware spreading through piracy by LadyCailin on Tuesday June 30, 2020 @11:01PM (#23697313)
I don’t understand how people dare to run anything but software they have written themselves. Open source software sounds good, but I don’t review each line of code myself, so we can never tell. So you must consider every program you didn’t write or review line by line as potential malware.
Re:New Mac ransomware spreading through piracy by saagarjha on Wednesday July 01, 2020 @04:34AM (#23699242)
I don’t understand how people dare run software at all. Everyone knows software has bugs, and what if it does something you didn’t want it to do?
Re:New Mac ransomware spreading through piracy by yjftsjthsd-h on Tuesday June 30, 2020 @11:00PM (#23697307)
There are backdoored binaries for FOSS projects (filezilla comes to mind), and well-behaved proprietary programs.