This is a really hard story to know what to think about. On the one hand, yes, hardware implants are a major risk. And having so many of our electronics manufactured in a country with massive state control over its economy and with which we have an adversarial political relationship is definitely a big concern.
On the other hand, the denials from the companies cited in the first article are remarkably strong. And again this article fails to give relevant details. It just cites a security contractor who says he had a client who had this issue.
But Bloomberg is a serious news organization and they are holding strong on this story as well. So what to think?
It strikes me that if your goal was to ramp up tension between the US and China at multiple levels, then planting this sort of story would be a great way to accomplish it. Politicians can cite national security. Wary consumers are triggered over privacy. Corporations become more and more gunshy of investing in China and partnering with Chinese manufacturers.
I hate to dream up conspiracy theories. And yet, we live in a world where many states, politicians, organized crime groups, political groups, and corporations are all intentionally spreading disinformation of all sorts all the time designed precisely to ratchet up tension and suspicion.
I don't really believe that's what's going on just yet. But I also don't believe it's as straightforward as the Bloomberg stories make it out to be, either. Something very strange is going on.
In terms of security concerns also - come on, we know by now to which lengths the US goes in this area, and they're surely doing worse stuff than this, I'd expect no one would doubt it any more. So, either they are genuinely surprised by this, which would be silly (a politically adversarial nation using an obvious opportunity - cheaper stuff being produced there for decades - and doing the same), or it's a part of a broader narrative that's being built.
And, to be clear, I don't think we (the world outside China) shouldn't be a bit worried given in what position _we've_ put China and how strong they are now - it's just that this kind of mass-manipulation and propaganda is the most-detested way of doing it for me...
At least China won't be as dangerous as the US or the Soviet Union in that it has absolutely no interest in enforcing its political ideals on other places or becoming a world police. I see no real reason why people should be worried about the rise of China as if this will turn the whole world Orweillian. China has its own way of organizing the vast and complex country and it's hard to come up with better practical solutions. Still if one doesn't like it they can just live somewhere else, and the authorities don't care, as long as it doesn't hurt Chinese business.
Not yet. But becoming a banker for whole third-world is almost done. And when your debts are big, you lose sovereignty.
They’re just more subtle, until they’re not. They have a very long term outlook on their efforts.
1. As a white-hat security researcher, you have an ethical responsibility to publicly disclose vulnerabilities after doing the necessary due diligence (informing the affected parties privately, and giving them the necessary time to respond, investigate, and come up with an acceptable solution).
2. As a US citizen, you can't report attacks carried out by US intelligence agencies.
I can definitely see the responsibility that patriotic duty would entail, but a citizen with no links to their country's intelligence agency being held responsible for the said agency's failure in maintaining operational discretion doesn't seem sensible to me.
Edit: update formatting.
Who says? Unless you've received a National Security Letter, a gag order from a court, or have a pre-existing relationship with the government that governs disclosure (e.g. security clearance), there's nothing preventing a researcher from disclosing lawfully obtained information. Stumbling upon a secret investigation doesn't make the information unlawfully obtained, even if you suspect it might be a secret investigation.
I suppose intent could be there if you share information about a device that says, "Warning: national defense injured if you disclose". But absent a duty I don't think a court would impute intent, especially considering the Free Speech issues (somewhat peculiar to the U.S.).
Notice that nobody has seriously suggested (AFAIK) that the journalists who assisted Snowden should be charged under the Espionage Act, even though their acts would seem to fit multiple provisions. I think that's because unlike Snowden they had no duty, which means the bar for the requisite intent and knowledge (i.e. whether something is really going to harm national defense) is incredibly high.
But who knows? It's a good point and it poses a ton of questions. Still, personally if I found a spying device on something I wouldn't hesitate to disclose it if it seemed noteworthy. I wouldn't feel chilled by the Espionage Act. The same law in some other country? Probably would think twice.
Sure you can. Short of a gag order (and maybe not even then) you can report intrusions all you like.
In any event, how does one determine the nationality of hardware that shouldn't be there? It's not like there's going to be a snarky "Designed by the NSA in Fort Meade" logo on the chips in question.
You also abide by a whole slew of laws regarding sensitive, secret, top secret, or SCIF information. If I knowingly, or even suspect, some information if classified, and I transmit it to anyone else than my federal assigned contact, I'm breaking major federal laws.
A lot of security professionals in the US have such clearances. So finding a NSA implant or such proof makes it dangerous to talk about by default.
So yeah, a gag order by profession.
> This claim seems like a big dilemma for US white-hat security researchers
It seems like the two are mutually exclusive.
https://dictionary.cambridge.org/grammar/british-grammar/pro...
https://www.quickanddirtytips.com/education/grammar/one-vers...
Are they? The authors of this story published an unverified and in corroborated story about Heartbleed a few years ago, claiming that the NSA knew about it and was exploiting it (https://www.washingtonpost.com/blogs/erik-wemple/wp/2014/04/...).
When the articles published by those "serious news organizations" concerns China, disinformation / lack of evidence are really common place if you carefully examine their source. I used to do so from time to time but grew tired of that
Cool. Let us test.
Error: Line 2:
> In my opinion, newspapers are all propaganda machines driven by some their benefit.
No conspiracy theory needed, traditional media is dying, and in their last gasps of air they are destroying their credibility for the sake of clickbait articles without proper facts and coberation. They are being deceptive, because they know outrage and politically dividing stories are still working.
It's really said, but transparent. No way, Apple officially writes that rebuttle on their website if the story is true.
Personally I'm confident Bloomberg's reporting is accurate to a high degree. Based on prior experience with investigative journalism there's no way they would go all in with a story like this if they weren't standing on firm ground. Every single sentence would've been vetted. For each statement made there would be someone whose job would be to reject it unless you could back it up properly. This is also why you don't see these entities defending their story against random criticism that pops up. Most if not all decisions have already been made by the time it goes public.
The fact that there's now a second story on the same topic is a good sign. The reporting of these things are usually followed up by additional pieces to increase the impact (and revenue of course).
They claim they have 17 independent sources. That's pretty impressive in itself. It also means that they probably worked real hard verifying their sources' claims and inputs. I find it unlikely that they would've acquired all those sources unless the thing was real.
And based on my prior experience I would make the exact opposite conclusion. Technical writers are rarely technical, and they seem to be happy to make stuff up and mislead - even if unintentionally - so long as they make their deadlines.
Every tech article written about a subject I was directly involved in has not even gotten the spirit of the topic remotely accurate, much less minute technical details such as what chip is used where.
That said - I fully believe supply chains are entirely compromised. I just don't think in this case I'd really put much stock into this specific reporting - they've already been caught blatantly misleading their readers by putting up a photo of a stock Mouser part and not denoting it as such.
I think a contributing factor is that it's generally hard to write about things you don't fully understand with the correct nomenclature. Especially when you might not be able to talk/ask for help about specifics with people more knowledgeable because of the secretive process.
Things could've been dumbed down, intentionally or unintentionally, by those involved. It wouldn't be hard to imagine a conversation like: "-So it was sort of a coupler thing? -You could say that, yes". Or what if the technical detail came from a Chinese source and Google translate mangled it?
The coupler thing is dumb and so is the picture (assuming it was a random product picture) but at least they might serve as a way of communicating the big picture: a hard to spot electronic "coupler" thing.
Maybe there is something there, and/or there is a reason to talk/substitute in vague terms, but insofar as the explicit technical details are concerned, they don't appear credible. Then you're left with an empty allegation that you will have to decide to believe or not based on no other ground than potentiality.
I do have to disagree about the competency of Bloomberg, though, they publish a lot of speculative, low-tech AI/ML scare articles that can be described at best as "inaccurate" and, more realistically, as "making stuff up". They used to have a good reputation, probably from their financial journalism, but their tech work is not good but any reasonable measure, in my personal opinion.
It would also be great to know what the attribution is based on. Just the fact that they're manufactured in China? Who else might get their hands on these devices in the shipping chain? What kind of traffic did they monitor? I guess just observing it's talking to a Chinese address doesn't tell much. I mean, just take an S3 bucket and dump your stuff in there. Setting up your own server in your home country pretty much screams "we're here!"
> I'm now wondering if someone found an NSA implant and misreported it as Chinese. We're going to end up in the stupid situation where people are afraid to report foreign intelligence attacks because it's illegal to report an attack by US intelligence agencies, aren't we?
That's pretty tinfoily, but it'd be a cool way to still report on it. "Whoopsie, I totally thought it wasn't you guys, sorry for disclosing"
From the original Businessweek article:
"Supermicro has assembly facilities in California, the Netherlands, and Taiwan, but its motherboards—its core product—are nearly all manufactured by contractors in China."
That's interesting. As someone who has bought hundreds of thousands of dollars of gear from Supermicro (and has been a huge fan of their products and designs) I always thought their chassis were their core product.
Recently SM started to go down the "you can't buy our JBOD chassis without buying them full of our qualified drives" ... I knew that was the end of the golden age (of SM).
Luckily this coincided with the introduction of the 60bay HGST JBOD chassis. We haven't looked back.
Yes, these units are stellar and anyone buying Supermicro JBOD units should be looking into these as much better replacements. If you have volume they can be even more competitive than Supermicro if you push.
<off to look up this beast>
I know that some refineries do direct delivery for some of their large customers, especially industrial lubricants and other by-products. If the order is big enough, or someone wants to pay the premium, then direct delivery could be very feasible for tech too.
Personally, as someone outside the US, I would gladly trust alleged Chinese malware over known NSA malware. Or even better, literally any other country outside the 5-eyes.
[1]: https://www.theguardian.com/books/2014/may/12/glenn-greenwal...
I know it won't probably won't apply to general purpose motherboards or devices, but is there a way to design or build some components or devices in a way that you can verify that they can perform their purpose and nothing more?
If we start with that concept, and slowly build up "verifiably secure" components, they can be the islands of security that we can build off of without having to worry if the manufacturing plant left their door open one day and some random person was able to sneak in.
For a motivated and well funded attacker who has an ability to manufacture a replacement chip with an additional coprocessor that can siphon or modify data from the main processors, network cards, and baseband modems, short of decapping every chip and component that comes through your assembly line your resources would be better spent on establishing trust mechanisms with your suppliers and the transportation couriers touching your devices before the end user acquires it.
https://en.wikipedia.org/wiki/Tailored_Access_Operations#Kno...
http://www.spiegel.de/international/world/the-nsa-uses-power...
A way to verify a chip is working as expected in a way that it can't be gamed without breaking multiple fundamental proofs, so that you won't need to worry as much about who makes it, just that it "passes the tests". (and you'd probably need a system to validate the validators, but splitting up the people involved means it is significantly harder to hack multiple products to all have them falsely verify each other)
Obviously I have no idea what I'm talking about and am just kind of musing at the idea, but trying to secure the whole supply chain from digging materials out of the ground all the way until it is in the hands of the consumer seems like an exercise in futility. You'll never be able to secure it in all cases, and like you said a truly motivated attacker is going to be able to break the chain (even if it means threatening a handful of people with death so you can get 5 minutes alone with a board).
Already exists in the form of 'country of origin' procurement for high security applications.
Since there are many flash chips fitting the same pin out, all it took was soldering a compromised flash chip (with firmware for the BMC chip) onto pads that are already part of the design to compromise the whole system without any obvious sign that the board was tampered with (because in some SKUs, both chips were populated).
If you wanted to "backdoor" motherboards that shipped with these BMCs, wouldn't it would be much easier to just install your own "customized" version of the firmware on them? It certainly seems that it'd be much more difficult to incorporate another device into the system.
[0]: https://www.aspeedtech.com/products.php?fPath=20&rId=376
[1]: https://www.aspeedtech.com/products.php?fPath=20&rId=440
Normally this wouldn't be worth talking about because most active chips are too complicated and too design/supplier specific to carry out an attack like this, but SPI flash is about as standard a footprint/protocol as you can get in EE short of transistors so if you ship a product that could be reprogrammed from unpopulated pads, you're opening yourself up to a large attack surface.
Honestly, after I read the latest BMC chip theory I was like: "Oh, shit. Have I done that?"
I'm not trying to be adversarial, even if it's only a theory it's an interesting one, but given the amount of conflicting information we have regarding this whole mess I think it's important to be clear about what's pure speculation and what's been reported by people supposedly in the know.
The BMC back then was by a company called ATEN, who make KVMs. The modern BMC is by ASPEED - I don't know if they're related.
What's described in the article is exactly how the old ATEN firmware worked normally. It was a spectacularly poor product from a security perspective.
I thought China was famous for extremely short turnarounds for industrial engineering edits, so it seems plausible that they could manufacture the boards in a reactionary way and not need to do much in the way of logistics to get them to their targets.
https://assets.bwbx.io/images/users/iqjWHBFdfxIU/i0hZ31udMZ_...
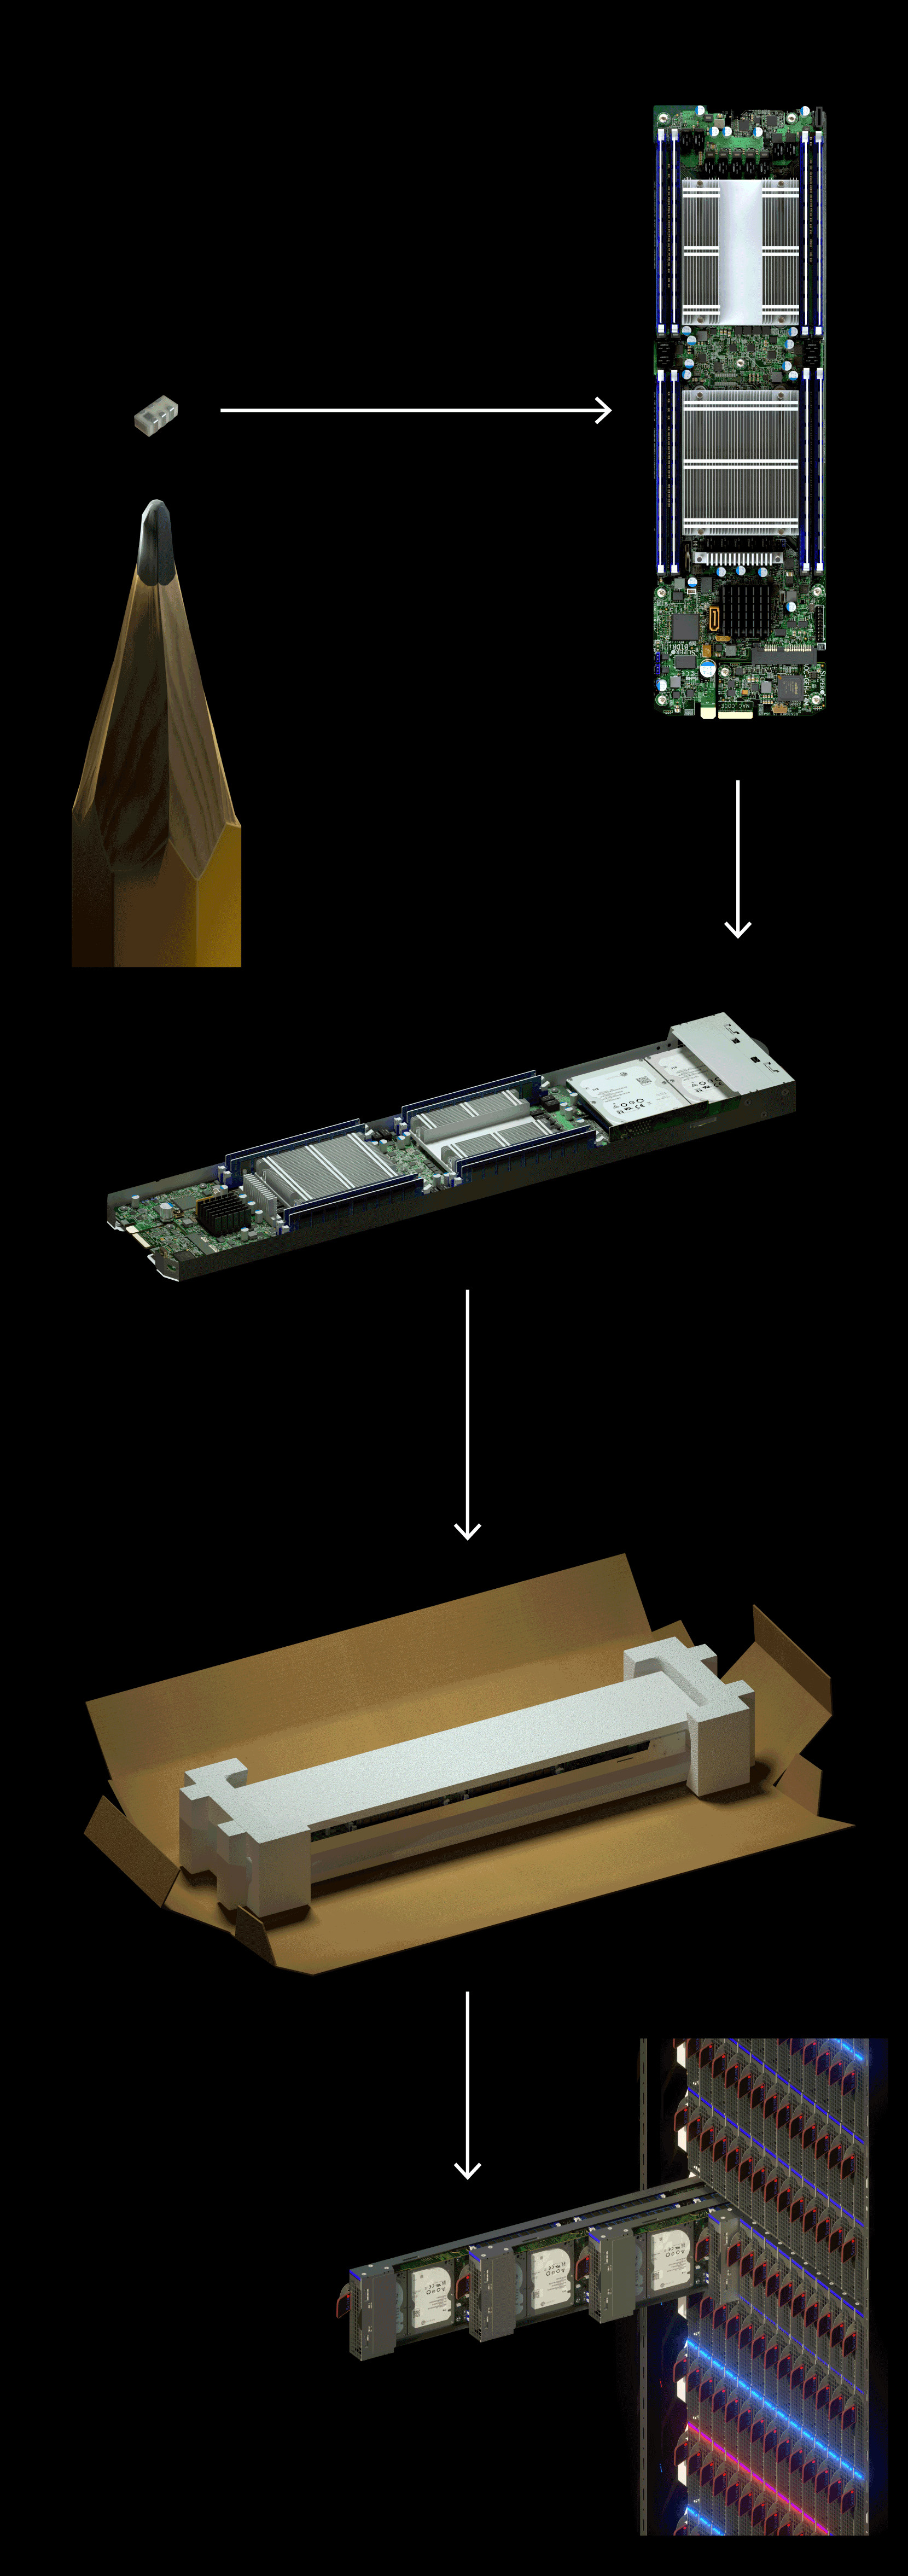
https://assets.bwbx.io/images/users/iqjWHBFdfxIU/i9VdsjZLS_P...
They really have no idea what they are talking about at this time and it's probably fluff.
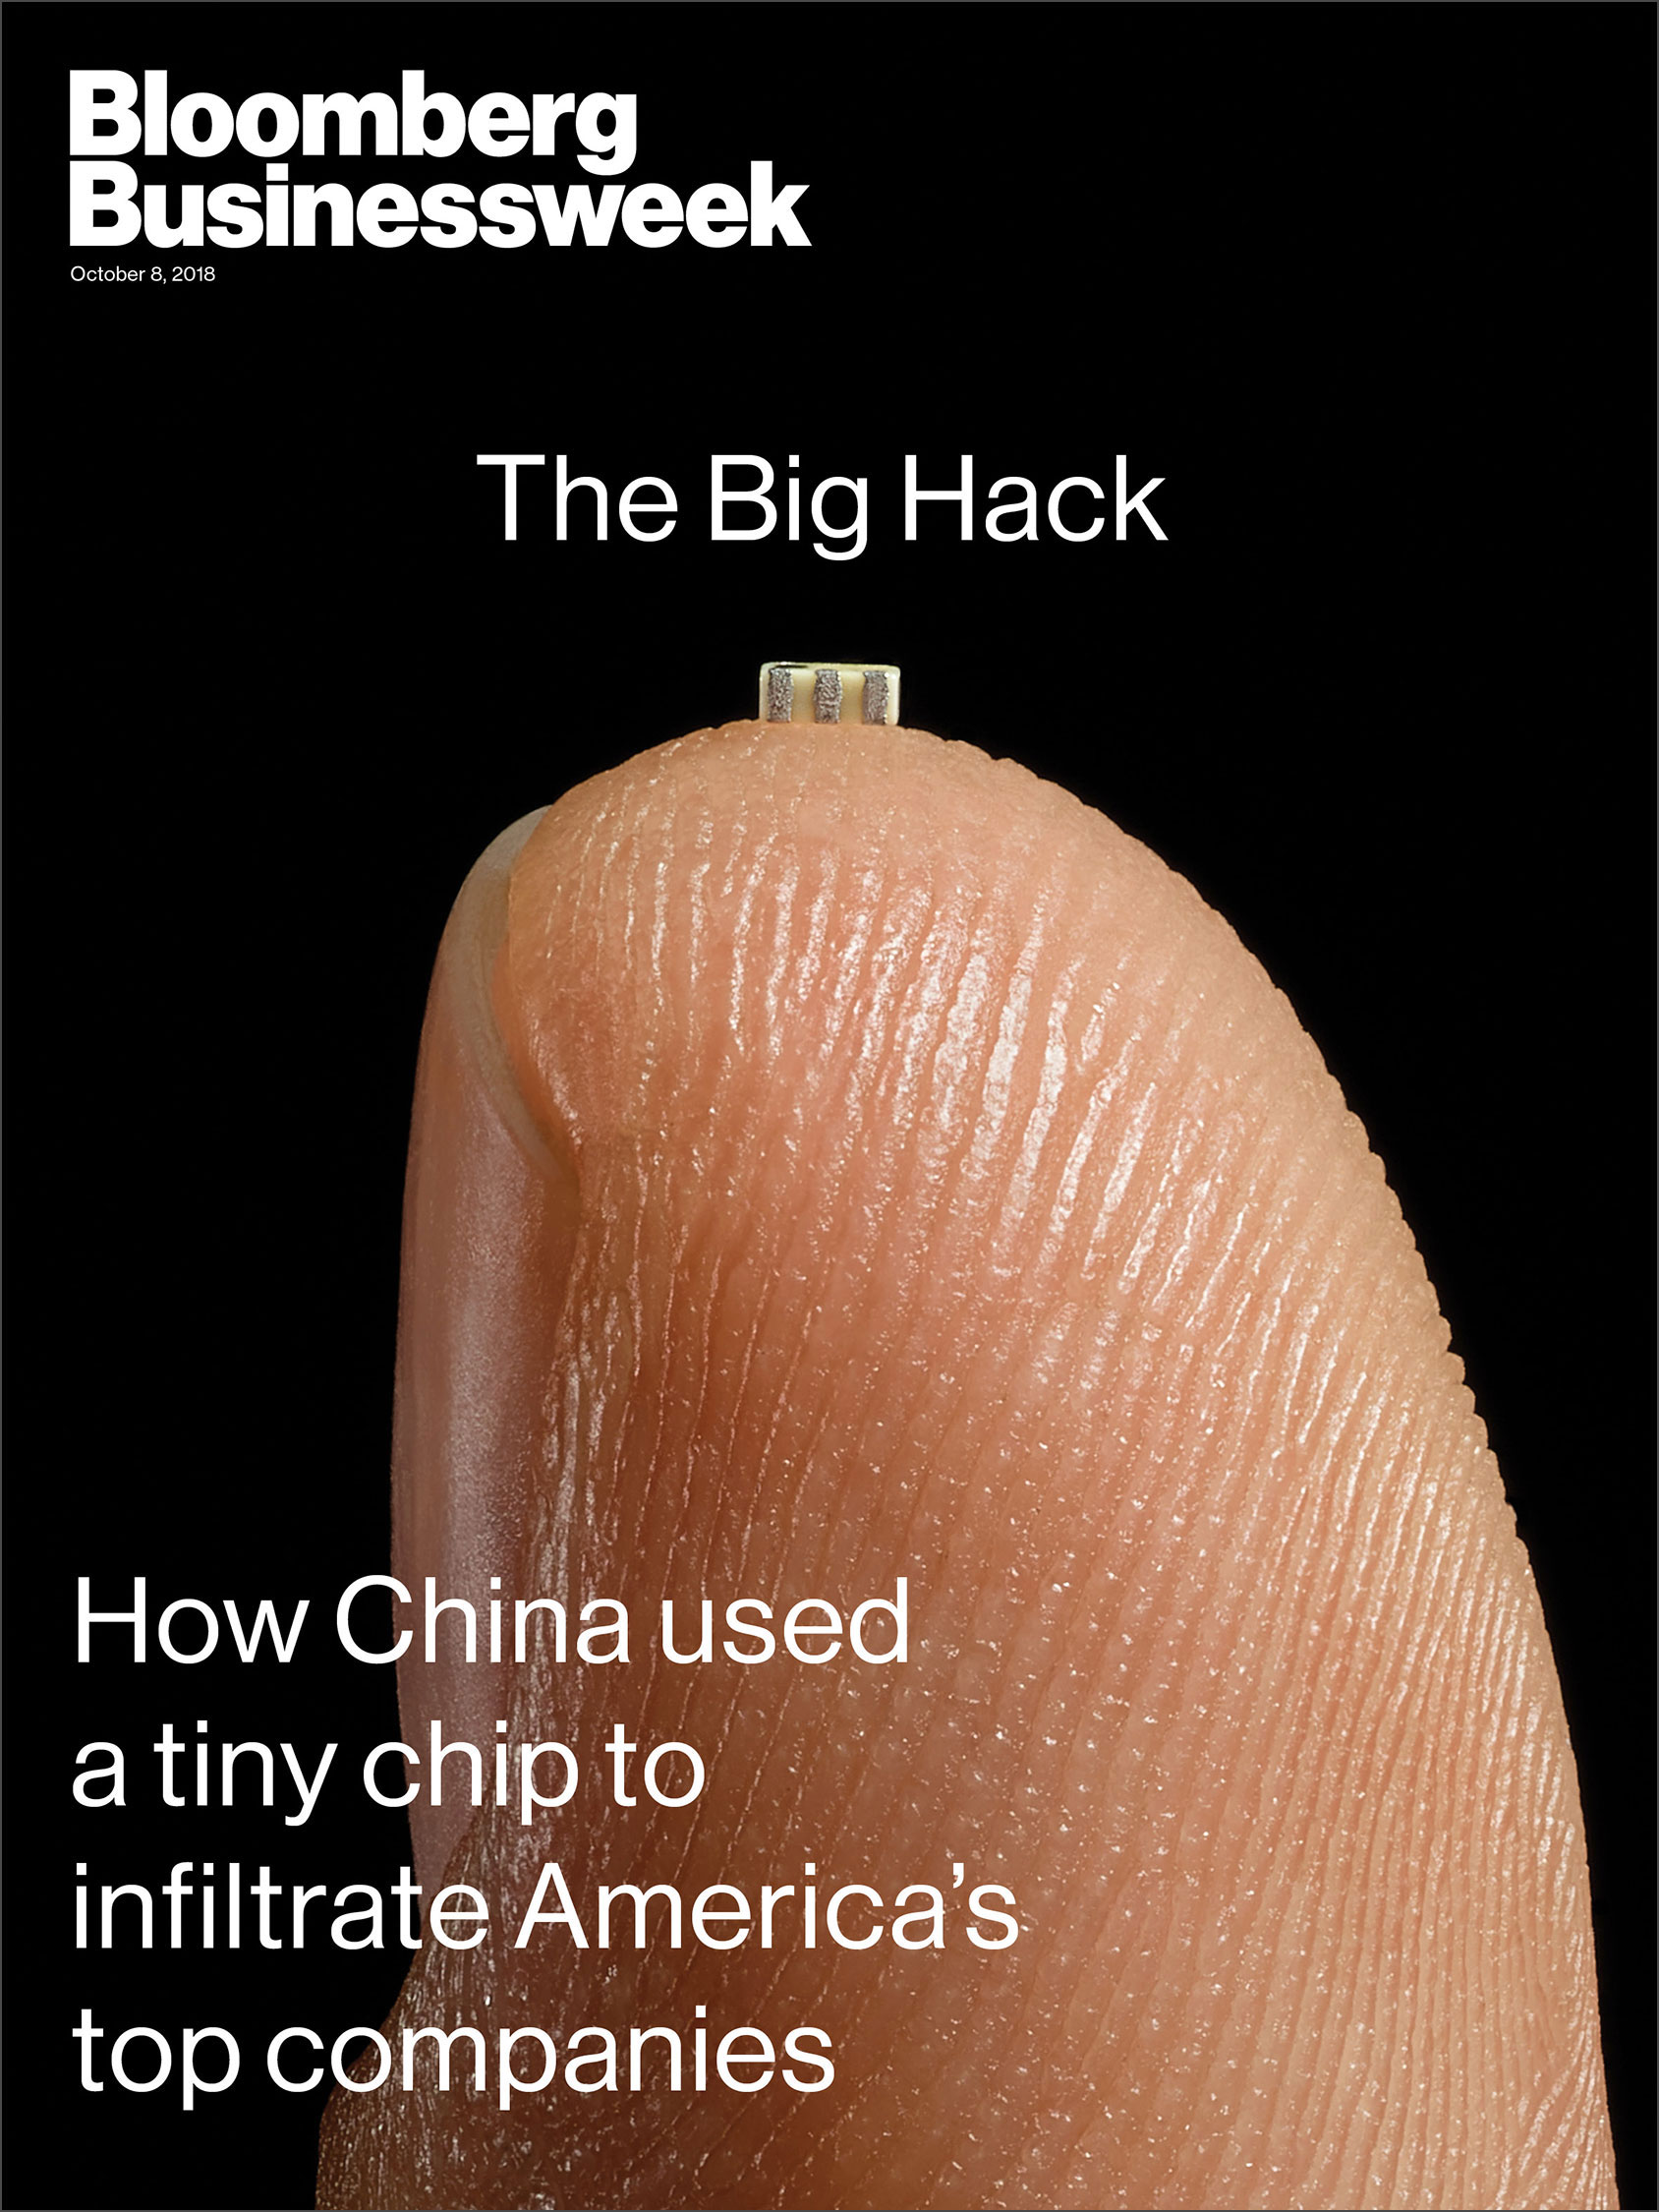
Long story short, that photo does not show the device involved.
"Robertson was unable to produce photographic evidence of the chips in question, saying they were described to him by protected sources. Indeed, Robertson in September asked Fitzpatrick what a "signal amplifier or coupler" looks like, suggesting the publication narrowed the attack package down to that particular component. Fitzpatrick sent Robertson a link to a very small signal coupler sold by Mouser Electronics. "Turns out that's the exact coupler in all the images in the story," Fitzpatrick said.
https://appleinsider.com/articles/18/10/08/security-research...
I would definitely spot that device if it were on these boards because it was described in detail and there were some pictures of what it supposedly looked like.
A device like that is not on either side of the board and it isn't in between the outer board layers (where it would be much harder to spot, especially if the cavity would be covered by a ground plane on one side).
I am not saying it is impossible, it is just very hard to hide something like that once you know it is there. The only candidate spots left that I can not check without destruction is underneath some of the devices or inside some of the devices. That would be a different level of sophistication than the original article alluded to.
In case you missed it, there is an article posted today [0] that has this quote from "Hardware security expert Joe Fitzpatrick", one of the Bloomberg sources, regarding "the supposed spy chip":
> In September when he asked me like, “Okay, hey, we think it looks like a signal amplifier or a coupler. What’s a coupler? What does it look like?” […] I sent him a link to Mouser, a catalog where you can buy a 0.006 x 0.003 inch coupler. Turns out that’s the exact coupler in all the images in the story.
The original article has now dropped into the real of SF for me until they show a detailed shot of an actual board with a parasitic device on it. Until then this is a wild goose chase.
Thank you for pointing this out.
They get FISA court orders that force american companies to attach their equipment.
Specific example aside, it's worth talking about why this does happen. "Black bag jobs" can mean "we didn't get a warrant", but they can also mean "we got a warrant and still aren't telling".
Even given a court order, there's still a possibility that employing surveillance by fiat will cause somebody to leak, or modify how they handle data, or simply reveal information about what sort of surveillance tools a given agency employs. Given that a FISA order can be obtained without a defendant, getting a court order and then doing the thing secretly anyway gives a sort of "bowling with bumpers" advantage where the project is approved if it gets revealed, but also done without revealing anything if it isn't.
More disturbingly, there's also substantial evidence that the NSA attacks companies covertly in places where they couldn't get a court order. Taking a specific device out of the supply chain and adding surveillance before it's shipped to the destination is a warrant-worthy project. Setting up systematic physical vulnerabilities with a use case of "turn it on some time in the future to get something interesting" isn't in the purview of a FISA order, so if the NSA did do that it would have to be without an order.
Other NSA programs that Snowden revealed were covert hacks. https://en.wikipedia.org/wiki/Global_surveillance_disclosure...
PRISM was at first reported as some sort of direct access to the servers of certain American companies, but it turned out to be the code name for a joint program with the FBI for using FISA warrants to request data from those companies.
You can see how this benefits the NSA; if the voice mail is outsourced to a foreign company, and the NSA buys intel from that company, it's technically not spying on US citizens, particularly if they're getting metadata.
https://www.washingtonpost.com/news/the-switch/wp/2013/11/04...
Additionally, the story quoted talks about how the UK obtained the data and gave it to the NSA.
Nowhere is the NSA installing covert implants. They just don't do that.
The CIA does that :)
Ah, so he pinky-promised? Well OK then!
You are taking the word of a spy? Did he say it wittingly?
PRISM
https://www.schneier.com/blog/archives/2018/08/backdoors_in_...
> Juniper has confirmed that an initial analysis of malware linked to the National Security Agency appears to affect its firewalls.
https://www.zdnet.com/article/juniper-confirms-leaked-nsa-ex...
Huawei & ZTE have been alleged with these exact type of attacks, by the US government
That doesn't make sense based on the assumption that US telecom companies already cooperate extensively with US inteligence agencies.
He went to prison because he sold stock based on insider information. Regardless of the reasons for his trade, it was still insider information.
Whether China or the US re-allocates your IP, you can expect a competing product made in China. That you might have a relationship with one of them probably doesn't change anything unless they actually think your firm is the best one for the job of maximizing the results on their tax base.
I mean maybe I'm wrong; would it make any sense that these Republics take private corporate property more seriously other parts of their Constitutions they have violated at least until caught?
The US makes the claim China does not and former president and CIA head George Bush floated corporate espionage as THE plan for handling the absurd costs of "intelligence" criminals after the cold war..
I'm always astounded that working in a competitive market seems to blind people to significant stated facts of the environment their market is operating in.
In nature, it might make sense to just outrun the weakest, after all, a bear has a limited appetite. But superpowers have unlimited apetites and will collapse like the USSR if they should ever expand slower than cancer.
Most of these attacks never leave the room at corporate HQ where they are discovered unless an engineer wants to permanently screw themselves out of a career.
I once tried to leave a linkedin recommendation for a friend I'd worked with on a high profile project where he discovered Chinese state actors performing corporate espionage and we stopped it. The FBI came in and carted off the servers, we switched data centers, re-deployed, and that was that. We would never have been the wiser if he weren't closely monitoring network characteristics. 3 years and 2 job changes later he messaged me back to say, "Thank you for the rec. but don't mention that shit!"
Could you expand more on that?
is it? and if you were witness to such an attack, how would you be able to attribute it to the USA vs some other actor?
Is this true? I mean outside a specific gag order or working under a clearance, you could find an issue with a piece of equipment, publicly talk about it and then be arrested because it turned out it was the US government who caused the issue?
Interesting. This one seems to rely on the presence of the USB connectors for powering. So, basically, any ethernet port with only Ethernet connectors should be safe from this kind of attack? The only powering option there should be PoE but I have yet to see someone buy PoE switches for a datacenter...
I know that some IPMI implementations can control/use the on board ethernet. There might be some hole there. Similar for the built in management on some Intel processors and nics.
It was a small datacenter but we had a bunch for PoE KVMs.
Can you provide a citation for this statement please
> You can't use uncertainty [...] as evidence for your own nuttery. Stop it.
To wonder aloud should not be so demonized much less demanded to cease.
I mean, sure, it could be NSA. Let's wonder! The fact that no one in public has seen one of those things isn't supporting evidence for that theory. It's even less grounded than the Chinese one.
Beyond that Apple, Microsoft, Tesla and probably Amazon have sufficiently capable public (or past public) researchers working for them. But I doubt many would want the publicity one way or the other.
The "trojan ethernet connector" paragraph mentions similarity to an NSA implant, which appears to be this: https://en.wikipedia.org/wiki/NSA_ANT_catalog#/media/File:NS...
I'm now wondering if someone found an NSA implant and misreported it as Chinese. We're going to end up in the stupid situation where people are afraid to report foreign intelligence attacks because it's illegal to report an attack by US intelligence agencies, aren't we?