If you spend your entire life with a camera pointed at your face, your face (and activity) will be accidentality filmed by that camera sooner or later. Indicator or otherwise. The indicator light is a good idea but I'm still spiritually on the side of the tape people.
Complex systems are hard to secure.
1. Electrically blurred glass. 2. Polarizing filters 3. Power kill switch, in hardware. But I guess Applw will balk at this too.
I will gladly trade a millimeter of thickness for increased functionality. It's the same thing where apple will ruthlessly optimize for thickness to the point where they can't cool the CPUs. They literally prefer form over function, as if the tool I use all day every day is an art piece.
Isn't that part of the appeal of Apple products? People will gladly spend more because of the looks, not the functionality.
Like fish said to be the final species to discover water, one mainlander comes to hk and surprise to see us so relax about security. What the law even assume people are innocent until proved otherwise ...
the mentality of hermit in One of the largest population of ... hermits. You just put on your shell.
As now become one of the hermit by force and talked as a hermit, may I suggest they just do it away with the camera. Use a wireless or usb based one. No hacking possible.
Economically (if not ethnically) trust is important as it lower the transaction costs. Chicago school heritage I guess of pre NSO HONG Kong. I switch to my two mac Mini of intel and arm. Unfortunately still have the old 3 cable apple monitor (work well with both 2018 and 2012 MacBook Pro) that have a camera. Guess a cover is ok.
Yeah, not ideal.
The user controls which apps get to turn on the camera...no one else.
I don't see Apple claiming they've done that but a correct design would make the indicator light work that way and be related to software at all. Meaning you could only disable the indicator light by physically modifying the device.
You can modify the Macbook of course, which is why the paranoid type will still use tape.
Some attacks I've seen will take a photo with the camera as fast as possible so you might not notice, but the light will always turn on.
There was an exploit, over 10 years ago like you said, that allow to disable it. But that was corrected.
Edit
- iıSeeYou: Disabling the MacBook Webcam Indicator LED - This was 2008 - https://jscholarship.library.jhu.edu/bitstream/handle/1774.2...
Looking for t1 links.
Edit 2
Can't find anything confirming the t1 right now..
https://support.apple.com/guide/security/hardware-microphone...
If the attacker has done this, they might as well just hide the camera somewhere else.
Your average blackmailer would be better off with the separate camera route (and likely wouldn't be sophisticated enough otherwise) but a state-sponsored attack could probably pull it off.
It's orders of magnitude easier to get access to a mobile device than to setup a camera in every possible location a target might move to. But they'll helpfully carry the device with them.
> iSeeYou ( 2008 )
Which is it?
EDIT: a commenter below said
"Macs newer than 4 or so years also have a feature that forces the LED to stay lit for at least 3 seconds after it has been turned on to prevent the single-frame-grab attack."
I really think an LED is barking up the wrong tree. A built-in hardware cover would have the same effect as the LED, and no one would have to trust it, since the camera would just be recording the back of the cover if it was hacked in stealth mode.
https://www.youtube.com/watch?v=IKY3hvYKPpA
Too bad it mainly shows your nostrils :(
I do physically disconnect or cover cameras. My desktop computer has no microphone unless I plug one in. Laptop and phone though? I definitely remember in the aughts that the police could remotely turn your phone into a bug without any user indication at all. To the best of my knowledge the only way to actually be sure you aren't being recorded with your own equipment is to remove power... of course now the batteries are soldered on, totally a coincidence I'm sure.
Boy, wait until you find about what's possible manipulating PCB or processor designs (the Bloomberg fiction piece "The big Hack" illustrates what would be possible with just PCB manipulation). Or firmware or anything else proprietary running with elevated rights (normal ones are already enough to cause a lot of damage on most systems).
All you can do is reduce attack surface.
Well, I don't mean to fuel your paranoia, but there are materials opaque to the human eye but not necessarily fully opaque to a CMOS sensor, especially one without infrared/UV filters.
It would be quite possible, trivial even, to design a web camera with a nice built-in black camera cover -- which is transparent to the camera.
If your laptop (or iPad, in the case of the latest gen) is an Apple T2 equipped device, this is somewhat relevant (“somewhat” as it’s not directly related to my original reply)
https://support.apple.com/en-gb/guide/security/secbbd20b00b/...
A better solution would be to have the microphone be physically removable, but even then it could have an internal power source and storage...
You may be able to verify a design like this once with a teardown, but it's impractical to verify your particular device, and next to impossible to re-verify this every time you leave your laptop unattended.
As someone who posts to Hacker News you are by almost any definition a potential information source or APT vector.
For the former a piece of tape is enough.
He didn't say it was.
What he said was that his threat model doesn't include state agencies. Many people use their laptops in bed and they probably don't want random people using their laptop webcam to take random nudes.
And, while I hear the NSA being quoted a lot, let's be fair, how many of us have the opsec to stand up to a genuine NSA attack?
A reasonable goal in thwarting the NSA should be to stop some random bureaucrat from typing on a few keys and getting access to your stuff without a signature. As long as some bureaucrat has to put their signature on a piece of paper and get budget to get my stuff, I'm safe against random trawling.
Besides, if the NSA really wants you, they'll just fabricate the evidence. It's way cheaper.
They didn’t need to use the word to imply it. I did however assume they’re weren’t so self-centeredly solipsistic as to think that their personal choices were the universal general case, or advisable for a typical participant on this forum. But then:
> Besides, if the NSA really wants you, they'll just fabricate the evidence. It's way cheaper.
Again, no. That’s another of those “surely this doesn’t happen” comments, and once again, it is flat wrong. Even setting aside that discrediting/compromising someone is likely to be different agency; just as with bugging them, there are still plenty more reasons besides eavesdropping or coercion, such as industrial espionage, or sabotage, and the main point is that this isn’t theoretical. It happens. Deal with it, don’t deal, up to you, but never assume you can’t be a target.
This is why I only take a disposable laptop and phone across US or Chinese borders. Both have intelligence services with the resources, ability, and inclination toward systematically documenting anyone even remotely interesting.
> As long as some bureaucrat has to put their signature on a piece of paper and get budget to get my stuff, I'm safe against random trawling
If this level of willingness to disregard the entire history of bureaucracy and covert action helps you feel safe, and if you have no direct or indirect ties to any other human being, body of data, or corporate entity that could ever be at any kind of risk, then why not I guess.
I must add, I peeked over his shoulder a few times, and my comment that it looks as good inside as it does out was answered with “yes, it’s like being asked to restore a work of art”.
Lenovo didn't allow you to configure a T480 with both the high-resolution display and the plastic slider, it was either-or. The high-resolution display was their premium option that omitted the slider and added two more IR cameras for Windows Hello support.
So in addition to not getting the slider, I also had to disable the IR cameras.
I'm half tempted to buy the version of the display bezel with the slider and see if it'll fit as a replacement.
[1] Yes, yes, assuming you can block all frequencies the camera is capable of detecting.
The point is whether you will be able to prevent the camera from taking a video/picture you don't want it to.
Unless you can physically disconnect or block the camera, there's not guarantee that a piece of software can't record.
The best Apple can offer here is that you will know the recording was done (assuming you are looking at your computer, and not looking away or in another room) .
A way to overvoltage/current and burn out the LED. Probability low, but nonzero.
More plausible situation: There are times when the camera is pointed at me, but my head is not pointed at the camera. Perhaps I left the laptop on in the corner of a room while it's playing music, or a myriad of other things.
A cover is a simple, foolproof solution to the camera issue.
Can you guarantee the manufacturer followed the design specification for every batch?
Threat models matter.
It’s a very different threat than most people have.
Most people on hacker news? Unclear.
I think a really large portion of users here would be extremely good attack targets. Developers with privileged access to source code and operations staff with privileged access to systems make up a significant portion of the users here.
Besides: Most people don't accidentally want to show up on a video conference while undressed when they accidentally hit the wrong button in some confusing skeumorphic app specific interface: The LED only warns you after its too late.
And in fact one of the devs was poached by a shady bunch of foreign looking suits who would have fit right in with big brother.
In all fairness you have a split second between the light coming on and the video stream initializing to err hide your shame. What are you doing in front of your computer with no pants on? Naked yoga?
Generally speaking - as developers type away on their packet handling or authentication code, they all too naively believe they won't be a target of a new friend or bribe.
The light indicator in modern webcams is a "physical" indicator. Sure, it won't stop it from being hacked, but it will light up whenever it is active. That part can't be hacked, since it's in the hardware.
Given the business he is in, the reason is blatant hypocrisy?
At the same time, he's going to be an exclusive target for myriad actors big and small, up to and including entire nations, so extra paranoia is probably warranted.
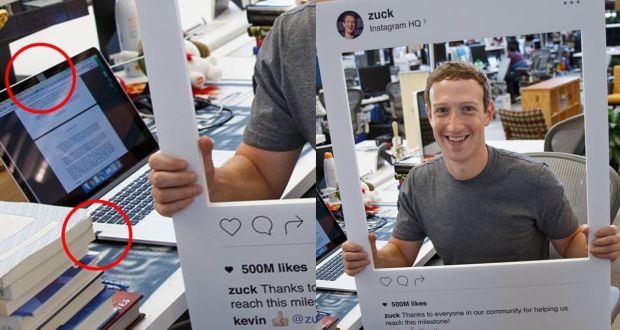
> There's a reason Zukerberg's laptop has its mic and camera tapped up
This is an incredibly weakly phrased argument; there's a reason people are flat-earthers as well. The existence of a reason does not automatically make that reason a good one.
I actually take his webcam tape to mean that his security group (which includes people who have serious hardware chops) doesn't think that the investment in a better option is worth it.
Lastly, about that 0day argument. Many camera LEDs are implemented in hardware, which means instead of hardware prevention they have hardware detection. There are reasons for both, and neither is unambiguously better.
The hacking consequences I care about are having my bank accounts drained, not having my picture taken.
Virtue signaling mostly.
It’s not difficult to open a laptop and remove those components all together. Especially for someone like Zuckerberg.
I think the simplest explanation is whoever was staging the scenery around him didn't think anybody would notice the taped laptop. If they did realize that, they probably would have untaped. It wasn't meant to be a detail you notice or centerpiece of conversation. That's my guess.
Yeah, people who don't understand how hardware works.
"Because I saw somebody smarter than I am had a piece of tape over their camera"
https://www.npr.org/sections/thetwo-way/2016/04/08/473548674...
For many people the trust in integrated laptop cameras has been thoroughly eroded especially in case of Macs. (From my experience by interacting with people not having much tech experience, limited to Germany, maybe also limited to the social cycle(s) I interacted with.)
The paradox thing is that the same people who often don't trust webcams in Apple Laptops or Apple All-In-One PCs do not bother or even think about weather or not the camera in their iPhone could spy on them or weather or not they microphone in webcams could still spy one them...
If I am in a conference room talking about strategy, an uncovered camera will just pick me up. The microphone will capture everyone’s conversation.
Also what are the chances that a microphone wouldn’t overhear something incriminating even if the camera were covered in your bedroom?
And I am really not trying to go down the road of wondering if you are doing something incriminating in your bedroom and your partner is being completely silent what that implies.....
Beside I'm not sure a "jerking face" would be more than awkward if published. A reverse angle in which you could identify what was the video used for the jerking session would be way more compromising.
And in this regard poorly protected IOT surveillance cameras have way more evil potential that webcam in my opinion.
There’s nothing notable or worse about the Apple issues. If anything, they are probably a lower risk than the average PC.
Most of this stories where not actually happening, I don't remember exactly but I think they came from a single story of targeted hacker attacks where such a thing actually happened and then people got blackmailed.
But it's was more comparable to some rumors which wildly spread and then many non technical people ended up believing and which somewhat had a truth at it's core somewhere so it's not easy to just put it of as "mad up".
Also it happened like a 5+ years ago, it just stuck with a lot of non tech people somehow. And it (normally) doesn't hurt so tech people aren't that likely to tell people that this isn't quite right. It's often already hard enough to convince them to do any privacy focused actions.
Until relatively recently, any userspace app on my computer could freely access the camera and microphone, including background processes and malware, so that feels a lot riskier. There seems to be a permission for this that must be granted in the newer macOS versions, but I assume there might be ways around that.
I could have a System 76 machine with latest xyz hacker proof Linux distro and I'd still assume all was heard and listened to through that device. Just makes no sense to trust any mass production device.
[1] Or least _was_, until I disconnected it - I needed to replace the screen anyway, and I _never_ used the camera, so I just popped the camera out at the same time
I don't see how what you're saying supports that. If your point is simply that Apple has resolved camera vulnerabilities in the past, that's nice, but doesn't exactly give me much peace of mind about future vulnerabilities.
Most webcams do report themselves to the OS while inactive, so they are actually communicating with the system (and thus powered)
No guarantee it can't be hacked again.
Because Apple said so? I simply don't have this level of trust.
Because someone disassembled their MacBook and reverse engineered things? And that person is trustworthy and competent? That is better, but even if it was true for the MacBook they reverse engineered, suppliers make tweaks to parts all the time. Can I be sure that my MacBook still has the exact same camera?
Because you opened up your MacBook to confirm? Maybe then you can trust it.
Apple claims that the LED comes on when the camera is active, which it claims helps protect your privacy. That seems to be true, and certainly no-one seems to have any contradictory examples that are not 12+ years old.
I can argue that when one uses a sliding cover, one can easily forget to reset it after a video chat. The design is bad. The right solution is simply not to have a camera. It's just a different design compromise.
I was the security architect for this feature on recent Macs. The LED is wired to the camera PMIC and is powered by the voltage rail that powers the camera. The PMIC will always remain on if the system has power. Macs newer than 4 or so years also have a feature that forces the LED to stay lit for at least 3 seconds after it has been turned on to prevent the single-frame-grab attack.
prevent? by the time the LED turns on, the attack has already happened.
Do the doors at Apple HQ have locks? Or is there just a little LED next to them that lights up when they open?
I think Apple's building security architect should have a conversation with their camera security architect.
A door without a latch does not prevent an unauthorized person from trespassing. A camera without a cover does not prevent an unauthorized person from trespassing.
Apples webcams are broken by design.
Other companies fixed theirs years ago: https://www.youtube.com/watch?v=37NFVGLX3vw
The point is that the hardware has been designed properly. Combined with the OS-level permissions, it should be assurance enough for the majority of use cases.
If you need further assurances, then by all means, use a physical cover.
Bonus points for using a Sawzall to get started.
At the end of the day, unless you have a really nice microscope, solid understanding of electrical engineering, and a few tens of thousands of hours ahead of you, you have to trust whoever you're buying the hardware from that it will do what they say it will. No amount of hardware efforts can solve the fundamental human trust problem.
/s
So, there's definitely value to a built-in cover; in my case it would stay shut permanently.
Edit: the gnarly thing might be ensuring it doesn't harvest power through data wires or store power in covert capacitors or batteries.
Remember the amount of effort VW was willing to expand to cheat emissions testing.
Source: write firmware for a living, and write drivers for physical switches.
I.e., a traditional switch inline on the circuit(s) connecting the camera / microphone to the rest of the system.
As an analogy, you wouldn't implement a car brake by running it through some firmware. Instead, you'd preferably make a direct physical connection between the pedal and the actual brake.
There are probably other ways. Stop trying to shame people just because you haven't thought of a way to bypass this.
The support document also suggests a paper-thin cover, so it’s not attempting to shame anyone.
Point being that the indicator light can be hacked and isn't too be blindly trusted.
... applies only to older Mac notebooks from like 2008 period which are long since obsolete according to Apple's announced support policy.
>2016: Your Mac’s Camera Can Be Hacked https://www.intego.com/mac-security-blog/your-macs-camera-ca....
... refers specifically the exploit above.
>2016: Former NSA employee: This hack gains access to your Mac's webcam https://www.cnet.com/news/mac-webcam-hack-ex-nsa-employee/
... is an attack that depends on the camera already being in use by another application and therefore has nothing to do with the camera indicator.