Will delay this update as long as possible.
From their opening sentence in that press release. Lol.
Every month.
(Which is still annoying, but not the raw level of frustration that weekly would be.)
MacOS is turning into quite the poo log lately. I respect that Apple has every right to completely destroy the legacy of the Macintosh, but they are slow playing it so that it's just a little bit better than the alternatives. The end result is my life gets just a little bit more difficult with every release.
I feel like the freaking frog on the stove while the water slowly heats up. When is it time to jump out?
And unless that's really recent, no, I have colleagues drop out of Teams meetings to enable microphone or screen sharing access all the time.
The funny thing about this, even on Sonoma - I could click the button to allow it, when it said "restart app" I closed the box (or clicked cancel), and it worked anyway. Specifically, I noticed it more on things like Teams/Zoom where I was doing a screen share, it just "worked" - no need to restart the entire application.
Whenever you feel like it. Just like frogs do:
> While some 19th-century experiments suggested that the underlying premise is true if the heating is sufficiently gradual, according to modern biologists the premise is false: changing location is a natural thermoregulation strategy for frogs and other ectotherms, and is necessary for survival in the wild. A frog that is gradually heated will jump out.
I disagree. Apple's various machinations to control the best available supply lines (deals with TSMC, etc...) make me feel quite entitled in saying what is and is not acceptable behavior on their part. This feeling amplifies with every "courageous" announcement they make sunsetting some useful feature they no longer feel like supporting.
There is a large difference in computing devices versus other simple objects, in that they need software and software can change which is problematic but should not be a problem for the customer/user...
In my opinion Apple is largely failing at providing a worthwhile platform, when they don't just discontinue stuff for their bottom line, most of the changes are for marketing reasons or increasing lockdown to extract more money from customers.
There is not a whole lot of useful stuff that have been added in the last 5 OS iterations but a lot of major annoyance or downgrades/roadblock/complications for usage, etc...
Can someone expand on this? How do you run software that isn't code signed?
https://arstechnica.com/gadgets/2024/08/macos-15-sequoia-mak...
This is one of those features where the benefits seem to very obviously outweigh the drawbacks. 99.9% of users just aren't running unsigned software, so the moment that happens, it is most certainly malware.
If you're developing software yourself, this isn't an issue either, since all the relevant toolchains, debuggers, etc., work just fine under this model. That's a supported workflow. The only thing that isn't supported is downloading some random unverified app bundle from who knows where and treating it as if you could trust it. You 100% can't.
And yes, I also believe that if an OSS project considers "muggles" their target audience, they should prioritize setting up code-signing. Consider it a service to their users. If the fee is a problem, it's important enough to spend the effort to find a way to finance it. If you can't find someone who is willing to put their name on it, you shouldn't ask people to run your software on their machines in the first place.
For me, quite a few? Internal tools at work, open source projects which publish builds on their github, that sort of stuff.
(And no, paying Apple a yearly subscription for the privilege of letting users run an app is not a reasonable expectation of small open source projects)
Problem solved.
I don't really see how the average user is positively affected by these changes - it's not like they will accidentally open terminal and enter random strings infinite monkey theorem style until they hit sudo spctl –master-disable. Ctrl-click was at least possible to stumble over, but I see no good reason not to at least provide a .plist setting to re-enable that behavior. Except to bully more devs into getting signing certs.
These are real, tangible risks.
I can't do the signing as it requires Apple stuff. Not to mention it is unethical to require it as it's used for gatekeeping not just security (requiring Apple to decide if you can run an executable is unacceptable).
Compare it to Android where you can use self-signed certificates and it has an actual function, it allows updates signed with the same certificate to access the existing stored data on the device. It improves security without gatekeeping. At least that was on the older Androids, haven't done work on any newer ones.
I can't do some kind of universal launcher that is signed by me because it would allow to run arbitrary code and therefore it would be banned.
Therefore the only solution is to search for various workarounds (eg. by teaching the users how to run the software) or if not possible anymore stop supporting newer versions of MacOS and rely on web applications to support the platform (like it's the only way on iOS).
Which would be even worse on the desktop as the usability can be quite bad, but at least users would have some chance to use the applications even on their closed system.
Therefore instructions how the users can run the application is the only solution.
Your problems are extremely insignificant in the big picture, where the priority of a serious operating system should be to support regular people in avoiding malware and malicious social engineering. macOS is a general purpose operating system, not a hobbyist or tinkerer OS, and the vast majority of its users are non-technical.
I get that it's annoying, but pushing the work on you is a massive benefit to your users.
It also allows to be used from a C/C++ project so you can do all the required steps, but it's quite more involved compared to simply building the software for all platforms at once.
It's also not related to how popular my language is. It affects any language including C/C++ if you want to have unified cross-compilation to all supported platforms (which is quite typical for any serious project).
You may not be aware but Apple has put roadblocks for such usages as well, you can't rent a Mac VM for automatic builds, it has to be rented for 24 hours at minimum. Using someone's private Mac for building may not be a good idea for various reasons.
And then you compare it to other platforms that don't require anything like this. I even mentioned Android which shows that you can use signing to provide a security aspect without the gatekeeping aspect.
The issue is wider and basically it's an anticompetitive behavior of Apple to any competitor to Xcode.
Enough for this to be annoying. Plenty of tiny tools don't pay for the privilege of doing free work, so aren't signed
> This is one of those features where the benefits seem to very obviously outweigh the drawbacks. 99.9% of users just aren't running unsigned software, so the moment that happens, it is most certainly malware.
You're obviously wrong with your made up stats (you don't need to be a power '1% user to want to install some a single useful unsigned app over the whole lifetime of using a Mac) and ignore the fact that part of the reason why it's 99% and not 88% is precisely because of features like this that make it harder to do so.
But there is an easy way to reconcile - make the old behavior configurable then the imaginary nonexisting 0.0000% users can continue without permanent disruptions
That has never been true. Neither for pro- nor casual users. This might be good for the bottom line of Apple, but I doubt that too, since they squander their reputation. This is non-engineers calling the shots, just like Jobs warned us about.
I do run quite a few unsigned apps and I don't even use a mac that often. This is just stupid...
Link to the talk or interview or whatever where he talks about this?
They have been ratcheting down on freedom in OS X (and then MacOS) since 2011 or so when I stopped using Apple for personal use. The introduction of the Mac App Store, subsequent lackluster performance, and introduction of scary warnings about running unsigned code in MacOS tell most all of the story. This latest update is just another step in that direction, making running unsigned code that much more difficult. The obvious endgame is to raise the next generation of Mac users to only use the Mac App Store for software, effectively replicating the golden goose that the iOS App Store has proven to be.
Some poor schmuck would find a viral comment that said something like "Mark Zuckerberg doesn't want you to know how to get Facebook Premium! Copy and paste this code into your browser, ignore Facebook's warnings, they don't want you to get it for free!" And badabing badaboom, stolen credentials get sent to some server.
I don't work at Apple and can only speculate on their motive, but since I advise my family to use macOS, it's my hope that this change would prevent them from reading something like "download this scary blob and then ctrl+click on it to open it for free Photoshop! Ignore Apple's warning, Adobe has paid them because they don't want you to get it for free!"
It does make it slightly more inconvenient for me, but I think chromedriver may be the only unsigned code that I run regularly.
More and more, I find that these sorts of "we know best" attitudes towards security utterly distasteful and the total opposite of empowering. Infantilizing, more like.
What I'd like is upon setup it asks if this is a dev machine, and change the preferences.
1. Need to disable gatekeeper to run unsigned code. 2. Need an active developer account. 3. You can't run downloaded unsigned code.
Driving them off Mac would be a gigantic mistake that over time would lead to the fading of the whole Apple ecosystem.
I think the mistake already happened, you can see fewer and fewer macOS only software and there is very little in the way of novelty/exclusivity (both iOS/macOS). Devs are now more and platform stuff more and more (mostly web technologies because it makes for good UI even though performance is not the best, it doesn't matter with today's powerful machines.
I'll add that one key point that Apple was better on is becoming very moot: software optimisation (performance and UI) matters a lot less in today's cheap powerful computing. Apple is supposedly selling top of the line hardware but skimping every way possible so in the end, when price matched, competitive hardware does not do worse no matter how bad the softwares are optimized on concurrent platform.
Then the usage of the platform will end for many users & developers. One could still live a quite long time on the older systems to ease the transition out.
I do create macOS binaries, although they mostly are just a byproduct if targeting it is trivial. Of course I do not sign any of them, to me that is more or less a scam comparable to ransomware.
This way I support Windows 2000 or newer, MacOS 10.6+, up to 15 years old Linux distributions with the same small binary for each platform, I did an extra mile in supporting WebAssembly target so it's easy to compile the applications to the web. This also allows to create applications for smartphones without the need for approval and having to follow any weird arbitrary rules.
Why support such old versions? Real world users are often stuck with old versions for various reasons, it's a minority of users but they can be the most important ones. And technically because the difference between these old systems and new systems is not that big. Often it just means to use some older API or do a few extra steps. It's all hidden in code that handles multiplatform stuff so it's not in the way. It doesn't add bloat either.
Well yeah because they are very sensibly doing it extremely slowly. Microsoft is doing the same thing; they're just a fair bit behind Apple.
How often do you have to re-authenticate your existing binaries?
https://cdn.arstechnica.net/wp-content/uploads/2012/07/gatek...
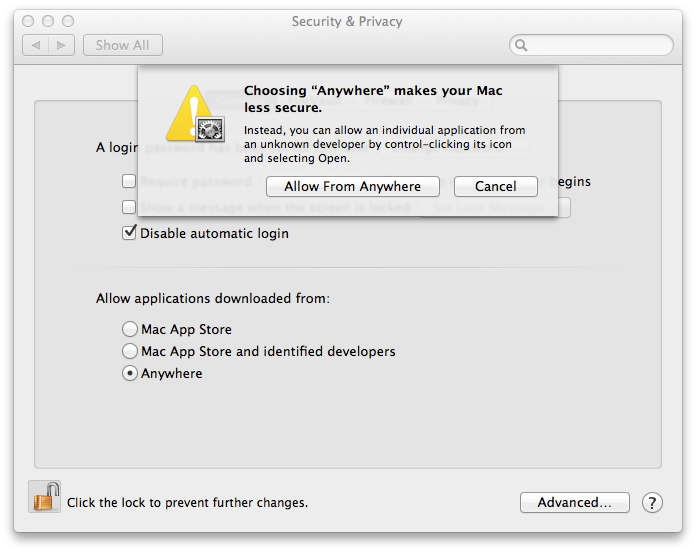
does zoom, chrome, google meet, etc still require this?
I bet I know the answer.
Did this conveniently break Rewind AI?
https://github.com/zackelia/bclm/issues/49
I had to start using it because macOS insisted on keeping my battery charged to 100% no matter what I did, and that can damage the battery.
Additionally, AlDente is even better than the native battery management.
Luckily, I gave 'battery toolkit' a try, and it has been working great:
Some app tries to open a file and fails. Doesn't tell me what the file name is. I just want to see the open() call.
The screen recording permission thing also doesn't help since I'm using Ice (https://github.com/jordanbaird/Ice) because somehow Apple still can't Sherlock this feature.
For non-technical users the choice is simple: either Apple decides what is allowed to run on their computer or cybercriminals do. After years of getting burned, non-technical users made their choice. I think it was the right one but the jury's still out for the future.
Perhaps one day these users will get squeezed out of computing entirely. That will be a terrible shame. The same thing is playing out with everything else though. Look at cars and household appliances.
The notion that you can reasonably have knowledge of and control over all the software that is actually running on your machine has not been realistic for decades.
My Windows 10 box became so bogged down that I was convinced it was running some undetectable malware. AV detected nothing, but after a critical look at open ports I just decided to wipe and go to Windows 11.
Here are some of the biggest risks today. Running third-party apps at all, unless they are absolutely necessary. I try to do everything possible with Google-provided apps within the Google ecosystem on my Android phone and the other devices as well, which limits the third-party attack surfaces. My Windows machine runs practically nothing outside of MS or Google. I don't need to.
Other big threats are beyond personal devices at this point. Connecting third-party SaaS to your accounts is a real problem. Facebook, Google Workspace, Slack, GitHub, any service that acts as a platform and runs third-party integrations, that's where you'll get bitten nowadays, and your local AV scans are powerless to shield you from footguns. Just to use HP printer features, HP wanted full, unscoped, read/write/delete access to my Google Drive!
Everyone's "hacked Facebook account" has really been just some stupid game that went rogue. Supply-chain attacks through browser extensions and the rest. Extremely difficult to police from the end-user's position, but deadly and dangerous, because they're out on the net and in the cloud.
The level of difficulty is absolutely intentional. For you, it's a small speed bump. For the guy on the phone with my grandma trying to hack her computer, it's more of a hill to climb.
And even if, we had issue with malware infecting iPhones like Pegasus. Locking down environments with these specific mechanisms isn't improving security.
>Building from source takes a long time, is prone to failure, and is not supported.
Having issues building your Homebrew packages from source? Well, you better not take it to the bug tracker.
I don't think it means that at all. They're both clearly supported by homebrew — one just happens to be the default. You can always use -s or --build-from-source to build whatever package you are installing.
(Ignoring the packages that are just wrappers around closed source software and fetch binaries whether you compile from source or not. Those are the exception, not the rule.)
I can run any open-source software I want. Other people can't run my precompiled binaries unless I opt into an attestation system that lets the OS respond to and pre-emptively block binaries from developers found to be issuing malware. Open source is unaffected.
I seriously fail to see what is wrong here.
Once you need to be in the apple developer program to build and run from source or something, that’ll be a legitimate nightmare. But we’re nowhere near that yet.
When Quarantine was released in Leopard, and Gatekeeper in Lion, and System Integrity Protection in El Capitan, and then "Allow from Anywhere" was removed as an option in Sierra... Each time, people were saying similar things. "Yea, it's bad, and it's getting consistently worse with every release, but surely we are nowhere near 'really bad' yet!"
What is the security benefit of removing the command-click shortcut?
That said there’s no reason they couldn’t have fixed either of those issues instead
Simultaneously, while the user interface of macOS has converged on iOS over the last half dozen releases and the ecosystems are more tightly integrated, not a single one of these changes has gotten in the way of developers running their own code. The situation now is no different than it was in 2006, for example. What has been made more difficult is running untrusted binaries downloaded from the internet. That's not the same thing.
This is the case for building and running things with restricted entitlements and system extensions.
Unless you disable system integrity protection entirely, which locks you out of your purchased App Store software, DRM content, etc.
Looks like there might be a way of achieving the same thing through the GUI? https://www.reddit.com/r/MacOSBeta/comments/1e2xlcg/disablin...
[1]: https://www.reddit.com/r/hackintosh/comments/1fh5wez/cant_di...
Also false. But Apple's glad you believe in that.
[1] https://github.com/cormiertyshawn895/RecordingIndicatorUtili...
IMHO there's a huge difference between no freedom for anyone (iOS) and secure-by-default, freedom only for powerusers (macOS / Android / Chromebooks / ARM Windows devices) ¯\_(ツ)_/¯
Not that Microsoft doesn't salivate about such "improvements" as well.
It’s fine to let the experts worry about securing our systems. The Internet is safer for it. And it’s fine to not think so, too. But for those people, realize that the product may not be for you. That’s why we have a dozen flavors of Linux.
But maybe I’m just getting old.
So the category of software will still have some working entries (existing players will try to get approved, and probably will), but it's hard to imagine anyone will want to build a new one knowing its viability on modern macOS completely depends on filling out a form and hoping Apple's approval bureaucracy likes you.
Anyone who's used these unusually locked down entitlements know whether you can apply for it before building the software, or if App Review needs to have their hands on something functional first to approve it?
As the hardware iShittification continued, macOS too was also being slowly stripped of features to ensure Apple controlled your data and what you could run on it. Support for independent Kernel extension (outside of Apple's control) was removed mainly to cripple existing independent Application Firewall and virtualisation software. Apple-made OS APIs for these were integrated to the newer macOS and offered as replacement to ensure Apple controlled how Application Firewalls and Virtualisations should / would work on macOS. (Such restriction on the kernel extensions for independent system developers is also meant to prevent support for other filesystem, like ZFS for example - the OpenZFS project is maturing fast on Linux, Windows and macOS and can be a game changer as its usage has the potential to "free" our data from a closed and controlling ecosystem, to be used on any platform of our choice.
Whether you are a developer or a user, a "consumer relationship" with Apple feels like a relationship with a controlling and abusive spouse who repeatedly gaslights you that you are imagining things and are the one at fault because "you just don't understand them".
Is the gist of it that it got locked down more?
1. Screen-recording permission once every week ?
2. No more sudo spctl —master-disable. Alternative way is bit complicated.
2. No more control+ click to bypass gatekeeper.
3. Why tcutil reset Accessibility not working for a specific app? It works for “All” .
4. Script to convert NSURL node ref url to posix url not working.
5. Normal usb Mouse pointer acceleration is not smooth. May be need to re tweak those again.
Anything else ? Otherwise all good.