For members of a relatively well-paid profession earning good wages from creating software, I wonder if the reluctance to support others earning money for quality work isn’t some form of cognitive dissonance.
// Pre-emptive “edit” before this comment has replies: Folks post a lot of arguments for “free” software any time there’s a comment such as mine — but justifications largely feel like post-hoc rationalizations conflating freedom of information and ideas with freedom from paying for value, ret-con’d stories we tell ourselves. I call BS — unless one is independently wealthy, to spend maker time on art or craft requires one to either earn money or enjoy patronage. Tools for work are more craft than art, and deserve to earn, especially as patronage or maker communes are in short supply. Not to mention the exercise of ethnocentric privilege implicit in demanding something of quality in exchange for nothing assured.
I absolutely would try to hook users on any SaaS. However, I go out of my way to avoid such products. If I can pay for them once, I much prefer it. (For something like jetbrains, I'm okay with a renewal fee because if I choose not to pay it, I can still use the older version.)
I make an exception for Bitwarden because I like the idea of my password manager having continual security updates. However, it's one of the most frustrating parts of the webification of services - I want to pay for things once, and choose if I want the expanded features at any given time.
I can tell you a "secret" you can download any version of 1Password, including version 3 from this website: https://app-updates.agilebits.com/
If password managers don't (or shouldn't) have an attack surface, what could (or should)?
I could also describe all the data that google stores as "just a password protected DB with a web GUI"
110% agreement.
Further, the only thing I like less than subscriptions is IAP not of new feature sets but ‘pay-to-play’ where the mechanics of use are negatively distorted to gamify purchase impulse.
I’ve argued — here, since inception of IAP on Apple’s app store — that the worst thing Apple has done to consumers was normalize removing the ability to show only single purchase paid apps in the app store. An vast class of less fortunate consumers either resign to less utility or waste time on an artificial “grind”, to encourage another class of “whale” to drive corporate revenues.
I don’t mind extracting cash from whales who can afford it. I do have a problem inflicting artificial digital scarcity of utility or enjoyment on the masses to create the ‘hook’ for whales.
As for subscriptions, it’s not clear to me that the treadmill of software/hardware upgrades is benefiting core use cases.
I like paying for generational or disruptive change, “voting with my wallet” on what’s of worth to me, but after a couple decades of purchasing generations of Adobe software only when the features mattered to my work, I moved from Adobe to e.g. Affinity and feature sets I own instead of rent when these recurring subscriptions don’t appear to meaningfully benefit my productivity or output.
For instance, it’s remarkable to me how similar the principles are between today’s (re-)emergence of Markdown for document composition and the early WordStar / WordPerfect / AppleWriter tools of the 80’s. I also like the experimentation by these Makers in ability to purchase a ‘pinned’ feature set, or support ongoing refinement. (Editors whether text or code, like JetBrains mentioned, seem to have a jump on this clever — and rare positive — use of IAP.) It’s difficult to show what increased utility of word processing has come from the most recent 20 years of paying for word processing upgrades. Today’s dev efforts suggest the sweet spot may be 30 years back.
The flip side of this, economic models are still dissatisfying for affordability of basic bricks and mortar world rights such as housing. The least worst answer appears to be rent (with a dystopian jag into ad-supported!), and it may be the least worst for software is rent as well.
Except when the ongoing annual software rents have risen to the same cost as one-time purchase (again, Adobe!), contrary to bricks and mortar where the over under is often 7 years of possession and use.
Back to artificial digital scarcity — I’m concerned that advertiser funded access to quality writing is losing ground to monthly subscriptions for content. Are less fortunate kids going to be able to subscribe to NY Times, WaPo, Atlantic, Guardian, National Review, American Spectator, and so on, for $5 a month each? (News aggregations such as Next Issue could resolve this, but even as Apple’s “News+” this struggles.) Even more dissatisfying when a print publication goes down the same path as cable, first charging for something that was free, then eventually layering in the same ad content as when it was free.
Artificial scarcity based IAP, data-broker supported (ad supported is fine, individual data for content is not), and the descent into the ironic sounding “gacha” model for software or content happy meals (utilities, clickers, news, etc.) — something thoughtful has to shift before we’re living in a future less Roddenberry than Idiocracy.
It's about freedom, not about price.
I will not shape my life and habits around software that can be discontinued, or suddenly changed so much that it breaks my workflows. I will not use software with proprietary formats or which has dependencies on external "cloud" services that can go away at any moment. I don't need that kind of aggravation.
Happy to pay any reasonable (or even slightly unreasonable) money for software, not an issue. Sell me each version as a stand-alone application that I can run forever without any external dependencies and I'll pay for it.
Try to lock me into a subscription model and/or make the functionality dependent on an external server, that'll be a hard No. Even if free.
I’ve found enough bugs in the Mac product that I assume there are security issues I’m not aware of.
If you needed it on both Mac and Windows, the subscription was cheaper.
The $2 billion valuation of 1password tells the entire story. They’re overcharging for what they’re providing and I think tech people can “feel” that which is why tech communities hate the subscription BS.
By your argument why can’t I buy that and self-host it too, decide if I want to upgrade for more features myself?
I also think $5/mo for 1Password for Families is incredible value. Zero regrets on paying for this because it meaningfully enhances my families personal security posture through elimination of reused credentials and enabling TOTP (sharing of code generation) on many sites we use, that it is cross-platform so no excuses for everyone to not use it, and the UX is so simple you don’t need to be “tech people” to succeed.
How much you charge and how you charge is definitely divisive, but 1Password feels very much on the cheaper end of the spectrum, not “overcharging”, heck Discord Nitro is $5 (Classic) or $10 and gets you very little by comparison IMO.
>enabling TOTP (sharing of code generation) on many sites we use
Are you generating TOTP codes via 1Password or something? That seems like a degradation of security. I did a cursorary search and didn't find mention of 1Password providing such a "service".
It isn’t a degradation of security, in my opinion, it’s an upgrade, when certain accounts are involved.
For these shared accounts, such as those used by my family, and on services which don’t support account-per-person in an “organization” or “household” sense, this still provides for TOTP in a way my spouse and I can both login. Ensuring just the loss of the password isn’t enough to compromise the account is an upgrade vs. not having TOTP enabled.
Where we can both have our own accounts and use U2F tokens that’s a better story, clearly, but 1Password having this functionality is great!
Even by that blog post, they have to go out of their way and clarify that using this feature means you are not longer using two-factor authentication.
Yep! People see open source as a goal, rather than a sustainable product being a goal.
GP here. I agree that all software developers and maintainers need to earn an income for their work. It's just that you don't know my circumstances, my geographic location, and the constraints I have to deal with when posing such a question. Believe me when I say that I have some real constraints that cannot be surmounted on this particular front. I don't like my circumstances, but that's just how things are right now and there's nothing I can do about it.
https://www.bleepingcomputer.com/news/security/-particle-chr...
The technology to store passwords safely has a marginal cost of zero (it's software). People storing passwords in third party places increases the threat surface, always. Finally, it's "ecological" in that safety/security of this sort needs to be evenly distributed to work its best.
I'm not saying we shouldn't pay people to make things safer, we absolutely should. But this is a bad model for it.
Though there's enough potential public harm such that looking at "public health" models is not a bad idea. Most places you don't have to pull out your wallet to get a Covid vaccine, you shouldn't have to pull out your wallet to get good password safety, for roughly the same reasons -- the harm from one "infection" can spread quickly.
> relatively well-paid profession earning good wages from creating software
AFAIK 1password doesn't practice location-based pricing, so how can you assume that "relatively well paid" people from different geographies of the world can all find it affordable?
Whoa! Knowing nothing about the OP you assume that he is the member of the oppressing class clamoring for the output of his slaves? And, since you're writing this in English, I think it's safe to guess you're assuming the person you're attacking is a white, so you're basically accusing this guy of being an entitled white who can't give up his slave labor
I was with you on the rest of the post but charges of "ethnocentric privilege" are a weird, racist escalation hiding in academic terminology there bud
Occam's Razor applies here: everybody likes free shit. This isn't a property unique to the evil whites
Specifically:
>In common usage, it can also simply mean any culturally biased judgment.
Also relating to the "Global North" (who it's very likely that any given poster here belongs to) and "Global South", which don't have anything to do with skin color.
Given you've created a throw-away to comment this, I suspect you know you're actually the one making a "weird escalation" and are aware that you're race-baiting in a non-genuine manner.
1Password recently raised $100 million at a $2 billion valuation.
Looks like they're going down the Dropbox path. Shame as 1Password used to be one of my favorite apps.
Source: https://1password.community/discussion/115018/support-for-lo...
My biggest complaint about the 1Password8 situation is that i've been "self hosting" version 7 for years using iCloud sync, and it has worked perfectly. I have my 1Password vault on every device for "free". With family sharing in iTunes, i had it for every family member for "free" as well.
With version 8 they're taking that away, and instead trying to push me to a $5/month subscription that essentially does the same thing.
I have faithfully purchased every version up until now, and had they kept local vaults/iCloud sync i would have purchased the next one as well. As it is now, self-hosted or not, i will be looking for something else. Afterall, all i really need is an encrypted file on a cloud share.
Unix Pass would be great if it didn't leak information about which sites you have logins for. "Easily" fixable by using Pass Tomb, but sadly that's not available on iOS.
Having said, I'm all for self-hosting and I hope it continues to become prevalent.
Most people have no clue about the amount of work required to runs things in a secure, redundant and resilient way. And no, a RaspberryPi in the corner, running on your LAN probably won't cut it. At least not for me.
I moved from 1Password, and my main gripe with Bitwarden are the apps aren't as polished. If it's not too expensive I'd consider switching back (1Password family is $60 per year, so I assume this will be less).
The most glaring issue (for me, anyway; I fully understand I'm just a sample size of 1!) they have is relying on the pop-up UI of the browser, which I guess is stateless (state is lost when the popup closes, it seems?). The decision of using this UI was already wrong from its inception, IMHO, not sure why they thought it would be a good idea. But more surprising is that they haven't yet moved to the much more reliable and user friendly method of opening their UI on a new tab, which was a no brainer when using LastPass. Oh well. They said to have this in the backlog, so hopefully it gets some attention sooner than later... but in the meantime the end users are faced with silly issues like this, software that loses user data should not be a concern in the first place, and for sure they won't care about some technical explanation about how the browser handles pop-up windows.
(for anyone interested: https://community.bitwarden.com/t/persist-bitwarden-ui-and-m...)
(he recommends using your browser's built-in password manager, which isn't as convenient but is much more secure)
Basically, I want the browsers to implement something close to what Apple has for password management on iOS. Ideally go a bit further and expose hooks for creating/saving a new login, too.
Unless they already do this, and nobody has actually taken them up on using it?
But this whole proposition totally breaks if I store my Amazon password in Chrome at work, and then later I cannot access it in Firefox at home, or the native app in my Android phone.
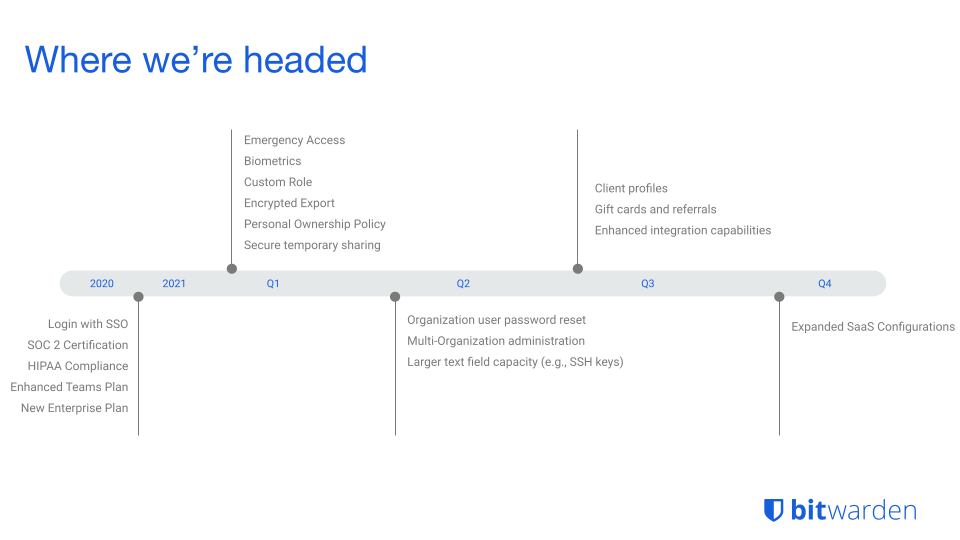
The one killer feature which is preventing me from switching is the ability to use multiple self-hosted servers at once (so I can separate family vaults from business) [1], but "client profiles" are likely to be implemented some time soon [2].
Now that I've learnt that local vaults are going away in 1Password 8 [3], I'll probably make a move to Bitwarden sooner rather than later.
[1] https://community.bitwarden.com/t/log-in-with-multiple-bitwa...
[2] https://community.bitwarden.com/uploads/default/original/2X/...
- Firefox Extension doesn't work fully in a private window in Firefox.
- Extension loses data when you click away from it.
- Extension is hard to navigate using keyboard - e.g. there is no way to copy specific username/password/otp code.
There is lots more issues.
I'm just really grateful this project exists. I've tried most of the major password managers out there and I feel like BW/VW is the clear winner, especially if you're willing to host your own server. If not, their pricing for an annual personal account is incredibly reasonable.
1 - https://keepassxc.org/docs/KeePassXC_UserGuide.html#_databas...
I don't want to selfhost anything. I've spend enough years doing that. All i really need is an encrypted file that can be synchronized using a cloud of my choice.
For a while, I used KeePassXC work my encrypted database file checked into my Dropbox storage. That allowed me to sync my passwords between devices but not give the cloud provider any way of knowing the passwords (since my KeePassXC master password was not stored anywhere besides in my brain). Unfortunately, Dropbox eventually changed their Android app so that synced files no longer were stored on the local filesystem, so adding a new password from Android or getting the new passwords from other devices would require manually uploading/downloading the file through the Dropbox app. I somewhat suspect this change was due to Dropbox eventually adding their own password management functionality to the app, but I didn't consider that until later, so I'm not sure how the timings lined up. In age case, after weighing my options I ended up deciding to just switch over to Bitwarden. (The migration was extremely easy; I was able to export the KeePassXC database file locally to XML file and then import that into my newly-creates Bitwarden account without any issues).
How does Bitwarden compare to Keepass?
1. Mobile is paid I think
2. Not open source
Now the same deal is $80 which I think is still ok but on the high side.
I like their hands off approach. Password autofill/save etc are also far better than most other password managers (esp bitwarden).
“Enpass lifetime premium: $79.99”
- self-hosted on docker
- mobile app and browser extension
- sharing secrets and storing files
- api
Is it really worth your time forking it to remove licence checks, when you could instead support the developers and not need to make any code changes?
Forking the code and removing licencing checks is perfectly permissible under the GPL. But it's pretty unreasonable in this case.
> but it seems to have some license purchase requirements even for the self-hosted options
which doesn't appear to be completely true, regardless of whether you think it's worth your time or or reasonable.
The license check is relatively easy to bypass, and there are also forks and reimplementations out there that already do so.
I do wonder how the licensing and pricing will be handled though.
Bitwarden officially allows self-hosting for the personal use tiers, but it seems to have some license purchase requirements even for the self-hosted options (other than the free tier).
Is there any password management application out there that makes sharing passwords or password vaults easy but is also free? I’ve looked at KeePassXC and Bitwarden. The former isn’t easy to use for sharing and sharing permissions. The latter doesn’t offer sharing among more than two people in the free tier.