It wouldn't surprise me if a lot of Twitter support people had access to these tools and that they often worked with larger (more valuable) accounts.
It also wouldn't surprise me if some employee had a bad 1:1 and then responded to a spear fish just because they were disgruntled. To take payment for it is particularly stupid.
Of course, could also be something more serious - but if it's really just the BTC piece and the people are dumb enough to talk to the press, it may not be a group of criminal masterminds.
I hope for the employee's sake they have communication that can help the feds catch the BTC group. Either way, an incredibly stupid thing to do on their part and I don't see a good ending for them.
If this turns out to be true, they'd be lucky not to go to prison.
Twitter is a disaster waiting to happen.
I can't think of any serious risk posed by 'the general population'. Maybe particular stocks would dip a bit?
People's accounts get hacked all the time. To help them recover is often a manual process, because the true owner of the account can become unclear. To be able to do that a support worker must be able to change the email address on an account, undo 2FA settings and make other changes because hackers will typically change the email address and add 2FA of their own phone as the first step in an account takeover.
If you're a sysadmin on a company email system, then you do technically have access to everyone's data on that system.
However, you're generally limited by company policy that you are not permitted to access/modify that data without direct authorisation, say from the employee themselves or from HR.
So, therefore, if you go and read the email of your boss, you're still in breach because you didn't have the authorisation.
The only item I can see here is fraud (impersonating the people whose accounts have been taken over), of which the mole would be complicit.
That's been exceptionally controversial, as it can turn contract breach into a federal criminal offence in the US.
Doesn't something similar happen with employer-provided accommodation and burglary laws?
I’m not sure what you’d charge them with?
I know HN doesn't believe in laws, but the rest of the world does, and they're the ones with prosecutors.
Parting shot: unnecessary, obnoxious. -1
Net: 0
They could argue, with the advent of remote working getting more and more predominant, that they simply left their computer unattended for a second while logged in.
Beyond that, they could argue they simply clicked on a link and something might have happened they aren't aware of. Or that they didn't know what running that one executable would do.
People seem to assume everyone takes tweets at face value and won't do a double take when it doesn't sound like something they would normally say.
Even here there was plenty of people on HN who were claiming outlandish possibilities while it was happening.
e.g., Vietnam is a livable place and GDP per capita is ~$2600. That'd get you a very modest living. GDP/capita is also up 2x from 10 years ago and 10x from 20 years ago. You could maybe squeak out 20 years with very modest living and few unplanned expenses and assuming the economy and thus cost of living doesn't grow tremendously (like it likely will).
Somalia would give you a little more value for your money. But I think if someone suddenly had that much money in Somalia, they'd probably be getting out of Somalia or hoping nobody found out.
Poorly executed, frankly. The tweet just wreaked of spam.
Almost anything else I can think of would require either (a) substansal amount of starting cash (for example trying to crash Tesla's stock price), or (b) be almost impossible to pull off without getting caught (blackmail, or again stock manipulation if you do it in a big enough way to make some decent money).
In terms of risk/reward, assuming someone found some easy trick and wanted to cash out ASAP, this feels like the best option.
Alternatively, is it possible they bought options on twitter itself? It’s down 4% in after-hours (which is less than I expected, but still enough delta to make some cash).
On the other hand, $1M in BTC might do the trick. Interesting thought experiment...
And you're also making the assumption that the accomplice thought about it rationally. All the attacker has to do is find someone who doesn't realize that they will get caught.
And/or they just thought it couldn't be traced back to them.
If that was the case they could only deal with bitcoin. Blackmailing with bitcoin may be smarter but maybe they figured that would be investigated more or treated more harshly? They could have released fake financial tweets and shorted the market - but that still would be investigated much faster.
I'm sure the 100k or whatever they got isn't as much as it could be - but for a random dude who paid 10k to a disgruntled employee it is pretty good.
I don't think there is something super nefarious involved. Probably some unpaid intern in a third world country where Twitter outsources tech support.
If the attackers had a big short position in TWTR, they may have made a lot more money than they received from BTC.
Also, if you had Elon tweet that, I am not sure if the price will go up or down like you expect. :)
Oddly enough, posting the screenshots resulted in some users getting their account suspended or Twitter pulling the picture down.
[0]: https://video-images.vice.com/test-uploads/_uncategorized/15...
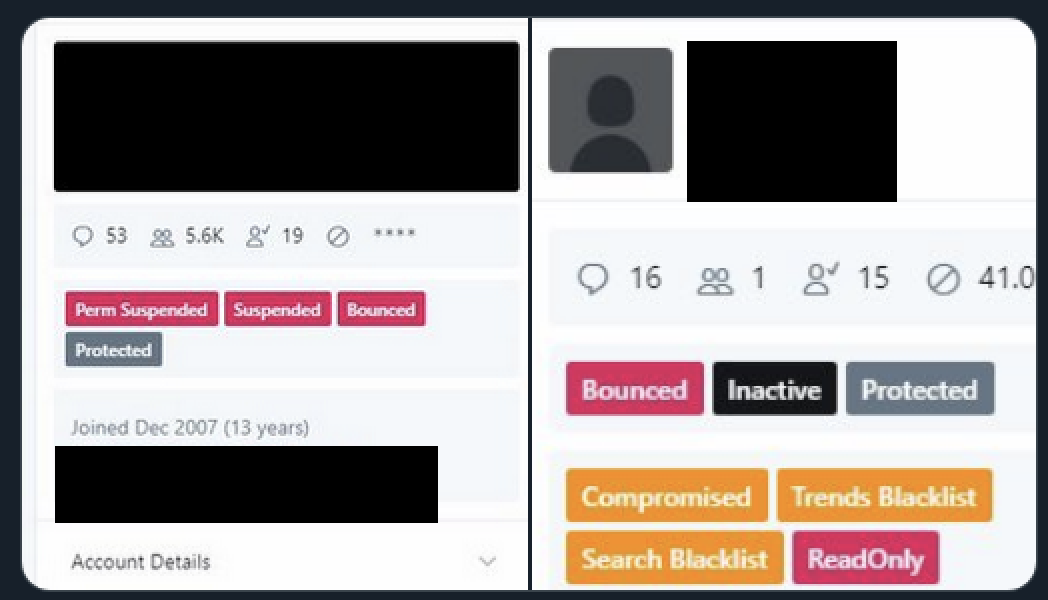
Apparently sworn statements have been made about this.
[0]: https://blog.twitter.com/en_us/topics/company/2018/Setting-t...
This doesn't seem to contradict what's shown in the screenshot (which only shows blocking from the search and trends page).
Also what do people consider as a shadow ban?
- Removing the tweets from people’s feeds, and only showing them if you browse/go to the offending users profile ? (Personally I don’t think this counts as a shadow ban)
- The offending user is the only person who can see their tweets, even if other users look at their profile (This is shadow banning imo)
That being said, what was the employee's endgame here?
Especially if the real motivation is not the BTC scam, but the access to who knows how many DMs for possibly blackmail/propaganda down the line. (And not necessarily just DMs from the known compromised accounts, either.)
General disgruntlement maybe? Maybe they were simply pissed off and looking for a way to hurt the company.
Sometimes people behave very irrationally. In the most sensational cases that manifests as violence, but I think it might also manifest as acts of sabotage.
Such social media platforms have to be tamper proof even from the CTO, the reddit incident proved that years ago.
This is going to hurt their credibility hard in the run up to the election.
The tool in question is likely used by low level support/abuse control workers. The huge pressure put on social media firms by liberals in recent years to crack down on "abuse", "hate" etc means they need a vast army of people to review complaints about harassment, "fake news", account hijacking etc. Those employees aren't all sitting in expensive San Francisco on a corp VPN, are they? They're probably going to be in places like India.
From the mention of BeyondCorp, it feels like there are a lot of Googlers in this thread who aren't really familiar with how Google handled the same problem, or at least, used to. For example back when Orkut was big there were huge numbers of people in Brazil who had the power to censor content, ban users, handle victims of phishing and so on. It was the only way to scale the moderation users and governments there demanded.
An ideal user admin tool is very fine grained. But once account hijacking entered the picture, it gets hard to truly restrict takeover permissions to a tiny number of people, because accounts are constantly being taken over by third parties and need to be reset back to the true owner via manual intervention. Attempts to automatically handle that are very hard, I know from experience. Hackers like to abuse any system put in place to stop them taking over accounts (like 2FA) to stop the true owner taking it back once captured.
Some of the scuttlebutt says that these guys are tied to multiple crypto hacks.
But my personal opinion is that this is just a 20-something trying to make a mark for themselves. We'll see within a week or two.
Without this bit of information from Vice it would make what Twitter officially posted downright scary and not add any comfort factor to what the heck is really going on.
> we spoke to two hackers and we were able to independently verify they were in control of hijacked accounts today. One of them said they paid the Twitter employee to help them take over accounts; not sure on the specifics here at the moment
https://twitter.com/jason_koebler/status/1283594885292077056