You're reading hackernews, you're not an average iPhone user. The Project Zero announcement was sensationalized - press is good for them. It was then picked up and further sensationalized by large news outlets whose readers are nowhere near as technically literate as HN's audience is.
They didn't understand what was being written other than "zomg, website can hax my entire phone and could've for two years, I assume all my data is on the darkweb".
The nuance, and details were completely lost to an average iPhone user.
Google has some responsibility when identifying flaws in consumer devices and software to be more clear about the actual impact, ramifications, and likelihood that your device was compromised.
https://googleprojectzero.blogspot.com/2019/08/a-very-deep-d...
"Earlier this year Google's Threat Analysis Group (TAG) discovered a small collection of hacked websites."
"We estimate that these sites receive thousands of visitors per week."
"TAG was able to collect five separate, complete and unique iPhone exploit chains, covering almost every version from iOS 10 through to the latest version of iOS 12. This indicated a group making a sustained effort to hack the users of iPhones in certain communities over a period of at least two years."
Google was responsible in identifying estimated scope. They didn't say it was widespread or impacting millions of devices. And that there are vulnerabilities of 2 years worth of iOS versions is pretty reasonable evidence that this has been a 2 year project.
Meanwhile Apple's counter-claims sound like pure damage control with no supporting evidence. They claim it was only operational for 2 months. Yet they provide no justification or evidence for that claim. They are in no position to monitor what happens on the web as they don't crawl it, and don't even attempt to explain why there would be exploits for 2 years of OS versions if this was only operational for 2 months.
But I'm not seeing any reason to believe Google was anything but responsible in its disclosure, nor that they sensationalized it in any way.
I agree. Google provided ample evidence why they believe the websites must have been exploiting phones for about 2 years (https://1.bp.blogspot.com/-97vEtS5TpiM/XWfds8hYAyI/AAAAAAAAN...). Meanwhile Apple appear to be playing down the severity of all this with zero evidence.
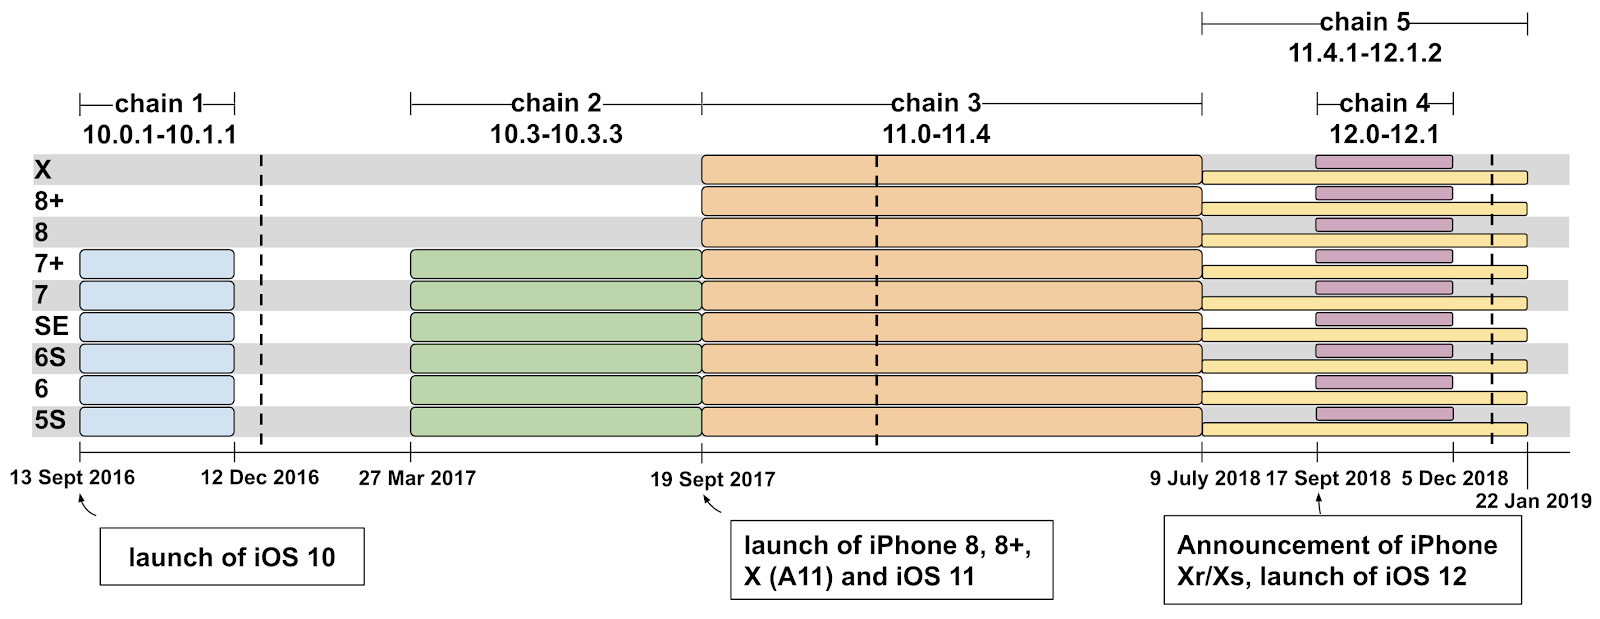
Chain 1: iOS 10 launched 13 Sep 2016 and 10.1.1 lost relevance when 10.2 was launched on 12 Dec 2016
Chain 2: iOS 10.3 was launched 27 Mar 2017 and lost relevance when iOS 11 was launched on 19 Sep 2017.
Chain 3: iOS 11 was launched 19 Sep 2017 and lost relevance with the release of iOS 11.4.1 on 9 July 2018
Chain 5: iOS 11.4.1 was launched on 9 July 2018 and worked until the release of 12.1.3 on 22 Jan 2019.
Chain 4: iOS 12 was launched 17 Sep 2018 and worked until 12.1.1 which was released on 5 Dec 2018.
The span of dates during which a particular version of iOS was the latest release does not necessarily mean that exploit chain was active contemporaneously. I can think of several reasons for someone to be unable to upgrade to the latest version of iOS, requiring an attacker to maintain and deploy exploit chains for multiple versions of iOS simultaneously.
1) Apple has historically dropped support for older iPhones with each new iOS major version.
2) Users who jailbreak tend to refuse to update until a jailbreak emerges for the new version.
3) Some users are slow to update
4) Some users might just refuse to update
Because of this reasoning I find it plausible that Apple only has evidence that the exploit chains were active for only two months and that the attacker chose to deploy the five chains for only two months. I do not find Google's chart insightful for understanding this attack.
Also, note that the exploit used in chain 4 was unpatched when Google discovered it. It looks like the reason it doesn't support newer iOS versions is because they abandoned it in favour of the cleaner chain 5, which entirely obsoletes it in terms of versions and devices targeted. Just this pair of exploits alone suggest that the attack was live in the wild for at least a year.
In theory I suspect that most recent exploit could be backported to cover all the iOS versions covered by all the other exploits too (and some they missed) but they just didn't bother.
I guess Apple could go back and look at their crash report telemetries to determine when the exploits were active. Google doesn't have that type of historical data for iOS devices. Of course there were no mentions of that as evidence.
E.g. once an exploit is detected by Apple, you might as well use it. Or an exploit that only relevant to an iOS version with low install base - just use it.
My thought was that they could be to target old versions, even if the site is new, but if the new exploits work on old versions that seems unlikely (though it could be to limit the exposure of the new zero-day - fingerprint an old version, present an old exploit - but if the exploits are new, that seems like a lot of work for next-to-no benefit).
That would make a lot of sense if we were talking about Android but how many iOS devices are still on iOS 10? Apple's stats show 97% of devices are iOS 11+ ( https://developer.apple.com/support/app-store/ ). It seems rather unlikely that someone would invest in finding & weaponizing a zero-day exploit against iOS 10 for less than 3% of users. Possible, sure, but Apple's claims needs evidence here.
I don't think that's Google's job at all, especially for a competitor's product.
Their project is to identify security vulnerabilities and disclose them to the public, in the name of public interest. We always have to assume worst case for security vulnerabilities, it's kind of the whole job of being a security researcher to determine what could have happened. Their job isn't to make Apple's users feel better.
It's also not Google's fault that media known for being wildly off-base when reporting on technical news was predictably off-base again.
To be credible, it would be especially true for a competitors product. If you're even remotely insinuating that they can or should go softer on themselves than others, they're 100% not credible, and that would only make Apple's stance that much more legitimate. If they aren't at least as tough on themselves - and they should probably be tougher on themselves than others - it's just a marketing team.
But I do think they have that responsibility. Disclosing flaws and vulnerabilities for consumer use cases requires nuance and less "just the facts, ma'am" otherwise you're actually doing more harm than good.
The stories will be blown out of proportion, and the world will go numb to them. Because the little, low impact issues are constant background noise - when they get blown out of proportion and 0.000001% are affected, and 90%+ were patched 6 months ago, all this does is contribute to the noise, and doesn't improve the signal.
At this point, I don't think it matter much to the typical consumer. Both camps have their fair share of zealots, and short of a press release stating something horrific, most people don't care to switch to the other side. iOS users claim superiority for their device features like iMessage, cameras, and UX, while Android users pretend like their device is for the technologically enlightened.
Credibility in a report like this is a non-issue for most users. It's not about responsible disclosure, facts, and the truth. It's about marketing.
It's funny how their public interest seems to stop at the line where Google looks good and their competitors look bad.
I would say that their public interest mission should include not inciting unnecessary mass panic by exaggerating claims or by using imprecise language that would allow the media to make exaggerated claims.
You know, like how they use much more toned down rhetoric when releasing info on Android bugs.
Maybe this sensationalism furthers the public interest by turning software security into a weird zero-sum game where every company is trying to break their competitors products. But I can also see how cases like this creat a negativity that prevents companies from collaborating to fundamentally improve security.
The security community works like this (public responsible disclosure), _because_ companies overwhelmingly proved that they couldn't be trusted to collaborate with security researchers.
That’s not what the Apple press release says. It says that it took them 10 days from when they learned about the bugs until they had “resolve[d] the issue” (fix implemented? released?).
Presumably Google contacted them sometime in between when Apple first learned about the bugs and when they finished fixing them.
This isn't a Maybe. Narrowing in on the statement of fact "where every company is trying to break their competitors products," query Ben Hawkes of Project Zero for an exact quote, but this about 100% lines up with it.
Here's one: https://www.vice.com/en_us/article/mbmgqp/this-is-worst-year...
The general population is completely burnt out about security stuff -- they hear about their bank getting hacked and releasing all their records like twice a year now. No one "panics" over that anymore either. This is no different, if they'll even be able to recall them being separate events a year from now.
https://arstechnica.com/information-technology/2019/09/andro...
Waiting for the patch to come to my devices...
And the 5 post write up on the PZ blog.
Security with mobile devices is definitely a don't throw stones in glass houses situation.
And in the past they've definitely written posts on issues that only affect Android (as far as mobile goes), like their super deep dive into remote broadcom wireless exploits.
https://googleprojectzero.blogspot.com/2017/04/over-air-expl...
> A partial list of devices which make use of this platform includes the Nexus 5, 6 and 6P, most Samsung flagship devices, and all iPhones since the iPhone 4.
I think that any level of care they would take in describing the impact of a flaw in their own product, ethically, the same level care must be taken when describing the impact of security flaws in a competitor’s product.
Otherwise this goes from white-hat to grey-hat hacking, and it serves to undermine the stated goals and intentions of Project Zero.
If they want security professionals to pay attention to them, it is.
I accept that maybe P0 just didn't carefully think through what they were saying; they've been straight shooters in the past. But the definitely gave both a misleading impression about the situation they described _and_ downplayed other risks.
If that keeps happening, I (for one) will end up treating them more like Oracle's security/marketing department. And that would be a serious loss, because P0 has been doing really good work.
I don't think you quite understand why Google Project Zero team exists in the first place. Their job is to make the world a more secure place. They seem choose whatever they want to work on to maximize their impact on the world –ranging from Intel processors to iPhones to some first party technologies like Chrome.
> Project Zero's mission is to make 0-day hard. We often work with other companies to find and report security vulnerabilities, with the ultimate goal of advocating for structural security improvements in popular systems to help protect people everywhere.
It is at least plausible that Google structured the posts and announcements to exploit that ignorant media coverage for their own competitive advantage.
So at least arguably their “fault” as they have ample experience with that media coverage process themselves.
It's in their financial interest to do so. They don't want their users gmail data (or from other googles services) to leak, even if it's not their fault.
But for security, they need to be working together. This is definitely a "rising tide lifts all boats" situation.
Many people will be annoyed by this "assume the worst" drama.
For example, drinking too much water, if we assume the worst, can kill you.
Also, walking around can kill you, if we assume the worst.
Also, just being around can kill you, if we assume the worst, hey, you could die of a stroke.
So, how is this "assume the worst" statement useful?
Er, yes it is? Or rather, to make a finer point, it was their responsibility—i.e., they knew the causal chain that would inevitably result from their action and chose to perform that action anyway.
If you knowingly give an alcoholic a drink, you’re responsible for them falling off the wagon.
If you leave your pet mouse out next to your pet cat and leave the room, you’re responsible when the mouse is eaten.
If you can clearly foresee something bad happening, and you have an alternative path that avoids that thing happening, and you choose to go down the path where the thing happens: your responsibility.
That’s not to say that nobody else is responsible. Responsibility is not exclusive. A war, for example, is the responsibility of two parties—either side can just give in to the demands of the other, to avoid it. Both parties, in their choice to not give in, are responsible for the war.
Apple could have written "Google is correct that the bugs existed for 2 years, but Google as well as us only found evidence that the bugs were actually exploited for a total of about two months and targeted a very narrow group of specific users." and so on.
Instead they opted for a "Google is lying about us!!1! They are IMPLYING THINGS". If a company as big as Apple with well stocked legal and PR departments publishes a press release like that, my mind immediately goes to "what are they trying to hide or downplay".
Seriously... did you overhear me talking to my relatives?
If not, you absolutely nailed the public perception.
(Edit: added title, changed wording to remove unclear usage of expat).
Google claimed an exploit was being actively used for two+ years (with no evidence beyond a variety of versions being exploited, which could also simply be the targeting of different versions). They also added editorial narrative like "we'll see cases of code which seems to have never worked, code that likely skipped QA or likely had little testing or review before being shipped to users." They then obviously sideband released the group that was targeted, making it a big news story. Unstated was that the same sites had Android and Windows exploits on them.
Project Zero is hugely valuable, but this was the first time it seemed like it became a marketing tool, using classic media release patterns for the biggest bang. Android is by far the most popular OS, with many serious exploits over its history (a 0-day privilege elevation just released by third-parties) -- does anyone remember Project Zero doing such an analysis of Android bugs?
This really ground my gears as well. You've just published lengthy posts on how to exploit these complicated vulnerabilities and chain them together, it's unlikely testing could have caught all of them.
And testing for security is entirely different from QA.
Do tell me Google, how is Stagefright going? Did you try QA'ing it?
The point is, all software has bugs; but there's no way Google can know what "QA" iOS goes through, and to pretend it's nothing is ridiculous. There's plenty of examples out there of code being reviewed by several super clever people, and yet they miss something. Trying to work backwards from a bug without the context of actually working in the team that wrote the code never works.
No; as the first sentence states, Project Zero found this independently:
> This exploit chain is a three way collision between this attacker group, Brandon Azad from Project Zero, and @S0rryMybad from 360 security.
(For what it's worth, this ended up in a jailbreak too, and has its own blog post: https://googleprojectzero.blogspot.com/2019/01/voucherswap-e...).
> Unused code is not uncommon. The point is, all software has bugs; but there's no way Google can no what QA iOS goes through, and to pretend it's nothing is ridiculous.
It isn't uncommon, but it is clear that the code was not QA'd, for the reasons given in the article: trying to call this method would instantly panic the kernel (which is easy to triage–you don't even have to have much knowledge of the iOS QA process to guess that).
Oops, my bad, I had in my head the opening of the first post talking about how they had come across the sites using these exploits.
I think we agree that this piece of code was not well tested. Where I think I set my expectations of Apple lower is that this code was never used, essentially forgotten about and that I've literally done this myself. And I simply don't believe you can tell simply from a bug whether "QA" happened or not.
Why I give the benefit of doubt to Apple here is that it's not in something that is called everyday in normal devices. It's not in part of the OS that sees constant use. If this error occurred (and yes I'm aware that the end result is the same) in say the network stack or media stack, then I'd start having my doubts, since they regularly process untrusted data, and Apple should have proactively checked, just like Android now does with Stagefright. But this was in an essentially undeclared api that was never even used by Apple themselves. I think this was more a fuck up rather than not doing their jobs.
As a side note, whilst I do have an iPhone, my 2015 MacBook runs Linux and i generally don't consider myself an "apple fanboy".
Have any source of that?
Yes, many times in fact. So besides that "question" just being a terrible "Whataboutism" fallacy, it's also just wrong.
From 2019 alone here's a handful of deep-dives into issues with Google software (well the last is linux but is done against Android specifically): https://googleprojectzero.blogspot.com/2019/03/android-messa... https://googleprojectzero.blogspot.com/2019/04/virtually-unl... https://googleprojectzero.blogspot.com/2019/02/the-curious-c... https://googleprojectzero.blogspot.com/2019/01/taking-page-f...
"Whataboutism" is entirely off base because that isn't what I did whatsoever.
We're talking about the motives of literal Google employees. Finding and reporting bugs is hugely important for everyone, but they sure are making a lot of noise, and adding a lot of narrative and PR tactics, for a long patched iOS bug.
Or maybe it's just that Android bugs are expected, so they don't get much attention any more?
"handful of deep-dives into issues with Google software"
First one I went into -- third party reported, widely known problem in external graphics library. Project Zero did not find it, did not report it, and this is just tourism after the fact that points the finger outwards.
Second one -- Linux kernel. Pointing the finger outwards.
Third one -- Clear fault in Chrome, but conclusion is that it's actually the fault of ASLR and that the OS isn't memory-bounding Chrome. Pointing the finger outwards.
Fourth one -- Tiny post that says it found a "couple" of bugs that are probably not exploitable. Bug minimization.
They have another that attacks Samsung software. Pointing the finger outwards.
This isn't a hugely compelling example of their intentions. Show me one where they make the extraordinary claim that it was long exploited without any evidence whatsoever (elsewhere you claimed that Google knew because they "crawl", but in actuality this Project Zero claim was made purely based upon the span of versions the bug targeted), or make editorial comments about QA or source control processes. Instead it looks an awful lot like hand-washing.
I most certainly did not.
> PFirst one I went into -- third party reported, widely known problem in external graphics library. Project Zero did not find it, did not report it, and this is just tourism after the fact that points the finger outwards.
You specifically asked if Project Zero did such a public analysis of a bug, which that post is exactly. If you wanted Project Zero discovered issues there's a whole boatload of them on their issue tracker.
> Or maybe it's just that Android bugs are expected, so they don't get much attention any more?
More whataboutism. And also wrong.
> This isn't a hugely compelling example of their intentions. Show me one where they make the extraordinary claim that it was long exploited without any evidence whatsoever (elsewhere you claimed that Google knew because they "crawl", but in actuality this Project Zero claim was made purely based upon the span of versions the bug targeted), or make editorial comments about QA or source control processes. Instead it looks an awful lot like hand-washing.
Show me one where they do that about iOS. You are reading things that aren't there. Google did not make any extraordinary claims. Kinda like how you accused me of claiming "Google knew because they "crawl"".
The "editorial comments" on code review/QA are covered in the follow-up posts. Notably task_swap_mach_voucher when called with a valid voucher would kernel panic. There is no charitable explanation for kernel calls that are reachable by any application and never work. The "editorial comments" that are you objecting to are, if anything, too soft in their phrasing.
What I "specifically asked" is if they've done anything like this regarding an Android bug. Not if they've ever reported in a passing sense, and in a blame-everyone-else-way about an Android bug.
"More whataboutism"
You keep using that word. I do not think it means what you think it means.
Ergo, again we're talking about a huge reporting cycle based upon a Project Zero release. If you think it's whataboutism you're digging really deep to try to prove your rightness (in a very Trumpian sense -- Alabama Alabama Alabama).
"I most certainly did not."
Yeah, you did. You claimed that Apple couldn't know how long it was exploited, yet Google -- because of their crawling -- could. The only possible basis for your argument was what I said (because obviously a widely targeted version base is because there are users out there with that version base, in the same way that a 0-day today for Android 8 doesn't suddenly mean it was invented two years ago, which would be a monumentally stupid claim that would be instantly discredited by anyone who put even a modicum of thought into it).
> a marketing tool, using classic media release patterns for the biggest bang
OP's point is that the article on the iPhone definitely reads like this.
Google also failed to mention that Android and Windows had been targeted by China as well.
These omissions certainly leave me less sympathetic towards Google.
If you want to discuss the exploit itself, that's great.
If you are going to bring how it is targeted into the discussion, there is simply no excuse for leaving out the fact that this is a narrowly targeted attack from a nation state adversary who is also actively targeting your own devices.
I don't know if their motivation was to harm a competitor or to avoid annoying China while you are hoping to resume doing business there, but they certainly left themselves open to both interpretations.
If you don't intend to tell the truth, then it's better avoid bringing up the topic altogether.
Project Zero is an amazing team that has only helped the state of security worldwide. Apple's defensive and accusatory response makes zero sense and goes against the very spirit of security today.
https://arstechnica.com/information-technology/2019/09/andro...
They have no problem covering Android bugs, they just don't write about bugs they didn't find.
I suspect they are, but backchannel them to the development team, versus airing them.
Project Zero (whether it's housed at Google or not) has a vested interest in making their detections as newsworthy as possible. Apple has a vested interest in downplaying those claims as much as possible.
But as a PR piece, which is what this was, Apple needs to keep in mind that they want to project how much they ENCOURAGE folks reporting security issues to them. Sounding defensive is not helpful to them in that regard.
Not everybody is Google. Will the next person be scared to report their findings because they think Apple will come after them rather than be appreciative simply because they don't approve of how it was framed? I'm not suggesting this is easy, only that as a PR matter it's probably best for Apple to take the high road even when their competition is being unfair.
Correct falsehoods, yes, but the tone was off here.
Apple patched this within days of finding out about it. This press release is about everything other than the strictly business aspect of reporting and fixing a flaw.
Apple says "Google’s post ... creates the false impression of 'mass exploitation' to 'monitor the private activities of entire populations in real time,'". But Google's post doesn't do that. Those sentences occur late in the blog post, and aim to educate about the risks posed by software vulnerabilities in general, not these specific vulns. That is abundantly clear from the text. The only way to get the impression that Google was doing otherwise is to merely skim the post.
It seems like Apple is mostly annoyed that the press latched on to this, although honestly I question how much it matters since nobody seems to pay any lasting attention to these types of stories anyway.
If I discover a security hole that's been present in Windows for 10 years, but only know of an active usage of it say, in the Ukraine by Russia, I'm going to say that the vulnerability is 10 years, not 2-months. 10 years is the length of time you could have been exposed. 2months, Ukraine, tells you how much more likely you were in danger for that location.
But you should not act as if the vulnerability existing for 10 years didn't affect you, because you don't know about how many other people were using it.
I think both the time the bug existed and the relevant timeframe of known exploits should be part of a responsible security disclosure.
Omitting either one is a disservice to users.
Android security has always been a bit of a contradiction of terms, and while Google has improved the OS, the combination of limited availability of upgrades due to carrier nonsense and the state of apps on the platform. An Android zeroday isn’t news.
The iOS defects are particularly jarring as they have been rare to date.
No matter where I buy my Windows PC from, my upgrades come from Microsoft. In fact, I have an ancient Mac Mini that can still receive Windows 7 updates.
I don't know if I would go that far. That problem comes from the way Android is organized. It's open, and it invites third party involvement. That in turn makes it nearly impossible for Google to control the OS lifecycle. You can argue that they should have kept it closed, like Apple. But if that were the case, they'd be in even worse anti-trust waters than they already are with the device.
More likely, they'd simply have failed. They had the software know how, but in no way had the expertise to build out a new type of device. It seems unlikely anyone else could have bankrolled a realistic challenge to Apple's dominance. So we would probably be in a situation where there was iPhone, and a bunch of shit phones from random manufacturers.
In light of all that, I think Google made the best decision possible. Maybe that's what you mean -- that Google made a good decision and that, despite that good decision, there are tradeoffs. But to me it sounds like you think Google failed in some way by making the choices that have led us to the current state of affairs w.r.t. updates. I don't think that's a fair read on the subject. At least, when I see someone doing the best they can, and there are flawed aspects to the performance, I don't say, "It's nobody's fault but yours that there's a flaw in this work." I would phrase it differently.
It would have obviously been Microsoft. They already had a mobile operating system and companies would have had no choice but to use it.
But if that were the case, they'd be in even worse anti-trust waters than they already are with the device.
Microsoft never got in trouble for having a closed operating system. And despite all of Rubin’s BS about the “definition of open”, everything that makes Android,Android outside of China is closed source and controlled by Google.
The phones sold by Apple don't have this problem. The phones sold by Google also don't have this problem. But the phones sold by carriers but running Google's OS have this problem. Phones sold by carriers but running Apple's OS would also have this problem, but Apple doesn't let anyone else sell phones with their OS.
The difference between your computer's patches and your phone's patches is that you are allowed to update your computer's operating system, but your phone has probably been carefully locked down by your carrier to prevent you being able to do this, which is very upsetting but that's a different matter.
PC makers also put various crapware on phones and use to do shell replacements. That never stopped anyone from upgrading...
When Google releases a new OS or an important security fix to Android, carriers need to merge this stuff in with all of their custom stuff, assuming that they still care to do so and support that device. As a result, phones running Android can fall years behind on patches.
Microsoft also allowed various carrier changes to Windows Phones but they could still offer upgrades across devices.
Phones sold by carriers but running Apple's OS would also have this problem, but Apple doesn't let anyone else sell phones with their OS.
Microsoft has had a vibrant ecosystem of third parties selling PCs running its OS for decades. The entire idea behind WinHec and Plug and Play in the mid 90s was to solve this very problem. The issue that either Google doesn’t know how to properly run a platform or didn’t make it a priority. You see that Google can architect a system where Google Play Services can be updated across manufacturers. They care enough to keep their spying mechanism updated.
The difference between your computer's patches and your phone's patches is that you are allowed to update your computer's operating system, but your phone has probably been carefully locked down by your carrier to prevent you being able to do this, which is very upsetting but that's a different matter.
That’s only because Apple wrested control from the carriers before any iPhone shipped to keep carrier crap off their phone and to keep control over its devices. Google never cared to. Android is just a badly architected system in this regard. Microsoft solved this problem two decades ago.
They definitely didn't update phones quickly when exploits were found for IE and Windows would got a security update.
We had some test Windows Phone/Mobile devices at work, and the cheaper models didn't really get upgrades. I would also guess if you had 7.5/7.8 devices, they stopped getting updates? I'm sure some devices kept getting regular updates.
We also had a cheap 32GB Toshiba tablet, which couldn't upgrade Windows 10 because it lacked drive space (even though it had nothing apart from Windows installed on it - it was for testing touch on Windows browsers).
And for all that, they still failed to make a dent in the market. Partly, OEMs and carriers were not as interested in supporting Microsoft's offering precisely because of how they could not put their own stamp on it. In many ways, Microsoft's offering was better on the fundamentals than Android's. So why didn't it succeed? Perhaps because of the very features you are praising.
The only reason Apple was even able to pull it off was because of their first mover advantage, combined with their extreme consumer appeal. Their phones were so much better than anything that was available at the time, but even with all that, they had to enter into an exclusive contract with AT&T for the first couple of years in order to get the control they wanted. Only after they had established a foothold were they able to say "no" to carrier and OEM customization. If they had been second to market, like Android, it's hard to picture them having that level of control and leverage.
Microsoft didn't lose because of those things (it shows how much better they are at being a platform company that they didn't repeat Google's mistakes), they lost solely because Android was free to OEMs. That's entirely a business model question.
[1]: https://www.wired.com/story/android-zero-day-more-than-ios-z...
To a certain extent, of course, attacks against Android outside of flagship Samsung and Google phones are much cheaper- look at any patchset and attack, and given that 30+% of the Android user base is on Nougat/Oreo and 10% is on Kitkat or earlier as a whole they are far more exposed.
Apple does not want sympathy and is not concerned with what someone in the tech community with advanced knowledge (and opinions) think. They are concerned with what is thought of them in the broader community that they sell to and that buy their products. This was the right thing to do. To point out what they could to clear up the issue.
> When Google posted the Project Zero articles, that did not impact my view of Apple in any way. However this press piece affects my view of Apple negatively, so from my perspective this press article has turned a more or less neutral event into one that is negative.
The vast majority of Apple customers not only don't know what Project Zero is or does but don't care. What they do care about is what is written in the mainstream media about Apple. And what the mainstream media digs up to stoke fear in order to continue to sell advertising.
Apple did the right thing here. I was glad to read this info. I have been using Apple products since the 80's and computers prior to that (mainframes in college).
That would be fantastic for all involved.
John Gruber's take:
> Reading between the lines here, what Apple is pushing back on is the fact that Google’s report on this attack against the Uyghur [1] community only mentioned iOS. Coverage of Google’s report created the impression that only iOS users were hacked, when in fact, the Chinese government also exploited Windows and Android users, [2] and that these exploits may have been targeting people everywhere.
* https://daringfireball.net/linked/2019/09/06/apple-pushes-ba...
Though he does also comment:
> Conspicuously unmentioned in Apple’s response: “China”.
:P
As sibling points out though, we may just not be the target audience.
What I mean is that it's extremely reactive, accusatory, and defensive, but in response to something that we aren't seeing. It can make sense if someone was running a huge news story about it, that we're just not in the audience for.
Given Google has already gone down the "use our security posts to discuss competitors bugs but not our own", it seems entirely reasonable for other companies to start treating the PZ blog as a marketing tool.
Project Zero finds and publishes bugs for most major platforms. Just look through their archives: https://googleprojectzero.blogspot.com
https://googleprojectzero.blogspot.com/2016/09/return-to-lib...
https://googleprojectzero.blogspot.com/2019/03/android-messa...
https://googleprojectzero.blogspot.com/2015/11/hack-galaxy-h...
Here's some about Chrome:
https://googleprojectzero.blogspot.com/2016/11/breaking-chai...
https://googleprojectzero.blogspot.com/2014/10/did-man-with-...
https://googleprojectzero.blogspot.com/2019/04/virtually-unl...
While that was undoubtedly of a larger scope, it was also the event that led to the creation of P0, so it would make sense that this gets more exposure than your average bug report. Most security bugs aren't multi-exploit zero-day chains found in the wild being currently used to oppress people by a state actor.
[1]: https://twitter.com/alexstamos/status/1170064458003054594
Most Google bugs are… much less interesting.
It does not take a genius to read that article and realize that the omission of the other targeted platforms was intentional.
You can interpret this many ways. Maybe they're casually discouraged from publicly talking about threats against Google software. Maybe competitors' software is just more vulnerable. Maybe the team shifts focuses every once in a while, and in 2019 they've just been on a real Apple/Microsoft kick. I don't know.
My general position is: Google The Company has done nothing at all to deserve the public's trust and good intentions, and I don't see why that position shouldn't extend to the Project Zero team. Its a garbage company, and the publications from the very talented and dedicated people on that team may be better interpreted in a more unbiased environment where we don't have to constantly be raising questions like "are they unfairly focusing on competitors products" or "are they giving internal teams the same time to remediate that they give competitors"?
But waiting 6 months? To release an embellished piece about a non-exploitable bug that was patched 6 months earlier?
2 WEEKS before Apple unveils the iPhone 11 no less. And you all STILL downvote me when I post about how I believe PZ is a clandestine group of hackers paid to dig up zero-days on competing products so competitors can get bug-doxxed days before large/important events.
When Google posted the Project Zero articles, that did not impact my view of Apple in any way. However this press piece affects my view of Apple negatively, so from my perspective this press article has turned a more or less neutral event into one that is negative.