This was a mistake and has been patched. But it looks like an MSA was created using the same email as your AAD before the fix.
Thus, from MS's perspective, there are two distinct accounts under the same email, hence the UX. It's really quite a mess, and yes the situation is weird. We're working on it make it better.
Try transferring the subscriptions to your work email using this method https://docs.microsoft.com/en-us/azure/billing/billing-subsc...
then onenote gets involved in the mix, which gets stored in onedrive. but the surface pen can only call the onedrive that accesses onedrive personal (msa) not onedrive individual corporate, because there are two onenotes, one built into windows one into office. the pen eraser can not be reprogrammed to use the PAID FOR CORPORATE onenote, just the free app. so never click the button on the only peripheral of the three thousand dollar computer you just bought, because it will lead you somewhere you dont want to go. so now onenotes are stored in the wrong onedrive. also for some reason your computer still has the onedrive for business client, formerly, sharepoint sync, formerly groove (acquired from ray ozzie who also tortured you introducing Lotus Notes to the world, back in the day) which is depricated, lets update you to onedrive, formerly live mesh, but now the correct client to use to access your aad onedrive for business. yes im sorry, one drive for business is no longer developed but you use onedrive not for business to access your onedrive for business which is different from your personal onedrive, and also different from groups. yes you could use the share feature to share documents in your individual (corporate not personal) onedrive with others, but the more correct way to sustainablty collaborate is by using gropu onedrives. and yes, you still have to click sync for each group/document library again on your second third and fourth computer, because sync settings cant be stored in the cloud or pushed to other users. if you want to mount your group/onedrive/sharepointteamsitedocumentlibrary as a drive letter without caching and syncing it we need to install a third party zeedrive service, because windows cant remount sharepoint drive letters on reboot well.
and microsoft wonders why people prefer dropbox/box....
tldr: teams vs teamsites (completely different). i can add people to groups or teamsites from outlook groups or teams, right? yes you can add people to teamsites from teams, but they are completely different things. msa onedrive vs aad onedrive vs group onedrive (not called a onedrive usually but accessable through the onedrive web/windows/mobile client using the onedrive api.) onenote vs onenote 2016. skype vs skype for business. channels vs folders, vs document libraries vs teamsites vs groups vs teams!>??!?! :( :( :(seriously why the fuck does my phone have onedrive, sharepoint, outlook groups, outlook, AND teams to get to files stored in and out of my office 365 groups, oh and lens can only scan to my aad onedrive, not a group. no messages cant pass between exchange, yammer, teams, and skype, except when they sometimes do poorly between teams and skype (for business of course, not skype.) why is outlook groups the only app with a follow button. from why when i follow an office 365 group team site document library (what should be called a group onedrive!!!) does it NOT show up in either onedrive nor sharepoint. why is the follow button different in teams, outlook groups, and the sharepoint web interface! yes there is a desktop teams app, but its really a copy of chrome without any chrome running web app locally on your computer, using at technology called electron which packages a client version of a javascript engine repackaged as a server repackaged as a client. i digress. but its sure not .net. and yes they use chrome, not edge. which isnt internet explorer. nor file explorer.
remember that time Bill Gates tried to download something off Microsoft's website. He should try using Office 365 for a week with a team of people. (http://blog.seattlepi.com/microsoft/2008/06/24/full-text-an-...)
If you want to know what outlook you have, here's a handy article they made to help you figure it out. Mind you, they forgot about outlook for windows phone, but with that many outlooks who can blame them?
https://support.office.com/en-us/article/What-version-of-Out...
When you say Outlook account, do you mean Hotmail? Outlook.com? Live.com? MSN.com? Microsoft Account? Windows Live ID? Windows 10 login? Windows phone login? XBox login? .Net Passport?
so the new sync process. go to office.com, sign in, click mail or onedrive. click the group. if mail, click files. now it brings you to a list of recent files as shown on a client served by the exchange server. to get to the correct sharepoint served web client, you need to click browse files in the upper right corner. no dont worry, your folders arent gone, the exchange client just brilliantly collapses the entire structure and shows only the files, in order of most recent. once you get onto the sharepoint server your folders will reappear. then click sync, then click allow, then yes, then sync now. then wait. if i add 30 people to a group, i have to walk all thirty through syncing and following. and dont worry as soon as i train them the sync button will be renamed. my new favorite one. there are now THREE terms used in different spots that all lead you back to the office 365 group team site document library (aka group onedrive.) they include: Open in Sharepoint, Browse Library, and Go to Site. For some damn reason, in the teams app "Open in Sharepoint" is the term used to launch the onedrive group web client, but in exchange its Browse Library or Go to Site.
It's a mess.
Enterprise Architecture teams have their work cut out trying to describe the choices they make.
I wonder if there's a sort of internal fighting for each team to squat on the "best" names for their product or service. Basically a Dilbertian confusopoly [0] where the goal is to make your project sound like "the obvious choice" regardless of its merits, with "Microsoft" on the front as the only way it stops being impossible to trademark.
I imagine other large companies struggle with this as well, although Amazon seems to have taken to the other extreme [1].
[0] https://en.wikipedia.org/wiki/Confusopoly [1] https://www.expeditedssl.com/aws-in-plain-english
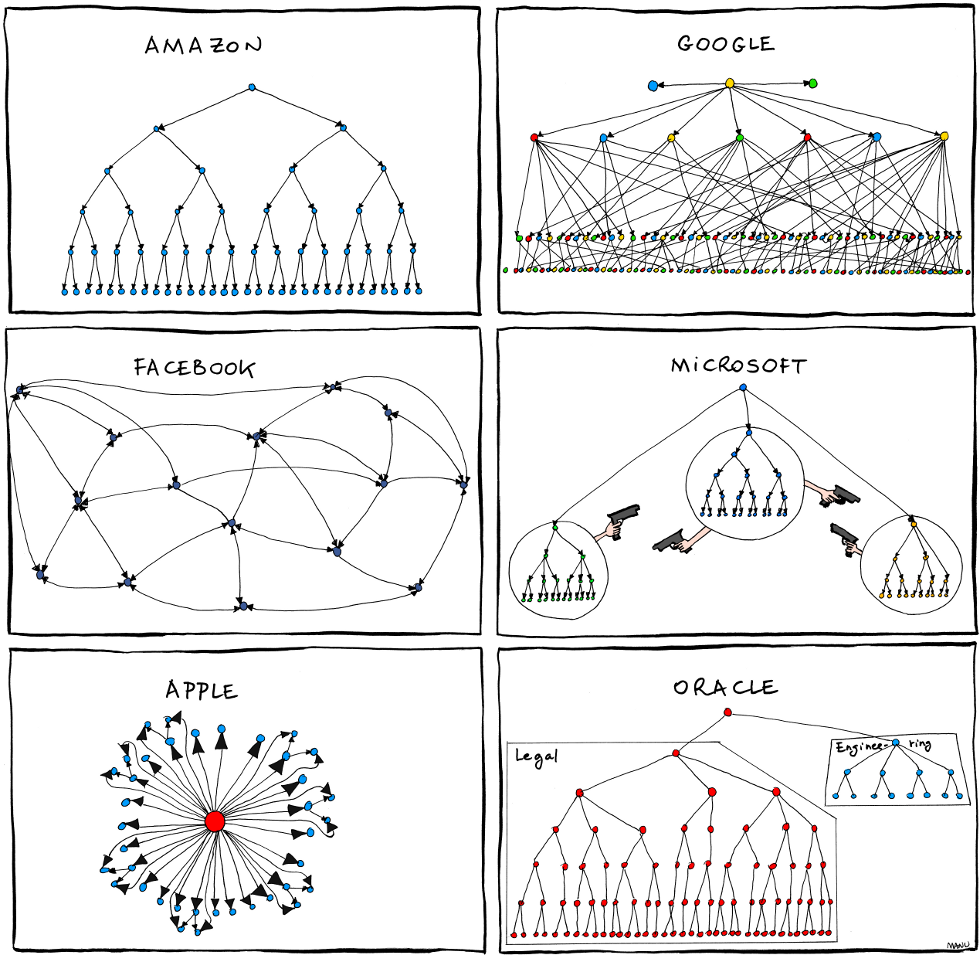
Branding teams and divisions are getting in the way of coherence and usability. I think ONE of the worst right now is the OneDrive vs SharePoint back and forth. First they were kind of hiding the SharePoint name, and renaming everything onedrive. SharePoint Workspace, formerly Microsoft Office Groove, became OneDrive for Business (because it was the client sync tool, not a server.) Now its making a comeback and certain things are "not" OneDrive, such as 'Office 365' Groups '''SharePoint 'Team Site'' 'Document Libraries''
At least in the Mail world the divide MOSTLY makes sense. Outlook is the Client, Exchange is the server. Yes, the OWA web/javascript client streams from the server and renders in your browser, but otherwise the divide is mostly intact. You NEVER see an Exchange app, and you rarely see the word outside the content of "connect to this server." The SharePoint branding team on the other hand cant handle being the server only and has now forced a SharePoint app that is like some bastardized fork of the OneDrive app. They mostly do the same thing, but not quite. Microsoft needs to draw a line and say "OneDrive = Client, SharePoint = Server" and try and not cross it. The OneDrive web client should be an interface that streams from the SharePoint server to your browser.
I wish they would have left 'Lync' as the "server" to the various clients.
If it's a company domain then there's not much reason to have personal account with the same work email address.
Every login will prompt to select the organizational account, or the personal account.
Not sure why only MS is being called out for it ... they probably modeled their system after Google.
Unfortunately you cannot merge. Google services will have an option to switch between the different accounts. The priority order is shared, and to change the order you have to log out of all your accounts and log in again, with the primary account first. I decided to keep my @gmail.com account first, so I only have to switch to the @example.com account when I check GMail.
Could be much better, of course. I was personally a bit frustrated with the process.
I mean, that is exactly what Google does. Google does allow the change you listed above, which is nice. But if you don't explicitly change your accounts, you keep getting the "pick an account" screen on every single login, just like the parent described, and just like Microsoft shows users too.
Google's UI for it looks like this : https://lh3.googleusercontent.com/-_g4V2wYd-SI/VrZF-5K2yCI/A...

Which is very similar to Microsoft's UI for it : https://docs.microsoft.com/en-us/azure/active-directory/medi...

Then, an admin who proves they control the entire example.org domain registers it for G Suite, and creates a 'crb' user.
You now have a conflict account situation: https://support.google.com/a/answer/7062710?hl=en
Also, when signing up the Google system will not allow you to use the same email (if it's registered) but once you "take over" or verify domain ownership, you can then claim / use that address - which I believe creates this situation.
I occasionally have to perform some bizarre incantation once in a blue moon to switch accounts when I want to comment on something and then switch back so I can see my subscriptions again.
The private account is the one created by you.
If anyone knows the exact difference, please explain! Would be greatly appreciated.
The Personal accounts (also called Microsoft accounts/IDs or Live IDs) are the ones you as an individual create directly with Microsoft. The prime example would be people who've had a Hotmail account for ages, and that eventually became a Microsoft account.
The confusion comes because since a couple years ago, you can create Microsoft accounts with any e-mail that you own, be it personal, from work, hosted in gmail, hosted by your employer, hosted by yourself... You name it. So it is possible to create a Microsoft account with your work e-mail, even if your work e-mail also has a Work/School Account tied to it. All the notifications for that Microsoft account will go there, but they are not for your "Work/School Account" (also referred to as Organizational account), they are for your personal one.
Yes, it is a mess. After a while I got used to it and now I'm comfortable navigating all my identities, but it can be very annoying when you first encounter it.
Gawd.. You're microsoft, you can create a whole new security protocol. Don't have this half baked persona solution.
If you can't figure this out, it really reinforces the reason for every time we come across something in Azure where we're like wtf isn't this feature supported?
But, ultimately, those licensing rules may be under MS's control as well. Even if they aren't, it sounds like it has a significant impact on their service's design and usability, so it's in their interest to make a change somewhere.
Just merge them into a single collection and have my experience be dictated by that merged collection. With how entrenched they are with the Enterprise world, they should have foreseen this scenario and designed their family of products to facilitate this seamless merging of authorization rules across disparate accounts.
Because user stories aren't: "I want to access my Office365 work account" or "I want to access my personal Microsoft account".
They're: "I want to edit or download a file I have access to in the Microsoft cloud" or "I want to find a file I have access to".
The school/work account is somehow created by a company administrator, but I don't know exactly how or where.
Coupled with the fact that I'd enabled 2FA made for a ridiculously poor user experience. By the end of the process I was so pissed off, I'm not sure if I'll ever use Azure or Office 365 again... we'll see.
They did add an option so you can change your personal account's email address so you don't have to deal with account namespace issues.
The other day I wanted to check if a windows key I had is still valid for another fresh installation before wiping my HDD. I don't even remeber the whole endavour, but I had to install some specific MS software for it...
Amazon manages to keep multiple accounts of mine, with the same email, but different passwords.
Though the more bothersome one in my mind, is that I can't login to gmail in chrome without attaching it to chrome... I don't want to attach my work email to my home chrome browser (which forces a couple extensions, and my home page). So I've opted to run both Chrome Canary (work) and Chrome release (home/personal)... It seems even worse UX when you have multiple google accounts you want to keep separate.
As to Skype, it's been weird since MS bought them, and I remember having great pain migrating/attaching to my MS account so I can have a single login, and it was just weird for some while.
Aside: I'm glad google domains includes DNS and email forwarders, so I can keep my really old domain emails forwarding to my gmail so I can on occasion recover old accounts.
I use LastPass religiously, but I don't even try to make it work with MS accounts.
- Work or school account
- Personal account
I get this prompt every time I try to log into Azure with my work email. If I choose the work account (the most intuitive option) my azure subscription list is empty. I have to log out and select the other option.
Why is there a difference and why isn't this transparent? I am authenticated, you know who I am, give me access to the things I'm authorized for. I don't know what kind of weird backend situation MS has, but asking me to understand it is terrible UX.