The scammers who push malware under the guise of tech support, free porn/games, etc. are effective enough to compromise millions of people and that's before you get to the question of what it'd look like if a government started pushing access for monitoring. How many people might consider installing something which this guy they met in a coffeeshop says will protect their messages from government surveillance? Now consider how many people might have malware installed by an abusive domestic partner, and where control of the device would extend to hiding the existence of spyware.
This is not to say that Apple is acting without self-interest here, only that I think there's really a pretty nasty market failure making it quite difficult to reconcile someone being able to make choices about their device with a fairly high risk of compromise with potentially significant consequences.
Facebook puts a large "Stop!" warning in the browser console when you try to open developer tools with a link to https://www.facebook.com/selfxss. I'd be really curious to see if that's helped to stop such attacks on their side.
Full text: "This is a browser feature intended for developers. If someone told you to copy-paste something here to enable a Facebook feature or "hack" someone's account, it is a scam and will give them access to your Facebook account."
If Facebook is willing to fool kids into giving up their privacy via side-loading, you can imagine why Apple is nervous about how things would go if anyone could easily do so.
Nah, thats a win2k era cop-out. The hard part is balancing secure by default and granting privs only when absolutely necessary (and authenticated)
I think a better angle is pushing for relaxing software distribution: keep the trust chain but let people run apps in the normal sandbox even if those haven’t gone through the current process. Exploits are still possible, of course, but the normal controls allowing user awareness of the device’s status would be intact.
We know exactly what happens when you do this. Less savvy users will be tricked into installing malware.
For instance, a couple of months ago:
>FlixOnline App Spreads Android Malware by Promising Free Netflix
https://www.thequint.com/tech-and-auto/flixonline-app-spread...
While there are people who make this argument purely on ideological grounds (similar to arguments you hear about individual freedoms vs collective rights), it's essential to recognize that _completely_ removing the ability of independent developers to write and run software if the manufacturer has decided they don't like that developer will slowly destroy the competition, creativity and freedom that created most of the technologies that are used today.
It's reasonable to make the argument that the manufacturer needs to secure the devices that they sell, even for users with low technical literacy.
Advocating for the manufacturers to be given total control over everything that every user can do with their device won't guarantee increased security, but it certainly would result in manufacturers being able to disable any software they chose to, regardless of legitimacy, without reason or recourse.
That's a prospect that is (IMO) far more terrifying than what it could prevent (some users falling for certain types of phishing attacks that install spyware).
I disagree with that conclusion (the latter scenario happens frequently and has lead to significant consequences, including death) but completely agree that it's not a good situation that the alternative is giving a couple of companies control over who gets to ship software. That's why I described it as a market failure — as a user you're left picking which set of drawbacks is less of a problem for you.
What I'd like is basically opening up the App Store walls: allow users to enable third-party stores but everyone runs their apps inside the same sandbox, and the OS vendor retains some global kill switch for malware but with some level of public oversight.
One edge case for this would be the apps which need special permissions: for example, some cell carriers have special entitlements on iOS which allow their apps to talk to their networks in ways which normally are blocked. Reconciling edge cases like that with multiple stores would require care.
We've been in this argument before and the most secure platform today is still the web, an open platform where the code is designed to run on demand.
There's a reason everybody asks to install their native app, there's much more data to gather there than in the web.
I'm not suggesting that the manufacturer should be creating closed platforms to "secure" things for the user; I'm saying that closed platforms can't guarantee an increase in security but will guarantee the slow erosion of openness in all other platforms.
I'm well aware of how native apps are heavily marketed over their web-app equivalents because companies want to gather more data, get access to push notifications (on iOS at least), etc.
If a person decides to give up control of their device to another person or organization (like the device manufacturer) fine, but that should be a voluntary decision on the part of the user, not something forced.
There is a wide gap between being unable to decide for oneself in the general case, like a child, and being unable to decide for oneself due to lack of expert knowledge. Sometimes, less is more. Apple built its brand on this insight.
As long as the dialog for unlocking your phone would clearly state the risks and what it does, unlike those toolbars upon installation, I think it would totally be OK.
Imagine if you couldnt install Linux on any PC because Dell didnt give you the keys to prevent you from hurting yourself. Or Apple didnt allow sudo in macOS. Seems kinda absurd right? Yet this is the standard for phones.
Also Id like to point out that Android allows installation of external APKs (after activating) and it didnt lead to a super increase in malware, as user still prefer the Play Store, and APK are usually left for the more technically inclined user for niche purposes or often times Region lock circumventing.
Are you sure about that? I pulled an old, cheap Android phone out of storage box to do some debugging. I needed a quick file manager app, installed one of the top results on Google Play that was baked with some malware that may have bricked the device (didn't bother to try to fix it, it's in the bootloader). Granted this was an old version of Android, but that's still a bit egregious. I can't recall anything like that happening on iOS.
https://blog.zimperium.com/new-advanced-android-malware-posi...
-> "Upon installation (from a third party store, not Google Play Store), the device gets registered with the Firebase Command and Control (C&C) with details such as the presence or absence of WhatsApp, battery percentage, storage stats, the token received from the Firebase messaging service, and the type of internet connection. "
It isn't hard to find similar reports, there are enough of them.
I want people to have more control over devices but there are some non-trivial threats which millions of people face which are currently defanged by things like the OS not allowing malware installs, or hiding the use of various sensors or data access, etc.
Sure, do everything you can to educate the user on what they're doing and make things as hard as possible for scammers, but ultimately it must be their choice who controls their device, not yours.
For example, if you buy a car there are safety features you cannot turn off without major modifications. Dangerous tools often have safety guards built-in to the design — for example, my blender doesn't say it's my choice whether to keep the spinning blade covered. My bank doesn't say it's my choice whether or not to identify myself when making a withdrawal.
For most people, iOS limiting the damage when they get compromised is a huge plus. Removing that entirely in the absolute position is bringing people back a couple of decades ago only now the malware will have access to their most private moments and data 24x7 rather than just their Geocities browsing history.
Now, consider what that means for something like unlocking the bootloader. Allowing that means undetectable malware, potentially irrecoverable. There's not really a good way around that and even if you try to inform people at the time they enable it that doesn't help if it's done when the device is out of their control (abusive partner, boss, police, etc.), and every on-screen indicator can be faked by the malware vendor. That leaves options like a physical switch in a prominent location which most people aren't going to want to pay for or see, and are more likely to be used by accident than intentionally.
To use a direct analogy with Apple's restrictions on users, you're free to modify and flash your car's ECU firmware. In fact, it's quite common.
Really? How have you defined common? Where is that data from? I can't imagine anything more than a tiny fraction of car owners are doing this. Most people are not hacking their cars, building Raspberry Pi controllers for their toilets, or have any desire whatsoever to side load an app on their iPhone. The HN community is not representative of the overall population.
But no one says the car manufacturers are required to make a car where you can flash the ECU. There’s just no reason for them to block it. If someone came up with a way to steal your car by tricking your into running an app that flashed your ECU then you can bet Ford would disable it pretty quickly.
Sure there is… if they are providing warranty on the vehicle then they should definitely block ECU mods, as a customer could flash original firmware back after causing damage.
And I imagine you can easily make an engine over-rev or overheat with a modded ECU, perhaps to the point of causing a fire or other catastrophe.
A phone is not, usually, a dangerous tool. Unless you can make it explode :)
> For most people, iOS limiting the damage when they get compromised is a huge plus.
Then just dont unlock. The unlock would need to be done from inside the OS, by the user, not by external actor.
> Now, consider what that means for something like unlocking the bootloader. Allowing that means undetectable malware, potentially irrecoverable. There's not really a good way around that and even if you try to inform people at the time they enable it that doesn't help if it's done when the device is out of their control (abusive partner, boss, police, etc.)
If you have an abusive partner, boss, etc. you're already at risk because they will keep looking at your phone anyway and you're in no position to refuse. A way better solution is to have a burner phone they don't know about.
Agreed with the police point, but I think after getting your phone from police you could just clean install iOS again to make sure nothing unwanted is there.
P.S. On 2nd hand market, you could just as easily reinstall stock iOS once you buy a new phone to prevent buying 2nd hand unlocked iPhone with malware.
What if _you_ didn’t? I outlined scenarios which are real risks for millions of people and a fair fraction of those either involve no or limited user consent. Maybe it’d be possible to have a secure factory reset – this is harder than it might seem with firmware in so many places – but that only helps if you even know that you need to. Anything which allows undetectable rootkits means that a large number of people will never even realize that because phones are general purpose devices and most people are not security experts. Worse, how many of them are actively being betrayed by trusted experts - abusive partners, unethical technicians, etc. - who will say it’s fine?
The reality is it isn’t 1981 and computers aren’t toys or cloistered academic devices anymore. Mass market platforms need to be more secure than 90s era tech allowed.
Exactly but what you’re missing is that with iOS this decision is made when you buy the phone.
Eventually also google, Amazon, anyone under the sun will do the same, just in case some aspect of your privacy is not captured.
Technical solutions (like preventing side-loading) cannot possibly eliminate the thing driving the behavior; profit motive for stealthily gathering data to build "better" user profiles to lease to advertisers.
A much better solution would be to create better permissions models (capability-based) for mobile devices.
As an example, one could build a granular permissions model which forced apps to be composed of multiple modules. Each module would have their own sets of mutually exclusive permissions.
An app that allowed the user to apply filters to photos/videos could be composed of two modules:
One which had read and create permissions for files the photo library along with read-only access to an app-local storage directory
A module which had the network communications permissions (exclusively by OS APIs that performed all the crypto[1]) and write-only access to the app-local storage directory (for downloading new filters)
By forcing apps to be broken up into separate modules and ensuring that all network communication is done from a carefully constrained sandbox (which can only read/transmit a tiny subset of data generated/available to the app), users could see exactly what the app transmitted without having to install their own self-signed root certificate (and maybe also jailbreak their devices if the app that they're interested in is using certificate pinning or ignoring the OS certificates).
The best way to technically combat a lot of this sort of data-slurping nonsense would be to force apps to have near[1] total transparency for all network communication for any user that wanted to see.
[1] The OS crypto API would have to provide a few authentication routines which blanked passwords, secret keys, etc. after use to prevent the unintentional leaking of secrets. Those APIs would obviously have to be designed to be resistant to malicious use by Facebook, etc.
If we're quibbling, they likely meant plurality as opposed to majority. It's close to an outright majority though.
I don't know why people even bother making statements like that here without backing them up, when it's pretty obvious the first response is going to be to request a source.
So, source please?
https://enterprise.verizon.com/resources/reports/2019-data-b...
That's the problem with using first hand experience. Unless you're doing a statistical review and your experience is actually collating data, the chance that your experience accurately reflects real world data is wildly dependent on the topic, and with one with as many variables as this, I would expect the chance a statement like that be correct more akin to luck than an correctly inferred results from a relevant subset of data. i.e. What industry you work in, what your actual job is, and what you already know about it is likely to wildly influence what you see. Even someone working in the security industry is likely to see only a subset related to their job/interests.
https://www.verizon.com/business/dam/img/resources/reports/2...
https://www.verizon.com/business/dam/img/resources/reports/2...
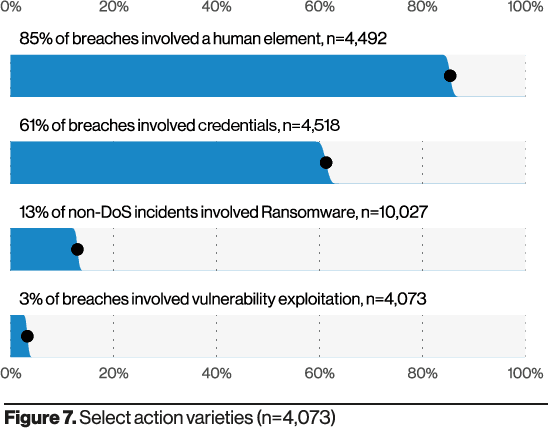
This is a very widely discussed trend in the industry and has been for literally almost a decade. It has lead to the tired trope of the number one hardening recommendation being "get rid of the users" as well as the much more helpful "users can't be expected to participate in their own security, it needs to be done for them transparently".
Those are not the same figures on the PDF listed. The PDF presented seems to be from 2019, and I can't tell because your images are presented out of context, but it looks like hey might be from a newer report?
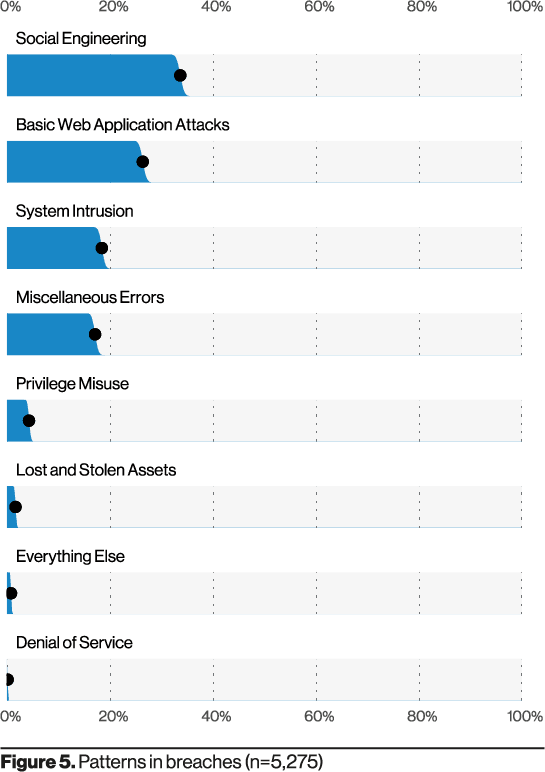
The PDF linked has a summary of findings that shows in figure 4 that 52% of breaches included hacking, and that 33% included social attacks.
Assuming I've found the document you're using as a source[1] (it's nice to have a newer version, but I hardly think it's fitting to ask me to reexamine a summary of findings chart that I was not originally presented with), it does go into more recent information.
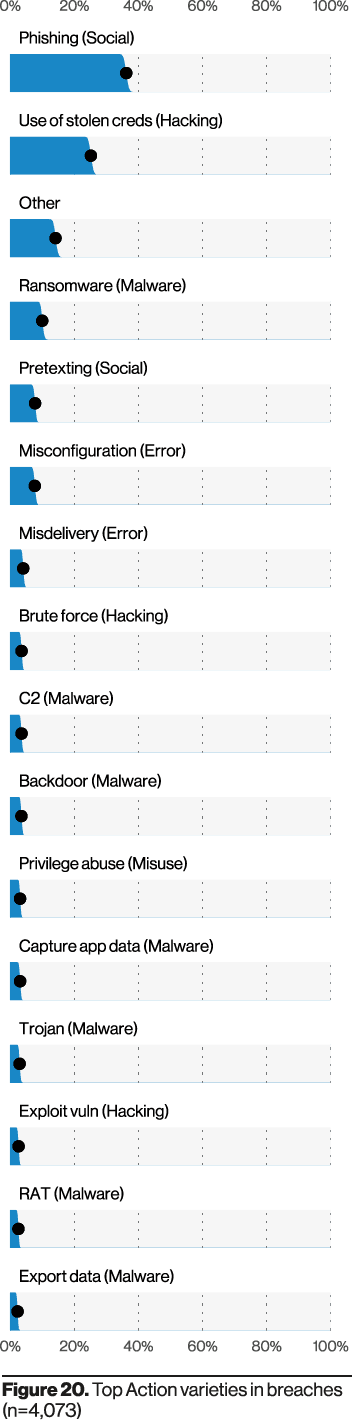
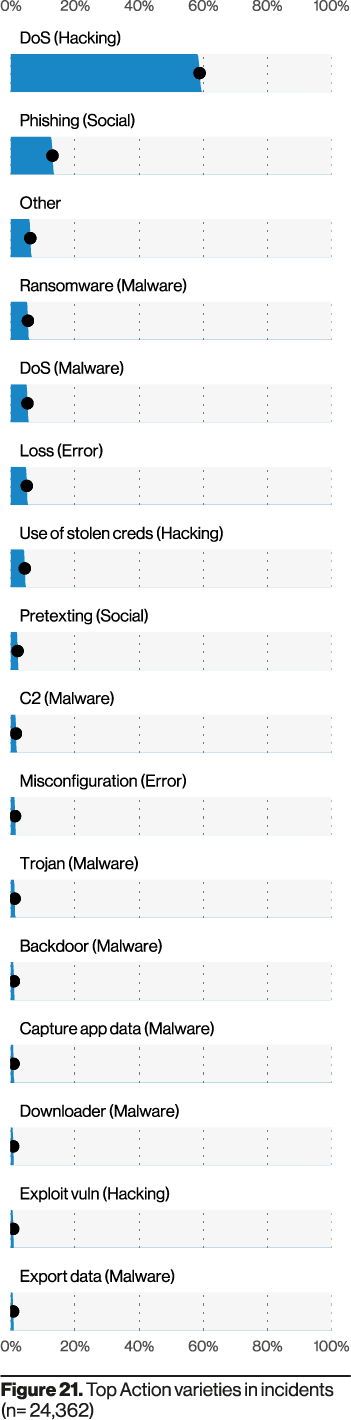
That said, figures 20[2] and 21 in the new report do shed some more light on what we're actually talking about, and brings up the difference between "incidents" and "breaches" in this report, and what they mean. They define an incident as something that compromised the integrity, confidentiality or availability of an asset, while a breach is something that results in a confirmed disclosure of information. While phishing (social) is top in breaches as a bit less than 40% and pretexting (social) also makes a good showing in the breach chart (figure 20[2]), the much more expansive category of incidents (figure 21[3]) is overwhelmingly dominated by DoS (hacking) at almost 60%.
While that may seem like splitting hairs, especially since the original comment mentioned breaches, it was in response to and in the context of iPhone users, which is end user security. These reports are about businesses, and note they're following the NAICS standard to categorize victim organizations. They source their data from paid external forensic investigations, direct recording by partners using VERIS, and converting partners existing schema of data into VERIS (paraphrasing Appendix A). I think this discussion is about people and security in general, and I don't think this data is about that, I think it's about companies and organizations.
Now, to be clear, on thinking about this more closely I fully believe that social engineering attacks likely could be the majority of attacks when taking into account end users, and I imagine quite a lot of end user malware and ransomware that is likely installed from email, but I'm not sure, and I'm not sure how much browser exploits account for that, or how much phones change the picture. If we were just considering home systems, the majority I assume are firewalled at this point, I would definitely assume social engineering, but with phones out hopping public ranges through data plans and sharing wifi at many businesses, I'm not sure how that may be changed.
In any case, I think it's completely valid to call out someone that makes a general factual statement such as "Most security breaches these days are social-engineered." without providing that evidence. It's not self evident, and there's a lot of data to look at, as we've seen.
1: https://enterprise.verizon.com/resources/reports/2021-data-b...
2: https://www.verizon.com/business/dam/img/resources/reports/2...
3: https://www.verizon.com/business/dam/img/resources/reports/2...
Some of the worst DRM has been because Apple has a vested interest in restricting your ability to use your computer freely.
I wonder why movie companies these days still insist on shipping DRM garbage. HDCP is broken on a fundamental level, you can grab strippers for about 90€ on ebay, and BD+ is similarly broken.
It literally has no purpose other than annoying customers who have rooted their Android phones (Netflix refuses to go above 480p) or want legitimate backups of their bought content.
Come to think of it, maybe that could be the basis of a right-to-repair law: companies which sell hardware products that restrict functionality or access to those who know some secret value must divulge those secrets to the device owner upon request at the time of purchase.
The only issue I can think of with a law like that is that it'd make DRM significantly less effective, though IMO that's not necessarily a bad thing.