It's not, the majority of hash power is in China. That means the Chinese government could start censoring bitcoin transactions in a week if they wanted to - by orphaning non-compliant blocks. Regardless of anything else, this centralization alone makes bitcoin a failed experiment.
https://cointelegraph.com/news/study-chinas-btc-miners-contr...
Second, I don't think we can conclude what would happen if China tried to censor.
China certainly has 51% attack capability against Bitcoin, but the only implication that of that which is clear to me is that they could potentially execute double-spends. Using 51% attack capability to orphan transactions is different.
With a double spend, there's two transactions, both signed with the same key, and no way to determine which is valid (which came first). There's no source of truth for that information.
With an orphaned block, there's only one transaction signed with the key, so you have a single source of truth. You know the transaction exists, and at some point (i.e. after a certain number of blocks), if the transaction isn't included in the chain, you can conclude with reasonable certainty that the transaction is being intentionally orphaned. This allows you to reject the chain that doesn't include the transaction as invalid, and choose the longest chain that does include it. We already don't blindly follow the longest chain: for example, blocks that are improperly formatted are already rejected.
This would, of course, having different criteria for what is considered a valid block would cause fork in the currency. There would be the Chinese censored branch and the uncensored branch everyone else is using. But for a lot of reasons, I think people would be unwilling to trade as much traditional currency for the Chinese censored currency as they would for uncensored Bitcoin.
Every fork is vulnerable to the same attack, which is why such a switch doesn't make sense. There's no way to prevent Chinese miners from mining on the "Western" bitcoin if it's the more profitable option. The censorship can be easily made reactive: first, all Chinese miners have to register and report their hash power. If the total hash power for any specific network is below X (eg. 65%) they don't have to censor. The moment they do, they start orphaning blocks that don't comply with the Chinese law. Note it also increases their profits!
The same forces (lots of cheap electricity) that resulted in the concentration of sha256 hashing in China also work for any other PoW; switching to a GPU-based PoW would at best only prolong the inevitable. Most likely GPU PoW is also China-dominated.
Proof of work has infinite economies of scale and the winner can take all property. The second property makes it profitable for the majority of hash power to cartelize and exclude others. If the cartel was smartly set by the Chinese government - allowing access to all Chinese miners and making it illegal to create smaller cartels - everyone in China would join and after a while it would be enough to mine with only ~20% of the available hash power. That's a 5x increase in revenue per watt hour!
Why? Initially, Chinese miners can mine with >65% of global power, excluding competitors. They do it until everyone else goes bankrupt, giving them 100%. Then, each individual miner can start mining with only 20% of their total power. To prevent fraud, it's enough to make everyone mine with 100% for one hour every week, all at once, to prove their total individual hash power. If some foolish foreign competitor arrives with more than 20% of the Chinese hash power, every Chinese miner turns everything on. This monopoly would be almost impossible to defeat.
However, even if you assume someone defeats it somehow - the only way to defeat it is to have an even bigger centralized entity! All that happened is a new monopoly, not decentralization.
All of this means bitcoin can never become "refuge from the growing foreign and domestic militarization of money. [..] an indispensable weapon against civil asset forfeiture, international sanctions, deplatforming, and mass surveillance" to any noticeable degree. It's currently left alone only because it's irrelevant except as a speculative toy.
But you corrected your assumption in the other comment thread, so I'll continue the conversation there.
No, it wouldn't. I don't think you're understanding the solution I'm proposing. There isn't an amount of computing power that allows you to submit invalid blocks.
>you know the transaction exists, and at some point (i.e. after a certain number of blocks), if the transaction isn't included in the chain, you can conclude with reasonable certainty that the transaction is being intentionally orphaned. This allows you to reject the chain that doesn't include the transaction as invalid
as what would happen is nodes that were online and observed the situation would follow one chain, but everyone else that joins later wouldn't be able to confirm that censorship actually happened, and follow another. If you have a solution that solves it, you solved the fundamental problem - absolute order - some other way and PoW becomes completely superfluous.
Then there's a problem of: what happens when there are contradictory transactions on two different chains at once? How do you decide which one is valid? This gets complex very fast.
If you want to try tackling the censorship issue in an automated way, you have to move away from PoW to a more typical consensus algorithm with online identities. In the simplest case, if all (ever - no new ones) network participants are online all the time, the problem becomes trivial and something close to your solution would work.
> I assumed you meant manually. This method isn't possible to automate under PoW, because any such actions require global time, but PoW is what provides time itself, creating a contradiction. What this means in practice is network splits.
I don't think you need global time to do this. More on this later in this post.
> as what would happen is nodes that were online and observed the situation would follow one chain, but everyone else that joins later wouldn't be able to confirm that censorship actually happened, and follow another. If you have a solution that solves it, you solved the fundamental problem - absolute order - some other way and PoW becomes completely superfluous.
This situation resolves itself naturally via the mechanism I proposed.
Let's follow the scenario you propose and see how it resolves. The following events happen in this order:
1. The Chinese government decides to censor transactions from a certain address, refusing to accept blocks which include transactions from that address.
2. A transaction from that address is broadcasted.
3. Chinese miners mine 5 blocks that don't contain the transaction. Nodes which have been on the network the whole time notice the censored transaction, and go to the next-longest chain, creating a fork.
4. A new node joins the network. From the new node's perspective, there are two chains, but the Chinese one is longer so you go with that. However, you still have the signed transactions from the shorter chain, and your node notices that the Chinese chain doesn't contain some of those transactions. At the time of joining, as far as you know, that transaction simply hasn't been included in the longest chain yet.
5. Chinese miners mine 5 more blocks that don't contain the transaction. The newly-added node now notices the censored transaction, rendering the current chain invalid, and goes to the longest valid chain, which is the one everyone else was on. Consistency achieved.
The implication of this solution is that when you join the network, you now have to wait for 5 confirmations to ensure none of the transactions you have are being censored in the longest chain (i.e. it takes 5 confirmations to know that the longest chain is valid). Which is certainly an important implication!
Note that absolute order doesn't matter here. We don't have to know the order of the transaction, only that it has existed for some number of blocks without being included in the chain.
> Then there's a problem of: what happens when there are contradictory transactions on two different chains at once? How do you decide which one is valid? This gets complex very fast.
The way you've worded it, that's not really all that complex--that's the same as a double spend, and it's resolved the same way any other contradictory transaction is resolved: follow the longest (valid) chain (where part of the definition is "valid" is "containing all transactions I've had for 5 confirmations").
However, I think you might have left out part of what you meant here, so I'll try to explain what I think you're hinting at. There's a sophisticated way for China to hide their attack. It works like this:
1. The Chinese government decides to censor transactions from a certain address, refusing to accept blocks which include transactions from that address.
2. A transaction from that address is broadcasted. We'll call this the censored transaction.
3. Non-Chinese miners mine a block that includes the censored transaction. This becomes the root of what we'll call the censored branch.
4. Chinese miners ignore the mined block that includes the censored transaction, and mine a block which doesn't contain the transaction. This block becomes the root of a branch we'll call the red herring branch. In that block, they include a transaction which they never broadcasted to the network. We'll call this the red herring transaction.
5. Due to superior Chinese mining capability, the red herring chain quickly becomes longer. However, after 5 confirmations, the network notices the censored transaction isn't being included in the red herring chain. So they invalidate the red herring chain and go to the longest valid chain, which is the censored chain.
6. 4 more blocks are mined on the censored chain.
7. A new node joins the network.
8. At this point, the censored branch doesn't include the red herring transaction, and the red herring branch doesn't include the censored transaction. So our previous resolution strategy doesn't work, because we don't know whether it's the red herring transaction or the censored transaction that's being censored.
First, I want to say, this is a really sophisticated attack and I want to congratulate you for coming up with it.
Second, I think this problem can be solved by sweeping up ALL the transactions in EVERY block you receive, even if they are in blocks which haven't been confirmed, and treat them as if they were broadcast to you on the network. This way, the red herring transaction gets included into the censored branch. This gives us a new resolution:
1. The Chinese government decides to censor transactions from a certain address, refusing to accept blocks which include transactions from that address.
2. A transaction from that address is broadcasted. We'll call this the censored transaction.
3. Non-Chinese miners mine a block that includes the censored transaction. This becomes the root of what we'll call the censored branch.
4. Chinese miners ignore the mined block that includes the censored transaction, and mine a block which doesn't contain the transaction. This block becomes the root of a branch we'll call the red herring branch. In that block, they include a transaction which they never broadcasted to the network. We'll call this the red herring transaction.
5. Due to superior Chinese mining capability, the red herring chain quickly becomes longer. However, after 5 confirmations, the network notices the censored transaction isn't being included in the red herring chain. So they invalidate the red herring chain and go to the longest valid chain, which is the censored chain.
6. A new block is mined on the censored chain. Since we've swept up all the transactions from the red herring chain, this block includes the red herring transaction.
7. A new node joins the network and assumes the red herring chain is the longest valid chain.
8. After 5 blocks, the new node sees the red herring chain does not contain the censored transaction, invalidates the red herring chain, and goes to the longest valid chain, which is the censored chain. Consistency achieved.
- Chinese miners (the network doesn't know that) publish a normal transaction.
- they don't include it for 30 blocks. Western nodes have already switched to a minority uncensored chain after 5 blocks, as they consider the transaction censored.
- Chinese miners include it in 31st block.
A new node joins. It follows the Chinese chain indefinitely.
The core of the problem is lack of objective time (or at least ordering): there's no way to prove to the new node that a transaction was actually censored in the past. From its perspective, the minority chain might have been created after the Chinese block with the transaction was published. As long as there's no external objective time, it's always possible to invent some attack scenario that splits the network for new nodes.
Last but not least, every minority chain is by definition vulnerable to 51% attacks, so even if a solution to censorship could exist in PoW, the minority chain could get intentionally killed this way, constantly generating double spends until people stop using it.
Only if China decides to hamper the speed of their miners by pointlessly trying unsuccessfully to censor transactions.
> - Chinese miners (the network doesn't know that) publish a normal transaction.
> - they don't include it for 30 blocks. Western nodes have already switched to a minority uncensored chain after 5 blocks, as they consider the transaction censored.
> - Chinese miners include it in 31st block.
> A new node joins. It follows the Chinese chain indefinitely.
Okay, yes. And so does the entire rest of the network, because now the blocks are valid. Yes, this is very bad, because anyone who spent money in the shorter chain can now re-spend their coins.
But critically, nothing was censored here. This is a transaction reordering, not a censorship attack.
China can do the exact same thing with fewer steps. All they have to do is go back 30 blocks, and start mining blocks with the transactions in whatever order they want. Eventually their branch will be ahead and everyone will switch to it.
So you are going to reorg after many blocks (enough to be sure a transaction is being censored). This sounds extremely undesirable as it kills finality. Today you can very reasonably be sure that after say, 6 blocks, a transaction is irreversible. That's not the case with this new rule.
With a perfect network where everyone receives all transactions immediately, and where transactions are prioritizes for inclusion by transaction fee first, and order received second, we can conclude after ONE block whether a transaction with a high enough transaction fee is being excluded. But the network isn't perfect. There's some network analysis to be done here to gather probabilities, but for the sake of simplicity, let's say the network is reliable enough that we can reasonably conclude whether a transaction is being excluded in 5 blocks (I think the number is actually lower, but let's go with 5 to be safe).
So basically, what we're saying here is that if we reject the fifth block that doesn't contain a transaction after we see it, then we're forcing a reorg.
The attack you're describing happens when someone waits for China to start ignoring a transaction, then attempts to use the resulting reorg to execute a double spend.
Last time I checked, the recommendation was to wait for 6 confirmations to prevent double spends, because it would be unreasonable for an attacker to attempt to catch up to the main block chain when the main blockchain has a 6-block head start. But if China forces a reorg after 5 blocks, then the attacker attempting to execute the double spend only needs to catch up 1 block.
Trivially, all this means is that we have to wait for 5+6 = 11 confirmations to achieve the same level of confidence that we got from 6 confirmations when China couldn't force a reorg.
But wait: China actually can't force a reorg that quickly with 100% probability. In order to force this reorg, China has to mine 5 blocks in a row. China only has 66% of hashing power, so the probability of China mining a given block is P=0.66. The chances of China mining N blocks in a row is P=0.66^N. So the probability of China even being able to force this reorg is P=0.66^5=0.13.
That's not nothing, but that's a lot of effort for China to put in just for a 13% chance of delaying a transaction. Given China can't actually censor the transaction, only delay it, why would they spend all those hashing cycles to do this? The incentives don't line up.
Followup question: how does a node coming online know not to trust China's (longer, censoring) chain? It wasn't online to have the transaction in its mempool, so it doesn't know to check for it in the longest chain.
I think it would need to check all candidate blocks with lower heights to see if their chains contain any transactions that aren't in a longer chain.
What happens if I mine off of a very old block and include my own transaction in it, and present it to you... how do you distinguish between what I just did vs the longer chain having censored the transaction this whole time?
> I think it would need to check all candidate blocks with lower heights to see if their chains contain any transactions that aren't in a longer chain.
Yes. You wouldn't need to store all these, though, you just sweep them up once you find the transactions included in the longest chain.
> What happens if I mine off of a very old block and include my own transaction in it, and present it to you... how do you distinguish between what I just did vs the longer chain having censored the transaction this whole time?
Broadcast all transactions you have which aren't already in the longest chain to the network, and wait for them to include them.
I'm not 100% sure, but I think transactions get rebroadcast automatically already until they're included.
> Startups will play a marginal role at best because their ultimate aim of monopolization flies in the face of what Bitcoin was designed to do.
I'd go further with this and say that decentralization is an active impediment to startups trying to create monopolies in the crypto space.
I think there's still room for development, but it will be hard for it to be motivated by profit. Particularly, a better-executed namecoin could be revolutionary if people started building infrastructure around it (i.e. as usernames, or a DNS replacement).
And until and unless you can use it to purchase the goods and services needed for daily life, and the military and police forces needed to secure the supplies lines of those, it will be at best a theoretical form of personal freedom.
Even if Bitcoin doesn't rely on trust, the rest of the functions of human society do.
States stop the exchange of goods within, into, or out of their jurisdiction of types or in manners not sanctioned by the state all the time, it's called “law enforcement”, and either the military or paramilitary police forces or both are often involved in it. It's never airtight, but it doesn't have to be to have a big effect.
But anyways, isn't that pretty much the anarcho-capitalist vs statist conflict that cryptocurrencies are ultimately trying to aim us towards?
Sorry if I'm completely misunderstanding your argument, but having trouble reading it in a different way.
The state will take over the entire supply chain to ensure that it transacts in a currency that it controls, crypto or otherwise.
Without that, the shared physical and legal infrastructure that supply chain depends on would cease to exist, and with it the supply chain.
Individuals, or the small communes that act financially as individuals in the crypto based trading system would have to trade in the simplest raw materials and finished products would be all have to be made hyper locally. Otherwise what entity would secure the transit of high value finished goods from supplier to customer?
I understand that it's a vision of the future that many people relish for its "freedom" from the state (but not so much from the local tribe). But universal crypto based transactions are not a drop in replacement for what we have now that keeps everything else the same. They come with their own radically different future-primitive vision for the world.
Another aspect of crypto is the ability to simply leave the oppressor's territory, taking your money with you.
I'm absolutely not saying this is a perfect solution, or that government is powerless in this situation, but it seems hand wavey to say they'll just seize control of every economic transaction. That's a VERY difficult thing to do.
And it's unnecessary. Black markets exist today and always will. The state would need to merely take over the major suppliers of raw inputs to all products, and major finished products, and that will be enough to keep crypto only relevant on the margins. If black markets become a problem due to crime (i.e. the mafia) they can be dealt with using law enforcement action.
> Another aspect of crypto is the ability to simply leave the oppressor's territory, taking your money with you.
I agree, and you will also leave behind many of the benefits that come from societies that have centralized organization, like i.e. roads and a justice system. No territory with a state that provides infrastructure is going to allow you to operate there indefinitely without paying for the privilege of using that infrastructure.
You will have to find a place with effectively no state, and provide the basics for yourself. But it would be hard, and it's not something that can scale to our current society's scale or prosperity, though.
Very hard bordering on impossible
> You will have to find a place with effectively no state
Why no state? I'm sure plenty of states would be happy to let you transact in crypto as long as you're willing to pay taxes. In fact, transacting in crypto isn't even necessary, all you need is the ability to convert crypto to local currency periodically.
What is the point of cryptocurrency if your freedom can be impinged upon by being compelled to pay taxes? What's the point of it isn't the primary medium of exchange? If it's not that, then it's just a deflationary store of value, functioning like gold, which nobody uses for daily transactions, therefore of limited value.
Why would that state accommodate your ability to convert crypto into local currency that they ultimately control? The only rationale would be to hurt their presumptive rival: the state you fled.
And more importantly, even if that works at the individual level for you and a few others who work that kind of deal with a state, how does that model scale to populations of multiple 10s of millions?
Another state may allow a few people to make that personal optimization in their territory, but they won't negotiate such agreements with millions of people. If you are a rare wealthy person able to strike such a deal with a state, you are then effectively an oligarch, and part of the state power structure.
States are made of people, and people only trust other people who they believe have skin in the game.
I think you're moving the goalpost from "crypto grants me more financial freedom" to "crypto makes me literally untouchable by governments". Nobody here is claiming the latter. I have no idea where you even got the tax evasion angle from anything I said.
Why do you think that the state that accepts you would give you anything like the market exchange rate for the cryptocurrency to their currency?
The only way would be if they had a competitive internal market for purchase of cryptocurrency, but it's not at all clear that would be the case, since in this situation, you would need asylum (a service they would be providing to you) more than they need your cryptocurrency. That would come at a price.
You could try to play these countries off one another to get the best possible exchange rate, but really, you'd have to be stupendously wealthy in crypto before those countries would begin to care enough to offer you any kind of deal.
Do you know what asylum is? I can permanently move to plenty of countries without asylum, I think you're getting a bit off track..
Maybe you don't know what it is for. People that are sane like Mr. Armstrong and Satoshi Nakamoto intended it to be used as a currency. If Satoshi is still alive I'm sure he was quite disappointed when Bitcoin decided to not scale past its blistering 7 transactions per second.
"Bitcoin can already scale much larger than that with existing hardware for a fraction of the cost. It never really hits a scale ceiling." -Satoshi Nakamoto
https://steemit.com/bitcoin/@cryptodailyuk/bitcoin-broke-coi...
Inevitably that hamstrings permissible opinions.
Not only that, the purpose of his company is to profit from cryptocurrency in a specific way, whether or not that's the 'right thing' for the space or not.
Their business model basically falls apart, for example, if people stop using fiat currencies and atomic swaps allow trades to happen without a clearing house.
All over this thread you can see waffle about money laundering or whatever else; which Coinbase cannot sidestep because they're forced to interface with banks that will cut them off, governments that don't like it if you don't do what they say, etc.
Increasing block size utilization has series tradeoffs for decentralization, privacy and reliability. Each year we learn and understand those tradeoffs better. Pro block-size increase people never seem to directly address them though, just talk around them and imply they don't matter. They do matter, a great deal.
The current system where every user is a network node is not the intended configuration for large scale. That would be like every Usenet user runs their own NNTP server. The design supports letting users just be users. The more burden it is to run a node, the fewer nodes there will be. Those few nodes will be big server farms. The rest will be client nodes that only do transactions and don't generate. https://bitcointalk.org/index.php?topic=532.msg6306#msg6306
The client nodes have to validate in addition to only doing transactions. Satoshi doesn't say that in his comment. But the faster the block size growth, the faster it gets to "every Usenet user runs their own NNTP server", and the fewer and fewer run full validating nodes.
His comment is self-contradictory.
It's funny you say that pro block-size increase people don't understand the decentralization, privacy and reliability trade-off, while the people against a block-size increase have never defined or quantified these trade-offs. And very often they also have the notion that "everyone must run a full node" that implies they don't have a good understanding of Bitcoin at all.
“Everyone must run a full node” is aspirational but not realistic. It’s nevertheless extremely valuable to continue working on ways of reducing the expense of running full nodes. MimbleWimble, Coda and others are doing a good job of exploring that problem space, as are some projects in Bitcoin that may take longer deploy.
When HN first started discussing Bitcoin almost a decade ago, the smartest skeptics here main objection was the obvious one that a distributed database where all the data is replicated across every node and which grows infinitely is likely not viable. They were right then and right now, it’s a hard problem and arguably the main existential risk to Bitcoin.
Throwing caution to wind so Bitcoin can have fast payments Now at the expense of failing at sound money later is short-sighted and irresponsible.
And nobody will claim otherwise. But there's always a trade-off, and focusing only on reducing the expense is severely misguided.
> Throwing caution to wind so Bitcoin can have fast payments Now at the expense of failing at sound money later is short-sighted and irresponsible.
The funny thing is, the inaction of the Bitcoin devs have made it fail at one of the core features of money. You cannot consider it to be acceptable, as fees are so expensive they price out a lot of people. Money should be easy to move around, and you should be able to buy large and small things with it.
Yet this is somehow preferable, because doing otherwise would make Bitcoin "fail at sound money", whatever that means.
That's conventional wisdom and applicable in lots of other places, but not in cryptosystem design. People have to accept that cryptosystems in general and cryptocurrency in particular are different domain from most other software engineering they're used to.
Any single error or bug can result in the complete compromise and failure of the entire system. The old rules of calculating acceptability of risk and errors based on whether they enable more value creation than they put at risk, no longer apply, because any/every error can result in total loss.
I believe different world views on this issue is one of the root causes of the schism in Bitcoin.
>The funny thing is, the inaction of the Bitcoin devs have made it fail at one of the core features of money. You cannot consider it to be acceptable, as fees are so expensive they price out a lot of people. Money should be easy to move around, and you should be able to buy large and small things with it.
That's a "nice to have" for sure, but not at the risk of a Global Financial Crisis style event happening to Bitcoin itself. The prudence of the Bitcoin devs has made it succeed at avoiding that so far.
>Yet this is somehow preferable, because doing otherwise would make Bitcoin "fail at sound money", whatever that means.
There's no need to be confused about that term, it has a simple, clear and easy to understand meaning. Sound money is money whose supply and value is both transparent and un-manipulatable.
When you choose to store savings in that currency, you know how it works, and you know it can't be changed in the future (to either your detriment or benefit). Sound money is a social contract that can't be broken or reneged.
By way of counter-example, in the GFC, the US Fed pumped up the money supply to prevent the failure of the banking system, risking devaluation of dollar-based savings and hyperinflation to the detriment of everyone else.
For another counter-example, the US Govt's inability to control its deficit and debt may one day result in it having to monetize the debt (print more dollars to pay for it), devaluing the dollar and dollar-based savings, and harming global confidence in the dollar as a reserve asset.
Cryptocurrency as sound money is a hedge against that, and that's the ultimate killer app. But if you lose enough decentralization, you lose this characteristic of it. Then its worthless, regardless how good of a payment system it makes.
And it will never be better than Paypal and other centralized payments services at merely transferring money quickly and cheaply, so if it has no other value proposition like sound money then its worthless.
This entire model does not sit comfortably with a permissionless, even anarchic construction like Bitcoin. Partially because it puts you in constant conflict with regulators whose relationship is your business. Secondly because if Bitcoin becomes a major currency in its own right, your role as an onramp is no longer necessary, or at least far more competitive.
And as every other exchange discovered, the real money is in offering a blistering array of coins and taking a percentage on trade between them.
Thus, it might be disappointing to cypherpunks that Coinbase is only a reluctant proponent of Bitcoin, but it's also quite predictable.
I'm not super familiar with Bitcoin's tech, but that seems sensible to me. The blockchain is already 250 GB at 7 transactions per second. If you multiplied that by 100, you still have orders of magnitude less transactions per second than credit card processors, but the hardware requirements are now high enough that few individuals could afford to run full nodes.
Fact is that each LN "channel" needs a committed amount of Bitcoin that can only be withdrawn by closing the channel. If you want your Bitcoins "secured" in you wallet, you need to close the channel. Otherwise you will - by design - have to constantly monitor the LN for malicious actors trying to withdraw you funds from your channels - which by the way is also only possible with an extremely reliable internet connection. Ultimately it's only possible to "secure" your funds against malicious actors by closing the channel. This leads to nice DoS attack vectors, see below.
Opening and closing a channel requires an on-chain transaction. This means when you only calculate with the US population, you need at least ~700 million on-chain transactions per month, assuming people get paid once a month, which is absolutely underestimating reality. Also assuming business don't trade with each other.
Assuming 7 transactions per second for the Bitcoin network (which in reality is much closer to 3 by the way), you get 7×60×60×24×30 = 18,144,000 transactions per month. So LN cannot even serve 5% of the US.
Reading the LN white paper should give you an idea on how bad it is when you compare it to reality and how people are actually using money.
There are probably going to be some big entities in the Lightning Network ("lightning service providers") that average users use to open channels in exchange for a fee. These LSPs need to closely monitor for malicious transactions, but the average user doesn't have to. The average user would only get ripped off if their LSP broadcast an invalid transaction. In that case, they could prove it to the network and everyone would leave the LSP. Eventually there will be long-standing LSPs with good reputation. People can open long-running payment channels with them. If on-chain transaction fees get really high, they could be set to timeout after a year. That gives both parties plenty of time to notice an invalid transaction. If they're paranoid about DoS or timing attack, they can close the channel a few days before it times out.
That's my understanding only from reading a few articles about how Lightning Network works, so what I'm saying might be ridiculous and I could be completely wrong.
But even if there was a way to identify bad actors, what you describe as "big entities" already exists. They are called banks, just you described one with more steps and that's a lot more complicated.
From where I sit, it seems like BTC was designed to be a currency that would free us from financial regulation, it has failed on both counts, and crypto enthusiasts are trying to turn it into an over-elaborate debit card because the alternative is for it to become a historical curiosity.
> Which can be be reneged on if one party is malicious, meaning they'll only occur between trusted parties?
This is not correct. My understanding is essentially each party is tying up Bitcoin as being between them on the blockchain, then trading cryptographically verifiable assertions of each other off-chain about what the latest status of the ongoing "tab" is between them. Either of them can close the tab at any time and reconcile to the blockchain.
They don't really need to trust each other, although this does introduce a dependency on some entity (whether the user's own server or a third party) to publish the latest version of the "tab" if the other guy maliciously tries to publish an older version of the "tab." And of course, that means you need some redundant storage / handling of those cryptographic assertions from the other guy about what the status of the latest "tab" is. But that doesn't require trust--you'd want to do it even if you trust the other party.
Or at least that's my understanding of it. I like the conceptual idea of LN but some of these details seem like dealbreakers to me.
That's the Lightning Network.
That's how two finserv companies would transact off-chain with each other, but when I go to buy a cup of coffee with a bitcoin, I'm not opening up a payment channel with them for one transaction, that would defeat the whole point. The coffee shop will use a payment processor, who isn't going to deal with me off-chain unless I'm the KYC'd customer of them or some other finserv they trust. (please correct me if I'm wrong here)
You won't want to open up a payment channel to them, but you don't need to. You just need an already open payment channel to someone who is, or (more importantly) there is some route of payment channels between you and them through any number of intermediaries.
There won't be a way to enforce KYC on the network itself, and you don't need trust for this to work.
But because of the inherent cost / time / complexity reduction benefits of just maintaining big channels between large entities, normal people and businesses will inevitably be incentivized to just work through banks to do this. The banks can just hold all their money and handle keeping the channels between themselves open and funded.
And that's where I think you're correct. It leads to a world where KYC can be required easily because the vast majority of legitimate use cases will be through centralized endpoints.
However, 250 GB is approximately 25 GB per year (since Bitcoin started in 2009), which, if you multiply it by 100, is 2.5 TB per year. That means it will take about 6.4 years to fill a 16 TB hard drive, which should cost less than $600:
https://www.techradar.com/uk/news/worlds-largest-hard-disk-d...
It's not hard to imagine someone paying under $100 per year to run a full node, whereas on the day that TechRadar article was published, the average price of a bitcoin transaction was $4.58 as seen here:
https://bitinfocharts.com/comparison/bitcoin-transactionfees...
1) have centralisation
2) assume storage space will expand exponentially since the entire point of bitcoin is many many copies of its ledger
3) come up with a new method more secure than PoW but still decentralised
Good luck with (3). (1) and (2) are not good choices. So they moved it off the chain into lightning network.
https://www.youtube.com/watch?v=agppUdX9YvI&feature=youtu.be...
An actual market-powered mechanism for data-pruning. As the price of new transactions rise, the amount paid by old (rebroadcast) transactions rise more. Network hits equilibrium where data in == data out.
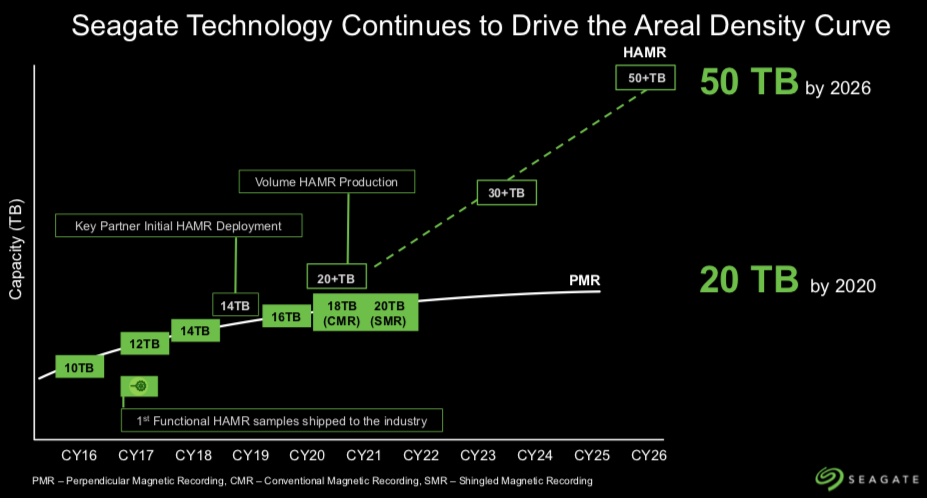
Would you say that the credit card network, or PayPal, has exponentially increasing storage requirements? It's possible for Bitcoin (for example) to be decentralised and useful to the world and only require linearly increasing storage space.
Fortunately it seems that storage technology will continue to scale linearly over the coming years too:
> (ignoring things like High Frequency Trading)
HFT is not a blockchain transaction. They are off blockchain transactions entirely because they trade money between bitcoin / other cryptos and dollars.
> there is only a limited number of potential active crypto-currency users
My entire point is that this limits them from growing. If the blockchain is kept from exploding, it helps to onboard more users.
> Would you say that the credit card network, or PayPal, has exponentially increasing storage requirements?
Indeed not. But their user base is now standardised. So they have a predictable number of transactions every second. However, their storage requirements are still obviously industrial grade server farms. The point of bitcoin is that everyone should have a copy of every transaction (excluding lightning network transactions). You see the connection? Not all of us can have our own server farms. If we all wants to store every transaction in the way the parent of my previous comment alluded to (increase block size), each of us will need our own mini server farm i.e. exponential storage growth.
> It's possible for Bitcoin (for example) to be decentralised and useful to the world and only require linearly increasing storage space.
Yes. It'll level off at some point. But we are far, faaar away from that point. So it'll take quite a while before it levels off.
Is that the point of bitcoin? Satoshi said:
> Long before the network gets anywhere near as large as that, it would be safe for users to use Simplified Payment Verification (section 8) to check for double spending, which only requires having the chain of block headers, or about 12KB per day. Only people trying to create new coins would need to run network nodes.
https://satoshi.nakamotoinstitute.org/emails/cryptography/2/
(He also didn't say anything about "lightning network transactions".)
> If we all wants to store every transaction in the way the parent of my previous comment alluded to (increase block size), each of us will need our own mini server farm i.e. exponential storage growth.
The BTC blockchain is currently 250 GB. If blocks had been 10 times bigger, the blockchain would still be less than 3 TB, and blocks would almost never be full, which would reduce transaction fees and help to onboard more users. I don't think that storing 3 TB of data requires a server farm.
Correct. I'm not going by what Satoshi said, but by what development the bitcoin core team is aiming to create now.
> If blocks had been 10 times bigger, the blockchain would still be less than 3 TB
Correct. The aim of the project is to keep it as small as possible. 3 TB may not seem prohibitive today, but that's because there's hardly been any usage of the network compared to what the real world looks like. If bitcoin truly competed with Visa / Mastercard, both of those numbers will start looking a lot bigger. If the compressed version was 3TB, the bigger blocks version now becomes 30TB - suddenly far out of consumer grade storage for a normal person.
To give an analogy, it's like saying that there should be a law limiting people to only buying 5 books, because if there wasn't a limit then someone could buy a quadrillion books, which would require cutting down all the trees in the world. You're trying to prevent a problem that won't exist, by introducing a restriction that causes a very real problem instead.
I don't think so. That also requires a faster cycling of transactions than the current 10 minute round. But yes, obv a larger number of transactions can fit into the block so throughput will increase.
> 30 TB blockchain (which would fit on two hard drives, which many consumers have)
1) I don't know if you understand who "consumers" are. 30 TB is far, faaaaaar away from what a normal consumer has. Most of us have a laptop at most and that limits us to 1 TB storage. I personally have a lot of cloud storage, but I'm not the average consumer. I'm highly tech savvy compared to the normal person. So go out and talk to people not in tech and see what their tech specs look like. If they can't match up to you, they still need to be able to process transactions.
2) I didn't say it doesn't need a 30TB blockchain. You're completely misunderstanding my point. I'm saying your glib observation of "oh it's 300GB now, it can scale up to 3TB if it's bigger" is highly ill informed. If you push it only 1 order of magnitude, you're going from 3TB to 30TB and it becomes untenable. Now instead if it was 10KB and scaled to 10MB, it obv makes no difference even with 3 orders of magnitude.
3) You're also not understanding the larger picture. If all transactions in history have to be stored in the blockchain, it requires scaling to become less than linear (or at max, linear) to keep up with consumer storage expectations. It doesn't matter what the size of the blockchain is now (as long as it's within say 1TB that the average consumer can access). It matters how big it gets when there are billions of transactions flowing through it every day. So by that account, even 250GB is a very big number because once we hit billions of transactions, unless the relationship is inverse exponential, we'll breach limits long before touching that point.
> You're trying to prevent a problem that won't exist
The problem that won't exist of billions of transactions passing through the blockchain? Possibly if we had off chain solutions, yes. Which we do in very early stages. If not, the problem is very very real.
Why does it have to fit on a laptop? Only miners influence which tx get into a block, not people on laptops.
>The problem that won't exist of billions of transactions?
Visa does 1 trillion tx/yr. Bitcoin tx is ~500 bytes That's just 500 TB/year. Miners with today's hardware can store that easily. A pruned observer node could run with just a few hundred dollars of hard drives even at Visa scale!
The bottom line is that Satoshi and others thought about this and no one saw it as a problem until Blockstream and other VC funded startups began pushing sidechains that they could profit from.
The very fact that you guys are not recognising this means that you still don't understand the concept of decentralisation and want to settle with the altcoin route of making up the word as you go along and if it fits your narrative. If your entire chain was at the mercy of a few large mining corporations, you are dead in the water. The attack vector is easily compromised and you have no leg to stand on.
Each node would need to download 1.4 TB of data per day (500TB / 365) to keep up, and the UTXO set would presumably expand dramatically with a volume increase of that magnitude, making it impracticable to store even a pruned state on a consumer hard drive.
And it needs 3TB?? Cmon, that's not lot of gain for a lot of loss of control by the average.
"Decentralization" is a means to an end. Not everyone have to run a full node, as long as there's enough.
It's amusing that LN is touted as a solution, since decentralized routing is an unsolved problem, meaning that LN will be more centralized than what it's supposed to solve.
Quite cool approaches. The problem is that you can't attach data to transactions, so only useful for a subset of applications, those unlikely to create much bloat in the first place.
Bitcoin will definitely singularly emerge as the new common 'numéraire' in the near to mid-term (5 to 10 years). I love that you specifically call out the omnipresent crypto scams, because they are what disappointed me from the whole endeavor once they emerged in the ICO craze. Once 1 bitcoin has price of 500,000 to a few million in USD per individual 'bitcoin' UXTO, it'll be obvious for governments to just start using it, and create dual money systems that are just layers on top of the (maybe single, maybe not) existing, working blockchain, despite its slowness. China is pursuing this now, even in anticipation of large price increases.
IMO Bitcoin is definitely the numeraire of the future, and it is certainly not a sure thing right now but I am extremely certain of this. It then becomes so trivial to do aggregate balance of payments calculations without so much sketchy behavior by fraudulent sovereigns that want to represent their own vision of 'real trade' for various purposes, such as economic warfare.
For non-finance people, numeraire is a representative abstraction of a 'unit of exchange', used to simplify things. You can then idealize situations like having riskless borrowing, which simplifies many formulae. But this is not an accurate portrayal of reality, (look up sovereign defaults, as one example. Greece, Spain, Italy, some Asian countries at different times, Argentina, Venezuela, etc.) So having a numeraire that isn't sovereign would be really impactful in making all economic participants way more honest, outside of the immediate smaller-scale effects of allowing people to get their cryptos ropped by unscrupulous people on the darknet.
From Wiki: "The numéraire is a basic standard by which value is computed. In mathematical economics it is a tradable economic entity in terms of whose price the relative prices of all other tradables are expressed"
Anyways, the Bitcoin protocol could definitely fail, for any number of a few different reasons, but at present barring some kind of major technological paradigm shift that breaks existing cryptography (maybe QC, maybe something different) it is uniquely positioned to become the de-facto standard for all balance of payments activity internationally. Scalability issues are definitely a factor, but hey, the mempool is working its hardest until they rewrite the underlying consensus mechanisms to work at larger scale. But as a settlement system and a darknet unit of exchange, it is extremely clear that this is the first hard asset that won't just vanish at the mercy of sovereigns. Very powerful new technology.
Notice the vague treatment of actual cryptocurrency applications. There are lots of predictions about startup activity, "flippenings" and venture capital, but little about the goods and services customers will actually be buying, or what specifically startups will be building.
It's this kind of thinking that leads people into the dark thicket that is "tokens": digital instruments bought and sold largely for speculative purposes. It's understandable. The ability to print money is a fantasy of many people from a young age.
The last two years have seem a solid refutation of this notion. Almost every token has lost value against Bitcoin. It seems reasonable to conclude that the carnage will continue.
So the money printing press ship has sailed. It's going to come as a shock for many people (some with economics degrees), but bootstrapping censorship-resistant money is a one-time deal. Any attempt to profit from the undertaking harms the credibility of the founders. Only the genuine scammers are left to continue the exercise.
Here's a vision for the future of Bitcoin. Bitcoin will extend its role as a refuge from the growing foreign and domestic militarization of money. It will become an indispensable weapon against civil asset forfeiture, international sanctions, deplatforming, and mass surveillance.
That's your application for Bitcoin in the '20s. And it's a doozy. It places Bitcoin on the side of personal freedom and on a collision course with some of the world's biggest governments, including the US. There will be many attempts to "ban" Bitcoin.
Startups will play a marginal role at best because their ultimate aim of monopolization flies in the face of what Bitcoin was designed to do.