News for hackers. Stuff that matters.
Re:How to Compromise the Enterprise Endpoint by Mandatum on Tuesday June 28, 2016 @11:05PM (#11999247)
"Apple Computers Don't Get Viruses"

Still a very common misconception, however it's fair to say that macOS is still much "less likely" to be infected because of quantity.

Yes, there are now drive-by packs, crypters and RAT's that include OSX as a target. But the ratio for infections would be vastly lower.

Re:How to Compromise the Enterprise Endpoint by wyqydsyq on Wednesday June 29, 2016 @12:12AM (#11999443)
Size of user base is pretty much irrelevant to how vulnerable an OS is, Linux/GNU and BSD derivative operating systems are inherently more secure than NT based ones due to user/group permissions and privilege escalation being a core aspect of the former, and a tacked-on afterthought of the latter.
Re:How to Compromise the Enterprise Endpoint by raesene6 on Wednesday June 29, 2016 @06:26AM (#12000651)
err no.

outside of rarely used acl systems basic unix/linux permissions are far less granular than the windows equivalents.

For desktops modern windows handles things very similarly to modern linux, which is to say that you don't run as "root" or "administrator" by default and programs request escalated privileges via sudo on linux and UAC on windows.

As to privesc vulns, most desktop linux distros have limited protections there. One kernel bug can see someone escalate from user to root fairly easily.

With modern Windows apps there is at least a sandbox in play, so that a sandbox escape is required in addition to the kernel bug.

Both Operating systems can be configured to be more secure of course...

Re:How to Compromise the Enterprise Endpoint by pjmlp on Wednesday June 29, 2016 @02:38AM (#11999895)
NT has a more secure model than UNIX since day one, modeled on top of object capabilities, much more powerful than UGW permissions.

If people decide to run as root that's their problem.

Also you don't need root to exploit UNIX users, getting hold of their $HOME is way more valuable than getting hold of the OS.

Re:How to Compromise the Enterprise Endpoint by Spooky23 on Wednesday June 29, 2016 @08:00AM (#12001041)
Sure, except that you have functions like processing fonts and image formats in the kernel. Layer on userland stuff like OLE and IE and you have a cocktail for security hell.

When things work correctly, NT has historically had a more robust and accessible set of controls, although I think modern UNIX closed that gap. But things often don't work correctly, and the complexity of the ecosystem makes it pretty trivial to exploit.

Re:How to Compromise the Enterprise Endpoint by pjmlp on Wednesday June 29, 2016 @09:28AM (#12001482)
It is not perfect, but it possible to configure properly.

Also NT always focused on the user productivity first and as server afterwards.

Whereas UNIX always focused on the server first and user productivity afterwards.

It is always a mix and match between security and productivity.

Re:How to Compromise the Enterprise Endpoint by Decade on Wednesday June 29, 2016 @04:40AM (#12000291)
A security model defeated by a bonkers architecture.

I’m especially baffled that font processing is in the kernel. Allegedly, Windows 10 now moves non-system fonts into a restricted user-mode process, so exploits are a lot harder. But it still acts like the kernel is doing the processing, for backwards compatibility.

Re:How to Compromise the Enterprise Endpoint by mappu on Wednesday June 29, 2016 @03:06AM (#11999978)
>object capabilities, much more powerful than UGW permissions.

    man 5 acl
>If people decide to run as root that's their problem. Also you don't need root to exploit UNIX users, getting hold of their $HOME is way more valuable than getting hold of the OS.

Same on windows.

Re:How to Compromise the Enterprise Endpoint by zyx321 on Wednesday June 29, 2016 @05:41AM (#12000486)
>>getting hold of their $HOME is way more valuable

>Same on Windows

Windows 8 Metro/Modern/UWP apps do not have access to your home directory.

What is being done to improve the situation on the Linux side of things?

Re:How to Compromise the Enterprise Endpoint by pfg on Wednesday June 29, 2016 @06:17AM (#12000629)
I believe Flatpak/Snap (Fedora/Ubuntu's new app packaging formats) makes this possible quite easily. It'll take quite some time until these initiatives really take off, but then again things aren't all that different on Windows today. A typical Windows system is still one Office macro away from losing $HOME.
Re:How to Compromise the Enterprise Endpoint by raesene6 on Wednesday June 29, 2016 @06:35AM (#12000686)
But then no standard desktop OS is immune to users executing code from untrusted sources, you need something more locked down like iOS for that.

To get a macro running in office the user has to explicitly ignore security warnings to do it, this would be the same in linux or MacOS where code execution capabilities were present.

Re:How to Compromise the Enterprise Endpoint by pfg on Wednesday June 29, 2016 @06:55AM (#12000756)
I'm making a comparison to Windows, and my point was that it's no different there today despite the fact that Metro apps exist (just like Flatpak/Snap exists on Linux). Walled gardens such as iOS are definitely superior in that respect.

> To get a macro running in office the user has to explicitly ignore security warnings to do it, this would be the same in linux or MacOS where code execution capabilities were present.

Sure, but it's pretty easy to ignore those warnings when you see something like [1] or [2].

[1]: https://3.bp.blogspot.com/-ginpmnFHC_E/V3J3kFADrxI/AAAAAAAAo...
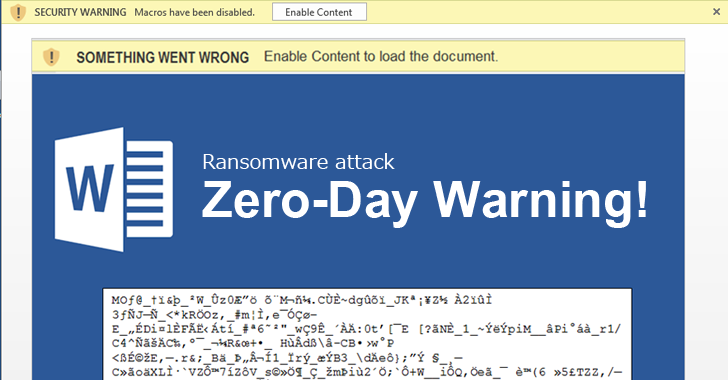
[2]: https://pbs.twimg.com/media/CiqwqUOWgAAVTzE.jpg:large

Re:How to Compromise the Enterprise Endpoint by raesene6 on Wednesday June 29, 2016 @09:41AM (#12001553)
indeed those messages are good examples of social engineering, but when comparing OS security there's nothing inherent about MacOS or Linux that would make them any more resistent to the same kind of social engineering attack.

I'd suggest that the reason that there are fewer attacks of that nature on those platforms isn't down to superior OS security but less profit available to attackers, due to smaller market share and perhaps lack of a ubiquitous target app. like office.

Re:How to Compromise the Enterprise Endpoint by pfg on Wednesday June 29, 2016 @04:28PM (#12004579)
I think you're missing my point. I'm not saying either is better in that respect (like zyx321 claims for Windows), I'm just saying they're both just as vulnerable despite the existence of sandboxed apps.
Re:How to Compromise the Enterprise Endpoint by pjmlp on Wednesday June 29, 2016 @04:55AM (#12000335)
The IEEE 1003.1e draft 17 ("POSIX.1e") document describes several security extensions to the IEEE 1003.1 standard. While the work on 1003.1e has been abandoned, many UNIX style systems implement parts of POSIX.1e draft 17, or of earlier drafts.

Note the implement parts of, that is not something UNIX has in any portable way.

Re:How to Compromise the Enterprise Endpoint by Mandatum on Wednesday June 29, 2016 @12:28AM (#11999489)
likelihood of infection != vulnerability

If you live in a bad neighbourhood, you're more likely to get shot. If you live in a nice neighbourhood, you might get shot, but it's much less likely.

The ability for someone to shoot you in each neighbourhood is irrelevant when talking about likelihood of being shot.