When things work correctly, NT has historically had a more robust and accessible set of controls, although I think modern UNIX closed that gap. But things often don't work correctly, and the complexity of the ecosystem makes it pretty trivial to exploit.
Also NT always focused on the user productivity first and as server afterwards.
Whereas UNIX always focused on the server first and user productivity afterwards.
It is always a mix and match between security and productivity.
I’m especially baffled that font processing is in the kernel. Allegedly, Windows 10 now moves non-system fonts into a restricted user-mode process, so exploits are a lot harder. But it still acts like the kernel is doing the processing, for backwards compatibility.
man 5 acl
Same on windows.
>Same on Windows
Windows 8 Metro/Modern/UWP apps do not have access to your home directory.
What is being done to improve the situation on the Linux side of things?
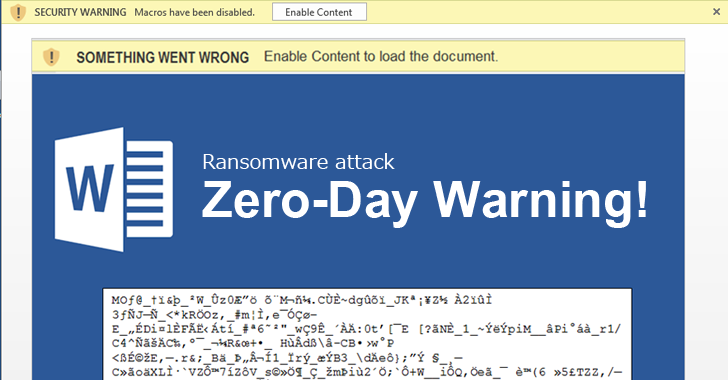
To get a macro running in office the user has to explicitly ignore security warnings to do it, this would be the same in linux or MacOS where code execution capabilities were present.
> To get a macro running in office the user has to explicitly ignore security warnings to do it, this would be the same in linux or MacOS where code execution capabilities were present.
Sure, but it's pretty easy to ignore those warnings when you see something like [1] or [2].
[1]: https://3.bp.blogspot.com/-ginpmnFHC_E/V3J3kFADrxI/AAAAAAAAo...

I'd suggest that the reason that there are fewer attacks of that nature on those platforms isn't down to superior OS security but less profit available to attackers, due to smaller market share and perhaps lack of a ubiquitous target app. like office.
Note the implement parts of, that is not something UNIX has in any portable way.
If people decide to run as root that's their problem.
Also you don't need root to exploit UNIX users, getting hold of their $HOME is way more valuable than getting hold of the OS.