To get a macro running in office the user has to explicitly ignore security warnings to do it, this would be the same in linux or MacOS where code execution capabilities were present.
> To get a macro running in office the user has to explicitly ignore security warnings to do it, this would be the same in linux or MacOS where code execution capabilities were present.
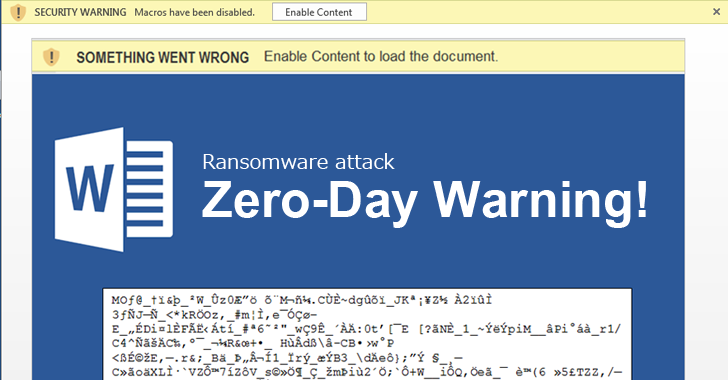
Sure, but it's pretty easy to ignore those warnings when you see something like [1] or [2].
[1]: https://3.bp.blogspot.com/-ginpmnFHC_E/V3J3kFADrxI/AAAAAAAAo...

I'd suggest that the reason that there are fewer attacks of that nature on those platforms isn't down to superior OS security but less profit available to attackers, due to smaller market share and perhaps lack of a ubiquitous target app. like office.