News for hackers. Stuff that matters.
Re:Zero-Day Exploitation of Atlassian Confluence by yabones on Thursday June 02, 2022 @10:20PM (#31603475)
This is a great case for why proxy pre-auth is so important. Doesn't matter how buggy and riddled with worms your app server is if nobody can get to it without a valid token. Sure, it introduces plenty of other problems, but it does really help with this. At the end of the day, you shouldn't be able to execute anything until you're authenticated.
Re:Zero-Day Exploitation of Atlassian Confluence by tyingq on Friday June 03, 2022 @01:05AM (#31604499)
Probably would have helped a bit if their java server process wasn't running as root as well.
Re:Zero-Day Exploitation of Atlassian Confluence by elric on Friday June 03, 2022 @05:17AM (#31605986)
No one sane runs confluence as root. But RCE is RCE. It's always serious, even if the user isn't privileged. It's significantly easier to get root access once you have access to an unprivileged acccount than without. And with tools like Confluence, there's a good chance that if you control the application, you can intercept login requests and steal credentials. Which can then likely help you gain access to other services.
Re:Zero-Day Exploitation of Atlassian Confluence by emmelaich on Friday June 03, 2022 @09:11AM (#31607734)
It would help if the run-user was not the same user that owns the files on disk. The run-user should only need to write logs and caches and databases. Not jsp files.

I usually try and make this so, but it is often very hard to impossible. Vendors do not make it easy.

Re:Zero-Day Exploitation of Atlassian Confluence by tyingq on Friday June 03, 2022 @07:42AM (#31606998)
>No one sane runs confluence as root.

See "Figure 1. Process tree in Volexity Volcano Server from the infected Confluence server"

https://www.volexity.com/wp-content/uploads/2022/06/Figure1....
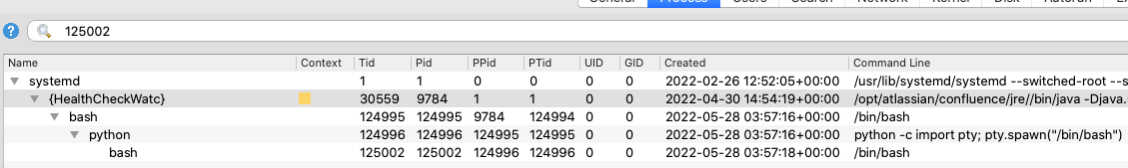
I didn't mean running as non-root would fix the problem, just that a remote root RCE was worse than a normal RCE.

Re:Zero-Day Exploitation of Atlassian Confluence by omegalulw on Friday June 03, 2022 @05:37AM (#31606153)
> And with tools like Confluence, there's a good chance that if you control the application, you can intercept login requests and steal credentials.

I thought Atlassian products were well trusted. Is that not the case?

Re:Zero-Day Exploitation of Atlassian Confluence by rst on Friday June 03, 2022 @08:22AM (#31607283)
They've had a string of script-injection vulnerabilities with similar severity -- the last was less than a year ago:

https://confluence.atlassian.com/doc/confluence-security-adv...

Each time, they patch the particular vulnerable script, but they don't seem to have done anything systematic which would eliminate the entire class of vulnerabilities (like, say, adding taint-checking for unquoted, client-supplied content before running code as an OGNL script). So they keep coming up.

Re:Zero-Day Exploitation of Atlassian Confluence by acdha on Friday June 03, 2022 @10:32AM (#31608813)
They’re widely used, which is not the same. If you’re a customer you’ll routinely encounter bugs, clumsy or inaccessible UI, annoying limitations, and performance issues which take ages to get fixed if ever. I would not assume that they’re better at security than everything else.
Re:Zero-Day Exploitation of Atlassian Confluence by latchkey on Friday June 03, 2022 @01:30AM (#31604625)
Nailed it.

Let's also admit that setting up iptables is harder than it needs to be. I mean, not after the first twenty times... you eventually remember all the arcane logic and expect everyone else to as well.

Re:Zero-Day Exploitation of Atlassian Confluence by bogantech on Friday June 03, 2022 @02:24AM (#31604909)
If you're manually editing iptables rules in production in current year you're doing it wrong anyway, you should have some form of config management like ansible/salt/puppet etc that make it dead simple to add rules or at the very least just use firewalld or something
Re:Zero-Day Exploitation of Atlassian Confluence by heurisko on Friday June 03, 2022 @05:18AM (#31605996)
In the past, I've found making tomcat listen on unprivileged 8080 and proxying it using nginx on 443 works well.
Re:Zero-Day Exploitation of Atlassian Confluence by miohtama on Friday June 03, 2022 @05:48AM (#31606241)
Even better running the system as a Docker, or other, container image with read only filesystem.
Re:Zero-Day Exploitation of Atlassian Confluence by gjvc on Friday June 03, 2022 @03:43AM (#31605390)
who in the hell does this?
Re:Zero-Day Exploitation of Atlassian Confluence by reegnz on Friday June 03, 2022 @05:17AM (#31605988)
Mostly Linux-illiterate people, who want to bind to privileged ports (443), and have no idea about systemd sockets[1] and socket-activation[2], so they stick with the first solution that works.

Most people don't know that you can have systemd bind to the privileged ports for you, and hand over the fd to the port to your (unprivileged) process.

Same goes for docker/containerd btw, if you run docker as root nowadays, you are doing it wrong.

[1] https://www.freedesktop.org/software/systemd/man/systemd.soc... [2] https://www.freedesktop.org/software/systemd/man/systemd-soc...

Re:Zero-Day Exploitation of Atlassian Confluence by latchkey on Friday June 03, 2022 @01:27AM (#31604614)
False sense of security or just plugging one hole in a wedge of swiss cheese. It isn't always the server, sometimes it is just the framework. A proxy won't stop that.

https://www.zdnet.com/article/equifax-confirms-apache-struts...

Re:Zero-Day Exploitation of Atlassian Confluence by FeepingCreature on Friday June 03, 2022 @02:55AM (#31605076)
The metaphor of plugging holes in a wedge of swiss cheese is actually the basis for the aviation industry's security model!

https://en.wikipedia.org/wiki/Swiss_cheese_model

Re:Zero-Day Exploitation of Atlassian Confluence by rob74 on Friday June 03, 2022 @11:07AM (#31609322)
It's more a risk management model than a security model. It tries to build a safe system from layers that are not 100% safe (e.g. because components on a plane may fail or people may not follow procedures exactly). That's why in an airplane accident it's not usually one single cause, but a whole string of things that have gone wrong. But still, we should try to keep the holes in the individual layers of cheese as small and as few as possible...
Re:Zero-Day Exploitation of Atlassian Confluence by JohnJamesRambo on Friday June 03, 2022 @08:33AM (#31607361)
This is really neat and novel to me, thanks for sharing.
Re:Zero-Day Exploitation of Atlassian Confluence by bombcar on Friday June 03, 2022 @09:16AM (#31607795)
The IT version of it is sometimes called "defense in depth" - even if each individual layer has weaknesses, combining them gets something stronger.

This often doesn't apply in cryptography; where adding two separate functions may result in a system that is actually weaker to attack.

Re:Zero-Day Exploitation of Atlassian Confluence by rob74 on Friday June 03, 2022 @11:09AM (#31609351)
Well yeah, if you put two slices of Swiss cheese side by side instead of on top of each other, you have given the attacker a wider choice of holes...
Re:Zero-Day Exploitation of Atlassian Confluence by bedatadriven on Friday June 03, 2022 @01:56AM (#31604748)
Your link points to a vulnerability that could have been mitigated by putting the internal application developped with Apache Struts behind a proxy server like Nginx or GCP Identity Aware Proxy (IAP) that authenticate the request before the request is forwarded to the application server.

This only applies to apps for internal use like Confluence or Jenkins, not publically accessible websites.

Re:Zero-Day Exploitation of Atlassian Confluence by Xylakant on Friday June 03, 2022 @01:52AM (#31604723)
Proxy preauth could be able to mitigate a vulnerable framework. The idea is that you never connect to the application server itself, but to a proxy that requires a separate authentication. That’s obviously not possible for a public-facing application.

Now, if the attacker has access to the proxy authentication, all of this doesn’t help much, but at least you could track and limit who can access what chunks.

Re:Zero-Day Exploitation of Atlassian Confluence by wtch98 on Friday June 03, 2022 @02:15AM (#31604868)
My confluence server is behind a proxy which requires a valid client certificate to talk to the server

I have other proxies which require OIDC authentication before passing any packets on

Now sure, I'm still vulnerable to internal attackers from my company, but that's an audited trail to a real specific user, not just a random botnet on the internet.

Re:Zero-Day Exploitation of Atlassian Confluence by benfrancom on Friday June 03, 2022 @06:48AM (#31606635)
Smaller attack surface internally, for sure. I also assume internal networks are hostile, not just from internal threats, but from external lateral movement.
Re:Zero-Day Exploitation of Atlassian Confluence by YPPH on Friday June 03, 2022 @01:56AM (#31604751)
I'm don't follow. If you have a pre-auth reverse proxy in front of your web application, you drastically reduce your attack vector.

An unauthenticated attacker can no longer simply rely on a vulnerability in the application or underlying framework, but must first obtain an employee's credentials, or find another vulnerability in the proxy or authentication infrastructure.

This isn't a false sense of security. It is a concrete additional layer of security which has tangible benefits.

Re:Zero-Day Exploitation of Atlassian Confluence by YPPH on Friday June 03, 2022 @09:53PM (#31616106)
I don't * - Too late to edit.
Re:Zero-Day Exploitation of Atlassian Confluence by jacquesm on Friday June 03, 2022 @03:43AM (#31605387)
Plug enough holes though and at some point it starts to have effect.

The real problem is if there only one wedge, you need to combine that strategy with multiple layers of security to get anywhere, otherwise the first hole is the last.

Re:Zero-Day Exploitation of Atlassian Confluence by RektBoy on Friday June 03, 2022 @05:32AM (#31606111)
Exactly, I mean everytime I saw any of this self-hosted SW, open directly to internet, my eye is starting to tick.
Re:Zero-Day Exploitation of Atlassian Confluence by harmon on Thursday June 02, 2022 @10:40PM (#31603609)
Agreed, if not a proxy then put your services behind a VPN or a bastion host when possible.
Re:Zero-Day Exploitation of Atlassian Confluence by dx034 on Friday June 03, 2022 @04:03AM (#31605516)
And the likes of Cloudflare access or VPN only access via Tailscale make it so easy to keep it protected. I'm always a bit shocked when I come across publicl ogins for Jira or Confluence instances of large corps.
Re:Zero-Day Exploitation of Atlassian Confluence by pm90 on Thursday June 02, 2022 @11:30PM (#31603948)
Yup. Really easy to set this up with the IDP's available today too.
Re:Zero-Day Exploitation of Atlassian Confluence by RulerOf on Friday June 03, 2022 @01:28AM (#31604615)
In the IdP/SP/SAML sense of it, I'm really used to that level of validation actually hitting the application and being processed through an authentication subsystem, rather than being done at the webserver level.

Possibly just some nginx features I'm not familiar with, or are there whole apps out there that serve to be nothing other than an authentication layer inside of a webserver? Are they popular?

Re:Zero-Day Exploitation of Atlassian Confluence by InitialBP on Friday June 03, 2022 @11:03AM (#31609284)
Sorry if I misunderstood the question, sounds like you are asking if there are some common tools that do auth outside of the application before passing traffic back.

Google IAP is a big one, and Cloudflare Access can let you do similar things (link an internal service to Cloudflare network and Cloudflare will deny someone ability to talk to that service until they've validated their identity to cloudflare and it matches your rules somehow.

Re:Zero-Day Exploitation of Atlassian Confluence by tatersolid on Saturday June 04, 2022 @11:08AM (#31621180)
Azure AD Application Proxy fits the bill for Microsoft 365 shops.

Nothing from Atlassian should ever be exposed to the public internet. Atlassian stuff is a security tire-fire with very old dependencies even in the latest releases, a painful reinstall/config merge needed for even minor patches, and no auto-update mechanism.

Re:Zero-Day Exploitation of Atlassian Confluence by RulerOf on Sunday June 05, 2022 @09:30PM (#31636507)
You absolutely do, but I was more interested in the mechanics of it at the webserver level rather than SaaS equivalents. The Google IAP one is helpful as I only knew about Cloudflare Access.
Re:Zero-Day Exploitation of Atlassian Confluence by tyingq on Friday June 03, 2022 @01:39AM (#31604661)
HTTP Redirecting out to an idp and it posting back to the application with a SAML assertion is pretty common, if that's what you mean. Lots of people do that with things like O365, the AWS Web Console, etc.
Re:Zero-Day Exploitation of Atlassian Confluence by RulerOf on Sunday June 05, 2022 @09:32PM (#31636516)
Of course. Just asking how is the web router aware of whether or not the redirect is necessary if you're not hitting the application to validate login state.