A phone service is implicitly device-locked (well, doesn't have to be, but it doesn't make sense to allow multiple devices per number anyway). Just using device credentials could allow anyone to log in with that information and use your subscription or pose as you.
As for ADSL or other forms of internet, there is already a second factor - ISPs generally know from which vicinity you are connecting from, and when you log in with your account information in your modem, they can match what's on your account to your physical "drop" and assert that it is at least within the same neighborhood - again, creating a physical second factor. This is also why your internet service generally needs to be "moved" whenever you change your residence.
A SIM card allows the freedom as the GP mentioned, without requiring someone from the centralized authority to process the request somehow.
There is a huge difference if you think about it for a bit.
The way forward is to get rid of the SIM and access those carrier networks through credentials, ideally I would love to see it as a cryptographic receipt that you get from your payment provider and pass it to the the carrier as a proof of right for account and usage of their networks.
SMS-based 2FA is not exploited by breaking any cryptography or exploiting some software vulnerability. It's by "asking nicely" the carrier's customer support idiots to associate a new SIM to the target account & number.
Replacing the SIM with username/password wouldn't do anything - instead of the attackers having to associate a new physical SIM they'll just associate a new set of credentials.
By the way, CDR processing (aka parsing CSV files and figuring out how much to charge - rocket science I know) is also routinely outsourced to the lowest bidders with no doubt terrible security practices: https://berthub.eu/articles/posts/5g-elephant-in-the-room/
Anyway, it's not only social engineering but even if it was it simply means that it's useless for security.
Just yesterday, a friend of mine got a fringe hacking incident or a bug. We are not still sure if it was hack but somehow the SIM card in her phone identified as another number from another carrier. Who knows what happened, her SIM wasn't swapped it simply think that it's another number as she found out when started receiving notifications about her new number. Maybe it was Apple's bug or something but who cares, the physical SIM did not change anything.
They did - see EMV payment cards for example.
> it simply means that it's useless for security.
It's not - SIMs close one attack vector where credentials can't be stolen by malware/bruteforced. Current SIM-swap attacks don't scale well; imagine how worse the problem would be if any Android malware could silently take over your number even after you've wiped the device clean.
The solution is to close the social-engineering attack vector by making carriers liable for any losses, not to remove a different layer of security because it's currently being bypassed by a different flaw.
> Who knows what happened
I doubt it was nefarious, I'll place my bets on misconfiguration somewhere. The telephone network is a massive mess and it could very well be that some carrier/equipment in the path rewrote the caller ID as something else.
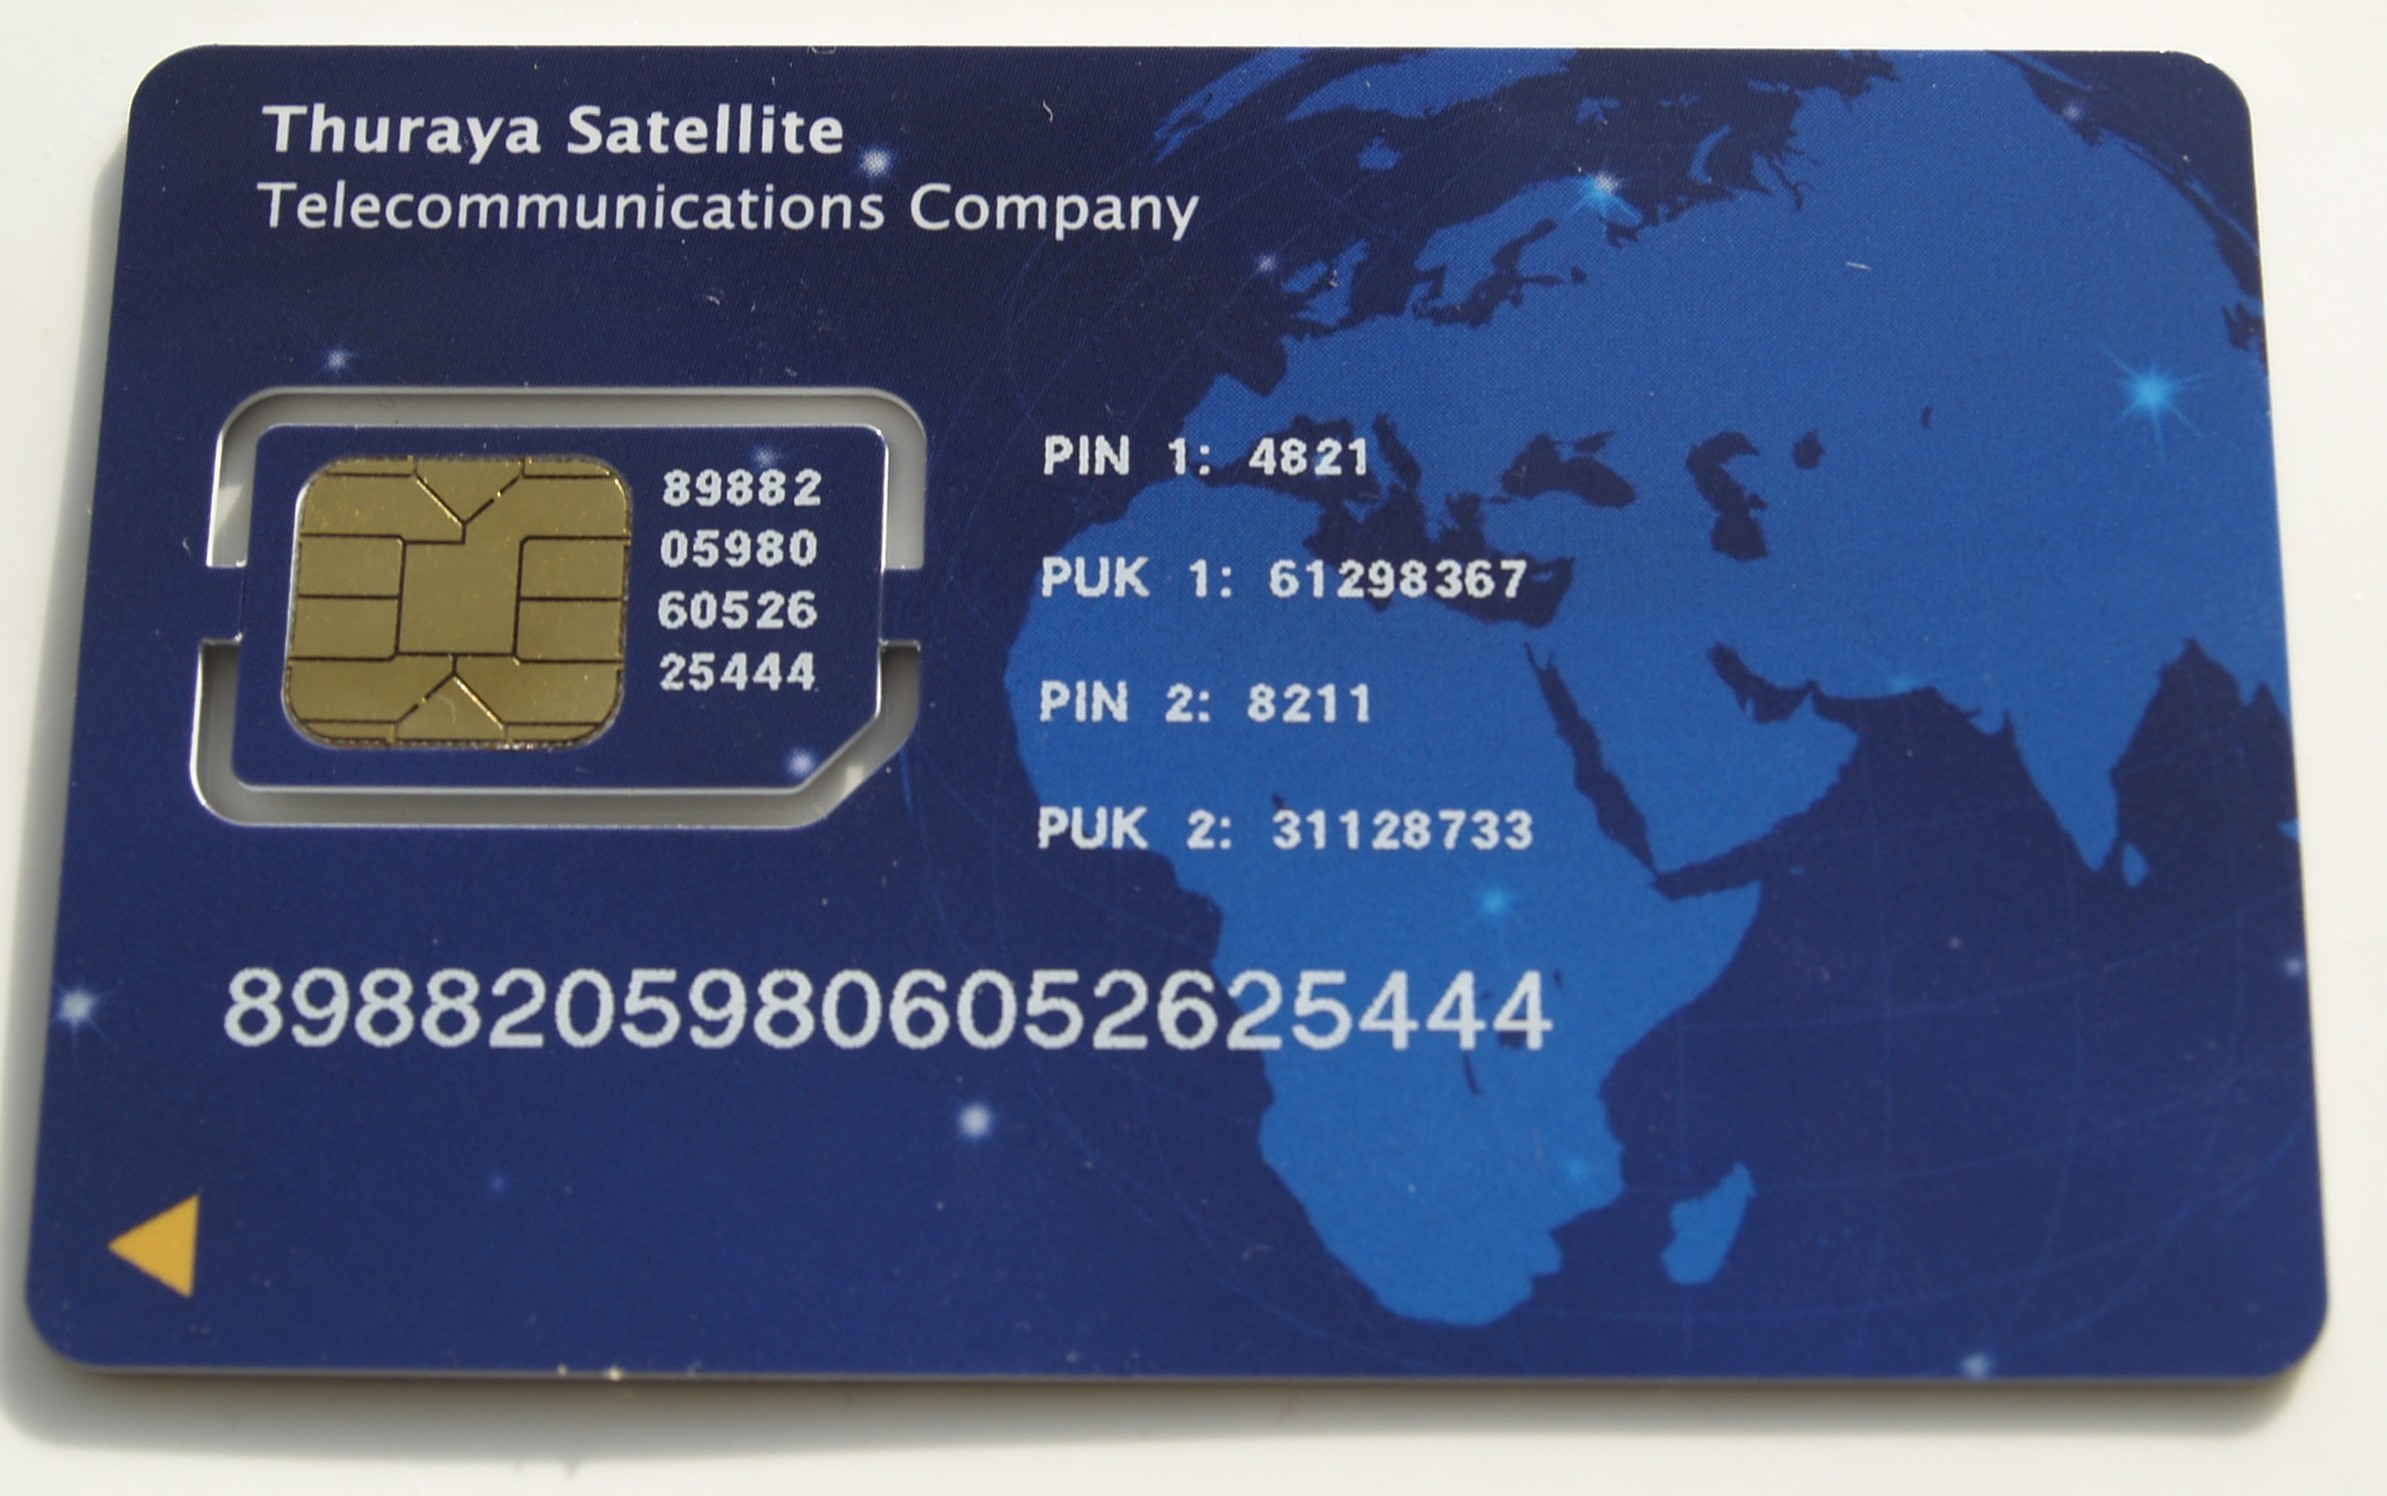
To drive the point home - this is a SIM card: https://upload.wikimedia.org/wikipedia/commons/5/55/Thuraya_... (although you can remove the mini-sim in this revision, originally they were exactly like modern EMV cards).
Again, if you're skeptical of the government itself and allowing them to tap your communication lines, then I understand your hesitation here (although 2FA won't protect you against warrants), but outside of that it's actually simple incompetence of the carriers - SIM swap fraud attacks are common in North America but surprisingly fewer outside despite having the exact porting capabilities, probably because there's a waiting period (usually 48 hours) enforced where the current holder of the SIM card gets warnings about the impeding deactivation in other countries. Annoying if you lost your SIM card, sure, but is much better than having an unauthorised person getting a shiny new SIM card without warning.
Not sure what's going on in other countries, but back when I was a phone store monkey in the UK this was not the case. A SIM swap could be done immediately and the previous SIM doesn't get any notification. If I remember right we needed to check ID, but we had no way nor proper training to tell a potential fake ID, nor what counts as an acceptable ID (the UK doesn't have mandatory ID cards, so a lot of people don't have ID) - I would defer to my manager in this case but I'm pretty sure the whole process was really at their discretion and whether the whole thing "feels" legit. Making it look like we'd get a sale is an easy way to sway the odds in your favour (we'd need to access the account anyway to make the sale, so you can play along and buy a new plan, and once we pulled up the account you can mention "oh BTW I need a new SIM" and we would oblige).
Fun fact: to access someone's account in-store we had to either text them a code and enter it in the web UI (good!) or provide knowledge-based answers such as amount of last bill, some digits of the ID/driver's license number or a security question answer. There was bruteforce protection, but here's the fun part - it was presumably implemented on the frontend only because you could reload the page on the last attempt and reset the counter of attempts! There were no consequences that I know of (neither from the company nor a notification/follow-up with the customer) to locking out an account either.
At least part of the system was Java-based (it blew up occasionally displaying a full stack trace full of PII) and was available over the Internet (there was a site-to-site VPN for the store, but the URL nevertheless loaded on a standard internet connection when I tried it probably due to misconfiguration, so it's very likely all of that was exposed during the Apache Struts or Log4J vulnerabilities).
I think the reason SIM Swap fraud isn't as common in the UK is either because getting the money out is more difficult or because other scams (authorized push payment fraud, scammers pretending to be tech support or tax authorities, etc) are just more profitable.
Back when I had to use AllScripts EHR software, if I messed up my password three times, I'd just restart the client application. Bam, three more attempts, no need to wait ten minutes.
(I don't know if this is still the case, but I sure hope it's not.)
Sure are a lot of rugged individuals who can do it all (they claim) yet seem to not notice they hardly accomplish any more than anyone else without the help.
I’m skeptical of other humans period. You’re regurgitating the most reinforced rhetoric in your experience. You’re decoupled from the actual work implementing solutions to these problems, and the ease at which theft and fraud occur without technology.
There’s no such thing as a 100% secure system. Physics doesn’t allow it. Accept it. Lean into your biology to self soothe.
I may mistrust the government but like everything else it’s just people, not a black box.
Come on internet geniuses; open source and hardware are right there for you to make this happen. Get funding. Prove you can do better. Show you’re more than syntactic and semantic drivel.
The collective of people making your phone work are incompetent, says the person whose probably never tried. What a joke.
Why not? This is a useful behavior that is currently emulated by forwarding calls to laptops and tablets with the same account when the devices are on the same Wi-Fi. You could get rid of the Wi-Fi requirement if those devices all simply had an eSIM with the same number.
Phones & SIMs don't even know nor care about their own number. The SIM has a field for that but in fact it's often left empty (iOS devices discover their own number by texting a known Apple number and getting the response via the Internet, they'll then populate this field out of courtesy but it's not necessary for functionality).
When a call comes in, the carrier decides which SIM it should be routed to. When a SIM makes an outbound call, the carrier decides which number to set as caller ID.
The functionality you speak of has nothing to do with SIM vs eSIM, it's about carriers having to actually innovate and do some engineering. Their current oligopoly means there's no commercial pressure for them to do so, and there's no reason why they would suddenly do this with the switch to eSIMs.
TIL! Is that why in some countries and some SIM cards my iPhone can automatically report its own phone number (when I look at my own profile under 'Contacts') and in some countries it doesn't do that?
Carriers who assign numbers to SIMs in advance could set that field directly. Others, either because they don't assign a number at the time of the SIM manufacture/personalization or just because they can't be bothered as it's not functionally necessary will leave it blank - in that case from my experience iPhones will populate the field with the number they get back from the iMessage & FaceTime provisioning step but again that's not actually necessary for functionality. The field is also user-editable in Settings -> Phone if you wish.
The sim is nothing more than an auth token which can easily be duplicated.
Your SIM provider certainly can issue a duplicate. Also, SIMs can be spoofed.
Fraudulent SIM swaps are attacking a different layer of the system, they are social-engineering underpaid idiots to associate a new SIM with a given account & number.
You could in theory social-engineer a bank to reissue someone's payment card and somehow intercept it in the post or steal it from their mailbox. That doesn't mean chip & PIN is insecure.
I was a phone store monkey in the UK a few years back and a dedicated attacker can absolutely bypass this: https://news.ycombinator.com/item?id=29714400
I can only assume it's not more common because other scams are more profitable and/or not enough targets (banks, etc) use SMS 2FA as their only method of authentication so a SIM swap wouldn't give you much.
In the Before Times: handy for travel. Having a (e)SIM for your personal number (but perhaps disable data), and when you arrive at your destination just pop in a new physical SIM for local data (and calling).
> We don't have SIMs for ADSL or Fiber internet?
I wish we did. At least for ADSL you can use PPPoE to login into a network with whatever hardware you wish to use instead of the telco's often janky, underpowered stuff. With fibre (GPON) they often lock in the MAC of the optic, so good luck using something else besides whatever is provided. If you're lucky you can remove the SFP module and put it into whatever you want.
This may not be useful for 99% of the population, but given this is HN we're on, I think a lot of folks can appreciate being 'hardware agnostic'.
Otherwise we're back to the 1960s when only Officially Approved™ equipment can be connected:
In Canada, Bell had their "Home Hub 3000" and plenty of folks took out the optic and put it in their own hardware; this possibility was 'discontinued' with the Home Hub 4000, which no longer has a removable optic. There is nothing inherent on the ONT that limits connectivity except the arbitrary telco design choices.
Fiber is actually quite complex. Most residential fiber going in today is GPON, and those systems are authenticated by the ONT, which is somewhat analogous to a hardwired SIM. Theoretically, you could reverse engineer the ONT and create your own, but you can expect to get your account closed if they catch you.
Then you have companies like AT&T who also force you to use their godawful routers and actively work to close off methods that allow using your own router.
And if you have metro-E, chances are the ISP provides their own media converter. Doesn't matter that they charge a $12k install fee and $1200/mo (for 500/500 - actual Comcast bill in Nashville, TN), they still won't hand you an SFP+ module.
The reason for it is because they are physically provided to your house so it would be redundant, but if that wasn't a case, imagine if we did have SIM for ADSL or Fiber. Getting access to your Internet service wherever you go without extra charges.
> We don't have SIMs for Reddit ot Twitter? > Why would we have SIMs accessing GSM networks? There's no fundamental reason why we simply don't sign in into these networks like signing in to HN.
We have login and password, which are like SIM, but you can memorize them.
Imagine if your access to Reddit, Twitter, HN was tied to your computer, because that's essentially what you're advocating for.
You have missed the point. OP is talking about how ridiculous having a physical bit of plastic to log in to the cell towers is. The physical sim provides next to no value.
And it comes at a heavy cost in space inside the phone as well as annoyance waiting for a new sim to ship in the mail. While esim providers email you a QR code and you are good to go immediately.
We don't have SIMs for ADSL or Fiber internet? We don't have SIMs for Reddit ot Twitter? Why would we have SIMs accessing GSM networks? There's no fundamental reason why we simply don't sign in into these networks like signing in to HN.
Surely, it adds a layer of anonymity and freedom where you simply use the system by paying it however there's an ongoing trend all over the world of de-anonymisation. In many places they are asking for ID and other documents in order to provide you with a SIM.
Physical SIM now means, it's yet another obsolete tech that costs money and takes space inside the devices only to sustain anonymity that is no longer desired.
SIM is just another causality on the way towards the tightly controlled world.
IMHO, it needs to happen at some point but we also need to rethink our rights in a world that is run by these huge networks.
Wouldn't be nice if our phones could have simply scanned for the networks, receive the offers from the available networks, pay and start using it?