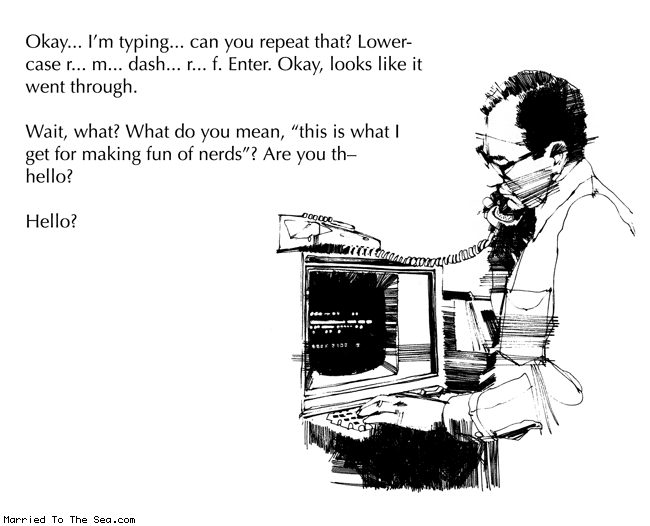
A non-root user (hopefully) can't root the system or rm -rf /root.
But everything interesting is stored in that user's home folder with implicit RW permissions anyway.
On Android apps just request everything. I imagine (without explicit knowledge) that an app given permissions could rewrite, erase, or pull down over the network contacts / photos / etc in the background.
Yet I was confused, because as a user all I cared about was my stuff that was ... right there in a non root account.
As you say all the stuff I was concerned about was right there, but nobody talked about how important that was.
On my Linux systems, particularly under Debian, there's some assurance provided through the Debian Project, its guiding documents (social contract, constitution, policy), and debian developers. The project explicitly serves the users. This doesn't prevent bugs and occasional malice, but tends to tremendously reduce incentives for it.
Smartphones ... are a mess, and Android rather particularly so. I've suggested entirely rethinking how app development is performed, particularly for basic utilities, closer to the Debian model. I have little hope of this occurring.
That was true up to Marshmallow (Android 6), when finer grained permissions were added.
> On Android apps just request everything
Well, this is as true as with any other operating system, isn't it?
Nowadays, I try to use F-droid as much as I can, applications there ask for reasonable permissions, and are open source, which makes it easier to trust them.
And it looks like it's been ported to Android and iOS. But it's not default, I guess.
But neither is AppArmor in Linux. So why haven't we heard about apps stealing stuff from /home/user/? Is it just that distros do a better job of policing their repos? Or that the userbase is too small to attract malicious app developers?
I don’t think this will do much besides blow away the root user's home directory, which probably doesn't have much in it anyway. But I get what you mean.
http://www.marriedtothesea.com/041808/this-is-what-i-get.gif
On German consumer shops, most "deal of the day" are still a mix of 4.4 and 5.1.
Not true on Android. Apps can be installed from third party sources, without having to root the phone.
Aside from making the permissions system even _more_ fine-grained, I don't know how you'd make the situation much better than it already is.
This isn't how many users use apps. For them any of these prompts are getting in the way of using the app, so they tap the button that would let them use the app quicker, without reading what the message said.
I'd say open source apps are more trustworthy that Google or Apple.
I've installed plenty of OSS apps but I've never built them myself and while I've looked at the source code, I have no way of knowing if what was in the repository was what got delivered.
You're right; I don't usually vet apps past the simple "is it FLO?" check (although I will do this before accepting a suspicious permission). However, I do keep a copy of the source of most of the apps I use. As a result, if it were to come out that the app is doing something shady, I could remove that part and keep enjoying the functionality of the app, whereas with a proprietary app I'd be SoL.
I also know that the developers know this, so they have an incentive not to do that stuff if they don't want a competing fork to take off. That is the main reason why I trust FLO apps more.
But the second one is, if there really is something off, there's an unambiguous proof of it - you can point directly at the implementation! And with luck, even at the particular person or organization responsible.
You can’t be sure of that at all. This isn’t just an epistemological point either - people are still routinely finding vulnerabilities in the most widely used open source software that were introduced two decades ago. This is despite extremely lucrative incentives for finding them. In many cases it’s because no one bothered to look; in other cases it’s because the numerous (ostensibly qualified) people who looked weren’t capable of finding them.
Open source software is a red herring for security. Its benefits are vastly overstated. You gain an incremental improvement in the theoretical ease of review, but this almost always comes at the cost of the overseeing organization having fewer resources to devote to security because its more difficult and uncommon to monetize open source software.
Overall I’d say open source software is at best weakly correlated with improved security posture. As it turns out most people don’t inspect their code before running it, and this includes those who fully buy into the many eyes aphorism. Of those who do inspect it, approximately all of them are woefully incapable of identifying real vulnerabilities beyond all but the lowest hanging fruit. Those who remain are typically extremely well paid for their expertise and will only look at software which features a sizable bounty.
Unfortunately most open source software, including widely used open source software, does not have a bug bounty and isn’t on e.g. Google Project Zero’s radar.
I and sure many others do look at the code, even for languages that I don't know. I often end up removing functionality that I don't need (less unnecessary code often means less security vulnerabilities) or patch it slightly to suit my needs better. For proprietary code I don't have that luxury, the other issue is that a lot of free-ware software tracks you and won't give you any opt-out options.
It's not weakly correlated if let's say I can remove finger protocol and get direct security benefits. Things like that make outdated proprietary binaries unusable from security perspective.
> approximately all of them are woefully incapable of identifying real vulnerabilities beyond all but the lowest hanging fruit.
Sure, but more often that not it is those that will get exploited and open source makes it damn easy to fix. Bug bounty shouldn't be the only incentive to make the software more secure.
But even with that, it's taken years to find some serious bugs.
However, when trusted apps are installed, they often demand all sorts of privileged access. And if they're malicious, there's no way to protect against them. Except that they get reported to Google/Apple and become unavailable. But that doesn't help people who already got pwned.
What am I missing?