http://www.ftdichip.com/Drivers/FTDriverLicenceTerms.htm
"Use of the Software as a driver for, or installation of the Software onto, a component that is not a Genuine FTDI Component, including without limitation counterfeit components, MAY IRRETRIEVABLY DAMAGE THAT COMPONENT."
May cause more problems than it fixes.
Of course if they have deliberately broken people's hardware that is a different matter, that clause in the license does not give them permission to in any way (either by my reading of the wording, or my understanding of how the law usually works in such cases).
Of course they should roll back the drive and investigate, but what if the problem is due to a new feature that can't be implemented some other way, and there is no way to detect a "genuine" chip? Should users of their chips do without a feature (or have to mess around opting in) because some other manufacturer's chip has a problem with it?
The only law broken by the counterfeiters is trademark violation for printing the FTDI logo on their chips. That's it! Everything else they did was legal. Otherwise, Intel and AMD would be bricking CPUs right now.
Reverse engineering is legal. Emulation is legal. Creating hardware that's compatible with another vendor's software is legal. Flashing your hardware with another vendors firmware is legal. Modifying hardware you purchased from a vendor is legal. Modifying software you purchased from a vendor is legal.
etc... etc...
Does anyone even know what entity designed and made the fake FTDI chip?
I find many people don't seem to understand what making compatible chip means. It's very common to have legitimate, drop in replacement for popular ICs. But this fake FTDI chip is certainly not the case here.
:-)
It doesn't matter if it's trademarkable. The entire purpose of VIDs is to distinguish between different vendors' devices. If I'm allocated a VID it's not my responsibility to ensure my drivers interoperate with other vendors' products.
How many products using counterfeit FTDI chips don't advertise USB compliance?
There are legal routes available to FTDI that don't involve bricking devices. I'm guessing that FTDI didn't talk to internal counsel before making this change.
I'll be quite surprised if Microsoft doesn't pull this patch.
marcan: "In case anyone was still wondering if this is intentional and malicious... Straight out of their driver. Function/variable naming and comments mine.
https://marcan.st/transf/ftdi_evil.png
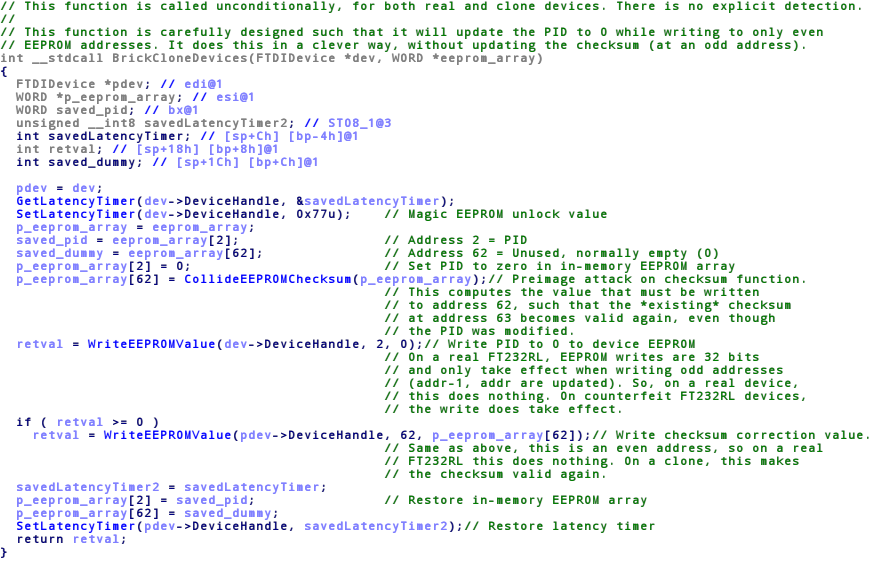
I figured out what's going on with the real chips: turns out their EEPROM is written in 32bit units. Writing to even addresses is ignored; the value is buffered and the address discarded. Writing to odd addresses writes the entire 32bits, using whatever value was last buffered for the other half. So both the PID write and the checksum write are ignored on real FTDI chips, as they are both written to even addresses. I still don't know why it works on clone chips though, since the checksum is written to the wrong place (it should normally be on an odd address); presumably they don't check it."
Basically driver is fuzzing 'chips claiming to be FTDI' with illegal instructions. Want to play clone games? better emulate me completely, otherwise tough titties. I like it. Might not work to well for FTDI in the end due to PR nightmare, but from engineering standpoint its quite brilliant.
Without access to the source code or a well-reversed disassembly of the FTDI driver, and a good grasp of the logic used in the counterfeit chip, one cannot be certain about this. And surely not to the extent of urging Microsoft to revoke driver signatures.