Zerodium used to offer up to 300k in 2021 https://www.securityweek.com/sites/default/files/images/Zero...
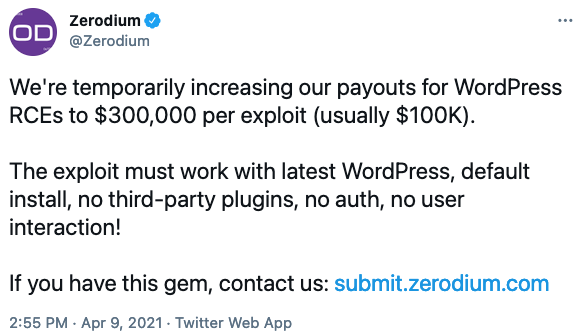
These brokers usually don't pay the bulk sum - they sell access to nation actors and you get payed out over time as long as the bug is not patched to discourage reselling and burning it. I doubt anyone would confirm if they got the full payment or not for something similar.
Why post these random unsubstantiated claims on HN?
To show everyone the Gell-Mann amnesia effect in action.
When HN top karma poster and security professional posts something like this, doubles down, and can’t even be bothered to support it in any way (I’m open to learning and changing my opinion) it completely blurs the line going into social media influencer. Quantity over quality.
Just because they're exclusive about their clients doesn't mean they're not real. Their impact and effectiveness is a separate topic though. I don't think they're still actively operating or taking new clients, at least.
btw: "Oh, so you've done x?" What a snarky and confrontational way to ask someone something. Especially when it's asserting a well documented company and person is "not real".
But that’s besides the point. You straight up argued that one isn’t real in the most asinine way you could.
Even if you were right that would be ridiculous. The fact that you’re wrong and have multiple people telling you you are makes it even worse.
I’ve seen you replying in snide comments whenever someone disagrees with you before. Your status as…whatever you are doesn’t give you carte to treat randoms like they’re beneath you.
This is how all of these sites work. You would not get 500k for every exploit obviously. You would get that (or more) for great exploits.
I’m noticing you haven’t addressed anything I mentioned at all. Is that just acceptance that it’s the truth or are you just having a bad day?
Edit: Actually, let me add that for a 0click exploit on mobile devices that leads to root level permissions you’re very likely sitting on millions of dollars.
https://securitycryptographywhatever.com/2024/06/24/mdowd/
It sounds like you're telling me you believe you might get six figures for a "great" WordPress core RCE. I believe that's false, and I believe that for reasons that probably indicate our premises are much too far apart to hash this out here.
I have open contempt for online price list "brokers" like Zerodium. I do not have contempt for other commenters here. I think it's important that you understand the distinction before coming at me the way you've been in this thread. Disagreeing with me, rebutting or refuting me, sharply or ungenerously: totally fine. Your weird psychoanalysis of me: not fine.
> Did you get mid-high 5 figures for a serverside vulnerability? I hear the Russians are paying $300k for Postfix! But the UAE might pay $400k through Crowdfense. These numbers are definitely real. How could they not be? They're right there on a web page.<
> Oh, you've done business with them then? Know someone who has?<
You’re replies have been snide and rude and you trying to pivot and say “you were merely talking about the brokers” is further showing you don’t care and feel entitled to continue.
Other users are calling you out on this behavior here and on other threads as well to the point that the comment you made starting this has stayed flagged.
Deflecting from someone calling out this consistent behavior is frankly ridiculous in the face of the receipts, especially trying to villainize the people calling you out for it.
Also, not even the main point anymore, but you’ve intentionally mischaracterized every argument others have put forwards including in your most recent response. I was extremely explicit about what kind of exploit commands a high price and you’ve chosen to again twist the argument to your desired conclusion:
> It sounds like you're telling me you believe you might get six figures for a "great" WordPress core RCE<
My “psychoanalysis” was an attempt at giving you grace but you seem intent on proving that talking down to others and then trying to sidestep justified criticism are default behaviors that you’re entitled to.
I’m just baffled.
bink is correct. The people who buy exploits are governments. There is very little interest in Wordpress or indeed any target that isn't a browser or a mobile. Browsers and mobiles are the only things that are perennially useful to an intelligence agency. Those two are reliable access vectors for the vast majority of things that interest government organisations.
ex: Target hits website -> site delivers RCE for some software that is on the target's system
I'd disagree here. Still 41% of all sites use Wordpress [1]... and that means a lot of targets, and a lot of ways to target them. Your good ole' deface/ransomware extortion scheme, leaking data supposed to be confidential (such as account lists), trusted spreaders for exploits, or the latest hit, bets on "prediction markets" that have some Wordpress site set as oracle. People are willing to screw around with airport weather stations to manipulate bets [2], it's not that much of a stretch to assume such incentives would also apply for website hackers.
[1] https://www.wpzoom.com/blog/wordpress-statistics/
[2] https://edition.cnn.com/2026/04/23/europe/france-weather-sen...
You also don't need an RCE for 99% of that.
This is just 100% an incorrect assumption. Even just an e-commerce site running Woo has troves of potentially valuable customer data. Not to mention whatever else might be on the server, or what that server is connected to...
I would hope not, but I’d be surprised if that were true across the millions(?) of Wordpress sites?
not big surprise
So never modified at all, even if plainly contradictory and/or ethically and morally compromised?
It had last been booted on it, complete with working hard drive an; MacOS X 10.3. So $1.299 -> $0.
Closest you're going to get is something like those kids in florida who just got wrapped for putting malware into steam games and draining peoples accounts. They were going to get caught anyways but it would have taken a lot longer to build a case against them if they weren't flaunting it on socials
Given that the article says that prompts are modified like they are holy scripture, perhaps sell the prompt for $500k.
The author works for https://www.assetnote.io/ , which has AI products for automated scanning.