News for hackers. Stuff that matters.
Re:Underground Hansa Market taken over and shut down by captainmuon on Thursday July 20, 2017 @12:39PM (#14814024)
I would love to know how they got caught. There is probably something to learn about opsec from this.

The paranoid side of me says Tor is unsafe (due to whatever - the authorities having backdoors on most hosting services, on your PC, due to the encryption being cracked by some unknown breakthrough or due to 90% of entry nodes being controlled by NSA). And NSA and FBI and co just have hundreds of people working on "parallel construction" of evidence.

Of course, a blunder by the operators is much more likely...

Re:Underground Hansa Market taken over and shut down by nfbush on Thursday July 20, 2017 @01:04PM (#14814296)
Every time a market has been taken down it's been due to OPSEC failure and other information leaks (e.g. Silk Road captcha IP leak, DPR's advertising of market being linked to his personal email address). AlphaBay Which got taken down first in this operation was due to a personal email being included in the header of the welcome email sent out to new users 3 years ago [1]

[1] https://www.justice.gov/opa/press-release/file/982821/downlo... (pdf)

Re:Underground Hansa Market taken over and shut down by Analemma_ on Thursday July 20, 2017 @02:57PM (#14815304)
> Every time a market has been taken down it's been due to OPSEC failure and other information leaks (

This is true, but it dangerously misses the point. Every time someone gets taken down, the know-it-alls on various fora sneer and go "Ha! What terrible opsec! I wouldn't have made that mistake!" No, you would've made some other mistake.

To run a darknet market and not get caught, your opsec has to be perfect. Every second, every minute, every day, every person involved, forever. That is simply not possible once an operation exceeds a certain size. Like the IRA once said: "We only need to be lucky once. You need to be lucky every time". This is the "defender's dilemma" that guarantees you will be caught as t goes to infinity: sooner or later, you'll make some mistake that burns you.

Focusing on the specific mistakes made by bust-ees only boosts your confidence and ignores that you, in their situation, would've leaked information somewhere else.

Re:Underground Hansa Market taken over and shut down by nissimk on Thursday July 20, 2017 @04:52PM (#14816191)
I'm sorry to nitpick and I mostly agree with you, but similar to a casino game that favors the house, if you are lucky and quit while you're ahead, you can avoid capture. Your statement is only true in the long run. Of course criminals usually become addicted to their risky behaviors just like gamblers... It's a frequent trope in crime movies: one last job before the criminal retires, but that last job is the one where he makes a key mistake.
Re:Underground Hansa Market taken over and shut down by armitron on Friday July 21, 2017 @11:44AM (#14821406)
This is a very superficial way to look at things, and ultimately, entirely wrong.

One of the cornerstones of OPSEC is persona creation & management. This is orders of magnitude easier to perform in cyberspace than in real life, and can be used as a catch-all safety -- for exactly when mistakes are made and layers are compromised --.

You will make many many mistakes, but part of a well-implemented OPSEC strategy, is to have those mistakes land in a compartment, an illusionary persona that you created out of thin air. Operation size has nothing to do with it and should be completely irrelevant when the compartmentation strategy used is solid.

Re:Underground Hansa Market taken over and shut down by maratd on Thursday July 20, 2017 @04:55PM (#14816215)
> That is simply not possible once an operation exceeds a certain size.

A good argument for not getting too greedy and keeping things small. It's the nail that sticks out that gets hammered down.

Re:Underground Hansa Market taken over and shut down by rothbardrand on Thursday July 20, 2017 @07:33PM (#14817064)
These opsec failures that you're talking about are very easy to find in the process of parallel construction.

So that these are the stated reasons is no indication that they are the real reasons.

They are, in fact, so very, very convenient the they smell like parallel construction to me.

Might not be, but they certainly aren't good evidence that parallel construction isn't going on.

Re:Underground Hansa Market taken over and shut down by krapp on Thursday July 20, 2017 @08:24PM (#14817265)
>Might not be, but they certainly aren't good evidence that parallel construction isn't going on.

On the other hand, the evidence that parallel construction is going on appears to be a belief that everything is parallel construction.

Re:Underground Hansa Market taken over and shut down by bripeace on Thursday July 20, 2017 @02:45PM (#14815224)
But where did they get the 3 year old email.

1) They were investigating AlphaBay for nearly 3 years 2) They came upon somehow control of an email address which contained 3 year old mail that contained the password reset email 3) They are capturing and storing large amounts of tor traffic much like the NSA does on clearnet see: xkeyscore

This isn't really explained in the indictment

Re:Underground Hansa Market taken over and shut down by jdenning on Thursday July 20, 2017 @06:28PM (#14816807)
Apparently, he leaked the email address in an early email sent to site users. It contained his real first name and birth year, and he used the address on several other sites.

When he was busted he was logged in to the site, and had several passwords/keys stored in plaintext on his machine.

Multiple OpSec failures.

Good analysis here: https://medium.com/@thegrugq/dark-net-trap-545ae5dd8476

Re:Underground Hansa Market taken over and shut down by fiatpandas on Thursday July 20, 2017 @04:57PM (#14816234)
They could have gained knowledge of the email address through classified means, and made up the email header story to hide their method of initially obtaining it.
Re:Underground Hansa Market taken over and shut down by burger_moon on Thursday July 20, 2017 @04:09PM (#14815838)
This is a really interesting question. Knowing how they got access to such an old email from an external source.
Re:Underground Hansa Market taken over and shut down by problems on Thursday July 20, 2017 @04:57PM (#14816226)
Honestly it doesn't seem that interesting - browsing /r/DarkNetMarkets, dnstats and just signing up yourself is enough. I've signed up for a few for shits and giggles but never bought anything, browsing is pretty interesting. You just need to find one person like me who'd be willing to give them the email... not exactly hard.
Re:Underground Hansa Market taken over and shut down by CM30 on Thursday July 20, 2017 @06:11PM (#14816722)
Perhaps it's from someone they were investigating for other crimes. I mean, it doesn't seem beyond the realm of possibility that law enforcement were going after say, a drug dealer who was using the site to sell goods, and found the welcome email from the platform he or she was using in their inbox.

That seems like one plausible possibility.

Re:Underground Hansa Market taken over and shut down by ATsch on Thursday July 20, 2017 @07:25PM (#14817032)
This is my pet theory. A seller was busted and the emails were siezed. Seems like the most likely possibility.
Re:Underground Hansa Market taken over and shut down by xorcist on Thursday July 20, 2017 @06:45PM (#14816873)
Isn't it likely that a number of recipients did not delete that particular message? Also that a number of them sold drugs by mail order, not uncommonly a short lived profession?
Re:Underground Hansa Market taken over and shut down by math0ne on Thursday July 20, 2017 @08:58PM (#14817374)
I'm sure they sign up for every darknet site constantly.
Re:Underground Hansa Market taken over and shut down by danek on Thursday July 20, 2017 @10:04PM (#14817571)
Does "parallel construction" mean "finding plausible but fake explanations for how we got the evidence so we don't burn our successful and secret investigation techniques"? Just guessing from context...
Re:Underground Hansa Market taken over and shut down by patrickyeon on Thursday July 20, 2017 @11:31PM (#14817852)
That's definitely a cynical way (that I would tend to lean towards agreeing with) to describe it.

The other spin would be "we discovered illegal activity through evidence that would be inadmissible in court, so we went ahead and focussed on gathering admissible evidence". Probably by looking in places they wouldn't have looked otherwise, but not by making anything up or breaking any laws.

Re:Underground Hansa Market taken over and shut down by trobertson on Thursday July 20, 2017 @10:06PM (#14817578)
Yes.
Re:Underground Hansa Market taken over and shut down by TotallyHuman on Thursday July 20, 2017 @01:31PM (#14814586)
Apparentle the Alphabay moron had his real hotmail address in the welcome e-mail they used to send and the same nick on another message board with more personal details as well. Massive OPSEC failure.
Re:Underground Hansa Market taken over and shut down by rothbardrand on Thursday July 20, 2017 @07:34PM (#14817067)
Or parallel construction. Easy to find after the fact.
Re:Underground Hansa Market taken over and shut down by jameskegel on Thursday July 20, 2017 @04:35PM (#14816059)
Please take about 20% off the tone there, it's not going to enhance the discussion.
Re:Underground Hansa Market taken over and shut down by pc86 on Friday July 21, 2017 @09:03AM (#14820125)
I'm sorry but if your business is running an illegal drug market and you're sending out account emails with your real name and year of birth from a non-burner email, I think "moron" is probably a pretty apt description.
Re:Underground Hansa Market taken over and shut down by jetru on Friday July 21, 2017 @12:04AM (#14817985)
hansa was serving plain http. I wonder how much this matters since they use gpg for making orders.
Re:Underground Hansa Market taken over and shut down by hackerboos on Friday July 21, 2017 @08:29AM (#14819835)
All Tor hidden service traffic is encrypted. You don't need SSL but you can use it.

It's hard to find an SSL provider that will sign a .onion domain though.
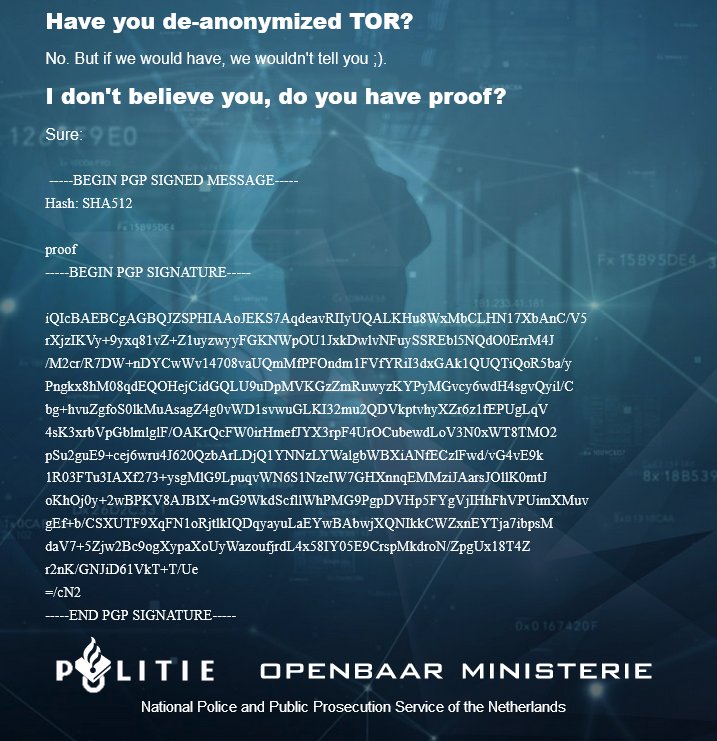
Re:Underground Hansa Market taken over and shut down by nthcolumn on Thursday July 20, 2017 @06:28PM (#14816801)
Dutch police claiming to have de-anonimized Tor: https://pbs.twimg.com/media/DFNMsZOXoAIBdZ2.jpg
Re:Underground Hansa Market taken over and shut down by captainmuon on Friday July 21, 2017 @02:16AM (#14818428)
I always find it incredible when these takedowns occur, how much effort they put into the graphical design. And it doesn't look like a hobby designer among the police did this, but they hired somebody.

Also, considering this is a drug sting, which should be a really serious thing, it's strange that they make a joke on the page.

I would expect a plain HTML page saying "This hidden service hosted illegal activities. All transactions have been logged. If you participated in these activities, contact your local authorities."

Re:Underground Hansa Market taken over and shut down by tripzilch on Saturday July 22, 2017 @07:29PM (#14830031)
http://rijkshuisstijl.nl/ (roughly "government house style / style guide")

We even have bespoke fonts, Rijksoverheid Serif and Rijksoverheid Sans: https://www.rijkshuisstijl.nl/basiselementen/lettertype

This image, however, seems to be a stock photo, the Dutch police logo, and white lettering. Given that it uses no less than four different fonts, I bet it was a quick paste job by someone from the cybercrime unit, not a professional graphic designer.

After some image searching, it turns out to be from a template: https://www.om.nl/publish/pages/51619/screenshot_zonder_brow...

Re:Underground Hansa Market taken over and shut down by ikeboy on Thursday July 20, 2017 @06:36PM (#14816839)
>Dutch police claiming to have de-anonimized Tor

That uh, says the exact opposite of what you say it says

Re:Underground Hansa Market taken over and shut down by nthcolumn on Thursday July 20, 2017 @07:03PM (#14816944)
Ok ;)
Re:Underground Hansa Market taken over and shut down by nthcolumn on Friday July 21, 2017 @10:10AM (#14820648)
fwiw and to spell it out for the hard of understanding they were trolling the users by saying have 'no' but we wouldn't tell you even if we had >WINK< (we did) and then present a PGP signature with 'proof' that they had - the sig is invalid btw and in any case could have been replayed. More recently I read that they allegedly waterholed a child abuse site in order to pwn one of the admins. So although none on Hansa they knew the admin was a disgusting piece of filth (or maybe by sheer luck?) Anyways - good work fellas.