News for hackers. Stuff that matters.
Re:Evidence points to another leaker at the NSA by silvestrov on Monday August 22, 2016 @12:18PM (#12337363)
Even if it's not Russia, the release of the hacking tools gives weight to the argument that nsa/fbi should not be able to demand companies to create a back door in their products.

> Apple: If we're forced to build a tool to hack iPhones, someone will steal it.

> FBI: Nonsense.

> Russia: We just published NSA's hacking tools

https://twitter.com/csoghoian/status/765785340892372992

Re:Evidence points to another leaker at the NSA by fooey on Monday August 22, 2016 @02:03PM (#12338143)
Let's make state sponsored backdoors mainstream, and then build all our of devices in foreign countries. What could go wrong?
Re:Evidence points to another leaker at the NSA by stcredzero on Monday August 22, 2016 @02:57PM (#12338507)
That's the best 2 sentence summary of the politics around technology and security I've seen so far!
Re:Evidence points to another leaker at the NSA by finid on Monday August 22, 2016 @02:58PM (#12338511)
State-sponsored backdoors have been mainstreams for decades. Practically every major piece of software and hardware that's not open source has a backdoor embedded.

Even popular anti-virus programs on Windows have been jimmied to allow state-sponsored malware through

Re:Evidence points to another leaker at the NSA by Analemma_ on Monday August 22, 2016 @03:12PM (#12338638)
> Practically every major piece of software and hardware that's not open source has a backdoor embedded.

[citation needed], and I mean a credible one with evidence, not tinfoil-hat raving.

Yes, we know that three-letter agencies look for, and probably have a stash of, zero-days for covert access. And they also do physical attacks wherever possible (like fiber taps at Google's datacenters). But those are two very different things from backdoors built in with the cooperation of the vendor. And despite how many people on the Internet treat "companies build in gov't backdoors" as just unquestioned fact, I've never actually seen any proof.

Re:Evidence points to another leaker at the NSA by galdosdi on Monday August 22, 2016 @03:16PM (#12338661)
I dunno. Before Snowden, a lot of nasty stuff that we now take for granted the intelligence community does, was seen as "tin foil hat." After Snowden, I no longer doubt the possibility of any realistically imaginable attack, ie, assume that if they have the physical ability to do it, you should assume they do it and are not stopped by any ethical concerns.

Our intelligence apparatus has cried wolf too many times, in terms of denying they do something and then it turns out they do it, to be trusted anymore. They've lost the benefit of the doubt and if they don't want people believing all the tin foil hat things, maybe they should stop doing so many of them.

Re:Evidence points to another leaker at the NSA by Analemma_ on Monday August 22, 2016 @03:26PM (#12338732)
> Before Snowden, a lot of nasty stuff that we now take for granted the intelligence community does, was seen as "tin foil hat."

This is true, but using it as a justification for "And therefore, my theory about what the intelligence community is doing is correct and does not need evidence" is a non sequitur fallacy that has become depressingly common in recent years. You still need evidence for individual allegations.

To show you what I mean, suppose I were to say, "The NSA has a constellation of mind-control satellites built with help from the lizard men!", and then responded to the deserved skepticism with "A lot of things that used to be tinfoil hat theories we now know to be true thanks to Snowden, so this is too!". That's obviously fallacious reasoning, but it's exactly what people are doing when they toss around allegations of backdoors with no proof. Again: there's no shortcut around the need for evidence.

> After Snowden, I no longer doubt the possibility of any realistically imaginable attack ie, assume that if they have the physical ability to do it, you should assume they do it and are not stopped by any ethical concerns.

I agree completely, but that's not what I, or the person I replied to, was talking about. The issue I was addressing in my comment was whether their backdoors are being built with the knowledge and cooperation of the vendors, which is very much unknown. Attacks like taps on cables are orthogonal to what I was saying.

Re:Evidence points to another leaker at the NSA by MawNicker on Monday August 22, 2016 @03:43PM (#12338857)
There's merit in just pondering. This is a message board not a legal proceeding. What you're saying isn't totally orthogonal. I'm often surprised at how terrible modern software is. I suspect they actively subvert and displace popular software that they can't hack. Most hacks are probably generic exploits of library code. I imagine they economized. They wanted Total Information Awareness. I can't prove any of this; It just seems sensible. He's doing a red team analysis. It's not of the same form of thought. You can't invalidate it with the arguments you're making except for in some logical domain or something. It's not a true/false statement. It's not even fuzzy.
Re:Evidence points to another leaker at the NSA by Analemma_ on Monday August 22, 2016 @05:42PM (#12339663)
I agree! And I don't mind pondering, as long as it's clearly marked as such. I do mind statements like "Practically every major piece of software and hardware that's not open source has a backdoor embedded" presented as established fact when they are not.
Re:Evidence points to another leaker at the NSA by MawNicker on Tuesday August 23, 2016 @01:33PM (#12345589)
A vulnerability is a back door. The only problem I have with that statement is it's exclusion of open-source software. It's got more back doors embedded in it than closed-source software.

Jimmy: a short crowbar used by a burglar to force open a window or door.

He didn't necessarily say it was collusion but I suppose it's fair to clarify. It seems narrow to suggest it's just a stash of 0-days. I suspect they've been heavily yet covertly involved in the popular software tool-chains and computing hardware.

Re:Evidence points to another leaker at the NSA by galdosdi on Tuesday August 23, 2016 @04:42PM (#12347431)
Not what I said. I said "realistically imaginable attack" ie ethics is the only thing hypothetically stopping them, not lack of fantasy technology. See if you can come up with a counterexample that actually meets that hurdle.

Mind control satellites and lizard men are both so far away from our current science and technology that even assuming the NSA could be a few years ahead, it's not worth considering. If there really were mind control sattelites or similar precursor technology available or in research today, and there were lizard men who had a history of being good at working with those and willing to sell their skills, then I would agree that it's plausible they're doing it.

Also, I'm more interested in the /practical/ applications of this knowledge of whether the intelligence community does a certain thing X, not the philosophical certainty of whether they do a thing X. You lock your doors because someone /might/ break in /maybe/, not because you're certain John Doe is planning on doing so at 4:30am tonight. Even if no one ever does, it's certainly technically possible, so if locks are cheap it's a reasonable tradeoff, even if you'll never be sure if they really helped.

You're probably right though that I'm moving the goalposts around! :-) I'm not trying to have a formal debate, just idly shooting the shit on the net, so I'm OK with that.

Re:Evidence points to another leaker at the NSA by kobayashi on Monday August 22, 2016 @03:42PM (#12338848)
>assume that if they have the physical ability to do it, you should assume they do it and are not stopped by any ethical concerns.

Prepare for that scenario as a possibility, but there should still be a burden of evidence before possibility is accepted as reality.

Re:Evidence points to another leaker at the NSA by guimarin on Monday August 22, 2016 @03:54PM (#12338944)
Intel Actice Management Technology fits the bill[1]. An out of band processor on select chips. Most likely it's on all the chips and only activated for consumers on the vPro and certain Xeon models.

1. https://en.wikipedia.org/wiki/Intel_Active_Management_Techno...

Re:Evidence points to another leaker at the NSA by Lordarminius on Monday August 22, 2016 @03:41PM (#12338843)
>[citation needed], and I mean a credible one with evidence, not tinfoil-hat raving

I think The Puzzle Palace (https://www.amazon.com/Puzzle-Palace-National-Intelligence-O...) made the same argument as far back as 1982

Re:Evidence points to another leaker at the NSA by Bud on Monday August 22, 2016 @06:15PM (#12339847)
You're aware that The Puzzle Palace was written by the same guy that wrote this article, right? Bamford.
Re:Evidence points to another leaker at the NSA by nickpsecurity on Monday August 22, 2016 @09:38PM (#12340756)
I did something like that in a counterpoint to an apologist for NSA here:

https://www.schneier.com/blog/archives/2014/03/friday_squid_...

Re:Evidence points to another leaker at the NSA by Animats on Monday August 22, 2016 @04:56PM (#12339377)
The number of bad random number generators found in crypto system is deeply suspicious.[1]

[1] http://eprint.iacr.org/2012/064.pdf

Re:Evidence points to another leaker at the NSA by igravious on Monday August 22, 2016 @05:14PM (#12339494)
Yes, but I wouldn't class that as building in a backdoor to a specific "major piece of software and hardware" or software and hardware range, I would class it as industrial sabotage on a more subtle and general scale. Equally pernicious but not the claim that is being made.
Re:Evidence points to another leaker at the NSA by finid on Tuesday August 23, 2016 @06:12PM (#12348196)
If they can have a backdoor in Lotus Notes, what else can't they have a backdoor into?

Do a search for "ibm lotus backdoor" or start from http://www.cypherspace.org/adam/hacks/lotus-nsa-key.html

Re:Evidence points to another leaker at the NSA by nitrogen on Monday August 22, 2016 @03:18PM (#12338678)
Dual EC DRBG.
Re:Evidence points to another leaker at the NSA by Karunamon on Monday August 22, 2016 @03:26PM (#12338730)
The RNG that was only ever used in one (RSA) company's product and then swiftly deprecated once the news dropped?

That's a far cry from "Practically every major piece of software and hardware that's not open source has a backdoor embedded."

Re:Evidence points to another leaker at the NSA by nitrogen on Monday August 22, 2016 @03:47PM (#12338883)
It's a bit disingenuous to call the RSA lib "one company's product" when it was used by many, many other products.
Re:Evidence points to another leaker at the NSA by Karunamon on Monday August 22, 2016 @04:58PM (#12339387)
Is it one company's product or is it not?!

The pedantry around here can be infuriating sometimes. You take issue with my strictly true comment, and ignore Analemma_'s comment upthread (every product) which is strictly false.

Re:Evidence points to another leaker at the NSA by igravious on Monday August 22, 2016 @05:19PM (#12339524)
The clue is in the name. It's a library, it is both the work of one company and used in many products, which is why it is suspected that it was targeted. You're both right. GP is not being pedantic.
Re:Evidence points to another leaker at the NSA by runjake on Monday August 22, 2016 @04:31PM (#12339204)
> like fiber taps at Google's datacenters

Likewise, [citation needed]. That would be pretty stunning, if true.

Re:Evidence points to another leaker at the NSA by FooHentai on Monday August 22, 2016 @04:48PM (#12339319)
This has been known about for ages and was part of the Snowden leaks: https://www.google.com/search?q=google+nsa+%22encryption+add...
Re:Evidence points to another leaker at the NSA by runjake on Tuesday August 23, 2016 @11:02AM (#12344257)
Everything I've read from the Snowden docs indicates traffic is intercepted over big pipes on backbones or at Internet Exchanges.

The parent poster was suggesting (and I was questioning) this occurred at Google Data Centers, which would prove explicit cooperation by Google.

A whole different ballgame.

The closest I've seen are the PRISM slides which imply cooperation from Google and the other big companies, but this could be bad choice of wording.
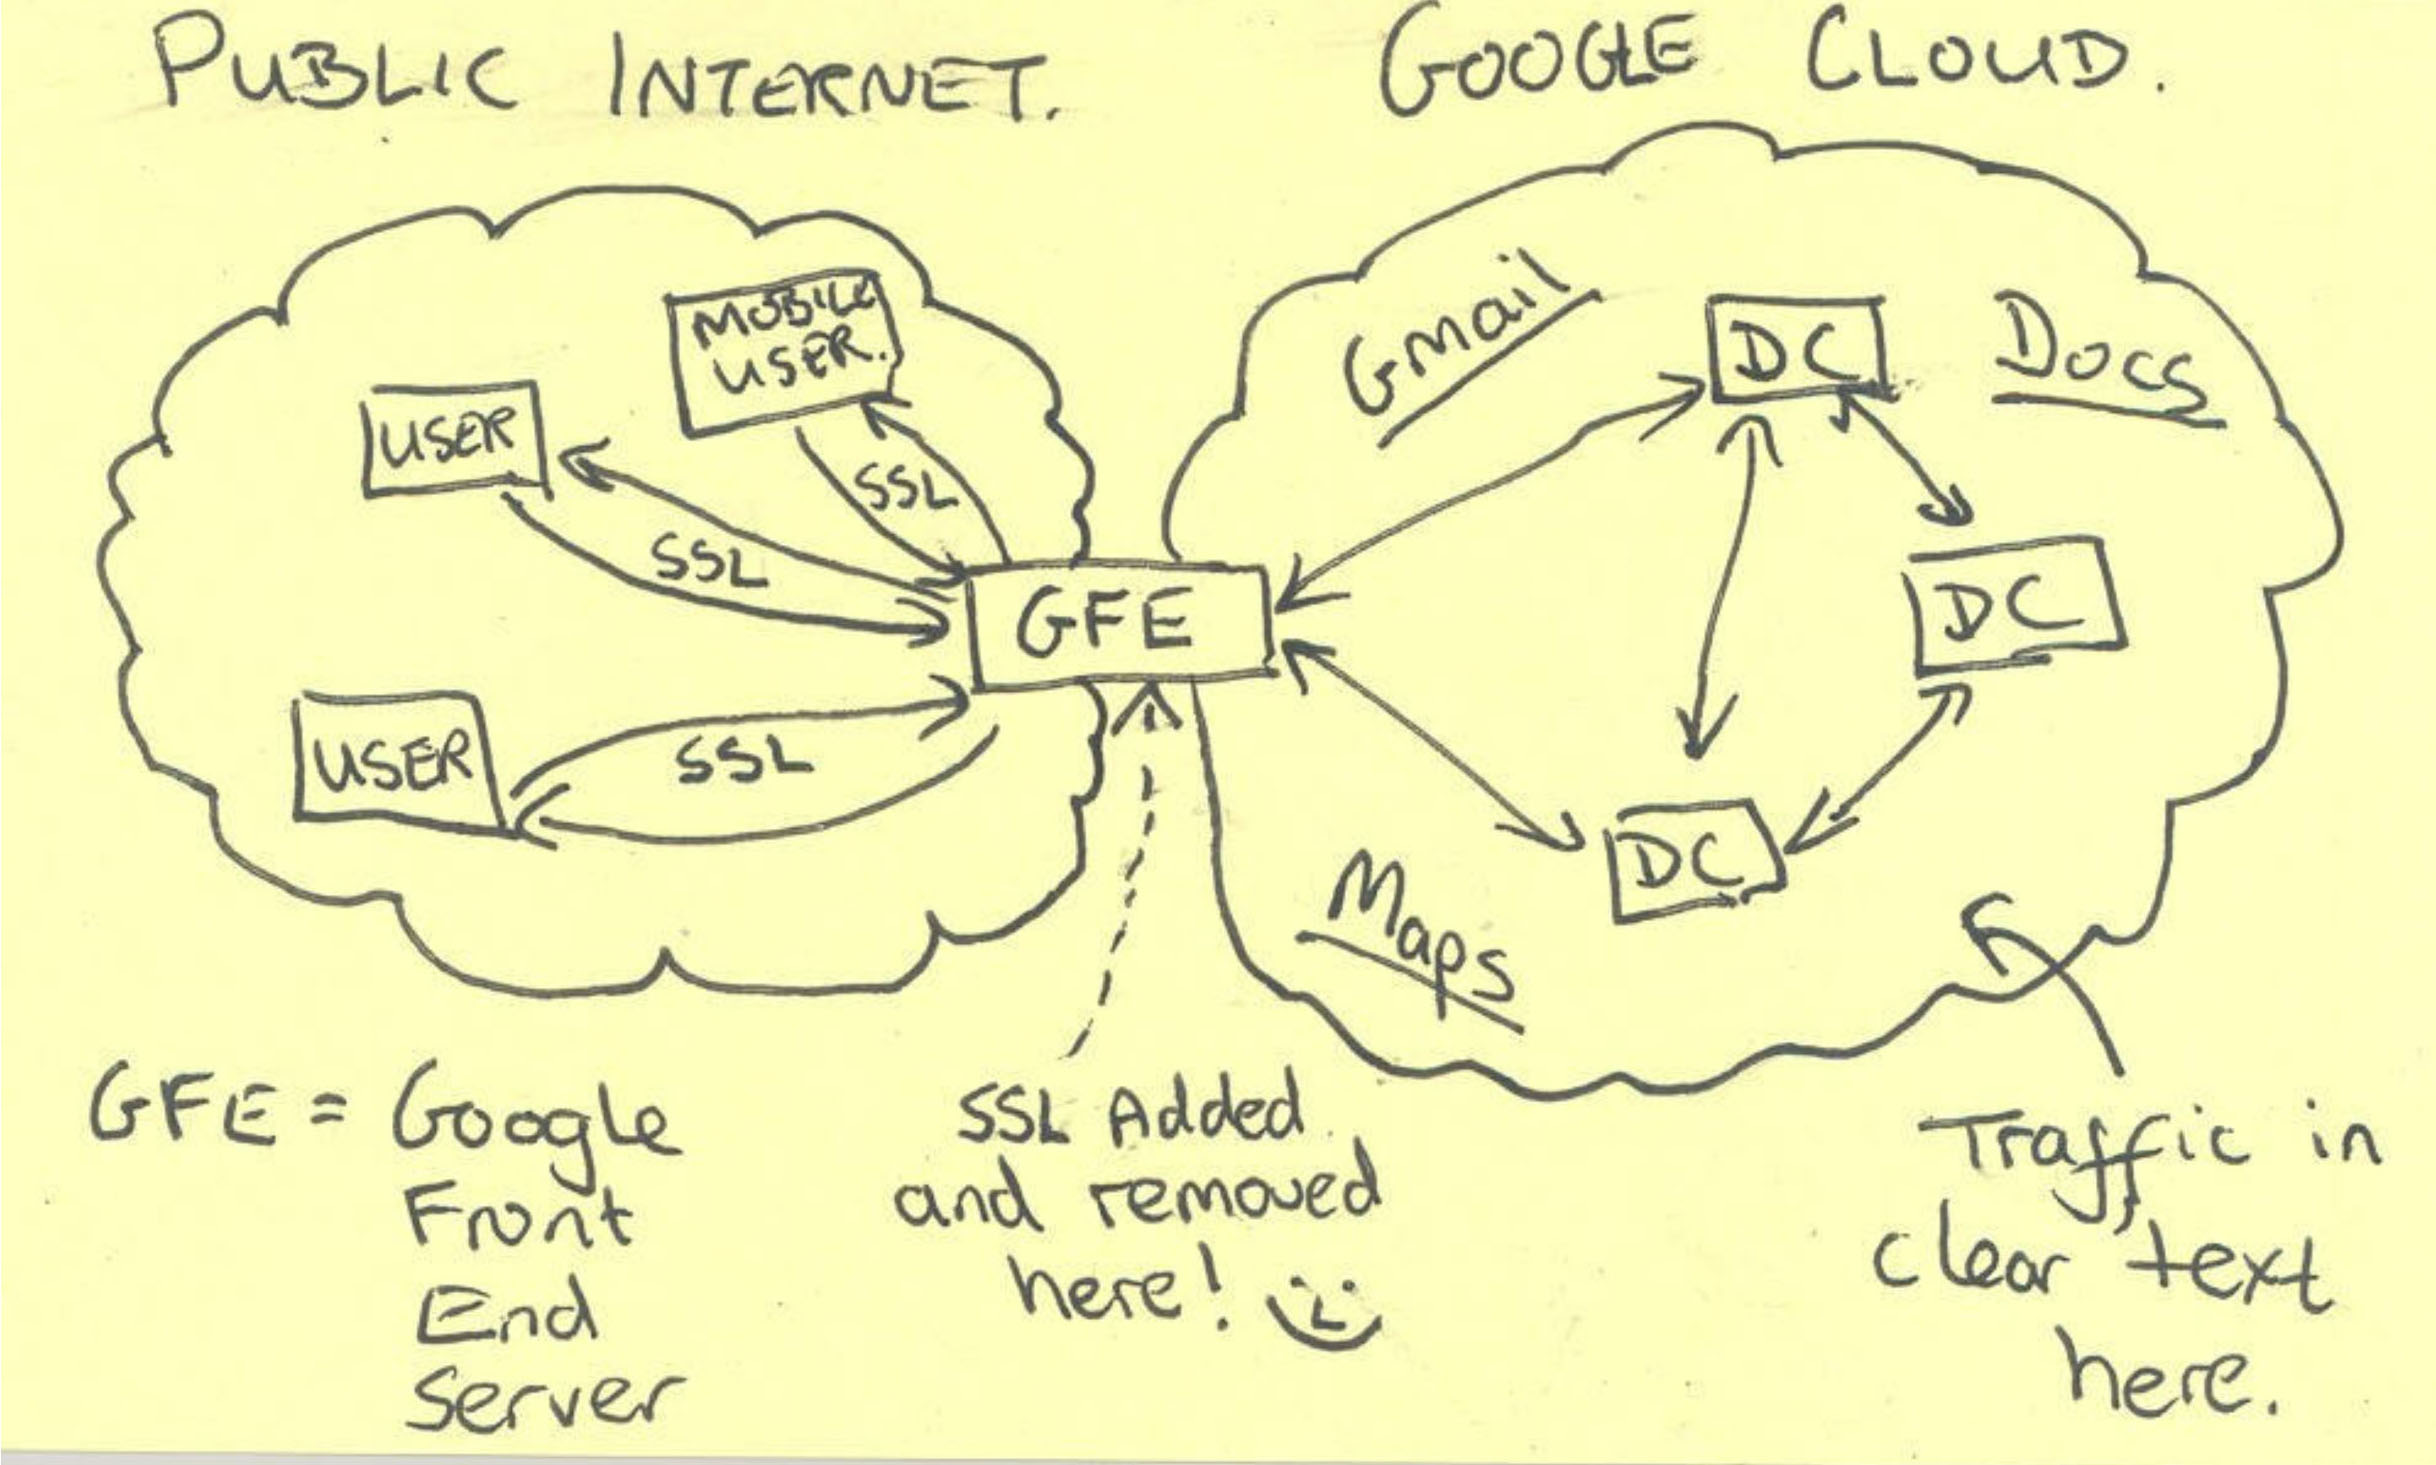
Re:Evidence points to another leaker at the NSA by FooHentai on Tuesday August 23, 2016 @04:33PM (#12347321)
No, this one was on the Google 'Front End Servers': http://www.japantimes.co.jp/wp-content/uploads/2013/11/nc201...

Regarding PRISM cooperation, I'm not sure where your doubt is coming from there. http://imgur.com/a/wRKtL

The slide was explicit, and is now many years out of date so without doubt the number of providers has increased. The means by which these provider agreements are reached is well known (National Security Letters) as is the fact that organizations are fully barred from disclosing their existence.

Re:Evidence points to another leaker at the NSA by MertsA on Monday August 22, 2016 @06:10PM (#12339822)
It was fiber taps between Google Datacenters overseas. The implication being that if your location history, emails, photos, secret diary, or what have you is transferred overseas at any point then you automatically have no more rights to privacy than a suspected terrorist.
Re:Evidence points to another leaker at the NSA by runjake on Tuesday August 23, 2016 @11:03AM (#12344263)
Re:Evidence points to another leaker at the NSA by finid on Monday August 22, 2016 @04:43PM (#12339279)
That's like asking me for evidence for the existence of the Sun. All I can do is shake my head...
Re:Evidence points to another leaker at the NSA by snowwrestler on Monday August 22, 2016 @05:11PM (#12339478)
If everything has a backdoor, then why would NSA need to stockpile 0-day bugs? Why would they need such a big TAO division? If they had a backdoor they would just use that.

The math doesn't add up.

Re:Evidence points to another leaker at the NSA by nickpsecurity on Monday August 22, 2016 @09:42PM (#12340774)
"If everything has a backdoor, then why would NSA need to stockpile 0-day bugs? Why would they need such a big TAO division? If they had a backdoor they would just use that."

That argument is not true. Spy non-fiction taught me that intelligence services sort of rate their capabilities on what intel they can bring plus how secret they must remain. The idea being a capability might be so good and so hard to replace that you only use it on highest-risk cases that nothing else works on. Additionally, lower clearances will have greater number of infiltrators. They should see less than higher clearances to reduce damage of leaks. Further, I predicted that the tools themselves were developed in Special Access Programs (SAP's) that compartmentalized away from even TS clearances then selectively released to them. Sentry Eagle et al confirmed my prediction.

You can actually see the bullshitting in progress if you look at that. Each level of clearance is told something different with the lower levels often getting lied to with only highest getting the truth. In one case, it was implied they were attempting to use supercomputers against crypto then TS/SCI version said they got companies to backdoor it. Quite the difference. ;)

Re:Evidence points to another leaker at the NSA by snowwrestler on Monday August 22, 2016 @11:42PM (#12341236)
The GP post claims that every closed-source product is perpetually backdoored. If this were true, then there would be no way to detect backdoor access, and no way to deny it short of going 100% open source, which is simply not possible for large corporations.

What you describe is how intelligence services actually work to develop and protect real tools for access. What the GP claims is a fantasy in which such work is not necessary.

Re:Evidence points to another leaker at the NSA by nickpsecurity on Tuesday August 23, 2016 @11:00AM (#12344236)
"The GP post claims that every closed-source product is perpetually backdoored. "

I agree that's a crap claim. Tried to provide alternative that showed situation is almost as bad as crap claims like that with 0-days. What overlap I did see was the emanation threat. That secrets leak out of any device and TEMPEST protection of them is illegal means that they are all backdoored for that in practice. Good news is it's a highly-specialist attack only a few countries know how to do that requires targeting and close proximity. Other good news is that smartcards and EM compatibility testing reinvented some defensive practices.

Re:Evidence points to another leaker at the NSA by comex on Monday August 22, 2016 @05:32PM (#12339604)
> Even if it's not Russia, the release of the hacking tools gives weight to the argument that nsa/fbi should not be able to demand companies to create a back door in their products.

Not really.

iOS already, today, for no other reason than to prevent downgrades, verifies every firmware upgrade/restore with an Apple server, which sends back a per-device signature. Technically, it would not be difficult for Apple to have that same server authorize a special spy firmware only for specific device IDs. The only way this could result in a mass compromise is if Apple were hacked, but hacking Apple already gets you that - the hard part isn't writing code to spy on people (especially if you've hacked them and thus have full iOS source code), it's signing it.

This is different from exploits for code vulnerabilities, where there's always at minimum a secret (the location of the bug) that can't get out, and in some cases going from there to a working exploit is also difficult.

At worst, if Apple went beyond compromising that one phone and set up an ongoing process to compromise phones as requested by law enforcement - then there might be some sort of online portal, and maybe it could be hacked either directly or by stealing a legitimate agency's credentials. Maybe then the spy system could be used by unsympathetic governments against their enemies, though only by stealthily submitting individual requests; there would be no way to exfiltrate something from law enforcement that would compromise everyone. I don't think that's what most people are thinking when they talk about a back door "getting out" or whatnot.

Personally, I agree with Apple's refusal to create and sign a spy firmware on ethical as well as pragmatic grounds. But there's a lot of misinformation about the issue.

Re:Evidence points to another leaker at the NSA by tw04 on Monday August 22, 2016 @08:28PM (#12340435)
>iOS already, today, for no other reason than to prevent downgrades, verifies every firmware upgrade/restore with an Apple server, which sends back a per-device signature.

Are we pretending now that the government couldn't MITM and fake the response? I think they've proven they can MITM pretty much ANYTHING their hearts desire.

Re:Evidence points to another leaker at the NSA by comex on Monday August 22, 2016 @09:09PM (#12340603)
> Are we pretending now that the government couldn't MITM and fake the response? I think they've proven they can MITM pretty much ANYTHING their hearts desire.

Only if they have Apple's private keys or can break RSA...

Re:Evidence points to another leaker at the NSA by tw04 on Monday August 22, 2016 @10:08PM (#12340885)
I hope the ... was because you're aware they already broke RSA.

http://www.theverge.com/2013/12/20/5231006/nsa-paid-10-milli...

Re:Evidence points to another leaker at the NSA by comex on Tuesday August 23, 2016 @12:45PM (#12345119)
Wrong RSA. I'm referring to the algorithm, not the company.
Re:Evidence points to another leaker at the NSA by zbyte64 on Monday August 22, 2016 @08:57PM (#12340563)
They literally have the tools to do just that.
Re:Evidence points to another leaker at the NSA by willstrafach on Monday August 22, 2016 @10:59PM (#12341069)
No they do not. The device will not install a firmware if the restore is not signed by Apple's private key.
Re:Evidence points to another leaker at the NSA by willstrafach on Monday August 22, 2016 @11:06PM (#12341100)
That is not how TSS is set up though. "Special" restores are heavily audited so many would be aware that it occurred. who knows how easy it would be to keep that contained.

Further, if people are paranoid of this, a crowdsource based mitm restore server could be setup (similar to saurik's) to watch the hashes and block restore + alert the user if a firmware file is about to be installed with a different hash than what it should be.

Re:Evidence points to another leaker at the NSA by DanielDent on Monday August 22, 2016 @06:59PM (#12340050)
I think these types of issues are why apple has started removing some of the encryption of the firmware itself.
Re:Evidence points to another leaker at the NSA by AceJohnny2 on Monday August 22, 2016 @12:40PM (#12337533)
Except the FBI explicitly said Apple could work on and execute the backdoor internally and destroy it after use. It would never need to come out of their secure facilities.

So I don't think this was the strongest argument for Apple. A better one is that once the US can compel Apple to do this, what's to stop Russia, China from demanding the same thing?

Re:Evidence points to another leaker at the NSA by silvestrov on Monday August 22, 2016 @12:49PM (#12337588)
When the back door is created, it cannot be destroyed. FBI had tons of other phones they wanted to access [1]. Hacking one phone would set a precedent that Apple would have to hack numerous other phones.

It is so simple to steal software, just like NSA's hacking tools were stolen.

If NSA cannot keep software safe, why can you think that Apple can? I think it's unreasonable to require Apple to have a higher level of security than NSA effectively has.

1: http://www.sfgate.com/nation/article/Apple-FBI-face-off-in-C...

Re:Evidence points to another leaker at the NSA by unfamiliar on Monday August 22, 2016 @02:04PM (#12338147)
> When the back door is created, it cannot be destroyed.

If the "backdoor" in question is a malicious signed OS update, then it can absolutely be destroyed. There are plenty of reasons to avoid backdoors without imbuing them with mystical qualities like the inability to delete them.

Re:Evidence points to another leaker at the NSA by charliedevolve on Monday August 22, 2016 @02:14PM (#12338223)
Signed updates aren't secure either. Ask Microsoft.
Re:Evidence points to another leaker at the NSA by ethanbond on Monday August 22, 2016 @03:41PM (#12338841)
The backdoor itself can be destroyed. The precedent of compelling a company to write an intrusion into its own software cannot be destroyed.
Re:Evidence points to another leaker at the NSA by a3n on Monday August 22, 2016 @03:20PM (#12338693)
It would be like requiring a pediatrician to keep smallpox in their refrigerator.
Re:Evidence points to another leaker at the NSA by toufka on Monday August 22, 2016 @12:49PM (#12337595)
>and destroy it after use...

And then recreate, and redestroy it for each of the >100 law enforcement requests in NY alone. Etc. Etc. Though the FBI says that, Apple pointed out in their brief that the reality of what that kind of situation would look like was absurd.

Re:Evidence points to another leaker at the NSA by pdkl95 on Monday August 22, 2016 @01:10PM (#12337758)
> once the US can compel Apple to do this,

What's to stop the FBI from repeating the same process in the future? Fighting future orders would be much harder after precedent is established.

Remember that after James Comey talked about spending "a lot" to get into the San Bernadino phone, he wanted a way into the phones that "doesn't involve spending tons of money in a way that's un-scaleable."[1]

[1] https://www.washingtonpost.com/news/post-nation/wp/2016/04/2...

Re:Evidence points to another leaker at the NSA by rdtsc on Monday August 22, 2016 @01:03PM (#12337700)
> Apple could work on and execute the backdoor internally and destroy it after use.

Right. So if there is a backdoor, they won't commit the code to a repo, but write it from scratch every time FBI calls them.

Yes, very realistic.

From that we learn two things, both bad and which tells us not to listen to or work with FBI if possible:

1) FBI is stupid and doesn't know how these things work

2) FBI is malicious and is lying

Re:Evidence points to another leaker at the NSA by balabaster on Monday August 22, 2016 @02:38PM (#12338390)
I have a fundamental issue with this paradox...

> 1). FBI is stupid...

While the tech industry like to cast aspersions about the FBI and how idiotic they are, I think this perception is wrong. I don't think they could possibly have access to the resources they do and be stupid. They may not always understand fully the technology they're working with, but I'm quite sure there are resources within their reach that would quickly set them straight where required. I'm sure at the very least they could create a GUI interface using Visual Basic to track their IP address.

> 2). The FBI is malicious and lying...

I'd like to believe they're neither but the more time goes on, the more my goodwill towards them fades... and while they're not the NSA, the doubt the NSA has cast on Government Agencies has tainted that with the "guilty by association."

I can't believe they're incompetent, I do believe they (largely) do what they do with good intent, I think their strategy is short sighted.

That leaves me asking the question: Have they lost sight of the future repercussions of the actions they take today or are they actively considering the future repercussions when making policy today?

If they're actively considering the future repercussions of policies they're making today, that is the greater cause for concern because they're actively making policy that ensures the state's ability to monitor (and in effect, censor) the future population - counter to the first and fourth amendments.

Re:Evidence points to another leaker at the NSA by smacktoward on Monday August 22, 2016 @02:52PM (#12338466)
> While the tech industry like to cast aspersions about the FBI and how idiotic they are, I think this perception is wrong. I don't think they could possibly have access to the resources they do and be stupid.

I responded to an FBI call for recruits to staff up their cybercrime divisions after 9/11, and was in their recruitment pipeline for two and a half years.

Based on my experiences during that period, I have no problem believing that they are stupid.

Re:Evidence points to another leaker at the NSA by HillRat on Monday August 22, 2016 @06:21PM (#12339875)
>I responded to an FBI call for recruits ... and was in their recruitment pipeline for two and a half years.

Dude! Just nine more months and they would have completed your SSBI and you could have been forwarded to the next stage!

God, it's like you don't want to put your life on hold for multiple years while an impersonal bureaucracy methodically sorts through your entire personal history.

Re:Evidence points to another leaker at the NSA by xkcd-sucks on Monday August 22, 2016 @02:14PM (#12338219)
>Right. So if there is a backdoor, they won't commit the code to a repo, but write it from scratch every time FBI calls them.

Ethics aside, this seems like a very lucrative gig for software companies that bill by the hour

Re:Evidence points to another leaker at the NSA by rdtsc on Monday August 22, 2016 @08:36PM (#12340468)
Hah! Let's not give Accenture any ideas now ;-)
Re:Evidence points to another leaker at the NSA by vonmoltke on Monday August 22, 2016 @12:49PM (#12337598)
What stops them from doing it now? What about Apple being willing to hop in bed with the US government affects whether they would with Russia or China, or whether either of them would ask for this from Apple?
Re:Evidence points to another leaker at the NSA by user731955373 on Monday August 22, 2016 @01:41PM (#12337967)
Even if they wouldn't "hop into bed" with other governments, if they had hopped into bed with the US govt. they would have lost revenue in those other markets, which would be likely to view Apple products as backdoored by the US government.

As a multinational company, it's in Apple's interests to maintain a 'no backdoors' strong privacy stance, or it will both lose foreign markets (that are afraid of US/other nation's backdoors) and have to contend with increased requests from various governments for backdoors/audits (they got backdoor access, why can't we?), and the associated revenue lose.

Re:Evidence points to another leaker at the NSA by vonmoltke on Monday August 22, 2016 @10:17PM (#12340921)
That's not the point I was challenging (which I couldn't highlight and quote because Safari in the iPad apparently decided I didn't need that ability). I was challenging the idea that cooperating with the US government somehow makes it easier for, or in any way affects the ability of, other governments to demand cooperation with their own programs. I was not saying there wouldn't be consequences for Apple doing so, or that they should have.
Re:Evidence points to another leaker at the NSA by leereeves on Monday August 22, 2016 @12:52PM (#12337623)
Why would you think Apple is more likely to cooperate with Russia or China than with the US government?
Re:Evidence points to another leaker at the NSA by vonmoltke on Monday August 22, 2016 @10:14PM (#12340913)
I don't, and said nothing of the sort. I said that their decision to cooperate with one government is independent of their decision to cooperate with another. Thus, cooperating with the US does not mean they can't tell Russia and China to go fuck themselves if they asked for the same thing.
Re:Evidence points to another leaker at the NSA by nathanaldensr on Monday August 22, 2016 @01:06PM (#12337735)
Money, more specifically the desire for it, knows no bounds. Apple is a multinational corporation whose goal is to deliver value (read: money) to shareholders. The idea of political boundaries meaning anything is a quaint notion that I feel was true only long in the past, if it ever was.

I'm not saying Apple is evil, merely that multinational corporations don't have to care about political boundaries.

Re:Evidence points to another leaker at the NSA by leereeves on Monday August 22, 2016 @01:12PM (#12337783)
That's true, but I meant to ask if there is any reason to think Apple is likely to cooperate with Russia or China, or if that was mere speculation.
Re:Evidence points to another leaker at the NSA by user731955373 on Monday August 22, 2016 @01:43PM (#12337979)
Re:Evidence points to another leaker at the NSA by maze-le on Monday August 22, 2016 @01:09PM (#12337755)
Lets forget the argument, that this sets a dangerous precedent for a moment... Even if you assume the strictest possible processes, even if you assume only the most genius techs working on a backdoor like this: In the end the people implementing and operating a backdoor are just people like you and me. People make mistakes no matter how good the skills and processes are. And if this mistake happens, as it will happen invariably, the backdoor is out in the open and usable for adversaries with even more malicious intent.
Re:Evidence points to another leaker at the NSA by wyager on Monday August 22, 2016 @12:51PM (#12337609)
Why do you trust that this was actually the FBI's intent? That sounds like a desperate PR gambit.