Google has extremely strict safeguards in place to prevent eg. employee Joe from accessing ex-girlfriend Mary's Gmail. Very few people would have full access to individuals' Google accounts. This kind of privacy breach would be very damaging to Google.
Niantic is a tiny startup with around 50 employees. I would expect most developers within the team would have full access to the production database, or would be given access if they had a need for it. It's unlikely that there's any oversight over who can access data - it's just a 'game'.
Where are their backups stored? Are they encrypted? Who has access to the decryption keys? We don't know, but I would bet any amount of money that their systems are vastly less secure than Google's are.
The relationship between Google and Niantic isn't relevant as to whether they are capable of keeping these credentials secure.
I know a bit about google's internal privacy safeguards (including how long they've been in place), and I know a bit (nothing that wasn't in the news) about the NSA's internal privacy safeguards from a certain point in time.
Obviously I don't know what it's like at the NSA today, but it's worth laughing (or crying) at the fact that there was a time when Google placed more restrictions and security in place to protect its users from rogue employees than the NSA did.
Not to get too political.
Do they store this API key with full access to a Google account the same way that an official Google app (e.g. Gmail itself) stores my secret data? If so, I probably trust it. Or do they just throw it in a GCE database without a whole lot of thought around a security policy since they're still a fast-moving startup, and maybe my credentials get logged somewhere, or synced to an analytics system that's not treated as classified and a whole bunch of employees can inadvertantly access, etc
Seems like I have no way of knowing (unless maybe it's in their terms of service?). It could very well be a "Huge security risk"
However, "Popular thing possibly has crummy security practices (we just don't know)" isn't HN-worthy, it's just FUD. I think both of us would prefer a HN full of well-researched articles over one full of clickbait FUD.
Bullcrap. Best security policy is trust, but verify.
Assuming that well established businesses have good security practices without doing proper review is what allowed all those fraudulent SWIFT transactions to go through a few months ago. It's perfectly valid to ask why the hell Pokemon Go thinks it needs access to your private email.
A third-party company, even with significant investment and history with Alphabet, requesting full access to my Google account despite needing ZERO access (i.e. for what they need, requesting no permissions would suffice) is sketchy and inherently untrustworthy.
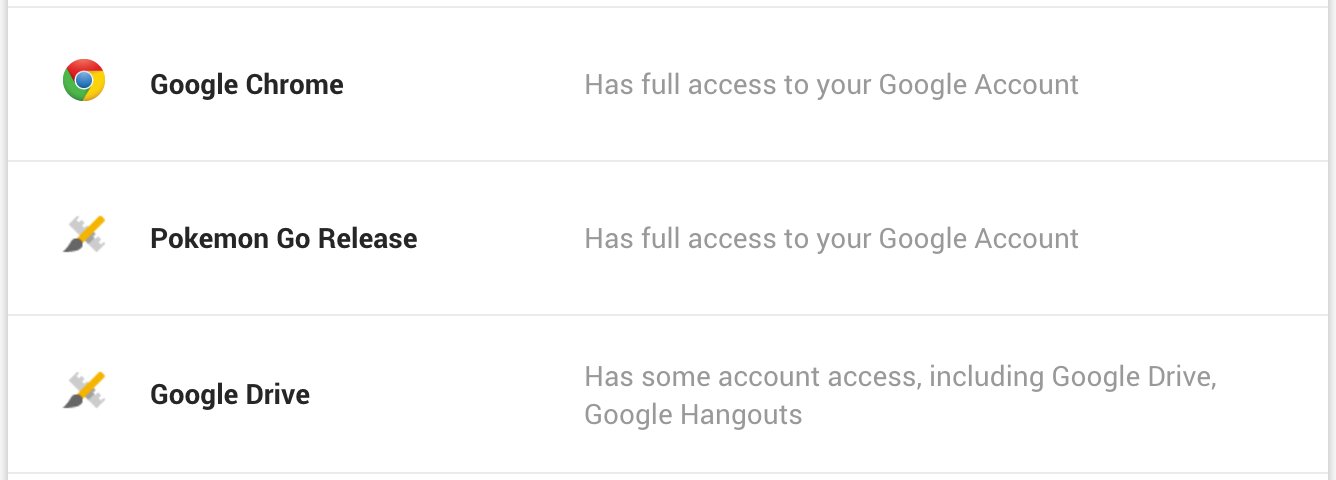
Not at all necessary for this situation to occur. I just finished implementing a system (nothing to do with Pokemon) that also requests permission from external sites in a similar way. The mechanics for doing this are fiddly and checking this is actually set up correctly is likely well down the priority list provided things at least appear to work.
It is entirely possible that someone who had never done it before set it up in a hurry then everyone in the dev team just blindly clicked through without ever properly reading what was being requested because they were all in a rush to finish their stuff.
Also Gmail allows you to create more than one account. Instead of all this alarmism in media just tell people they should create a separate account in Gmail just for games instead of using the one you are worried about some big billion dollar company accessing it (which they already do).
Niantic are also the folks behind Ingress, if you've heard of that.
[0] Specifically, Alphabet owns a significant portion of Niantic, along with Nintendo: https://nianticlabs.com/blog/niantic-tpc-nintendo/ (they were previously wholly-owned by Google).