News for hackers. Stuff that matters.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by MenhirMike on Thursday July 04, 2024 @11:38AM (#40875747)
Does anyone have a recommendation for an Open Source 2FA OTP app? That's the only thing I use Authy for, to scan the QR Codes into the App and generate the 2FA tokens, but in a way that allows me to migrate to another phone without having to re-set all the 2FA tokens on the vendor side.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by SushiHippie on Thursday July 04, 2024 @11:49AM (#40875822)
For Android I'd recommend Aegis

https://f-droid.org/packages/com.beemdevelopment.aegis/

Or if you have a YubiKey you could also use it for TOTPs

Windows, Linux, Android: https://github.com/Yubico/yubioath-flutter

iOs: https://github.com/Yubico/yubioath-ios

I personally use Bitwarden for TOTPs (with a self hosted vaultwarden instance), it's by far not the most secure way to store your passwords and TOTPs next to each other, but it saves so much time.

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by alias_neo on Thursday July 04, 2024 @11:53AM (#40875839)
This.

I migrated to Aegis a while back because I wasn't happy with how hard it is to get secrets out of Authy, or that someone else is managing them, and they they need my phone number (guess I was right, again).

I use Folder Sync on my Android to sync the Aegis auto-backups to a MinIO bucket I host at home.

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by tamimio on Thursday July 04, 2024 @12:11PM (#40875987)
Ente Auth or bitwarden builtin one or keepassXC builtin one.

Migrating from Authy is a headache, though you don’t have to reset the tokens. I found a way to do it (1), but I had to do it manually because Authy only exported the email/user and the token. Now, if you are like how I used to be, having the same email for different accounts, the exported JSON will be confusing and there's no way to tell which account is for which service. Only in the Authy UI can you tell. I had to follow the order of the JSON and the app, one by one, for my 700+ accounts, and verify that it works by going to the service site and testing the generated code from the new app. It took a whole week!

Edit: to add, I wouldn’t recommend using Yubico or hardware-based ones unless you will have two or more replicas, losing them is easy compared to having your tokens backed up in an encrypted KeepassXC db for example.

(1) https://gist.github.com/gboudreau/94bb0c11a6209c82418d01a59d...

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by MaxMatti on Thursday July 04, 2024 @11:43AM (#40875783)
I used Aegis for a while and really liked it, switched to Bitwarden now but the UX was better
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by hypeatei on Thursday July 04, 2024 @12:10PM (#40875976)
I use both and make offline backups regularly.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by mrb on Thursday July 04, 2024 @11:54AM (#40875852)
I use andOTP https://github.com/andOTP/andOTP and my favorite feature is the database of 2FA can be backed up PGP-encrypted and reimported on another device. But sadly it is no longer maintained. The latest version on Google Play Store is from 2021 and can still be installed and works fine on Android 14.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by bobbylarrybobby on Thursday July 04, 2024 @11:48AM (#40875815)
I'm of the opinion that it's basically fine yo store them in your password manager. Yes if your password manager is broken into you lose everything (same as having no 2fa in that case), but you still prevent people from guessing your password and often avoid having to deal with email- or text-based 2fa. And if your password manager is broken into, there's a good chance your device has been broken into, in which case it doesn't matter where you store your 2fa.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by brightball on Thursday July 04, 2024 @11:54AM (#40875846)
I mix it up and store some 2FA on different apps.

When it’s not a system I’m deeply concerned about I will just use the 2FA on the password manager.

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by nwhale on Thursday July 04, 2024 @11:48AM (#40875819)
If you do not need QR codes, oathtool is great. You can protect your tokens, recovery codes etc. with gpg -c or similar, so the encryption is entirely separate from the authentication mechanism.

And you actually know what is going on. Works for GitHub.

https://www.nongnu.org/oath-toolkit/

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by TheBozzCL on Thursday July 04, 2024 @11:43AM (#40875777)
I use a YubiKey with their Authenticator app.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by WanderPanda on Thursday July 04, 2024 @11:41AM (#40875766)
I‘m using Raivo. It hasn’t let me down, yet
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by mm263 on Thursday July 04, 2024 @11:46AM (#40875797)
The same Raivo that was sold to some shady dev who proceeded to delete all of the OTPs that I had in the app?

https://www.reddit.com/r/privacy/comments/1d3zqvv/raivo_auth...

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by pxeger1 on Thursday July 04, 2024 @11:44AM (#40875786)
Raivo was bought by a shady developer last year and is no longer open source. If that wasn’t enough, a few weeks ago they released an update which deleted all your codes - failing at literally the one job a 2FA app has!
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by notatworkbro on Thursday July 04, 2024 @11:43AM (#40875780)
I've implanted my 2FA token in my arm and just hope it never breaks :D
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by fragmede on Thursday July 04, 2024 @11:49AM (#40875823)
Which one did you get? Did you get the Apex Flex from Dangerous Things? How do you like it/how was the process?

https://dangerousthings.com/product/apex-flex/

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by prophesi on Thursday July 04, 2024 @12:37PM (#40876209)
For Android, if you happen to use Keepass as your password manager, I really like KeePassDX[0]. If the camera app you use doesn't support QR scanning, though, you'd need an app for that (and I don't think any FOSS camera apps implement this, as for as I can tell).

This one[1] seems the most up-to-date, by a German research group. You'd share the link as text to the KeePassDX app, search for the entry it's for, and it populates it with the HTOP/TOTP secret.

There are iOS Keepass clients that support this as well, though from what I can tell there's some drama with source code[2][3] in the landscape.

[0] https://f-droid.org/en/packages/com.kunzisoft.keepass.libre/

[1] https://f-droid.org/en/packages/com.secuso.privacyFriendlyCo...

[2] https://github.com/MiniKeePass/MiniKeePass/issues/606

[3] https://keepassium.com/articles/keepass-apps-for-ios/welcome...
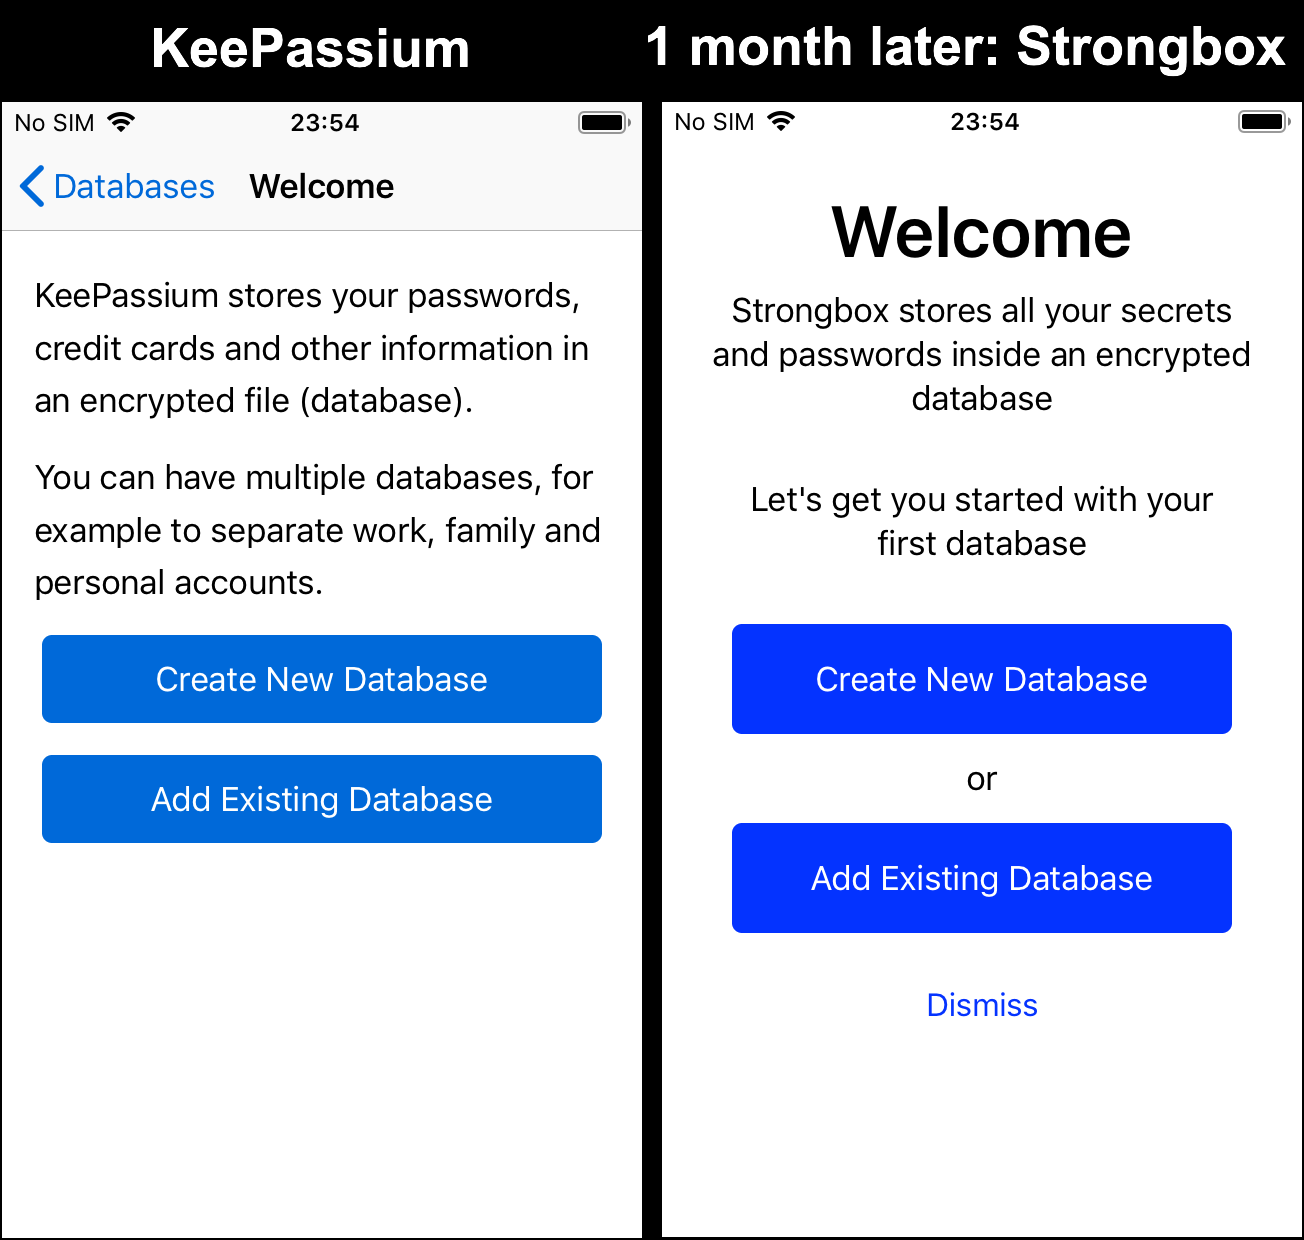
And other allegations under the ethics & transparency sections of KeePassium's list of iOS alternatives https://keepassium.com/articles/keepass-apps-for-ios/

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by pnw on Thursday July 04, 2024 @01:44PM (#40876710)
I started with Keepassium but ended up with Strongbox which has been great.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by holigot on Friday July 05, 2024 @05:26AM (#40881206)
Don‘t know if Strongbox is working well? Developed by a single programmer… and no Audits available.
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by pnw on Monday July 08, 2024 @07:08PM (#40910759)
They address that here: https://strongboxsafe.com/support/#reamaze#0#/kb/security-an...

Is Keepassium audited?

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by KeePassium on Tuesday July 09, 2024 @07:32AM (#40914851)
We are undergoing the same CASA audit (required to access Google Drive API). And we do have people forking and building the project from source, so one can hope they read what they compile. Strongbox' source code is half-closed (see #784 in their repo) so source-level independent audit is impossible.

Otherwise, no. A third-party audit costs like a year of part-time developer, and at this stage the developer is more useful.

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by holigot on Thursday July 18, 2024 @09:47AM (#40995562)
Wise words! Most of the people think, that Strongboxsafe is an Open Source App, which is definitely not the case!

Overall a good app, but if you want true Open Source KeePassium is the app to choose.

Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by etoulas on Thursday July 04, 2024 @04:50PM (#40877935)
Re:Twilio Confirms Data Breach After Hackers Leak 33M Authy ... by izacus on Friday July 05, 2024 @03:52AM (#40880625)
As mentioned elsewhere, Aegis and Authenticator Pro are both good on Android. Both are available on Play Store and on F-Droid.