Sibling comment mentions proxying, which would be an explanation. But still, there is absolutely no working abuse handling on Chinese or Russian networks. Either they do not care or are complicit.
It’s inconvenient enough to suggest most western hackers attacking western targets would choose something else if they had the option. Thus either China’s cyber security is terrible and or these attacks are coming from Asia.
And as an attacker you couldn't care less about latency when you schedule a job of scanning bunch of ip addresses for vulnerabilities to one of thousands throwaway hacked home pcs in your fleet.
Latency doesn’t prevent such things from working, but your better off hacking local resources and then using those resources to scan locally. So all things being equal either there’s a huge surplus of especially vulnerable Chinese machines or a surplus of Asian hackers.
To be clear there could just be a huge surplus of easily hacked Chinese machines, but that itself would be noteworthy.
https://files.mastodon.social/media_attachments/files/022/47...
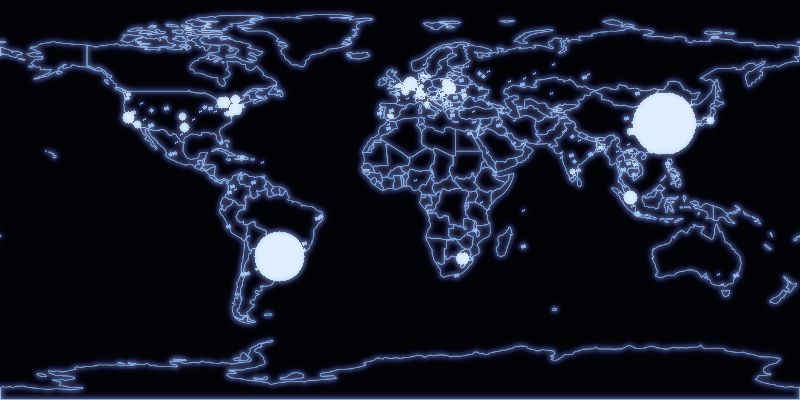
It's not perfect though: Botnet activity isn't going to come from any particular ASN, but a wide array of unpatched smart fridges and compromised enterprise routers all over the world, so it doesn't crop up in this type of analysis.
- AS9808 China Mobile Comms, China
- AS4837 China Unicom, China
- AS132203 Tencent, China
- AS211252 Delis LLC, US
- AS209605 Host Baltic, Lithuania
- AS4134 China Telecom, China
- AS16276 OVH, France
- AS134963 Alibaba, Singapore
- AS45102 Alibaba, China
"china bad" or not, i have hard data that most of this spam orginates from chinese or chinese-controlled ASes.