News for hackers. Stuff that matters.
Re:Ask HN: Developer abused “sign in with GitHub”? by arc-in-space on Friday December 09, 2022 @03:32AM (#33919015)
Whoa, I'm very surprised at the amount of "told you so" and blaming the user in this thread. How many times are we going to retread the same tired arguments in this industry? Not everyone who uses github and other SSO sources is a elite hacker that knows exactly what the buttons they're pressing mean, plus sometimes we just make dumb mistakes. At the very least github should make it much higher friction to give a third party access to fuck with your account, and only make it dead simple to act as a identity provider.
Re:Ask HN: Developer abused “sign in with GitHub”? by message on Saturday December 10, 2022 @06:36AM (#33931739)
This. Also the whole situation reminds me the early days of Facebook, when people abused your account with posts to the wall and so on.
Re:Ask HN: Developer abused “sign in with GitHub”? by iamsaitam on Friday December 09, 2022 @04:19AM (#33919320)
You don't have to be an Elite Hacker to read a permissions list and be informed about what you're consenting to.
Re:Ask HN: Developer abused “sign in with GitHub”? by nulld3v on Friday December 09, 2022 @09:22AM (#33921457)
The UX for the authorization prompt is awful. The only difference between a regular sign in prompt and authorizing access to repositories is a single word: "Repositories".

For example, these two prompts look very similar:

https://community.atlassian.com/t5/image/serverpage/image-id...

https://user-images.githubusercontent.com/2584493/51578239-b...
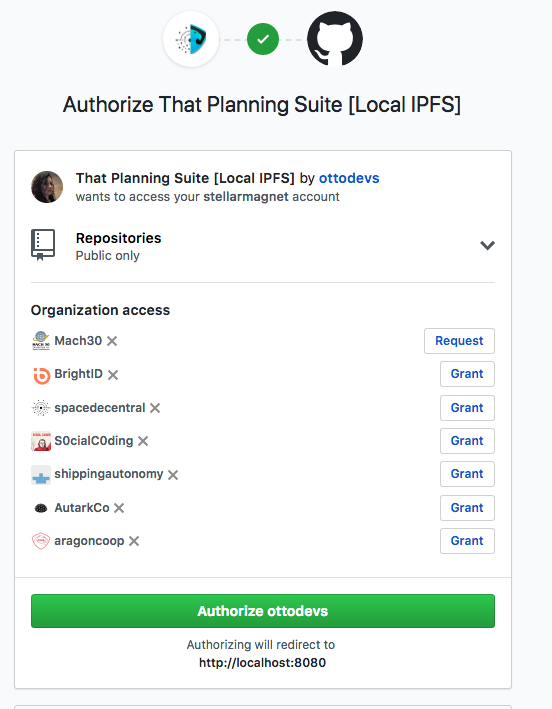
But they have entirely different levels of access!

Re:Ask HN: Developer abused “sign in with GitHub”? by vertis on Friday December 09, 2022 @05:49AM (#33919928)
Everyone over reaches on permissions though. It's practically industry standard to ask for a whole bunch of permission you don't need. Such that the likes of Google have multi-year efforts to crack down on it and reduce the ability to do it (in say Android).

It's also a matter of UX. Github (or anyone with social login) should be clear about what your granting. "Do you trust this website? They will be able star repos on your behalf"

Re:Ask HN: Developer abused “sign in with GitHub”? by dpkirchner on Friday December 09, 2022 @09:49AM (#33921744)
> "Do you trust this website? They will be able star repos on your behalf"

... "and if they do this too often, it's your account that will be punished" (in big bold red text and with a 15 second delay before the authorize button is enabled).

Re:Ask HN: Developer abused “sign in with GitHub”? by abdulmuhaimin on Friday December 09, 2022 @04:44AM (#33919480)
because every time this happened, I will always think, great, now company gonna waste another resource for the benefit of the stupid, careless, lowests common denominator, and absolutely no benefit whatsoever (or worse) to people with common sense.
Re:Ask HN: Developer abused “sign in with GitHub”? by ThunderSizzle on Friday December 09, 2022 @07:38AM (#33920565)
Is it really a waste of time for Github to target the site instead of the users?

If anything, Github already wasted time by targeted the user into a victim, rather than the original source of the API call.

Re:Ask HN: Developer abused “sign in with GitHub”? by abdulmuhaimin on Friday December 09, 2022 @10:37AM (#33922419)
I didnt say that. Dont put word in my mouth.

Punish the site. But dont bother wasting anymore resources to protect the stupids. Its their own action, let them be accountable for their own choice.

Re:Ask HN: Developer abused “sign in with GitHub”? by vertis on Friday December 09, 2022 @05:46AM (#33919908)
Bad actors exist everywhere and manage to get even distinguished security people at times.

What you're doing is victim blaming. The phishing/scamming equivalent of shouldn't have been walking down an abandoned street at 1am in the morning.