News for hackers. Stuff that matters.
Re:Tell HN: IPv6-only still pretty much unusable by lzaaz on Wednesday December 07, 2022 @12:26PM (#33897234)
It is a substitute to an actual firewall because I don't need a firewall since NAT makes all of my listening ports unavailable to my WAN.
Re:Tell HN: IPv6-only still pretty much unusable by vel0city on Wednesday December 07, 2022 @12:42PM (#33897469)
Depending on the NAT implementation this can be incredibly naive. Many home routers will send ANY traffic incoming on a port to the NAT'd IP address, even if the sources don't line up.

So say Alice is behind a crappy NAT and wants to talk to Bob. Alice's router opens a port on its edge, lets say 1234, and sends traffic to Bob on port 80.

Let's say Charles knows Alice's IP address. Charles starts spamming Alice's router, eventually hitting port 1234 with bad data.

Alice's router is dumb. It sees traffic on port 1234, checks its NAT table, and sees that data is supposed to go to Alice. It happily rewrites that packet and passes it along to Alice. Now Alice is getting traffic from Bob *and* Charles. Uh oh!

Many game consoles are explicitly designed around this bad, broken behavior. You'll open a port to the matchmaking server and then the matchmaking server will tell people to connect to that IP address and port combination. Crappy home routers will happily route that data through its NAT configuration to the console despite the console never explicitly opening up traffic to those other parties. This is why some game consoles will complain about closed NAT versus open NAT.

Re:Tell HN: IPv6-only still pretty much unusable by zajio1am on Wednesday December 07, 2022 @11:02PM (#33904002)
> Alice's router is dumb. It sees traffic on port 1234, checks its NAT table, and sees that data is supposed to go to Alice.

While in principle that is possible, in practice almost all home routers are based on Linux, and Linux netfilter NAT implementation distinguish connections based on port and IP, not just port, so this would not work.

Re:Tell HN: IPv6-only still pretty much unusable by nonlogical on Tuesday December 13, 2022 @08:20PM (#33978768)
I think you would enjoy this article from Tailscale: https://tailscale.com/blog/how-nat-traversal-works/

The poke a hole to outside world to a random server, log the port allocated to you by your router and have someone else use this to connect to you is the basis of STUN protocol.

Re:Tell HN: IPv6-only still pretty much unusable by Jochim on Thursday December 08, 2022 @04:45AM (#33906141)
Home routers often greatly simplify the interface.

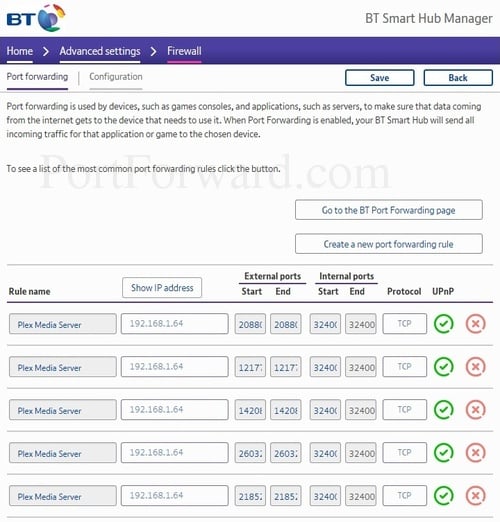
BT, one of the largest ISP's in the UK, only allow the configuration of destination IP and external/internal ports[0].

I've never expected my NAT to do anything other than map ports. I can see why the ability to map source IPs to different ports would be useful but relying on that as a security feature feels like a foot-gun. I wouldn't feel comfortable exposing an application that doesn't have some form of authentication and/or blacklisting.

[0] https://portforward.com/bt/home-hub-6/Port%20Forwarding.jpg
Re:Tell HN: IPv6-only still pretty much unusable by lzaaz on Wednesday December 07, 2022 @12:50PM (#33897581)
That's like saying that a bad firewall implementation leaks like a sieve. This is not what I was talking about.
Re:Tell HN: IPv6-only still pretty much unusable by lazide on Wednesday December 07, 2022 @01:05PM (#33897778)
Any router running a poor NAT implementation (aka most of them) essentially has a built in firewall bypass for the right attacker.

A naive NAT implementation can allow an attacker to bypass the firewall.

Re:Tell HN: IPv6-only still pretty much unusable by jraph on Wednesday December 07, 2022 @01:21PM (#33897994)
Curious, could you expand on this?
Re:Tell HN: IPv6-only still pretty much unusable by vel0city on Wednesday December 07, 2022 @02:38PM (#33899136)
I gave an example just a few comments above this. Alice never wanted Charles' traffic, the firewall should not have let it through. But because the NAT is dumb, and the firewall rules are often tied to the NAT on these crappy home routers, it's allowed. So now because Alice wanted to talk to Bob, she opened a port to the world that she never wanted opened as wide.
Re:Tell HN: IPv6-only still pretty much unusable by jraph on Wednesday December 07, 2022 @04:57PM (#33900873)
Thanks! (you added this afterwards, right? Or it's just me being tired and skipping this)
Re:Tell HN: IPv6-only still pretty much unusable by Dagger2 on Wednesday December 07, 2022 @04:33PM (#33900592)
This is straight up untrue. The only thing NAT does is change the apparent source address of outbound connections. Inbound connections aren't outbound connections, so it does nothing to them.

NAT is not a substitute for a firewall.

Re:Tell HN: IPv6-only still pretty much unusable by noipv6 on Wednesday December 07, 2022 @12:30PM (#33897277)
those of us who want to have the same port on different computers available to the internet might see that as a bad thing
Re:Tell HN: IPv6-only still pretty much unusable by staringback on Wednesday December 07, 2022 @12:30PM (#33897282)
Oh you don't need a firewall then? I guess accessing a routers web interface from the WAN is a-okay
Re:Tell HN: IPv6-only still pretty much unusable by jraph on Wednesday December 07, 2022 @12:37PM (#33897368)
My shitty cable modem which is also a router does not expose its web interface to the world by default.

I don't understand why you'd need a firewall if

- you trust devices on your network (yes, big if, but even then: the only reachable ports of a machine from the outside are those explicitly open to the outside, most stuff listens to 127.0.0.1 anyway)

- you only configure your NAT to forward ports you would open on your firewall

Re:Tell HN: IPv6-only still pretty much unusable by sph on Wednesday December 07, 2022 @12:43PM (#33897484)
My shitty router also firewalls incoming IPv6 connections by default, unless I manually allow them per-device, so I don't get your point.
Re:Tell HN: IPv6-only still pretty much unusable by jraph on Wednesday December 07, 2022 @12:55PM (#33897649)
My point is lzaaz's one https://news.ycombinator.com/item?id=33897568

I didn't think of my cable modem as a firewall. Maybe technically it has one to provide the feature of blocking access to its web interface from the world, or maybe it just listens to the right network. I don't know, but for all intent and purposes, setting up a firewall myself does not seem necessary.

To be fair, I was also a bit annoyed by staringback's phrasing.

[dead]
Re:Tell HN: IPv6-only still pretty much unusable by jraph on Wednesday December 07, 2022 @12:45PM (#33897531)
What's with the attacks??

I make sure what I build supports IPv6 (and I'll use tunnels if it's what it takes) but I can't make the only cable ISP available at my place support IPv6. I wish it did. I wish I didn't have to use its garbage hardware.

Re:Tell HN: IPv6-only still pretty much unusable by lzaaz on Wednesday December 07, 2022 @12:49PM (#33897568)
My router's httpd listens on the LAN not the WAN unless I tell it to. This is unrelated to what I said.