News for hackers. Stuff that matters.
Re:How can you be fooled by the U+202E trick? (2013) by ajuc on Wednesday February 16, 2022 @06:03AM (#30358508)
The problem in this case was that we depend on convention (filenames and extensions) for security.

Operating system should already know if a file is executable and desktop should be using this information when presenting files instead of conventional names.

Yes it would mean that when you download a file you have to set the executable attribute before you can run it. It's already almost exactly like that on Linux. That's a good thing.

Re:How can you be fooled by the U+202E trick? (2013) by thaumasiotes on Wednesday February 16, 2022 @06:21AM (#30358629)
> Operating system should already know if a file is executable and desktop should be using this information when presenting files instead of conventional names.

That already happens. If you set the "Details" view in Windows, it will display one file per row with various columns showing file metadata, including the file type. So for the example in the post, you'd see "[Word icon] annexe.doc - [the date] - Application" as opposed to "[Word icon] annexe.doc - [the date] - Microsoft Word 97 - 2003 Document".

Re:How can you be fooled by the U+202E trick? (2013) by ajuc on Wednesday February 16, 2022 @06:38AM (#30358741)
I meant more like huge red and green exclamation mark near the file icon, not "type: Application" hidden in rarely shown places.

In linux it's pretty obvious: https://www.rootusers.com/wp-content/uploads/2018/01/gnome-t...
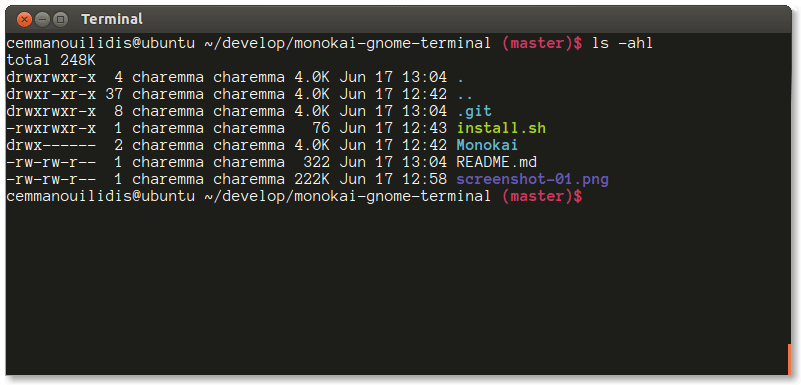
The main advantage is that the UI for opening documents (vim file) is different from the UI for running executables (./file) which is different from the UI for running executables as administrator (sudo ./file).

This makes it impossible to accidentally execute a file that looks like a document.

Re:How can you be fooled by the U+202E trick? (2013) by trasz on Wednesday February 16, 2022 @07:13AM (#30359014)
On Linux you have another problem though: you can have several files with the exact same name, just encoded differently.
Re:How can you be fooled by the U+202E trick? (2013) by jcelerier on Wednesday February 16, 2022 @07:53AM (#30359367)
As a desktop user, it makes me physically ill everytime I have to do that. I'd honestly pay for someone to make auto-executing the default on most common Linux distros. Like, in 20+ years of using computers, I don't remember one time where I downloaded something and did not want to run it afterwards.
Re:How can you be fooled by the U+202E trick? (2013) by loudmax on Wednesday February 16, 2022 @08:40AM (#30359757)
Fortunately for the rest of us, common Linux distro maintainers have a better understanding of security than you appear to.

If I download a pdf, I don't want it to run. I probably want to open it, but if I've gone through the trouble of downloading it onto the filesystem as opposed to just opening it in the web browser, there may be other things I want to do with it. Maybe I want to print it, or maybe I want to break it up into component parts. Or maybe I want to transfer it to a sandboxed environment before I open it because I don't trust it.

If you don't want to take an active role in maintaining security on your computer, then by all means use a commercial operating system. Pay a license and let Microsoft and Apple make those decisions for you. They have competent people who can program reasonable default settings for the average user. If you're running Linux or an open source operating system, you've already decided to take these responsibilities into your own hands.

Re:How can you be fooled by the U+202E trick? (2013) by jcelerier on Wednesday February 16, 2022 @09:49AM (#30360640)
> If you don't want to take an active role in maintaining security on your computer, then by all means use a commercial operating system. Pay a license and let Microsoft and Apple make those decisions for you. They have competent people who can program reasonable default settings for the average user. If you're running Linux or an open source operating system, you've already decided to take these responsibilities into your own hands.

That is a beyond ridiculous take. The last Windows OS that did not make me mad was Win98, and every time I have to use Mac machines I want to gouge my eyeballs out. I want an OS that lets me shoot myself in the foot as much as I want.

> If you're running Linux or an open source operating system, you've already decided to take these responsibilities into your own hands.

no, I just want to use the fastest possible OS for my use case on my hardware, which is Linux.

Re:How can you be fooled by the U+202E trick? (2013) by devit on Wednesday February 16, 2022 @08:31AM (#30359678)
Here's a gift for you:

inotifywait -m -e create "$(xdg-user-dir DOWNLOAD)"|while read d e f; do chmod +x "$d/$f"; done

You can add "-r" if you want to also do it on subdirectories, and you can specify another directory instead of the default downloads directory.

Though I don't really recommend doing this since you should not be executing downloaded binaries often enough for this to be worth doing.

Re:How can you be fooled by the U+202E trick? (2013) by jcelerier on Wednesday February 16, 2022 @09:47AM (#30360614)
> Though I don't really recommend doing this since you should not be executing downloaded binaries often enough for this to be worth doing.

I literally do this multiple times per day. What in hell do you folk do with your computers?

Thanks for the script ! There's a few tens of thousands of files in my downloads folder, I hope this isn't going to pollute the inotify fds too much...

Re:How can you be fooled by the U+202E trick? (2013) by assbuttbuttass on Wednesday February 16, 2022 @09:56AM (#30360751)
I usually install programs through the distro package manager. Out of curiosity, what are you doing that requires downloading so many executables from the web?
Re:How can you be fooled by the U+202E trick? (2013) by pixl97 on Wednesday February 16, 2022 @10:48AM (#30361504)
>requires downloading so many executables from the web?

Hopefully not leaking company information to clever attackers.

I work with a number of clients in high security environments where you have to get permissions to perform operations like execution (or even setting chmod x on a file). It really does limit people running random things and causing destruction.

Re:How can you be fooled by the U+202E trick? (2013) by alpaca128 on Wednesday February 16, 2022 @11:24AM (#30361991)
When you seriously download and run multiple executables a day I wouldn't call that a common use-case. At least 99.9% of my downloaded files are not executables. Those are usually pulled via the package manager or git, so basically I only download an AppImage if both the repos and flatpak can't install it.

I have no idea in what situation I'd need to load so many executables via the browser.

Re:How can you be fooled by the U+202E trick? (2013) by jcelerier on Thursday February 17, 2022 @05:53AM (#30371749)
I mostly use appimages
Re:How can you be fooled by the U+202E trick? (2013) by marcosdumay on Wednesday February 16, 2022 @10:47AM (#30361491)
I can't remember the last time I had to do it. Not on the last 4 years for sure.

Executables tend to come compressed with a lot of other files nowadays, and compression software knows to set the executable bit when extracting them.

Re:How can you be fooled by the U+202E trick? (2013) by thfuran on Wednesday February 16, 2022 @08:21AM (#30359597)
You've never in your life acquired an image or text document from the internet?
Re:How can you be fooled by the U+202E trick? (2013) by jcelerier on Wednesday February 16, 2022 @09:46AM (#30360592)
when I do my OS has no trouble opening them in my image or text viewer. The issue is when I download something that should be executable, and I have to paintaskingly open a terminal, and

    cd ~/Téléchargements; chmod +x <try to remember the first letter><hit tab 15 times><miss it><go check inside the firefox download manager><restart><end up typing the whole name> 
before being able to run it.
Re:How can you be fooled by the U+202E trick? (2013) by armada651 on Wednesday February 16, 2022 @10:28AM (#30361193)
This seems like more of a UI issue than anything. Could be fixed by simply presenting the user with a prompt asking whether they want to allow this file to execute as a program if it's missing the permissions.
Re:How can you be fooled by the U+202E trick? (2013) by kazinator on Wednesday February 16, 2022 @06:12PM (#30367161)
Honoring that right-to-left reversal character is also a "UI Issue".

The Windows UI could just render that character as a tofu box, and not evoke its reversal semantics.

Re:How can you be fooled by the U+202E trick? (2013) by ajuc on Wednesday February 16, 2022 @10:33AM (#30361269)
This is bad for variety of reasons.

Consider writing a bash script that makes a subdirectory with current date if it doesn't exist, downloads url from the command line argument into that directory, changes the permissions and runs it.

Then your workflow could be:

- keep terminal open

- Alt+tab to firefox, browse, copy link to executable file

- Alt+tab to terminal, ./handle.sh <paste the link> ENTER

- Alt+tab to firefox again

- rinse and repeat

There's many benefits - you don't get thousands of files in one directory (which can lead to performance degradation and even random errors), there's little risk that you run the wrong file, you don't waste as much time.
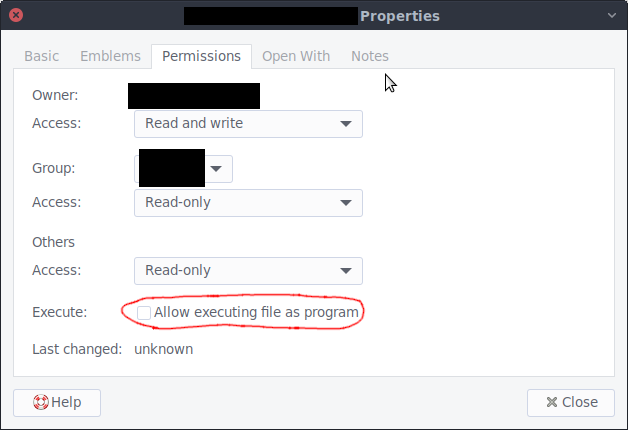
Re:How can you be fooled by the U+202E trick? (2013) by 6yyyyyy on Wednesday February 16, 2022 @12:48PM (#30363149)
No need to open a terminal

https://files.catbox.moe/tkefli.png

Re:How can you be fooled by the U+202E trick? (2013) by jcelerier on Wednesday February 16, 2022 @04:27PM (#30365940)
the idea of having to go in those damned menus one more time just to launch an app sends shivers down my spine. I already barely tolerate windows and macOS's prompts when downloading executables.
Re:How can you be fooled by the U+202E trick? (2013) by marcosdumay on Wednesday February 16, 2022 @10:43AM (#30361416)
Hum... How do you run it?

If it's from a GUI, file browsers have the capacity to that that bit too.