News for hackers. Stuff that matters.
Re:Inferring Your Mobile Phone Password via WiFi Signals by gefh on Tuesday February 14, 2017 @01:02PM (#13645563)
Holy shit. From a brief scan it looks like the paper concentrates on recovering a numeric pin, but these attacks never get worse, only better, so I assume full keyboard access is not too far off. What's the defense? Have your phone manage the passwords and unlock via fingerprint?
Re:Inferring Your Mobile Phone Password via WiFi Signals by gene-h on Tuesday February 14, 2017 @03:24PM (#13646788)
Well if one modifies the channel state information in an unpredictable manner while performing sensitive operations, it becomes very difficult to extract any information. The simplest way to do this might be to fidget. Use one hand to type and another hand to fidget with something.

A more high tech method would be to use a modulated wifi reflector that is randomly modulated.

One should also watch out for wifi hotspots with ominously pointed directional antenna

Re:Inferring Your Mobile Phone Password via WiFi Signals by danielhooper on Tuesday February 14, 2017 @02:26PM (#13646333)
The defence is definitely to not use public wifi. This technology works because they can identify small target windows (e.g. you just accessed a URL to login to your bank account) in which to make and process these measurements. Any kind of abnormal obfuscation of your device should introduce enough noise to prevent this attack from generating any meaningful data from the victim, but I'm running on assumption.
Re:Inferring Your Mobile Phone Password via WiFi Signals by zrm on Tuesday February 14, 2017 @08:03PM (#13648873)
Couldn't this work against any wifi? Impersonating a public access point gives you some extra unencrypted information so you know the server IP and can more easily infer when a password is being entered, the same things you conceal by using a VPN over public wifi.

But what stops a passive wifi observer who can guess those things or already knows them?

Re:Inferring Your Mobile Phone Password via WiFi Signals by droopybuns on Tuesday February 14, 2017 @02:45PM (#13646505)
I think this is pretty hand-wavey and requires a lot assumptions to be true.

Also: "We collected training and testing data from 10 volunteers." Not a statistically useful sample set.

Under very controlled environments, measuring signal deltas may be possible- but I would like to see sample data that suggests high success rates before I think this is worthy of concern.

Finally- Self tuning antennas are a thing. This is going to get harder over time. https://www.qualcomm.com/videos/qualcomm-rf360-dynamic-anten...

Re:Inferring Your Mobile Phone Password via WiFi Signals by zkms on Tuesday February 14, 2017 @03:59PM (#13647122)
The easiest defence is to temporarily kill all the radios (wifi, bluetooth, LTE) while someone is entering a password.
Re:Inferring Your Mobile Phone Password via WiFi Signals by frandroid on Tuesday February 14, 2017 @01:58PM (#13646083)
Or scramble the numeric keypad on every try, but that would get annoying fast.
Re:Inferring Your Mobile Phone Password via WiFi Signals by birdman3131 on Tuesday February 14, 2017 @03:10PM (#13646677)
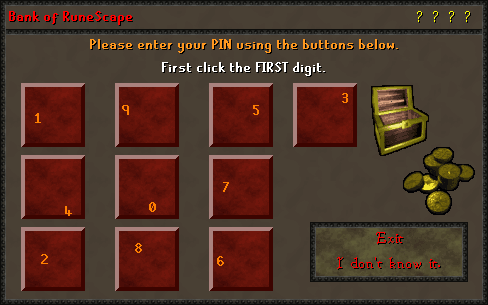
Anybody who plays Runescape will recognize this. They have a pin you can set to gain access to your in game bank. It has a fair few security features to combat keyloggers which were (and still can be) a major issue.

Some security features I can recall.

Random layout of the numbers on both the button itself and which button has which number. This is shuffled on every click.

Upon clicking all numbers and the mouse pointer vanish. This prevents screenshots taken on clicks by some keyloggers from working.

No keyboard input. Annoying but needed to combat keyloggers.

http://vignette2.wikia.nocookie.net/2007scape/images/c/c3/Ba...
Re:Inferring Your Mobile Phone Password via WiFi Signals by pmontra on Tuesday February 14, 2017 @02:41PM (#13646477)
My bank did that with a JavaScript number pad. They went back to a standard password field with the new design of the site a couple of years ago. That made me feel less safe because I understood why the were complicating the input.

Another strategy I've seen is to ask some random digits of a longer PIN, with a mask to fill out.

Re:Inferring Your Mobile Phone Password via WiFi Signals by dTal on Tuesday February 14, 2017 @08:20PM (#13648953)
Some banks (e.g. Barclays) use a card reader that generates a unique key each time. Since this also requires that you have your card to log in, it's my understanding that this offers massively improved security.
Re:Inferring Your Mobile Phone Password via WiFi Signals by adevine on Tuesday February 14, 2017 @02:17PM (#13646257)
I've seen some secure financial sites that already do that.
Re:Inferring Your Mobile Phone Password via WiFi Signals by ultrasandwich on Tuesday February 14, 2017 @02:44PM (#13646496)
Convenient option on Cyanogenmod. Been using it for about 2 years and it's surprisingly easy to get used-to.
Re:Inferring Your Mobile Phone Password via WiFi Signals by sundvor on Tuesday February 14, 2017 @10:57PM (#13649570)
Touch typing? Should present significantly different to one finger key hunting.

Fingerprints and never using public WiFi would both be good strategies. (I use my fingerprint to log into my banking app when on mobile.)

Re:Inferring Your Mobile Phone Password via WiFi Signals by Piskvorrr on Wednesday February 15, 2017 @08:01AM (#13651671)
Touch typing on a flat, featureless surface? Best of luck with that. I tried, and tended to drift off-center within a few tens of keystrokes. The F and J nubs on physical keyboard are there for Good Reasons - but even without, feeling where exactly you are striking the key (center or corner) gives you feedback to reposition. Touchscreen gives you nothing.
Re:Inferring Your Mobile Phone Password via WiFi Signals by sundvor on Monday February 20, 2017 @07:00AM (#13686558)
Ah, you're completely right - for some reason I had it in my head it was about laptops. Even the title was a big reveal.. Oh well.
Re:Inferring Your Mobile Phone Password via WiFi Signals by djrogers on Tuesday February 14, 2017 @01:55PM (#13646061)
> Have your phone manage the passwords and unlock via fingerprint?

Yes, that would defeat this particular attack.

Re:Inferring Your Mobile Phone Password via WiFi Signals by mratzloff on Tuesday February 14, 2017 @02:15PM (#13646242)
Never use public wifi. I don't.
Re:Inferring Your Mobile Phone Password via WiFi Signals by cortesoft on Tuesday February 14, 2017 @02:19PM (#13646285)
That is a large cost to pay.
Re:Inferring Your Mobile Phone Password via WiFi Signals by libeclipse on Tuesday February 14, 2017 @02:24PM (#13646319)
It isn't really. Mobile data is a must from a security point of view. Combine it with a VPN and you have your out and about internet access sorted.
Re:Inferring Your Mobile Phone Password via WiFi Signals by erikpukinskis on Tuesday February 14, 2017 @03:32PM (#13646855)
How is a VPN on mobile data safer than a VPN on public internet?

Also, what safety does a VPN add if you are already using https?

Re:Inferring Your Mobile Phone Password via WiFi Signals by et-al on Tuesday February 14, 2017 @03:40PM (#13646938)
The process of connecting to public wifi is risk. Most public wifi networks have a landing page that you have to click through before proceeding/granting you access. That page could have a malicious script.

Last year after a trip in Germany, my older iPhone had a random password saved in Safari settings. On top of that, every time I tried to delete the password, it would reappear when I went back (iCloud sync was off, etc.). I don't remember browsing anything out of the ordinary, but did connect to a bunch of public wifi spots. Here's to hoping it was just a really persistent ad-tracking method.

Re:Inferring Your Mobile Phone Password via WiFi Signals by erikpukinskis on Wednesday February 15, 2017 @01:04PM (#13653967)
Do you browse the web expecting sites not to have malicious scripts?
Re:Inferring Your Mobile Phone Password via WiFi Signals by et-al on Wednesday February 15, 2017 @01:30PM (#13654177)
For my use case, I hope so.

I generally don't browse on my phone, so if I'm opening up Safari on a public network, it's to a known site or bookmark to quickly reference something (e.g. transit map, exchange rate). It's totally possible an ad on the NYT or Bloomberg has some malicious Javascript, but currently I'm naively assuming otherwise.

Also, I think many people on their phones will connect to a public hotspot just to check Facebook / Instagram / Snapchat these days and not much else.

Re:Inferring Your Mobile Phone Password via WiFi Signals by mhluongo on Tuesday February 14, 2017 @03:41PM (#13646947)
For the second one, I believe you can still ID what sites a user is likely using if you're in the middle, regardless of https, via eg reverse IP lookups- just not what they're sending to that site. A VPN covers that.
Re:Inferring Your Mobile Phone Password via WiFi Signals by jimmaswell on Tuesday February 14, 2017 @02:57PM (#13646585)
Mobile data is often slow or unavailable depending on what room of a building you're in etc. outside of cities.
Re:Inferring Your Mobile Phone Password via WiFi Signals by cortesoft on Tuesday February 14, 2017 @06:55PM (#13648476)
Mobile data is expensive and slower than WIFI. There is a reason people connect to a WIFI with their phones.
Re:Inferring Your Mobile Phone Password via WiFi Signals by vardump on Wednesday February 15, 2017 @05:27AM (#13650973)
In many (most?) countries mobile data is cheaper than wired connections, but obviously with worse latency.

Slower too maybe, but we're long past the point it really matters, except for latency sensitive applications. 50+ Mbps is just plenty for most applications.

Only real need of wifi to save some battery power and maybe to get better latency and jitter for VoIP and interactive applications.

AFAIK, US and UK are still pretty bad. I guess they have to limit bandwidth and data volume to be able to, ahem, listen to their customer.

Re:Inferring Your Mobile Phone Password via WiFi Signals by kwhitefoot on Wednesday February 15, 2017 @11:47AM (#13653331)
> mobile data is cheaper than wired connections

In which countries is that true? Certainly not any that I visit.

Re:Inferring Your Mobile Phone Password via WiFi Signals by flukus on Tuesday February 14, 2017 @06:31PM (#13648331)
Is it really? The biggest bandwidth user is cloud apps and if you care about privacy you wouldn't be using them anyway.
Re:Inferring Your Mobile Phone Password via WiFi Signals by josu on Tuesday February 14, 2017 @02:28PM (#13646349)
As far as I understood, this attack vector has nothing to do with using public wifi.
Re:Inferring Your Mobile Phone Password via WiFi Signals by gene-h on Tuesday February 14, 2017 @03:13PM (#13646695)
The attack presented in this paper relies on the user connecting to the wifi hotspot. This is necessary so that they can figure when a sensitive operation is happening.

Without this information, it is difficult to determine if the user is inputting a password. In addition, if we know the user is using the bank of america app, and we know that the app uses a specific key lay out, it becomes a lot easier to figure out what keys they are pressing.

There is no reason that the other technique they discussed, which does not require the target to connect to a specific wifi hotspot, could not be improved though.

Re:Inferring Your Mobile Phone Password via WiFi Signals by calebm on Tuesday February 14, 2017 @03:46PM (#13646983)
If you want to be really secure, just never use the internet.