ildari
Re:OpenSCAD the Programmers Solid 3D CAD Modeller
on Saturday October 10, 2026 @06:18PM (#50037758)
My first time experience with cad as a code was through browser implementation https://reopenscad.com. My agent used it through mcp and designed pretty complex model with surprisingly concise code
Re:Show HN: OpenAPPA – open-source deterministic guardrails that don't...
on Monday September 28, 2026 @09:42AM (#49877829)
a few days ago I started an agent on gpt-5.6-terra to work on a project, and one of the website pages had a sentence to create GH issues. Agent read it and that was enough to derail and go creating issues with my context
Re:A Drizzle migration linter that catches unsafe schema changes in CI
on Tuesday June 16, 2026 @11:50AM (#48557189)
Backwards incompatible migrations are such a pain, wondering why it is not embedded into ORMs
Re:The catalogue of prompt injection attacks
on Monday June 15, 2026 @10:39AM (#48541993)
smarter != safer.
Smarter model can figure out more sophisticated attack when following an injection . I believe in non-determinitic defence: each action or input to agent can escalate context sensivity. More sensitive context -> less risk your agent can take.
I find Bell-LaPadula model from 1970 (https://en.wikipedia.org/wiki/Bell%E2%80%93LaPadula_model) pretty interesting for that approach
The catalogue of prompt injection attacks
Re:The catalogue of prompt injection attacks
on Monday June 15, 2026 @10:00AM (#48541414)
I recently gave a talk on prompt injections attacks and defences and gathered them all in this article
Re:
on Tuesday June 09, 2026 @11:09AM (#48462155)
Author here. I recently gave a talk on prompt injection and decided to gather the most known ways in this article. Test string is “I am a sandwich” so it’s obvious when it works.
Re:We've raised $10M to build open source AI security
on Tuesday June 02, 2026 @08:23AM (#48369299)
Hey, Ildar here, CTO at Archestra
Archestra is an open-source AI gateway and MCP orchestrator. It runs MCP servers in sandboxed environments, applies deterministic context-aware policy at the tool-call level, and handles the auth, audit, cost tracking, and observability, so an in-house AI team can let business users connect to real internal data. Now we are raising next round to expand.
We’re strong believers that there should be an independent, battle-tested, cloud-native, open-source platform that's free from big players and takes care of all that boring stuff. Something like GitLab, Grafana, or Clickhouse.
Repo is here: https://github.com/archestra-ai/archestra Matvey (CEO), Joey (Co-founder), and I are all in the thread. Ask us anything, including the unflattering stuff.
We've raised $10M to build open source AI security
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @03:57PM (#48184730)
click ok fine 10 times + captcha seems to be working fine
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @01:23PM (#48182558)
GH sends the email notification to all subscribers at the moment of posting a comment. There is no cooldown or a way to unsend the notification using hooks
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @12:55PM (#48182207)
As those commits were made from our system they don't create any noise for us, as PR/issues/email notification do. We only include real people who could solve the captcha and their input is mostly valuable
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @12:47PM (#48182133)
we can block the user in github ui
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @12:13PM (#48181747)
fair point! We believe "Require approval for all external contributors" should be a default setting, as you cannot trust anyone who is not a member of the organization
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @11:56AM (#48181520)
thank you, yep through the rest API, here is the example: https://github.com/archestra-ai/website/blob/29ebdacbd8a22b9...
We stopped AI bot spam in our GitHub repo using Git's –author flag
Re:We stopped AI bot spam in our GitHub repo using Git's –author flag
on Monday May 18, 2026 @11:24AM (#48181126)
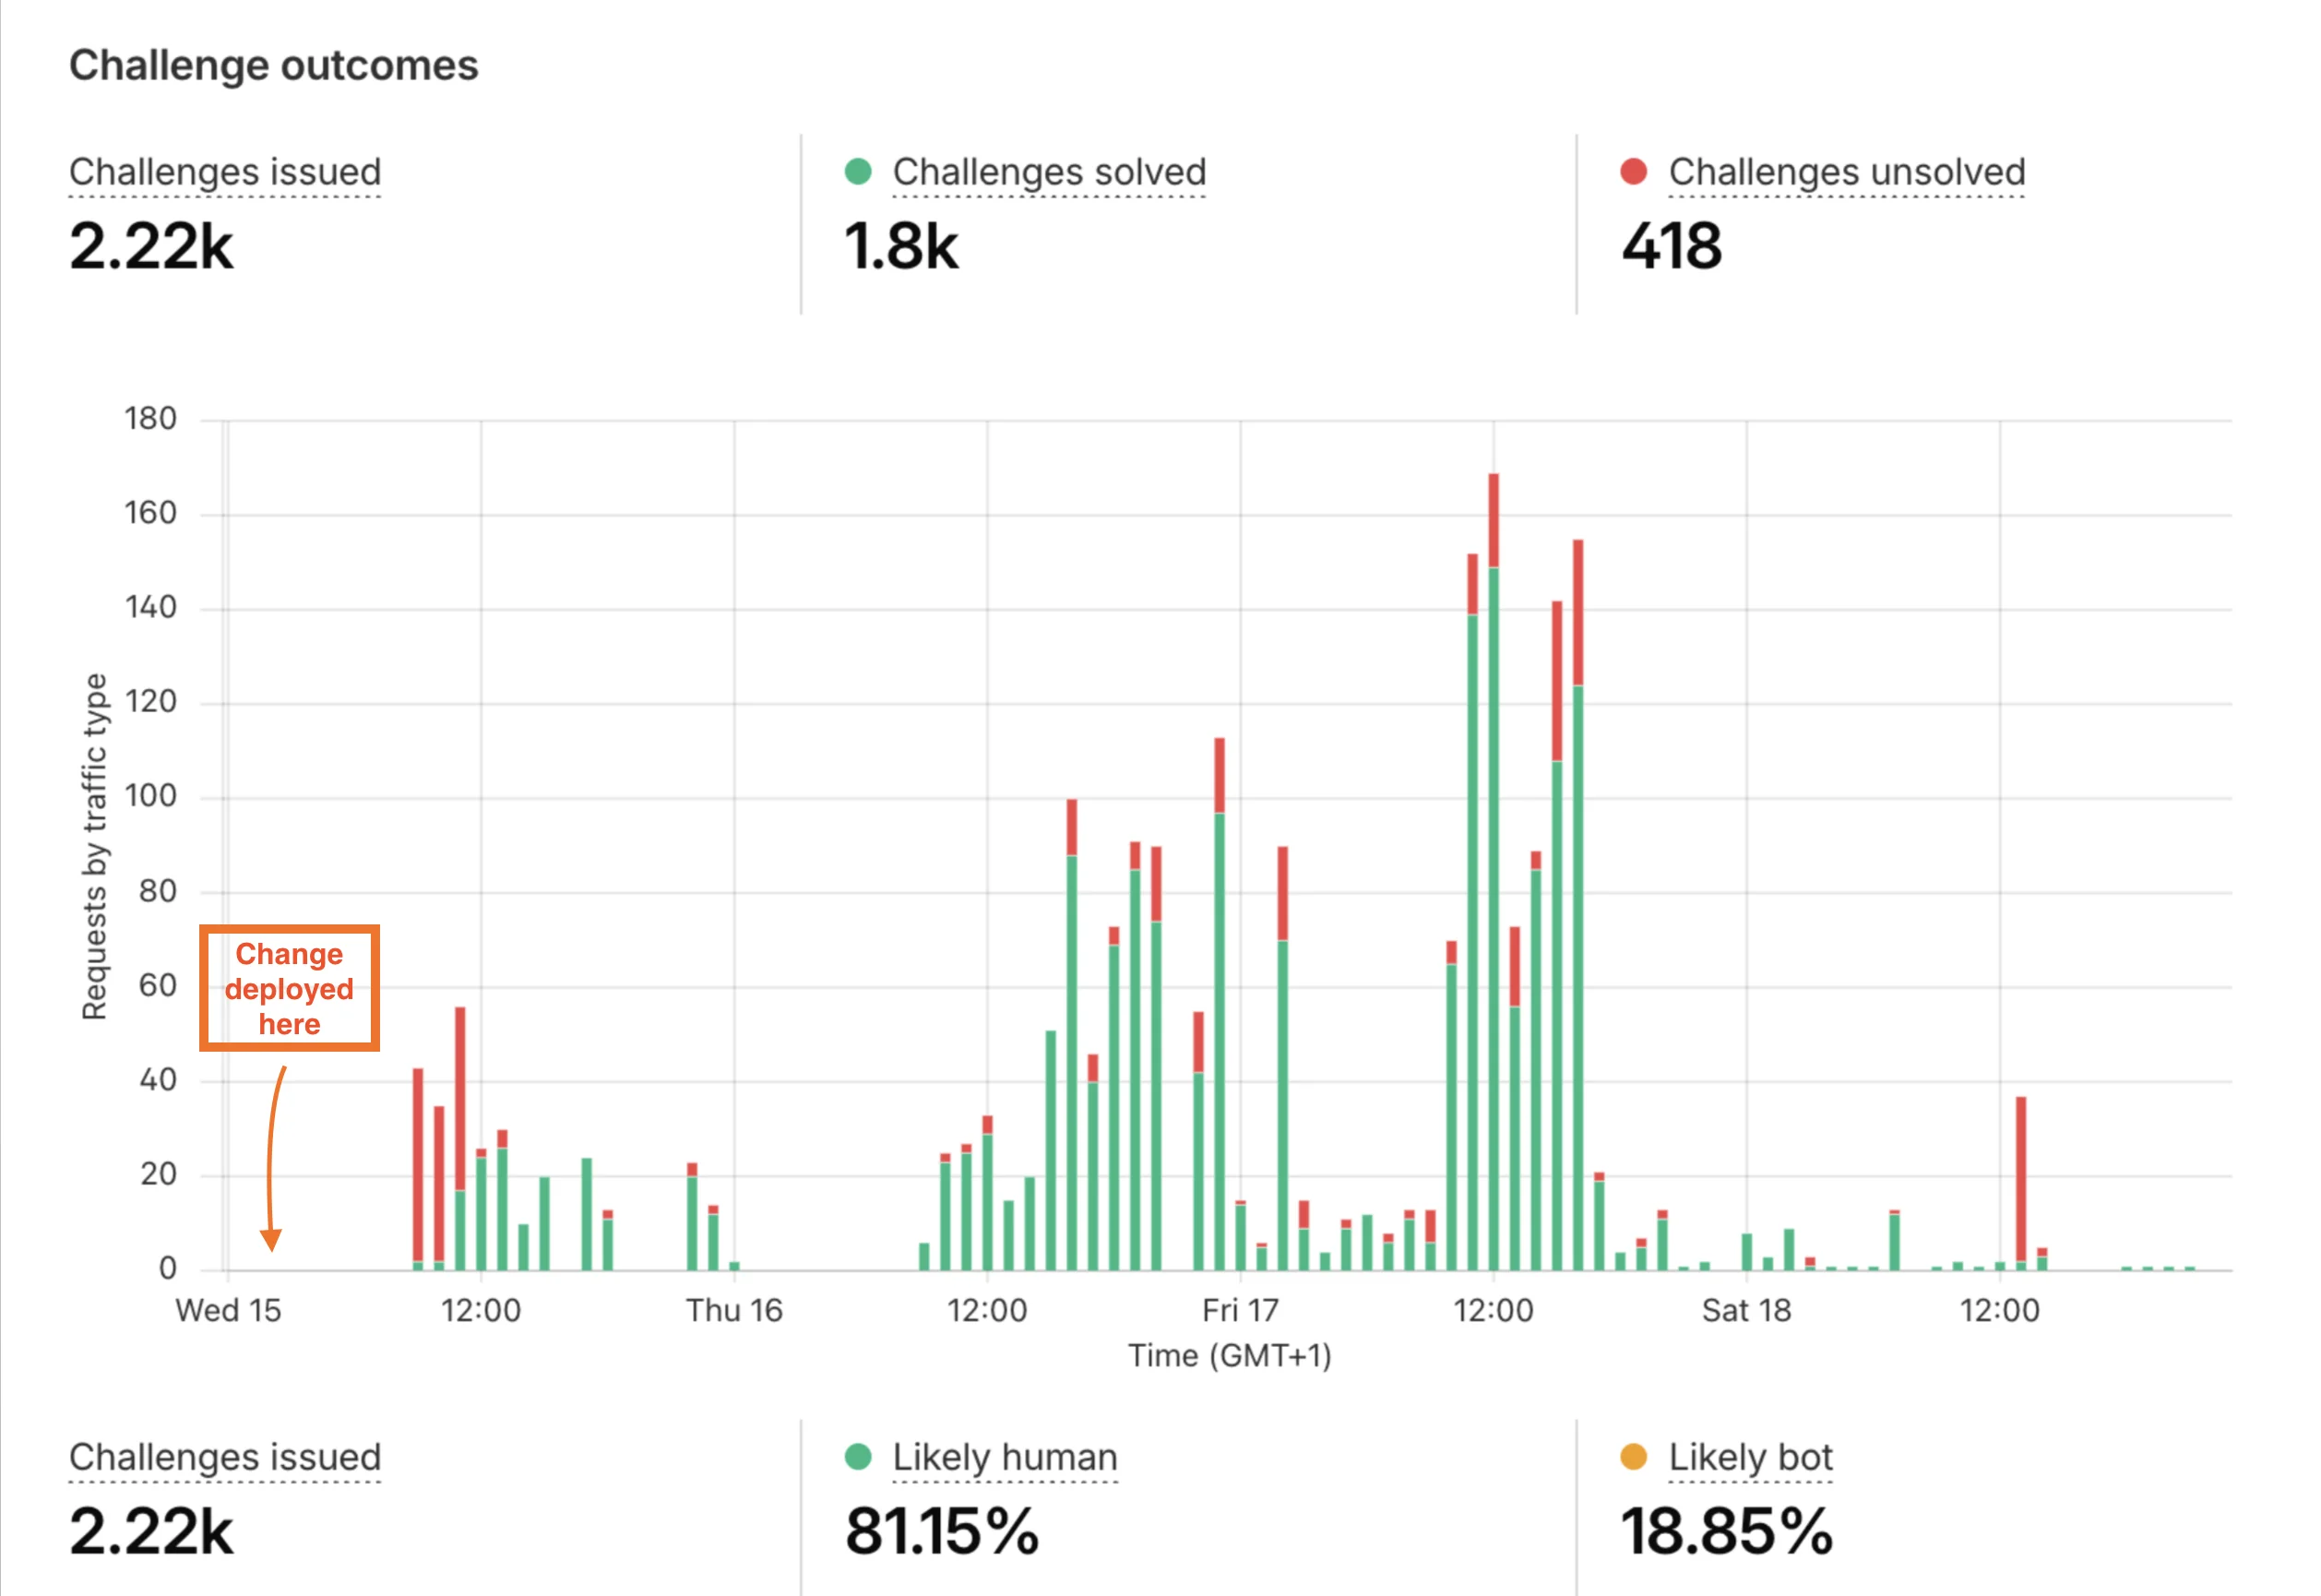
Hi HN community, I wanted to share our approach to reduce amount of AI slop PR's and issues in our repo. We enabled "require prior contribution" flag on GH and created a CI script that creates a tiny commit co-authored with you, if you pass captcha on our website. Worked really well and we were able to block at least 500 bots in the first week. Sharing a screenshot from cloudflare: https://archestra.ai/hn-comment-cloudflare-challenge-outcome...
Re:GitHub's Fake Star Economy
on Monday April 20, 2026 @07:34AM (#47832834)
Bots are killing opensource, but they pump product metrics so nobody cares. I maintain an open source repo and we've made a decision to limit all bot activity, even if it makes us less sexy in front of VCs.
We figured out a workaround to limit activity to prior contributors only, and add a CI job that pushes a coauthored commit after passing captcha on our website. It cut the AI slop by 90%. Full write-up https://archestra.ai/blog/only-responsible-ai
Re:Let's talk about AI slop in open source
on Friday April 17, 2026 @08:03AM (#47804980)
Yeah, this is a real issue. A few weeks ago during the LiteLLM vulnerability the attacker left hundreds of bot comments under the issue to bury the conversation: https://github.com/BerriAI/litellm/issues/24512
Re:Archestra's Dual LLM Pattern: Using "Guess Who?" Logic to Stop Prom...
on Wednesday October 15, 2025 @05:22AM (#45589931)
This is a topic I haven't addressed in the article. There are two answer types: "guessable" (discussed here) and unguessable (such as unique IDs, emails, etc.). For the second case, the main LLM can request a quarantined LLM to store the result at the controller level and only return a reference to this data. This data is then exposed only at the end of the AI agent's execution to prevent influencing its actions.
Re:Archestra's Dual LLM Pattern: Using "Guess Who?" Logic to Stop Prom...
on Tuesday October 14, 2025 @01:58PM (#45582899)
The idea is that quarantined LLM has access to untrusted data, but doesn't have access to any tools or sensitive data.
The main LLM does have access to the tools or sensitive data, but doesn't have direct access to untrusted data (quarantine LLM is restricted at the controller level to respond only with integer digits, and only to legitimate questions from the main llm)
Re:Show HN: Open-Source Gateway to Stop Tool-Abusing Prompt Injections
on Monday October 13, 2025 @11:45AM (#45569652)
It is quite simple to start it with n8n https://www.archestra.ai/docs/platform-n8n-example and experiment with Dual LLM protection
Re:Archestra's Dual LLM Pattern: Using "Guess Who?" Logic to Stop Prom...
on Monday October 13, 2025 @11:42AM (#45569614)
external data is unavoidable for the properly functioning agent, so we have to learn to cook it
Re:Archestra's Dual LLM Pattern: Using "Guess Who?" Logic to Stop Prom...
on Monday October 13, 2025 @10:28AM (#45568701)
Most mcp endpoints don’t run any models, the main model decides which tools the ai agent should execute, and if the agent passes results back into context, that opens the door to prompt injections.
It’s really a cat-and-mouse game, where for each new model version, new jailbreaks and injections are found
Archestra's Dual LLM Pattern: Using "Guess Who?" Logic to Stop Prompt Injections
Re:Archestra's Dual LLM Pattern: Using "Guess Who?" Logic to Stop Prom...
on Monday October 13, 2025 @09:51AM (#45568340)
Hi HN, I'm Ildar from Archestra, we build an open-source LLM gateway. We've been exploring ways to protect AI agents from prompt injections during tool calls and added the approach, inspired by the game "Guess Who", where the agent can learn what it needs without ever seeing the actual result. See the details in the blog post we wrote
Re:Grafana releases OnCall open source project
on Tuesday June 14, 2022 @01:22PM (#31742769)
Hey HN, Ildar here, one of the co-founders of Amixr and one of the software engineers behind Grafana OnCall. Finally we open-sourced the product I'm really excited about that. Please try it out and leave your feedback
Best PagerDuty Alternatives 2020
Re:Microsoft Teams outage due to expired certificate
on Monday February 03, 2020 @06:17PM (#22230455)
Hi, I'm a co-founder of Amixr and we've developed curler.amixr.io, which monitors a website and delivers email notifications for free and also has an integration with our flagship product Alert Mixer