Re:Problems with the Golang runtime and toolchain
by vorador on Tuesday December 30, 2014 @03:25PM
(#8816545)
This is only remotely related, but the golang maintainers have refused to include support for the (insecure, but used on some legacy systems) ECB encryption mode, because it's insecure: http://code.google.com/p/go/issues/detail?id=5597 .
[ Parent
| on HN ]
Re:Problems with the Golang runtime and toolchain
by pa7ch on Tuesday December 30, 2014 @03:34PM
(#8816586)
Although they don't have an ECB func, You can trivially implement it from their AES library. I imagine the thinking goes something like, if you don't know enough to write a couple lines to implement ECB, you probably shouldn't be using it. It really doesn't take a deep understanding of crypto understand ECB.
ECB is the simplest AES mode, you just encrypt each block of your message using the same key. Here is an image of a penguin encrypted with AES-ECB:http://upload.wikimedia.org/wikipedia/commons/f/f0/Tux_ecb.j...
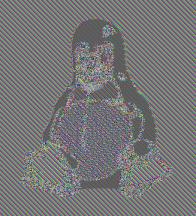
Do you see the problem?
Re:Problems with the Golang runtime and toolchain
by georgemcbay on Tuesday December 30, 2014 @05:00PM
(#8816987)
Yeah, this. Didn't realize people actually saw this as an issue worthy of worrying about.
The Matasano Crypto Challenges I did way back when were in Go and the ones involving ECB were just done as for loops over the standard library AES Decrypt/Encrypt methods, something like this:
  for i := 0; i < blockCount; i++ {
    start := i * blockLength
    end := start + blockLength
    aes.Decrypt(decryptBuffer, input[start:end])
    output = append(output, decryptBuffer)
  }