The only reasonable understanding is that these protocols are for for publishing to the public. It is not possible to reliably retract anything published to thousands of other peoples' computers. We used to try to teach people that the internet is forever, and that's even more true with federated protocols. That doesn't make them a bad idea.
I understand why people want to be able to delete things from the internet, but it doesn't work that way. It has never worked that way. It can't work that way unless every computer is locked down to running remotely attested government-approved software, and that's obviously worse.
It was already wayyy too complex. And this? Yeah, they (you? sorry) really need to just give it up.
Permissioned / private data is non negotiable for any social media tech trying to gain mass adoption.
The entire point of services like Bluesky and Twitter is broadcasting your activity out to the internet for anyone to see (which of, course, is technically little-or-no different from "grab")
You seem rather confused. I do not work for Bluesky. I am an independent developer building completely separate applications on ATProto.
Also, ATProto can be much more than social media tech, more like a plug-n-play distributed system
Or more precisely, it might. We now have a better idea of how people actually behave and it's not in accordance with "the internet is forever," and I have no interest in blaming them for 'human nature' in that way.
And it's all still dangerous. Again, I know the internet is forever, but someone else posting about ME might not.
This isn't an individual thing. It's "ecological."
And I have no interest in making Big Brother THAT MUCH EASIER to build.
It does seem like fewer people are posting personal content that way lately. Perhaps most people are better off sharing things one to one, or in small groups that are meant to stay private. That doesn't make it bad for the more public formats to exist; they're just not for everyone.
The internet is forever, don't want it propagated? Don't post it.
> Well-behaved servers will honor delete requests, but the protocol doesn't mandate it.
Probably because they cannot truly guarantee or enforce it.
Don't use it if you don't like it. Some of us like the strong identity and content verification.
Proverbial Big Brother ALSO likes "strong identity and content verification."
I'm also putting forth the idea that the ATProto thing for social media makes us marginally less safe, due to its technical "centralization via confirmation" of the data it "broadcasts."
Except that the design of Bluesky severely increases the possibility of your data getting out of your control. And I can hear the immediate responses of "oh if you didn't want it public, don't post it," but as should be frightfully obvious -- not everyone thinks like that.
That doesn't mean that there is no danger of people having "buyer's" regret later, or more importantly that there are issues beyond the individuals.
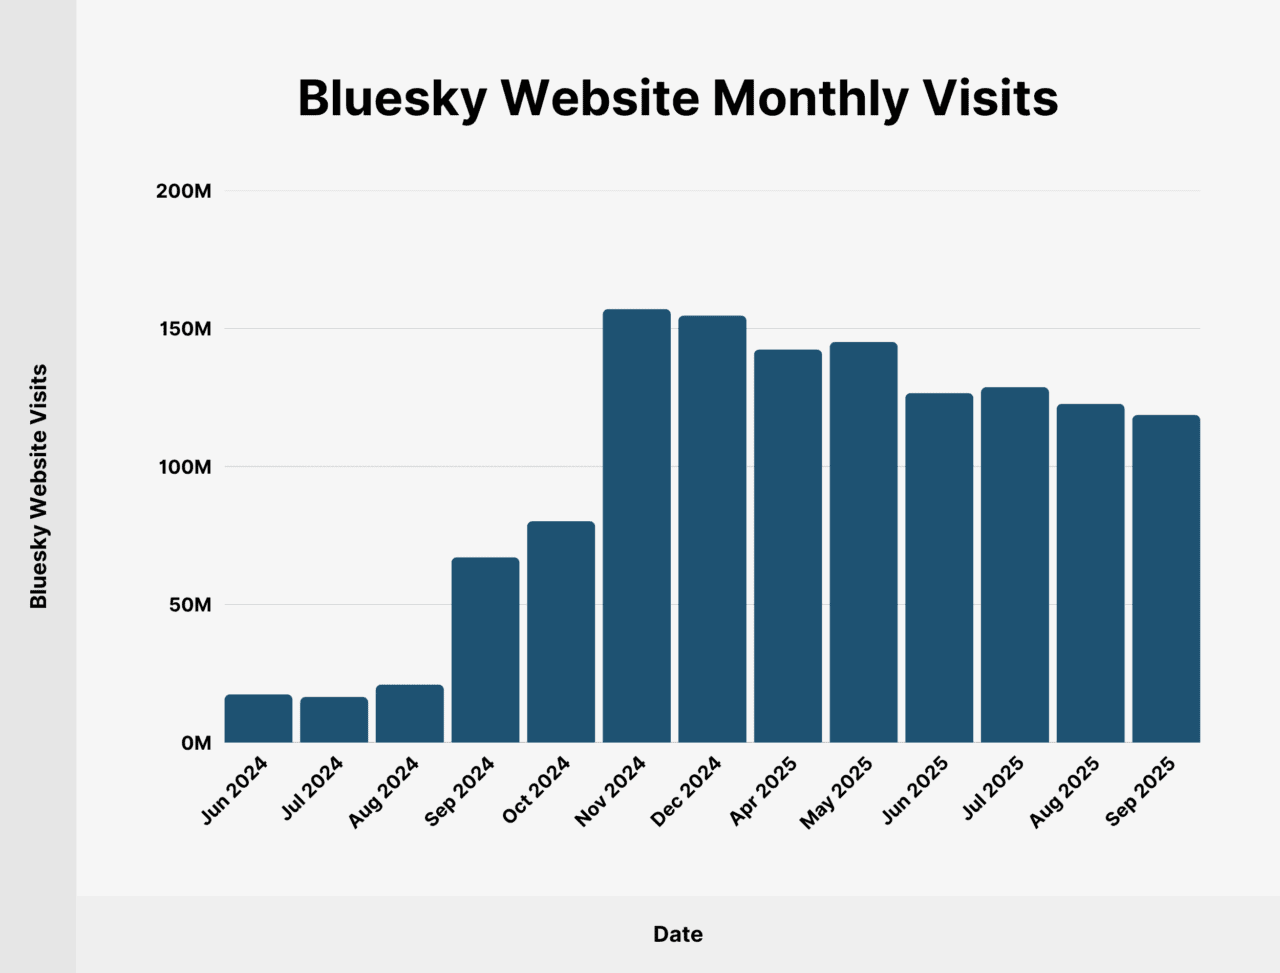
This is also visible in your stats if you extend the time window. They had a peak in 2024 and are pretty much declining month to month ever since.

The entire point of a platform like Twitter / Bluesky is reach, not privacy.
Posts and discussions there are meant to be public, and highly visible.
It's not that people don't care. It's that this is not what the platform is for.
What's important for a platform like that is not even anonymity, but functional pseudonymity.
And that thing is on its way to the effectively outlawed with the push for "age verification".
People do notice it and leave [1], but at some point, there might be no place to go to.
[1] https://www.reddit.com/r/privacy/comments/1rmlzhy/welp_goodb...
But no, we're way past "if you don't want it public don't post it." and then wiping our hands and being done. We need to think in a policy kind of way on this.
And again, things are already dangerous -- but ATProto makes them more dangerous. It's something like a chain-of-custody thing. I think the world is collectively safer where the gathering of data like this is less reliable and less verifiable.
ATProto's model makes the building of the proverbial evil Big Brother panopticon thing a LOT easier.
twitter/x/bluesky - a big tech company owns your data
mastodon - a grassroots community organization owns your data
zulip - someone you've met personally owns the data
your blog - you own the data
(and yes these are a bit of a category error, but to achieve privacy maybe we should broaden the category and sacrifice reach)
Because you have "possesses" (which can be anyone) vs. "controls?"
Twitter - single point of big company external control
Mastodon - One or multiple unverifiable fallible likely grassroots, points of external control
Bluesky - Once out, merely the illusion of control, because your data is out there, verifiable?.
there is just no way to police what happens to data that is broadcast, which doesn't remove control away from the reader
it's annoying because in the abstract it's something everybody has the potential to need and need badly, but if you're afraid to put something out there to your name/pseudonym you really shouldn't
Which is to say, it provides a more robust model for your (true) information and data to be exploited by others than even the Twitter model.
The Mastodon-slash-email model that relies on individual servers is better because decentralization is safer -- Those models bear more genuine "ability to delete" and more "plausible deniability."