Re:Partial password usability sucks
by NotAnEconomist on Wednesday March 06, 2019 @05:32PM
(#19323608)
Advice and tactics for passwords have been bad for a long time, perhaps even comically so:
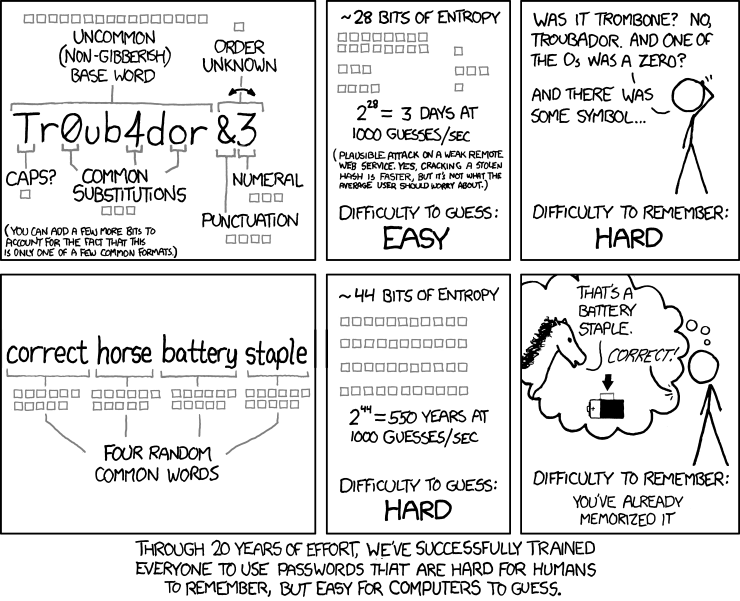
I agree, and a concise response to this article can pretty much be summed up as "Don't roll your own security" for... the fun of it I suppose, I wanted to take a swing at one particularly (IMO) good tear down of why it's stupid for technical reasons, but simply rubber stamping "Don't roll your own security" is pretty acceptable on any of these proposals.
This stuff is complicated, if you're a professional at it good on you, it's a tough job, otherwise... just listen to the professionals/best practices and don't feel the urge to be creative, you'll probably break something. It is possible that everyone is wrong, but it's unlikely... and when everyone is wrong (for example Dual_EC_DRBG) if you're using that system it'll be hard not to be aware of the issue when it comes to light.
A password has an entropy n, a higher n yields more security but comes at a cost in terms of memory power, I think it's reasonable to state that very high entropy passwords exhaust our memory quite quickly which is why password reuse is so common, this particular authentication is requiring the user to have a high entropy password n, and then is reducing it to an entropy m where m is at most as large as n (usually much smaller) and using that for authentication.
We, users and tech people, don't care about the cost to transmit bits over the wire or the cost to verify those bits on the far end (in this scenario) we care about the cost on the user's memory more than anything so why are we optimizing this puzzle to be least efficient for our most valuable resource.
When I first read this article I thought this practice was silly, now it strikes me as stupid... it is a transformation that simply discards some of the potential security of the system for no reason.
(Also, banks love ease of use, which is why up here in Canada they love to send out password dongles to customers that make it even easier to log in to a site than this while still requiring possession of a physical thing - and many of those dongles require additional authentication to activate whenever using, though not all)