Re:Is My Credit Card Stolen? (A ruse to educate people about...
by ROFISH on Thursday April 22, 2010 @09:14PM
(#1286923)
You know what, this is a phisher's dream. Even if we could trust this website for not saving the data, the connection is a regular non-secure connection, so all somebody would have to do is catch some open wireless connections or similar.
[ Parent
| on HN ]
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by AngryParsley on Thursday April 22, 2010 @09:21PM
(#1286931)
View the HTML source. The credit card inputs aren't part of the form. They're never sent across the wire.
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by carbocation on Thursday April 22, 2010 @10:30PM
(#1287064)
Perhaps a keylogger's dream, but then I suppose you would have two problems. And regex would not be one of them.
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by rlpb on Thursday April 22, 2010 @10:18PM
(#1287037)
This doesn't matter. If the connection is intercepted, the credit card inputs suddenly can be part of the form.
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by AngryParsley on Thursday April 22, 2010 @11:19PM
(#1287141)
That's true for any non-https site. They could inject stuff into wellsfargo.com or whatever.
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by arnoooooo on Friday April 23, 2010 @03:32AM
(#1287529)
Another way this could be a good scheme is if people trust it and start sending it as a way to educate people, and when it starts getting momentum, it is changed and does start recording numbers.
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by pquerna on Thursday April 22, 2010 @09:17PM
(#1286925)
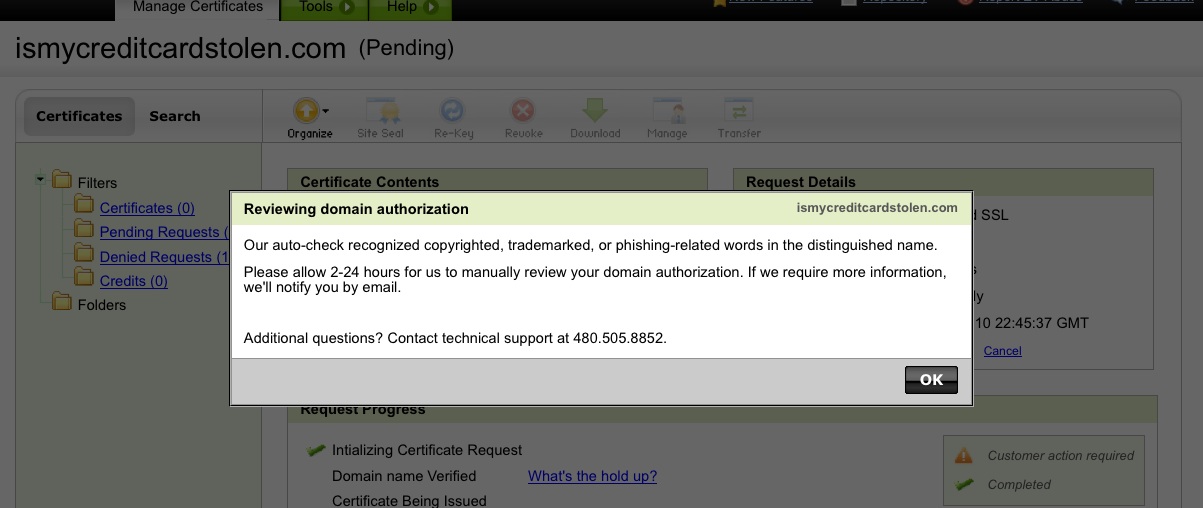
we have applied for an SSL certificate, from both GoDaddy and Comodo.
they are both 'pending', since apparently, having 'credit card' in your domain is suspicious: http://ismycreditcardstolen.com/anti-phishing.jpg
Re:Is My Credit Card Stolen? (A ruse to educate people about...
by rlpb on Thursday April 22, 2010 @10:19PM
(#1287039)
I'm not convinced that this will help so much here. Assuming that victims won't be checking for SSL, getting someone to an insecure copy of the site will do. I don't see how this would be your problem, though.
Security is a strange beast.