Dentrax
Re:Windows Bluescreen and Boot Loops (update: caused by a Crowdstrike ...
on Friday July 19, 2024 @05:53AM (#41004289)
I'm just curious, don't they have something like "gradual rollout" to update their app? They just bulk-update simultaneously across entire agents? No way. Something is a bit off for me. But there are good lessons to learn for sure.
Show HN: Falco-GPT: AI-generated security remediations for Falco audit events
Re:Show HN: I created Prometheus Exporter to monitor my xDSL Modem (On...
on Friday March 17, 2023 @03:45PM (#35201893)
Show HN: I created Prometheus Exporter to monitor my xDSL Modem (OnCall enabled)
Re:Pirate Weather: A Free, Open, and Documented Forecast API
on Wednesday January 11, 2023 @06:26AM (#34337310)
This is really cool! Can't wait to try. But I'm getting: "Exceeded daily email limit." during sign-up.
Syzbot dashboard: continuously fuzzes kernel and automatically reports bugs
KubeCon and CloudNativeCon Europe 2022 YouTube Playlist
BPF ring buffer: usage scenarios, core design and program examples (2020)
Show HN: Cosigneth: Container Image Signing and Verifying on Ethereum [Testnet]
Show HN: Build and push container images without Docker Daemon based on BuildKit
Start working with container images on macOS without requiring a Docker
Re:Ask HN: Firefox connection problems after enabling DoH?
on Thursday January 13, 2022 @04:18AM (#29918554)
It worked, thanks! How can we check the Firefox's logs?
Show HN: Manage Kubernetes Admission Webhook's Certificates with Cert-Manager
Expose Traefik with K3s to the Internet
Secure Open Source Rewards
Hardening ELF binaries using Relocation Read-Only (2019)
Roles and Benefits for SBOM Across the Supply Chain (2019) [pdf]
Protect your open source project from supply chain attacks
OSV – Open-Source Vulnerabilities
Show HN: Kink – Run KinD clusters as a pod in Kubernetes
Postmortem Culture: Learning from Failure
Mapping CNCF Software Supply Chain Best Practices to SLSA Levels
Implement kernel audit container identifier
Show HN: Created our first space mobile game (teaser) – made with Godot Engine
Everything you should know about certificates and PKI
Re:Show HN: I implemented Tilde – Operator for Go Compiler after month...
on Monday June 21, 2021 @09:18AM (#27578839)
Hey! This is my first attempt to learning of the contribution to Go Compiler. I just wanted to write a blog post about the journey.
Your feedbacks are valuable! Thanks!
If you do not use Medium, you can read the blog on the repository: https://github.com/Dentrax/go-tilde-operator/
Find the issue proposal: https://github.com/golang/go/issues/46847 Find the implementation PR: https://github.com/golang/go/pull/46848
Show HN: I implemented Tilde – Operator for Go Compiler after months of research
Re:Show HN: Cocert: split your private keys securely amongst untrusted...
on Wednesday May 26, 2021 @03:03AM (#27287299)
That's so cool! If I knew this, I could get some use-case scenario inspirations. But still, you are able to sign your content of diaries with the cocert.
Re:Show HN: Cocert: split your private keys securely amongst untrusted...
on Wednesday May 26, 2021 @03:01AM (#27287287)
Actually, we store the passwords inside the PEM file itself, which is encrypted by TUF [0].
> If you can store the password securely can you not then also store the private keys securely?
You don't have to store the private keys securely. On the contrary, you can store your private keys publicly, if the decryption password strong enough.
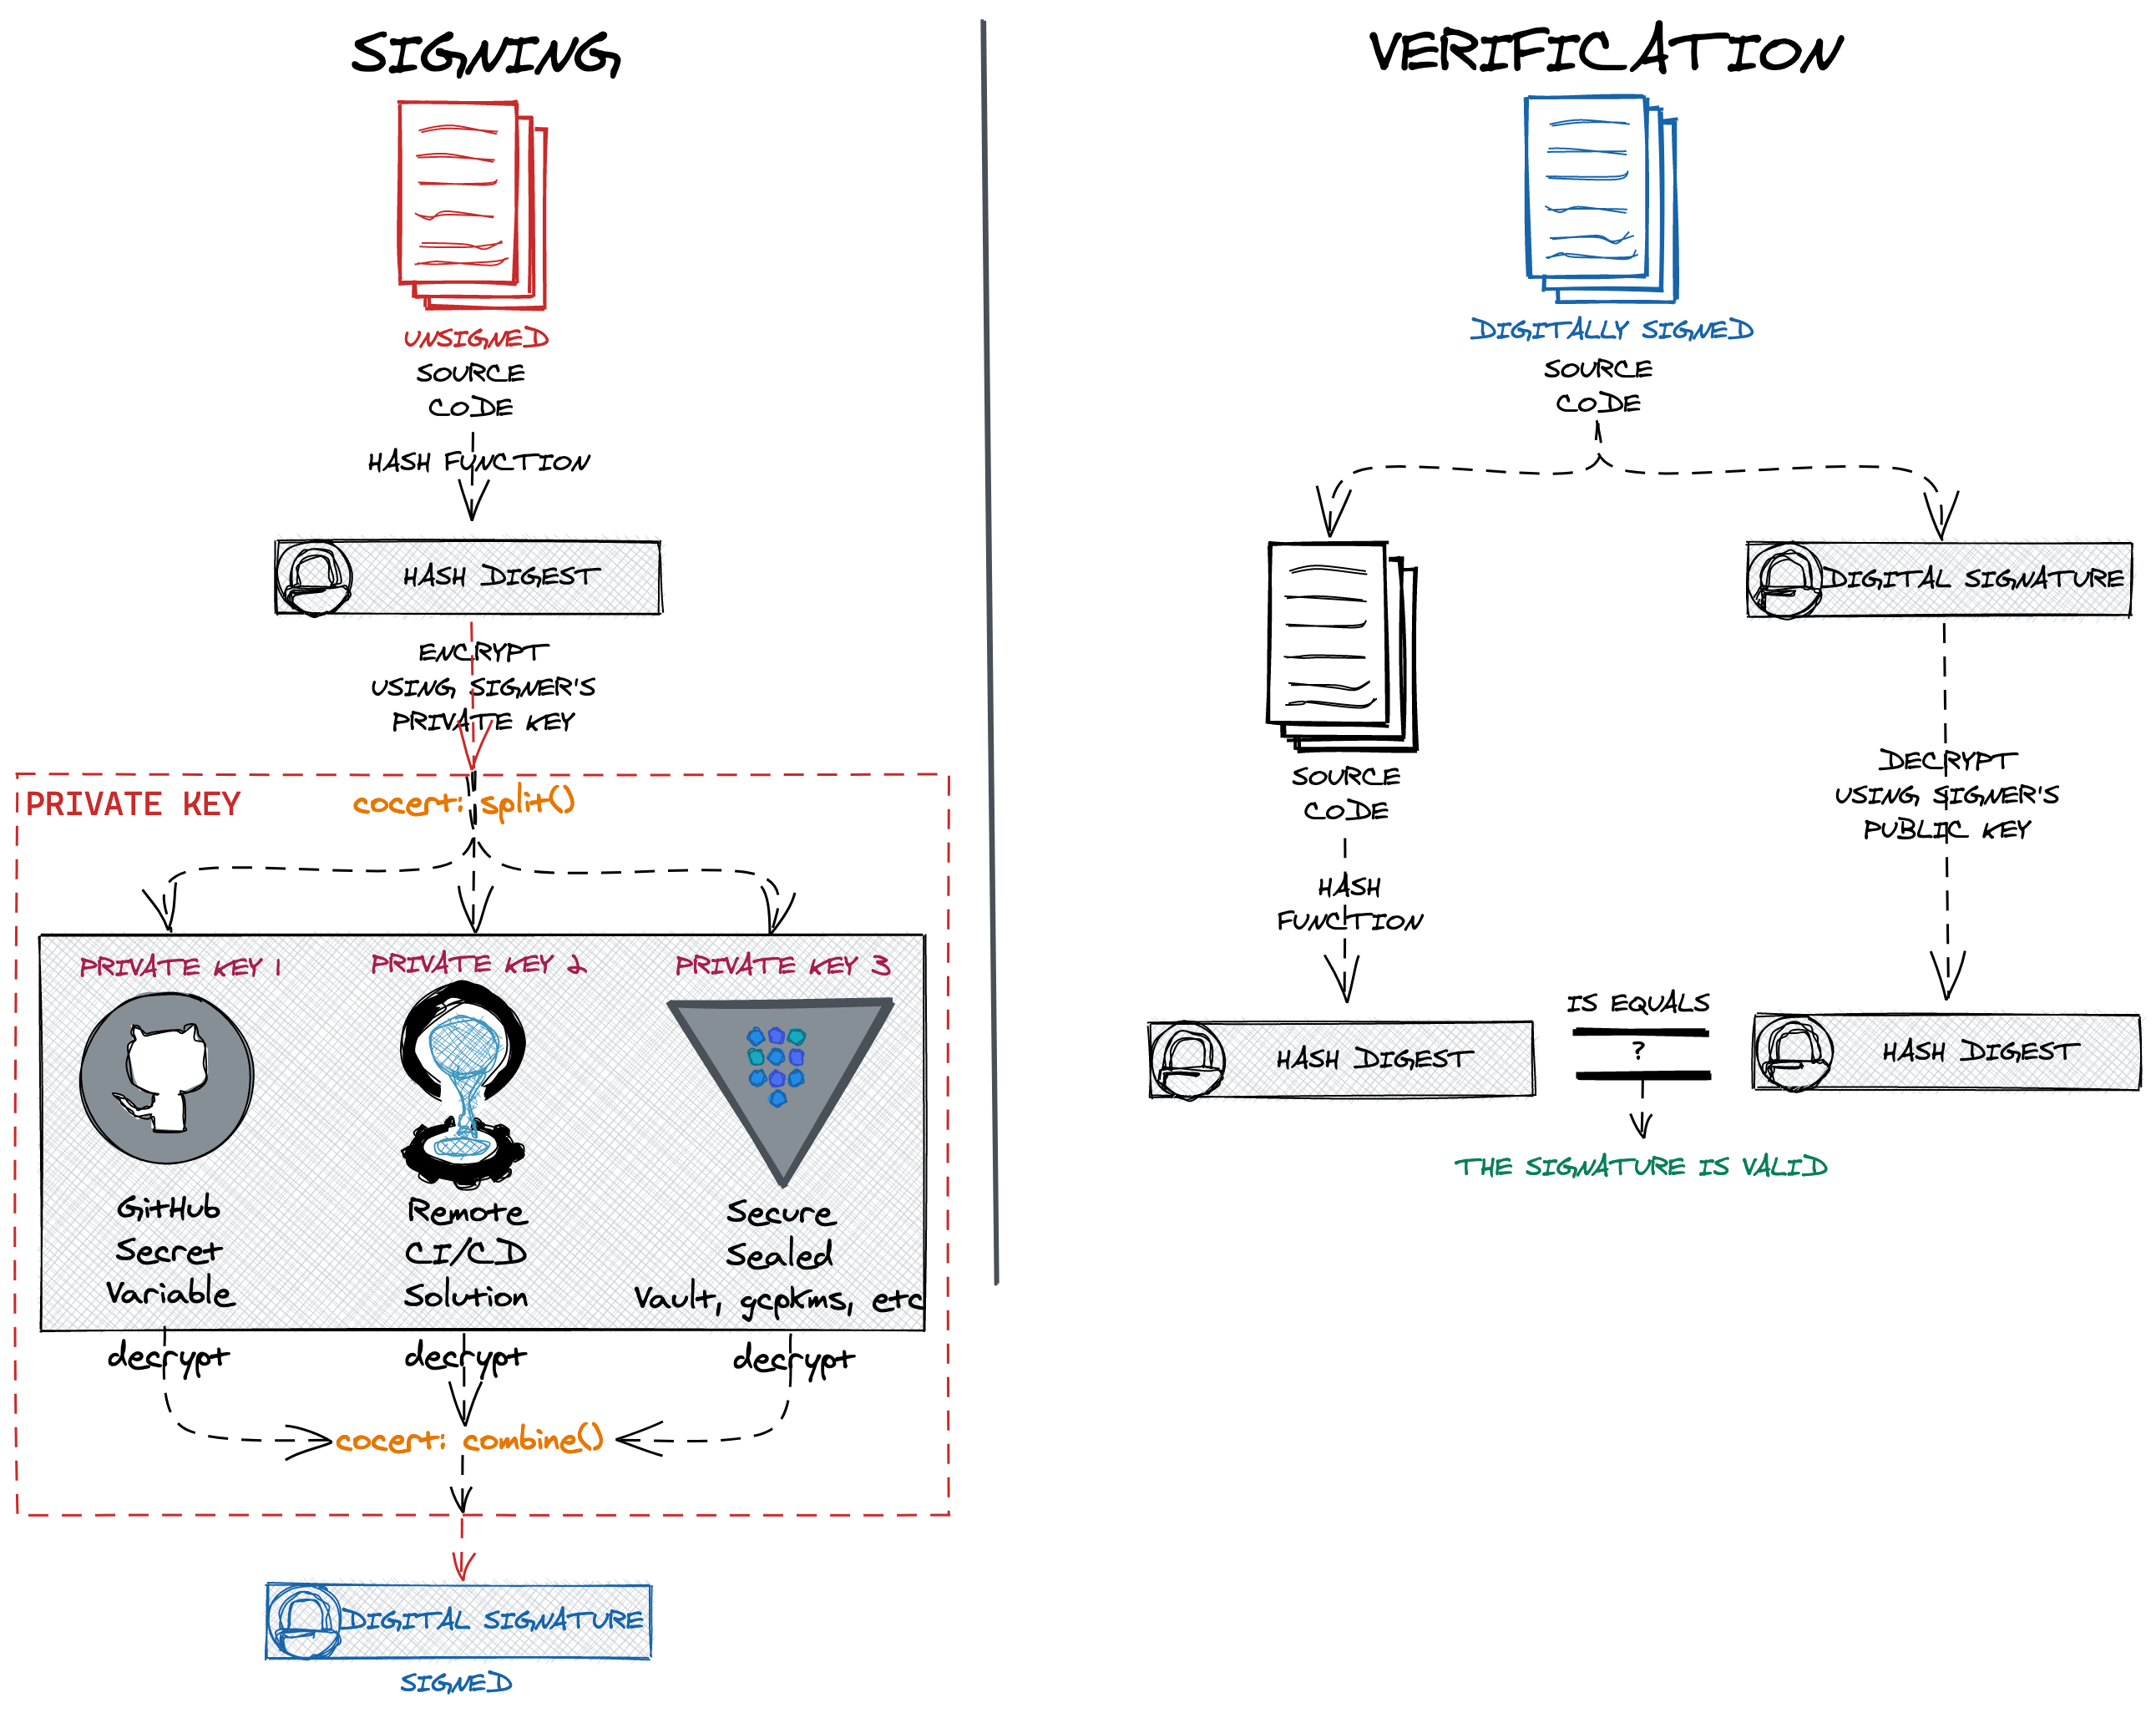
If you want to decrypt keys in the pipeline, of course your decryption keys still need to be stored securely. Which is why I added some KMS providers in the use-case diagram. [1]
[0] https://github.com/theupdateframework/go-tuf/blob/master/enc... [1] https://raw.githubusercontent.com/Dentrax/cocert/main/.res/u...