News for hackers. Stuff that matters.
Re:Slack was hacked by scrollaway on Friday March 27, 2015 @01:38PM (#9277811)
Third party authentication should be the norm. Leaving authentication to providers that absolutely know their shit, just like we leave payments to third party services.

Of course, that requires a decent protocol, and Mozilla is doing the world a disservice in not marketing Persona better seeing as it's the right solution....

Re:Slack was hacked by santosha on Friday March 27, 2015 @01:57PM (#9277954)
Major privacy issues, single point of failure etc etc. We leave payments to third party services because nobody wants to deal with the compliance nightmare that PCI-DSS is, not for security reasons. Payment is also mostly less sensitive to availability and latency issues than authentication.
Re:Slack was hacked by scrollaway on Friday March 27, 2015 @02:28PM (#9278173)
So in a world where PCI-DSS isn't a thing, you're fine entering your credit card data directly on the forms available on random websites?

Why's a password so different, seeing as most people reuse those passwords? Why do we essentially allow (and yes, I am excluding those that use password managers in this statement, I'm one of those) access to our webmail and other critical services to random websites on the internet? What makes this right?

> Payment is also mostly less sensitive to availability and latency issues than authentication.

That's patently untrue. Latency issues are nonexistant in both areas, and availability issues are critical in both areas.

Re:Slack was hacked by makeitsuckless on Friday March 27, 2015 @03:18PM (#9278454)
Yes, I have no problem entering my credit card data directly on the forms available on random websites.

Credit card payments online are so ludicrously insecure that it baffles me it's even legal. I only use them when dealing with the US (although some of the major retailers like Apple have finally started accepting 21st century payment methods), and I simply assume my credit card info has been leaking all over the place for ages.

The whole basic premise of credit cards is "we know it's totally broken, we'll just refund you the money because it's cheaper than fixing the problem".

Re:Slack was hacked by jasonlotito on Friday March 27, 2015 @03:45PM (#9278580)
> So in a world where PCI-DSS isn't a thing, you're fine entering your credit card data directly on the forms available on random websites?

Yes. It might be a hassle should someone misuse it, but the status-quo effectively means if I didn't make the purchase I'm not responsible for it.

More importantly, this was proven before PCI-DSS was a thing.

Re:Slack was hacked by mike_hearn on Friday March 27, 2015 @02:03PM (#9277990)
You mean like how Authy specialised in two-factor authentication, but still managed to have basic string concatenation bugs that rendered their entire 2FA system bypassable?
Re:Slack was hacked by yellowapple on Friday March 27, 2015 @04:08PM (#9278695)
Huh? This is the first I've heard about this, and searching for "Authy concatenation bug" isn't turning up anything useful.
Re:Slack was hacked by zaroth on Friday March 27, 2015 @04:36PM (#9278823)
Here's the write-up from Homokov. The guy is a pen-testing genius: http://sakurity.com/blog/2015/03/15/authy_bypass.html

But if you just want the money shot: http://sakurity.com/img/smsauthy.png
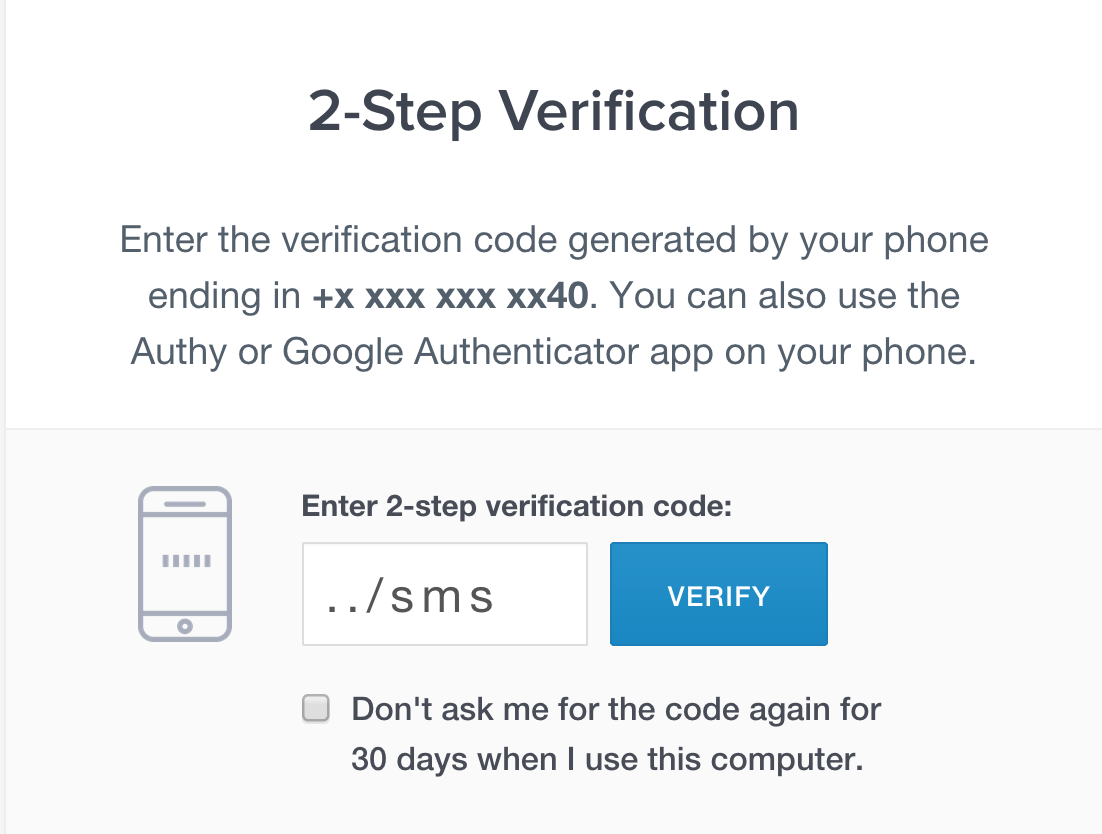
Yes. Typing '../sms' in the field bypassed the 2nd factor. Just, wow.

Re:Slack was hacked by yellowapple on Friday March 27, 2015 @04:57PM (#9278953)
Huh. Well now I know. Thanks!

Amazing what you can do with improperly-implemented input sanitation :)

This probably could've been prevented by disallowing non-number inputs, no?

Re:Slack was hacked by zaroth on Friday March 27, 2015 @05:10PM (#9279008)
"In fact the root of the problem was default Sinatra dependency 'rack-protection'".

They were doing the input sanitation, but it wasn't the very first thing in the processing pipeline, since "best practice" was to pipe everything through 'rack-protection' first.

Homokov was first to state, this was really a black-swan type bug which 99.9% of the time makes it into production. Apparently, they were doing the "right thing" and still got burned.

Re:Slack was hacked by homakov on Friday March 27, 2015 @06:51PM (#9279558)
The parent meant "This probably could've been prevented by disallowing non-number inputs" in SDK libraries. Yes, if SDK would cast everything to digits it wouldn't be possible. It is also quite obvious security-in-depth for a 2FA API. Now they do it.

*HomAkov

Re:Slack was hacked by yellowapple on Monday March 30, 2015 @04:39PM (#9292421)
Or even just input validation on the form itself before passing on to the API, which is more of what I was getting at. I don't know about the details of Authy's setup, but I know that AJAX (for example) supports enforcement of specific value types in text fields.

Basically, the form itself could have (and maybe even should have) required numeric-only values, seeing as Authy's codes are either 6 or 7 digits long and contain no alphabetical or special characters.

Re:Slack was hacked by zaroth on Friday March 27, 2015 @08:10PM (#9279863)
:-( Sorry, typo. And HN won't let me edit now, grrr!
Re:Slack was hacked by drewwwwww on Friday March 27, 2015 @04:21PM (#9278747)
Re:Slack was hacked by dhfromkorea on Friday March 27, 2015 @04:43PM (#9278864)
hey, that causes some immediate stir in my mind as a user of Authy. Could you share any reference to the incident you mentioned?
Re:Slack was hacked by wolf550e on Monday March 30, 2015 @08:10PM (#9293518)
Re:Slack was hacked by scrollaway on Friday March 27, 2015 @02:29PM (#9278178)
... no? no I don't mean like Authy.