News for hackers. Stuff that matters.
Re:Common LibreSSL porting mistakes by callesgg on Friday May 02, 2014 @04:07AM (#7684581)
To me it seams way to early to switch.

Wait until libreSSL is battle tested, and we know if it is actually better or worse than the original.

Re:Common LibreSSL porting mistakes by scrollaway on Friday May 02, 2014 @04:35AM (#7684636)
How exactly do you think LibreSSL will be battle tested?
Re:Common LibreSSL porting mistakes by callesgg on Friday May 02, 2014 @04:48AM (#7684660)
By OpenBSD

From http://www.libressl.org/ "LibreSSL is primarily developed by the OpenBSD Project, and its first inclusion into an operating system will be in OpenBSD 5.6. "

Re:Common LibreSSL porting mistakes by icebraining on Friday May 02, 2014 @05:10AM (#7684709)
OpenBSD will tests its implementation; it probably won't test ports to other OSs. So unless you use OpenBSD yourself, it won't be of much help.
Re:Common LibreSSL porting mistakes by ForHackernews on Friday May 02, 2014 @10:57AM (#7686050)
Maybe that's an argument for more people running OpenBSD.
Re:Common LibreSSL porting mistakes by i386 on Friday May 02, 2014 @06:41AM (#7684924)
Will they? Point me to their CI server
Re:Common LibreSSL porting mistakes by estebank on Friday May 02, 2014 @07:01AM (#7684994)
I can point you to their test rack:

http://www.openbsd.org/images/rack2009.jpg
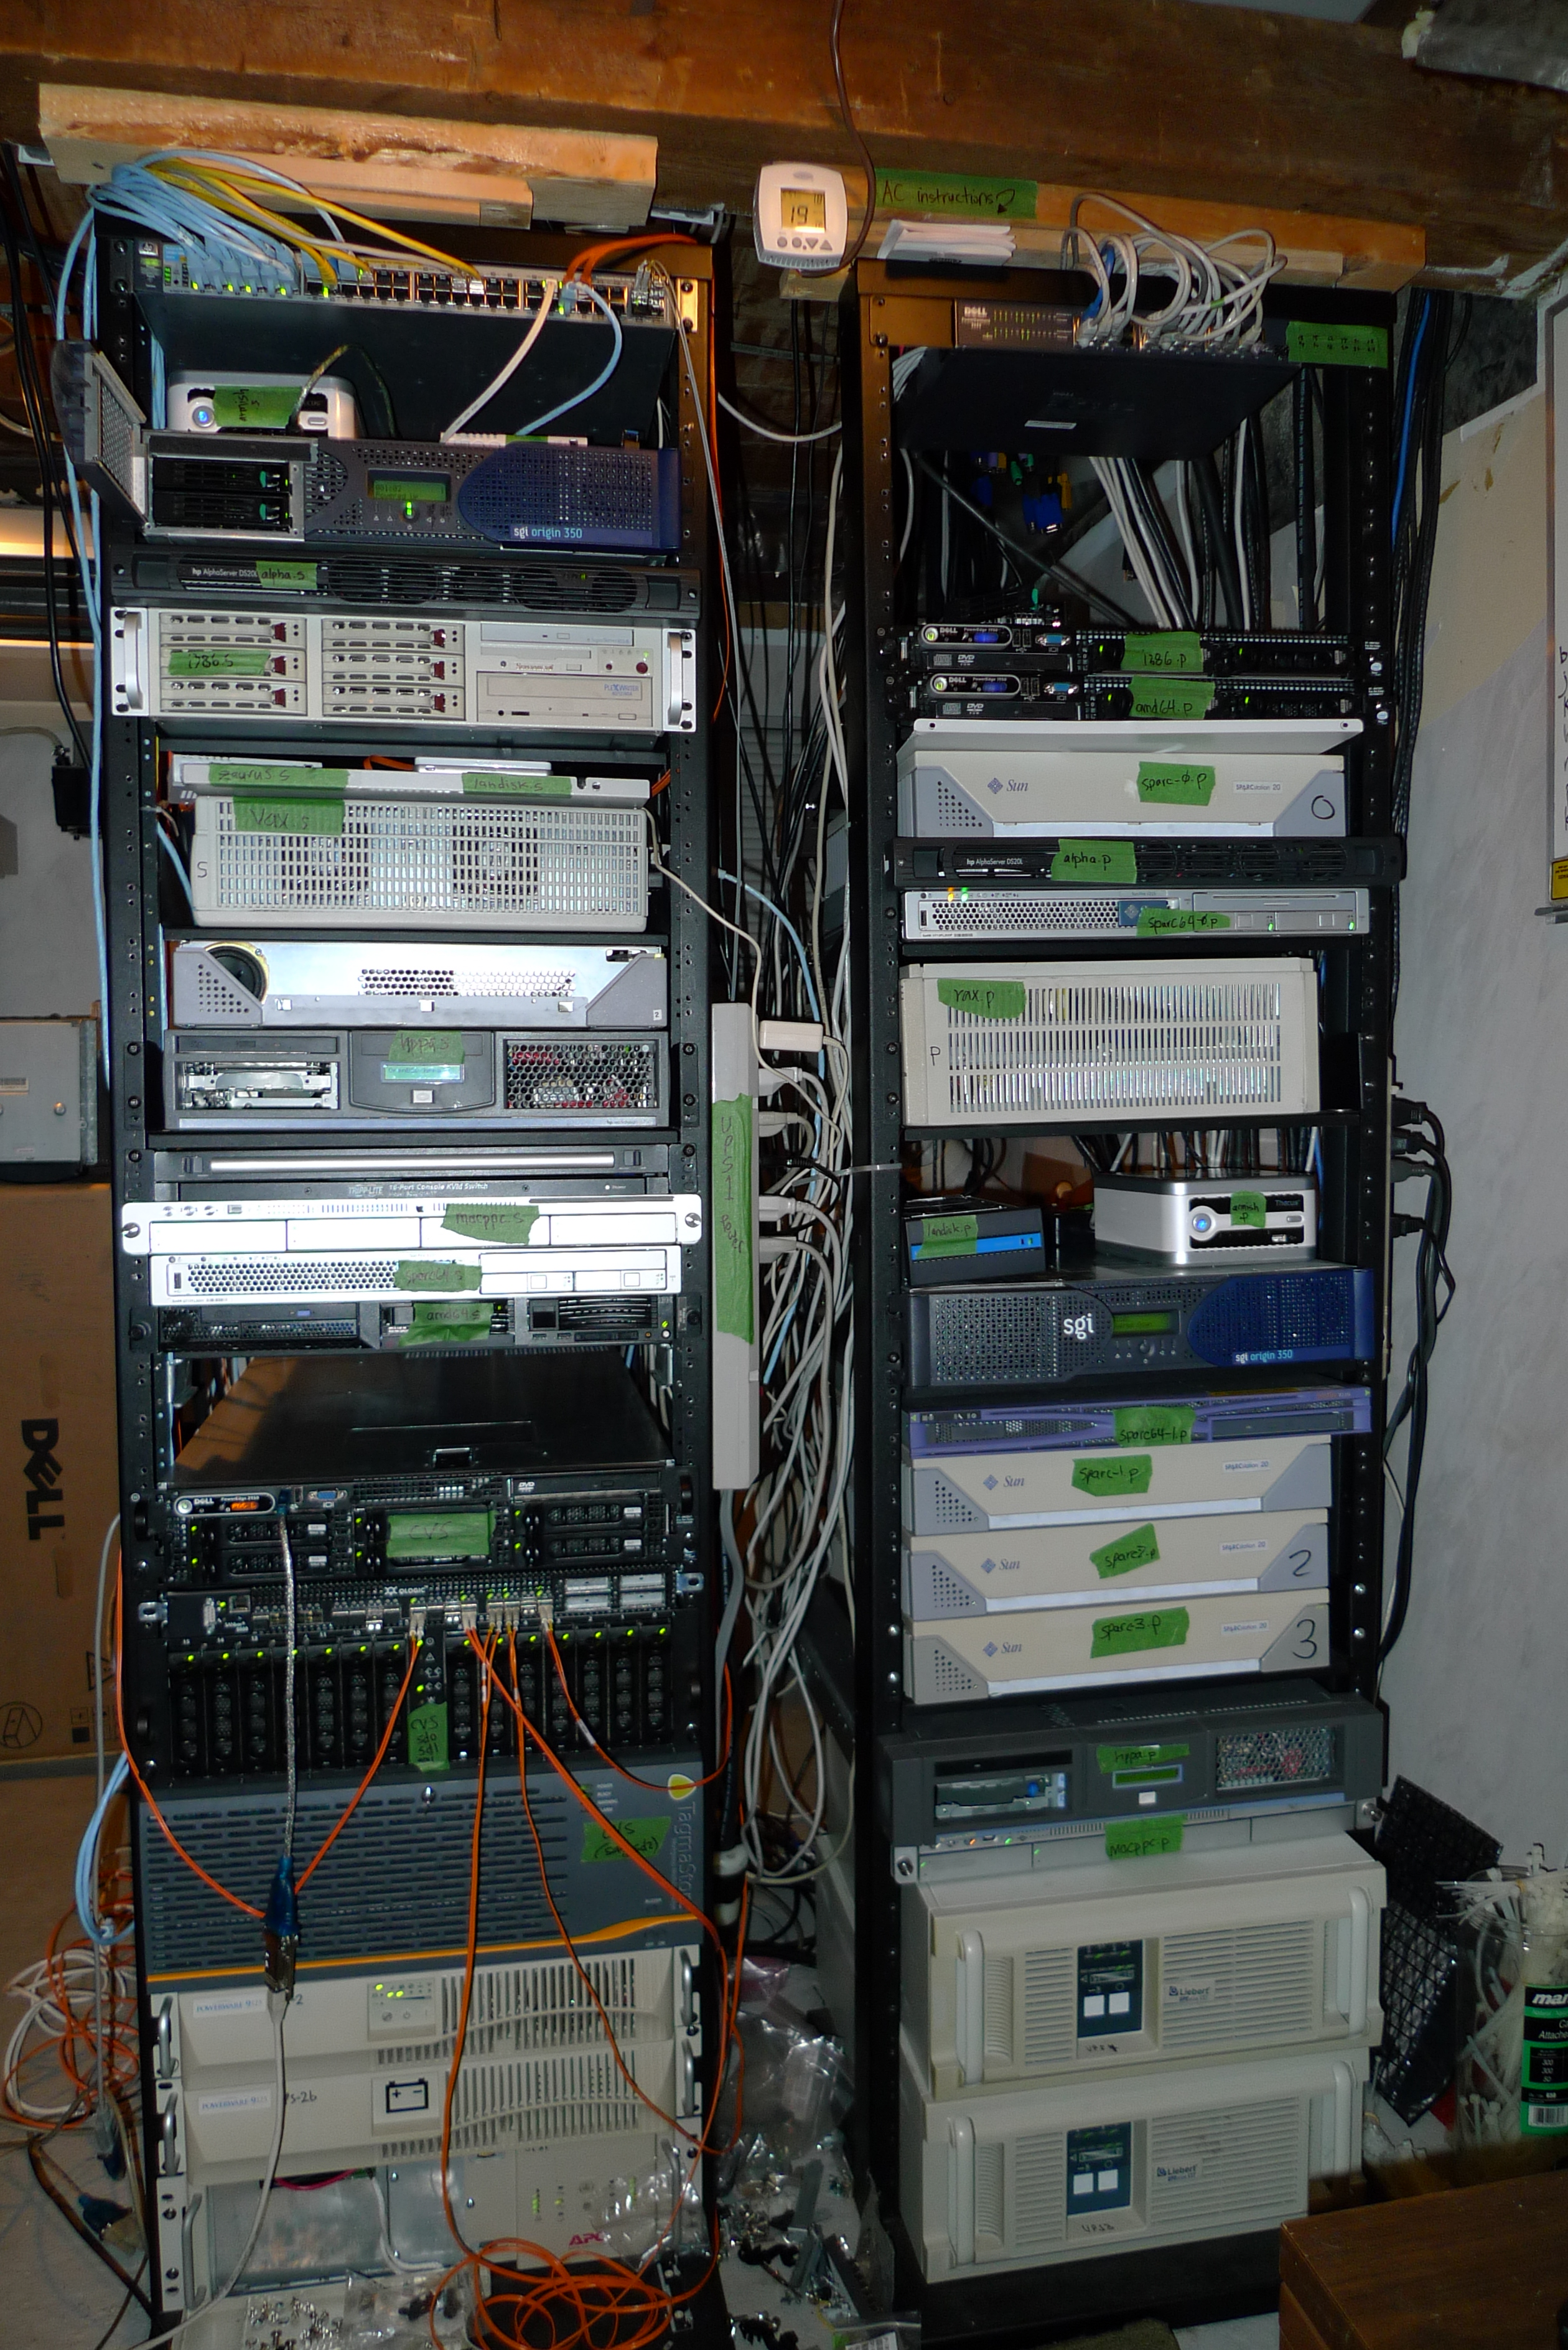
They run every version of OpenBSD in every machine they support, including 32bit SPARC, HP 300 and SGI. By running in all those machines they uncover subtle bugs that are made evident by architecture differences.

Also, please see http://anoncvs.estpak.ee/cgi-bin/cgit/openbsd-src/tree/regre...

Re:Common LibreSSL porting mistakes by makomk on Friday May 02, 2014 @07:58AM (#7685140)
That wouldn't have caught Heartbleed, wouldn't have caught a vulnerability like the one in Apple's TLS implementation, wouldn't have caught... Basically, testing that your software works in normal operation isn't enough to ensure it's secure, you need to explicitly test its behaviour under attack.
Re:Common LibreSSL porting mistakes by bsder on Friday May 02, 2014 @06:51PM (#7688640)
Actually, OpenBSD did have things in place that would have caught Heartbleed. OpenSSL went out of their way to create a situation that defeated them.

Look, the whole OpenSSL debacle is the fact that OpenSSL has ONE programmer working on it reliably. LibreSSL now has 5x-10x the manpower that was working on OpenSSL--and that's STILL probably low by an order of magnitude.

Google should pledge 5 people to work on LibreSSL by itself. They clearly have them since one of their internal audits uncovered Heartbleed.

The thing is nobody in the companies actually cared until the NSA started spying on them.

Re:Common LibreSSL porting mistakes by wlesieutre on Friday May 02, 2014 @09:23AM (#7685487)
In that case, you can't use OpenSSL either because its testing clearly doesn't ensure it's secure. So, good luck with that?
Re:Common LibreSSL porting mistakes by bonetruck on Friday May 02, 2014 @11:20AM (#7686201)
All OpenBSD developers work on -current and commonly on multiple platforms. Snapshots are rolled continuously for most platforms and made available to anyone who wants to run the latest code without having to build it themselves. The entire ports tree is compiled regularly on -current too. The compiled packages are then made available.

Check out the 'snapshots' folder of any mirror. More info here: http://www.openbsd.org/ftp.html

Re:Common LibreSSL porting mistakes by i386 on Friday May 02, 2014 @09:53PM (#7689191)
A bit unfair that this was down voted. Why does the hive mind think collectively that this is OK state for LibreSSL/OpenSSL - a critical component of internet security - to be in?

What does "testing" mean in the LibreSSL/OpenSSL situation anyway? It compiles? A regression suite passes? Manual verification?

Re:Common LibreSSL porting mistakes by clarry on Friday May 02, 2014 @06:26AM (#7684885)
Battle testing sounds like something you'd do to a new implementation. But so far there's very little new in LibreSSL; it's just cleanups and bugfixes. Do you battle test dead code removals and bug fixes?
Re:Common LibreSSL porting mistakes by DanBC on Friday May 02, 2014 @06:31AM (#7684892)
Yes. Otherwise you get the Debian SSL bug.

https://www.schneier.com/blog/archives/2008/05/random_number...

Re:Common LibreSSL porting mistakes by clarry on Friday May 02, 2014 @06:37AM (#7684913)
If anything, battle testing failed to catch that bug.

Some other form of testing could've caught it. Careful code review could've caught it.

Battle testing evidently has failed to catch many of the OpenSSL bugs that have been fixed in LibreSSL.