News for hackers. Stuff that matters.
Re:$200,000 to the first person to break Telegram by sneak on Wednesday December 18, 2013 @07:22PM (#6932045)
This is irrelevant - the "secret chat" mode is not the default (according to someone else in this thread) and you're just shoving the key verification process off on to the user with these silly graphic patterns (which, if OTR is any indication, the user won't verify anyway).

This is still vulnerable to server-side _key_ MITM. It's the hushmail/iMessage/etc silent escrow key attack.

Re:$200,000 to the first person to break Telegram by nwh on Wednesday December 18, 2013 @07:26PM (#6932053)
The interesting thing with the graphic patterns is that they're lossy. If you assume that a person will just describe the pattern or show a picture of them to one another, it becomes fairly easy to forge them.

http://telegram.org/img/key_image.jpg
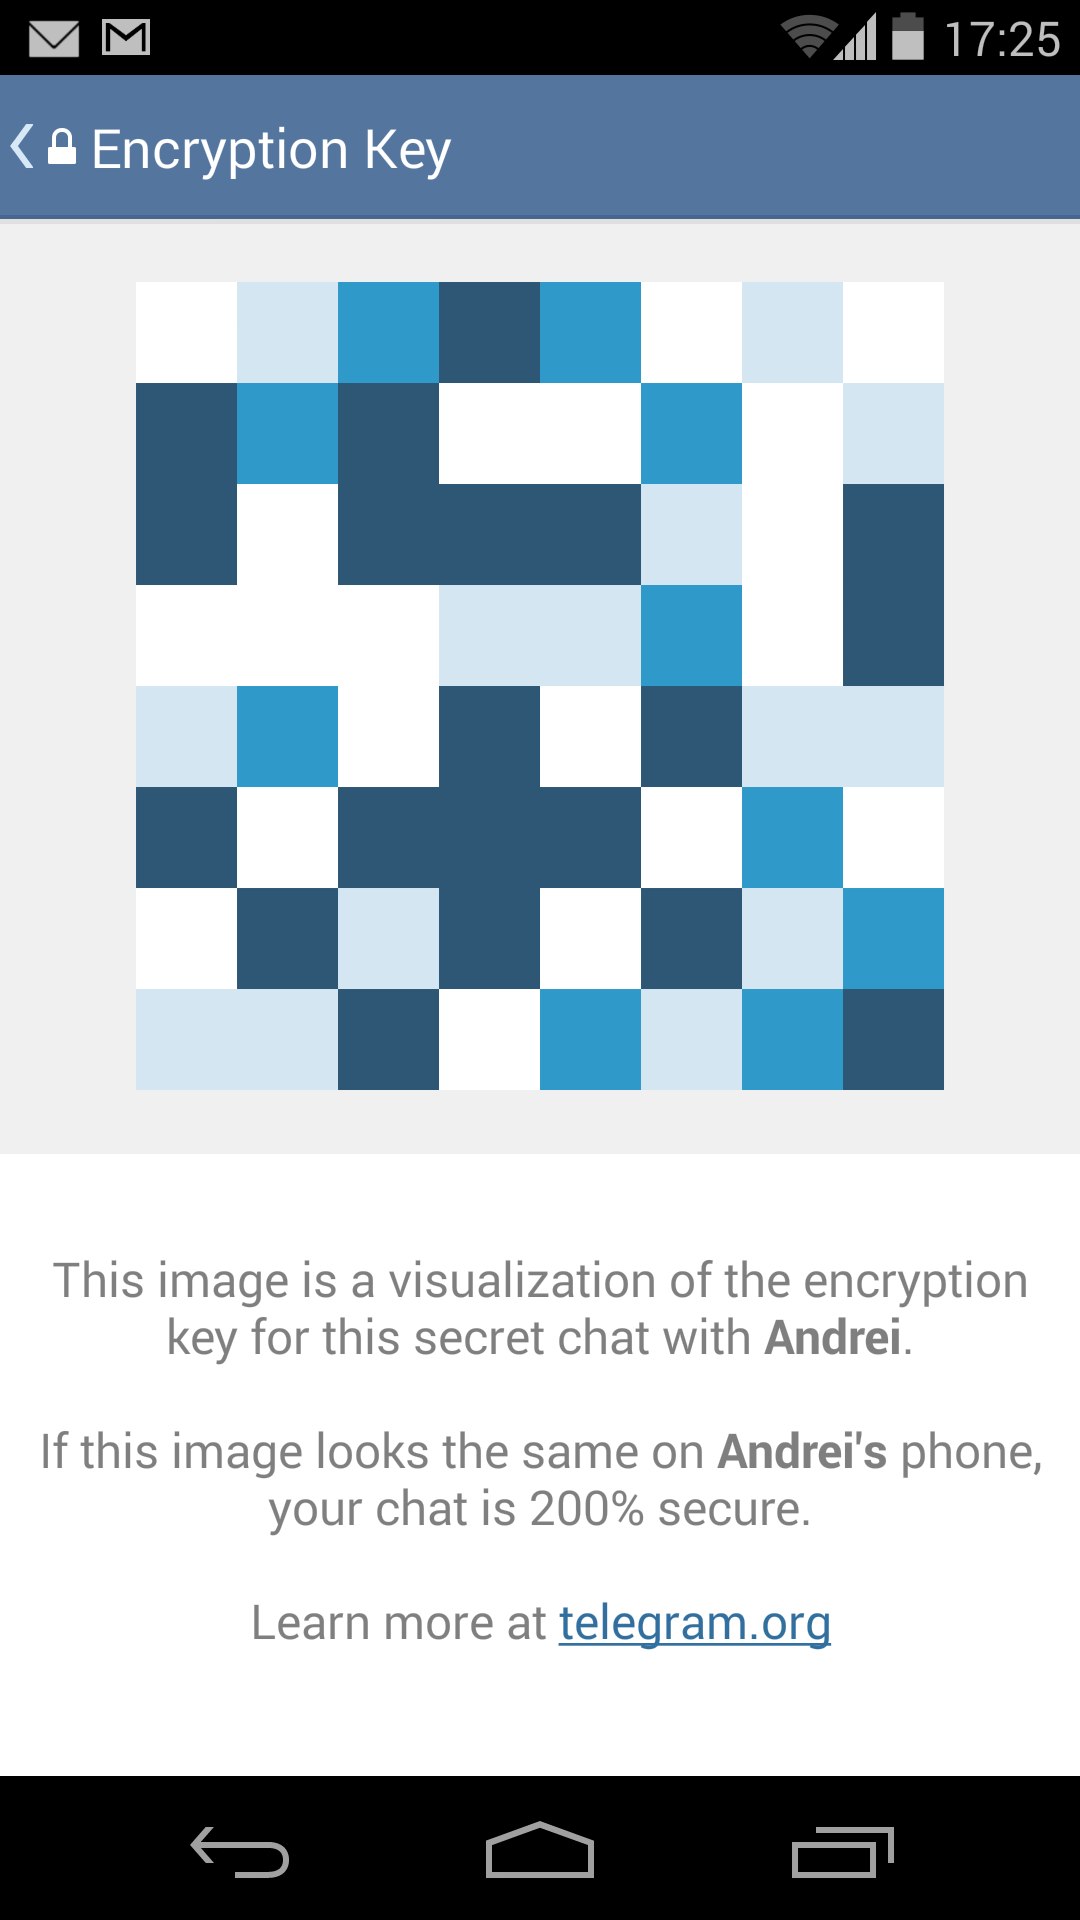
Blue in the top and bottom, white line through the middle. So little information that anybody could simply brute force the keys until they found one that matched the description well enough.

I'd happily write a little attack for that, but it's clearly not "breaking" the system enough for the bounty.

Re:$200,000 to the first person to break Telegram by sneak on Wednesday December 18, 2013 @08:06PM (#6932220)
Someone did exactly this "fuzzy fingerprint" attack for ssh host keys in 2003:

https://www.thc.org/papers/ffp.html

Re:$200,000 to the first person to break Telegram by nwh on Wednesday December 18, 2013 @08:13PM (#6932249)
That was a very good read that I wasn't aware of, thanks for the URL.