At the end all profit. While in current state, the culprit, Google profits.
And please keep fallacies like "do it yourself" for yourself, I am talking about collaboration, feel free to open another thread on top level about forks.
Same goes for /e/ ... they just dont compare.
GrapheneOS has two use-cases that are they excelling with, security and privacy.
While security is not really my threat model (some rubber-hose cryptography aka large wrench, solves this issue for any attacker), privacy violations are everyones issue. Even if they dont care.
Yes, but this is not the case. Their mission is to build a secure phone, to take two steps back and build it on a basis that is insecure and lacks proper support for basic security features they have spend a significant amount of time integrating isn't taking them anywhere.
> At the end all profit. While in current state, the culprit, Google profits.
I doubt GrapheneOS will Profit from supporting fairphone. Google is profiting because they deliver the basis of hardware and software support that meets the grapheneos standards. If someone else did that, i'm sure theyd consider. Fairphone doesn't profit because they don't delive the product.
> And please keep fallacies like "do it yourself" for yourself, I am talking about collaboration, feel free to open another thread on top level about forks.
This is not a fallacy. Graphenos is opensource. Anyone can port it.
> Same goes for /e/ ... they just dont compare.
They don't compare precisely because they make all the compromises that grapheneos doesn't.
edit To the comment below i can't complain
> This went far enough. I have stated my thoughts, if the view doesn't change, GrapheneOS will continue to sell Pixels.
Please consider the level of retardation this comment requires, it's impressive.
This is not how we have civilized discussions. To say this just because you disagree with someone about the security of an OS...
Hope the mods see this.
Before Pixel, the next is Samsung, while no one is bothered by linux kernel 3.x running on wifi SOC. Or how many linux kernels is actually running on a running phone, regardless of GrapheneOS. /s
edit, cant answer to logical fallacy bellow:
>Corporation made phones as opposed to organically grown
> Again, no one is locking down GrapheneOS you can literally download the source and try to get it to run on any device you like. You just want someone else to do the work for you because you lack the skills and it's not available for the particular phone you want.
Again, this is a fallacy. And while I am searching for a way for GrapheneOS to grow, you are searching for a way to keep it limited to corporation made phones. And it is corporations that have the most interest to make it insecure trough hardware, SOC is just one day to do it. So you are failing even on security perspective.
Corporation made phones as opposed to organically grown phones?
Again, no one is locking down GrapheneOS you can literally download the source and try to get it to run on any device you like. You just want someone else to do the work for you because you lack the skills and it's not available for the particular phone you want.
Okay, maybe you are not a native speaker, so you might mean a different thing with fallacy.
Here's the dictionary definition of fallacy
> an idea that a lot of people think is true but is in fact false [0] > a false belief [0]
My comment was
> Again, no one is locking down GrapheneOS you can literally download the source and try to get it to run on any device you like. You just want someone else to do the work for you because you lack the skills and it's not available for the particular phone you want.
Here is the link to the GrapheneOS Source: https://grapheneos.org/source
Here's the GrapheneOS FAQ regarding other Devices [1]
> Many other devices are supported by GrapheneOS at a source level, and it can be built for them without modifications to the existing GrapheneOS source tree. Device support repositories for the Android Open Source Project can simply be dropped into the source tree, with at most minor modifications within them to support GrapheneOS. In most cases, substantial work beyond that will be needed to bring the support up to the same standards. For most devices, the hardware and firmware will prevent providing a reasonably secure device, regardless of the work put into device support.
[0] https://dictionary.cambridge.org/de/worterbuch/englisch/fall... [1] https://grapheneos.org/faq#supported-devices
Where's the fallacy?
---
Now after editing he makes this argument instead:
> And while I am searching for a way for GrapheneOS to grow, you are searching for a way to keep it limited to corporation made phones. And it is corporations that have the most interest to make it insecure trough hardware, SOC is just one day to do it. So you are failing even on security perspective.
There are no not-corporation made phones on this planet. Every conceivable part of a phone is made by a corporations from parts extracted from this planet by corporations, shipped and assembled by corporations. Do you think that the Fairphone, made by the fairphone corporation is not made by a corporation? From There Wikipage [2]
> Fairphone B.V. > Company type Privately held company
> And it is corporations that have the most interest to make it insecure trough hardware, SOC is just one day to do it. So you are failing even on security perspective.
So google, spending literally billions [3] on cybersecurity with a direct interest and industry leading track record in keeping pixel devices secure has an interest to make it insecure?
I stand by judgment: The required retardation for this kind of argument is amazing.
[2] https://en.wikipedia.org/wiki/Fairphone [3] https://blog.google/technology/safety-security/why-were-comm...
---
So, i'm dealing with a first grade tech student that learned some cybersecurity words. Here's how you can prove me wrong, answer the following simple questions:
1. Why should the GrapheneOS Developers do the work you want them to do? They seem uninterested and I don't see you paying them the 100s of thousands of dollars to hire someone to do the work for them.
2. Name a Phone that's not made by a corporation.
Feeling better, after I have mentioned it to you twice, I am interested into cooperation and you are still coming back with same nonsense, that has nothing to do with it?
> So google, spending literally billions
Yes, in same manner as USA government, spending additional billions in undermining random generator(1), as they know it will be secure for them, but not for you.
And trusting corporations, that they are doing it right while they can profit heavily from it(2), is on on strange level of thought(3).
If you want security, go away from corporations, but this is not really the reason, right? You want to impose false sense of security, just to the right level.
I, on opposite, know there is no security (we can test rubber-hose cryptography, lets academically test if you will enter wipe pin under the threat of large wrench) and we will see, what your decision will be, but I want to be reasonable enough secure from data grabbing companies, which is what you are denying to others with security as excuse.
While there is practically no chance someone will tie me to a chair, companies are stealing users data on daily basis and this is not a threat for you, compared to someone wasting thousands of dollars getting into your phone.
Yep, I was also fascinated with security and "bits" of cypher algorithms, while I was 15.
1. https://en.wikipedia.org/wiki/Dual_EC_DRBG#Weakness:_a_poten...
2. https://news.ycombinator.com/item?id=44334167
3. https://insight.kellogg.northwestern.edu/article/leave_my_br...
---
> 1. Why should the GrapheneOS Developers do the work you want them to do? They seem uninterested and I don't see you paying them the 100s of thousands of dollars to hire someone to do the work for them.
They dont do any work regarding security that would matter. As hardly anyone is using GrapheneOS. Most people use it for privacy, I don't know a one single person that would use it for security, I have bootloader unlocked as I don't care, its not something that would be a reasonable threat to me, while government actors are not something, I can defend against as they will break my legs and I will beg them to allow me to enter pin.
> 2. Name a Phone that's not made by a corporation.
So they can immediately stop doing it. It is futile, insecure and worthless even from perspective of privacy unless they give people a chance to use it. And currently they dont with excuse of security.
---
Something about gay fish.
https://imgs.xkcd.com/comics/security.png
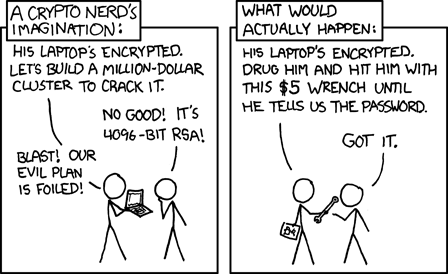
On the other side, you can academically test privacy of my phone, where you profit a few dollars if you steal my data, not even worth a wrench.
We will quickly determine, which part of GrapheneOS is doing its work better and which part, security or privacy is more useful for users.
I am just realistic. You are delusional.
>Please consider the level of retardation this comment requires, it's impressive.
Yes, thats why I have stopped discussing with you and I dont know why I even started - futileness discussing with GrapheneOS evangelists is well known over the internet.
It'd be nice if you blatantly didn't break HN rules.
This feels super entitled to me. GrapheneOS Devs have a mission and they get to make that. You get it for free and if you like it you can give them money. If they don't support the hardware you like you are free to fork it and get it to run yourself.
And if security isn't something you care about but privacy is and you feel like there's a difference here you can still install /e/os or lineageos and similar on the fairphone.