Re:Google’s Fully Homomorphic Encryption Compiler – A Primer
by l33t233372 on Tuesday February 14, 2023 @01:25AM
(#34786126)
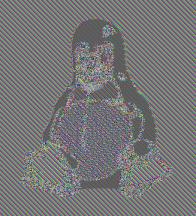
ECB should never be used under any circumstances. Library creators would do well to rename their functions along the lines of ECB_NEVER_USE_THIS_IS_NOT_SECURE.
Those standards are meaningless by themselves without specifying a mode (e.g. GCM, CTR, CBC, ECB, etc). A thing people sometimes try to do with them (no idea if this is what vaulttree is doing) is use some less secure mode that is determistic and do equality matching (this is almost always a bad idea and usually leaks way more than you would naively assume). For example, if you use ECB mode you can search as long as you are searching along block boundries.
https://www.microsoft.com/en-us/research/wp-content/uploads/... is an interesting paper about this sort of thing.