Re:Sshuttle - tunnel all your traffic through ssh
by jerf on Monday April 04, 2011 @05:24PM
(#2408610)
The commit log seems to imply DNS has been added: https://github.com/apenwarr/sshuttle/commit/0bf0351d9becae3d... (along with a few subsequent patches)
But I have not tried it.
Re:Sshuttle - tunnel all your traffic through ssh
by fs111 on Monday April 04, 2011 @05:24PM
(#2408607)
I personally don't use it for security reasons, but to be able to listen to last.fm easily through a vps in a country, where that is for free. (just one example)
Security is never just a software you install, it also depends on you, knowing, what you do.
Re:Sshuttle - tunnel all your traffic through ssh
by tlrobinson on Monday April 04, 2011 @05:27PM
(#2408623)
Sure there are other uses. I'm just making sure people know, because it's being advertised as a VPN alternative, and this problem wasn't obvious to me when I first looked at it.
Re:Sshuttle - tunnel all your traffic through ssh
by tianyicui on Monday April 04, 2011 @09:02PM
(#2409258)
I just tried, it does have the ability to route DNS requests through the tunnel.
Out of curiosity, is it theoretically possible to route other kinds of traffic over this, e.g. UDP, ICMP(ping)? Thanks.
Re:Sshuttle - tunnel all your traffic through ssh
by tlrobinson on Monday April 04, 2011 @09:08PM
(#2409269)
Sure it's possible (see: http://en.wikipedia.org/wiki/IP_over_Avian_Carriers). I don't know why they haven't done it yet.
Re:Sshuttle - tunnel all your traffic through ssh
by Xurinos on Tuesday April 05, 2011 @08:38AM
(#2410658)
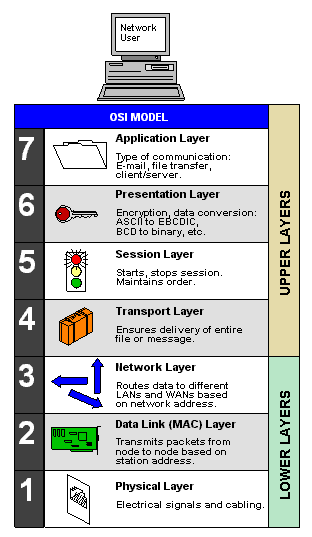
You are referring to the lowest OSI layer. It is easy to propose laying out new line (or network of birds), but the costs are huge.
Re:Sshuttle - tunnel all your traffic through ssh
by fs111 on Tuesday April 05, 2011 @01:55PM
(#2411961)
OSI? Really? http://pablotron.org/files/7_layer_burrito.html
Re:Sshuttle - tunnel all your traffic through ssh
by mariana on Monday April 04, 2011 @09:38PM
(#2409328)
Would it be too hard to add non TCP traffic tunneling? This already supports DNS traffic through the tunnel but I wonder it is feasible to tunnel all kinds of traffic (UDP and ICMP mostly) through it?
Re:Sshuttle - tunnel all your traffic through ssh
by pmjordan on Tuesday April 05, 2011 @08:08AM
(#2410580)
The SSH connection is inherently a reliable stream, so you need to be careful - it should work if you drop UDP packets if the ssh stream's send buffer is full, but there might be severe performance traps down that route. Maybe an expert can elaborate. The other issue is you'd need to do manual NAT-like connection tracking to match up sources and destinations. I could imagine many UDP-based protocols not taking kindly to that sort of treatment.
By the way, (open-)ssh itself supports a tun/tap VPN mode (-w I believe) that creates actual network interfaces on the two endpoints, and thus can transport any IP traffic. It needs to be explicitly enabled on the server, and needs kernel tun/tap support, which is usually missing on VPSes that don't let you run your own kernel (modules).
I tried sshuttle awhile ago and abandoned it because of this. The only thing worse than no security is a false sense of security.