It’s a complex and laborious process, including multiple partially automated steps both in sending, receiving, and processing an application for an absentee ballot, as well sending, receiving, and processing the absentee ballot itself (in one of several possible languages, as requested by the voter).
This includes a manual step of comparing the voters signature on an outer envelope, which is scanned by machine and presented to remote data entry techs for side-by-side comparison with the signature on the scanned application for the absentee ballot. If the signatures aren’t a good enough match as decided by the human, the ballot is rejected (and the voter eventually notified).
So if you’re not sending applications for an absentee ballot out to voters, where is this signature coming from that you are comparing against? It can’t possibly be the electronically captured signature on the drivers license, because that one is chicken scratch...
[1] - https://www.ocvote.com/election-library/docs/2007%20Grand%20...
* The tampering envelope is extended to weeks instead of hours.
* There is a non-zero risk of vote secrecy violation.
* There is a non-zero risk of voter pressuring.
Coming from a country that earned the right to vote through violent revolt, it is strange how established democracies, especially the US, are cavalier with weakening the voting process: vote on a Tuesday [???], no paper trail voting machines [???], mail-in voting [???].
In a perfect world I would execute elections in the same manner we do in Iceland. Voting booth, paper ballots, pencils for marks. We have a presidential election this summer and everyone was worried if COVID would suppress the vote. Looks like it won't since we only have 2 active cases and new cases are almost none (can't find the numbers atm but iirc we had 7 new cases in the month of May).
[0]: https://www.brennancenter.org/our-work/research-reports/auto...
One more thought: Simple >>> Complex.
Small variations in a technically correct process may break some of its properties. The more complex the process, the easier is to inject variations, some of them adversarial. If gerrymandering is to be taken as an example, this can be taken to quite some extremes by two sides driven to win the zero-sum game at all costs. But even in absence of that, bugs happen.
To nitpick one detail, I'm not persuaded by the secrecy violation prevention argument. You either prevent secrecy violation by anonymization, or you prevent vote fraud by keeping a link between the voter and the ballot. You can't have both at the same time. In person voting minimizes the bounding box of anonymization: in space, at the ballot box, and in time, the election day. Hopefully both parties afford to have observers during this space-time interval. As you spread out the voting process, both spatially and temporally, it becomes increasingly impractical / too expensive to maintain observers of the entire process.
With that, we are left with the following attack vectors: the server and its software, either via hacking or via subtle rule tweaks, targeted ballot invalidation, voter pressure. As a technopesimist, I'm especially uncomfortable that a key piece of the process is an opaque blob of silicon that can't meaningfully be inspected by a human observer. Echoes of Diebold voting machines, plus billions of dollars poured into elections. But I can see why HN audience is prone to be persuaded this is a good idea.
Clarification: serial number is mailed with the ballot, contains a signature (like two part keys for API f.ex.). You submit the serial for signing through authentication mechanism (verifying the voter). The signature can be either PKI or hash. This way you can validate serials, signatures and have them independent from the ballot after separation. If you have designated drop-off locations you insure the ballots are tamper-proof after being filled out (barring massive system-wide fraud).
http://mediad.publicbroadcasting.net/p/northwestnews/files/s...
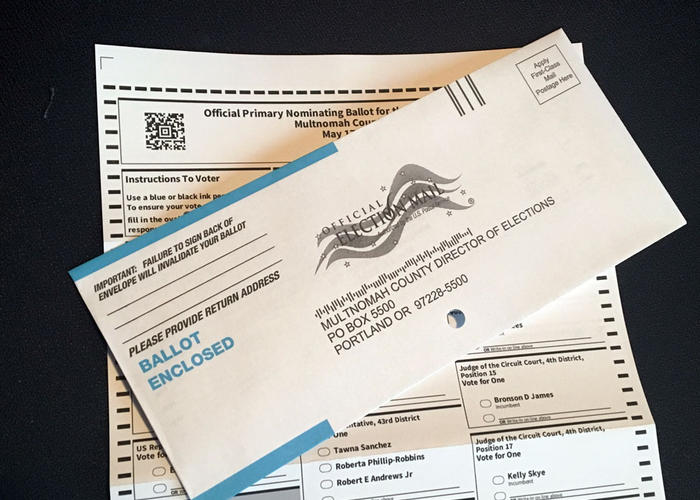
1. Ballots contain: a ballot, a serial number, a small envelope and a large envelope. 2. The voter fills in the ballot and stuffs in the small envelope and closes it. 3. Voter now needs to get a code from a webpage and add to the serial number card. Here's the part where infrastructure in Iceland is excellent. Nigh everyone has personal electronic certificates on their phones so authentication is easy. I must admit I have no idea how easy or hard this would be in the States. 4. Puts the small envelope and the serial number card in the large envelope and closes it. 5. Mails in the large envelope. 6. Precinct opens the large envelope and validates the serial number. If it is valid, puts the small envelope in box headed for counting. 7. Count the votes. Declare results. 8. Investigate the "bad serials and validation number".
There are fun things to think about doing to increase confidence in the voting process. In this scheme I describe the validation code could be a hash of the serial and a salt. Then you could actually release all the validation cards so voters can actually verify that their ballots were counted.