Re:SMS is not 2FA-secure
by fedorareis on Friday January 10, 2020 @09:35PM
(#22017700)
It depends. If your iMessage account is tied to an Apple ID used on multiple devices with 2FA enabled then the code is sent to one of those other devices to validate the login on the new device. So if you are fully in the Apple ecosystem and have 2FA enabled then I believe it would be secure. I know I get alerts on my other devices any time I have had to re-add my phone number to an Apple ID. It tells me my phone number is now being used on another device. So at the very least you would probably be notified.
[ Parent
| on HN ]
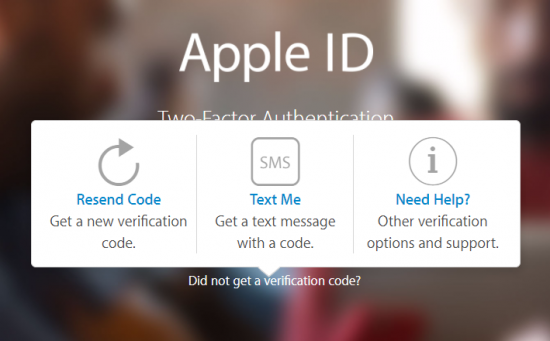
When you get the prompt to input the code, just choose "Did not get a verification code" and it will fall back to SMS.
See: https://blog.elcomsoft.com/wp-content/uploads/2016/03/apple_...
Re:SMS is not 2FA-secure
by fedorareis on Friday January 10, 2020 @11:10PM
(#22018062)
Interesting, I did not realize that.
This is a great find too
iMessage is only tied to an Apple ID for the e-mail part (where they can send iMessage to your e-mail). The phone number part is independent of that and you can take it over provided you prove ownership of the phone number (by inserting the SIM into an iPhone, it'll send an invisible SMS to Apple and back and that then activates iMessage on that number on that new device).