Re:IBM Quad9 – A free security solution using DNS to protect...
by krylon on Thursday November 16, 2017 @11:35AM
(#15714011)
A recursive resolver does not need to forward queries. ;-)
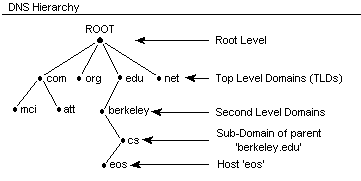
Conceptually, it starts with the root nameservers and works its way up - dot by dot, recursively, hence the name - until it finds the domain the host in question in it, then asks the nameservers for that zone and caches the result.
It is possible - with BIND9 at least, but I guess other DNS servers offer similar capabilities - to use forward servers for convenience/caching or to redirect queries to specific servers depending on the name in the query. But it is not mandatory.
Re:IBM Quad9 – A free security solution using DNS to protect...
by bjpbakker on Thursday November 16, 2017 @12:00PM
(#15714270)
True, seems I read over the recursive part. In which case it is definitely not easy to set up.
But even for a recursive DNS server that is only used by a single client aggregation for popular dains is not impossible.
There are better and definitely easier ways to have anonymous DNS lookups
So who do you forward your queries to? :)