You can still make the apps you're talking about with html+css and enforce js=off in your user browsers, but there is a reason no one wants to do that these days.
And unless I'm not mistaken, there have been plenty of exploitable bugs in the core rendering engines that involve only html/css, so your utopian world STILL depends on a secure sandbox.
I'm going to heavily disagree with you. There were plenty of sites that were successful without using heavy JS. Most webapps I see can run easily without JS, they just choose not to. Yes, there are exceptions, but they are exceptions.
"The core features people want" aren't JS-pop-ups, and slow browsers. They want sites that work quickly, are easy to understand, and work on mobile just as well as on a desktop. I would argue that JS makes all of those aspects worse.
Not quite: users want to achieve specific tasks as quickly and easily as possible. Certainly "work quickly" and "work on mobile" are two huge pillars of that for many (probably the majority of) tasks, but for many applications you have to make significant trade-offs in functionality under the constraints of a static site.
Anything built on the web is competing with something that already is or can be built natively. Native applications don't have to concern themselves with this sort of limitation on interactivity as a trade-off for latency, which is an advantage. On the other hand, the web has the (huge) advantages of open discoverability and no-install distribution. It makes sense for both platforms to be working to fill in their gaps while trying to minimize the trade-offs.
It's clear that slow startup due to big chunks of js (and media) on load has become a big problem, and people are working on that, perhaps without much to show for it yet, but it isn't obvious to me that ceding the territory of interactive applications back to native implementations would be the better way forward.
Of course, this is all in context of a typical webpage. There are exceptions to this.
Hi, that's me. The reason is, quite simply, because this is not a good user experience:
https://pbs.twimg.com/media/CmaP3JvUcAA8-5a.jpg:large
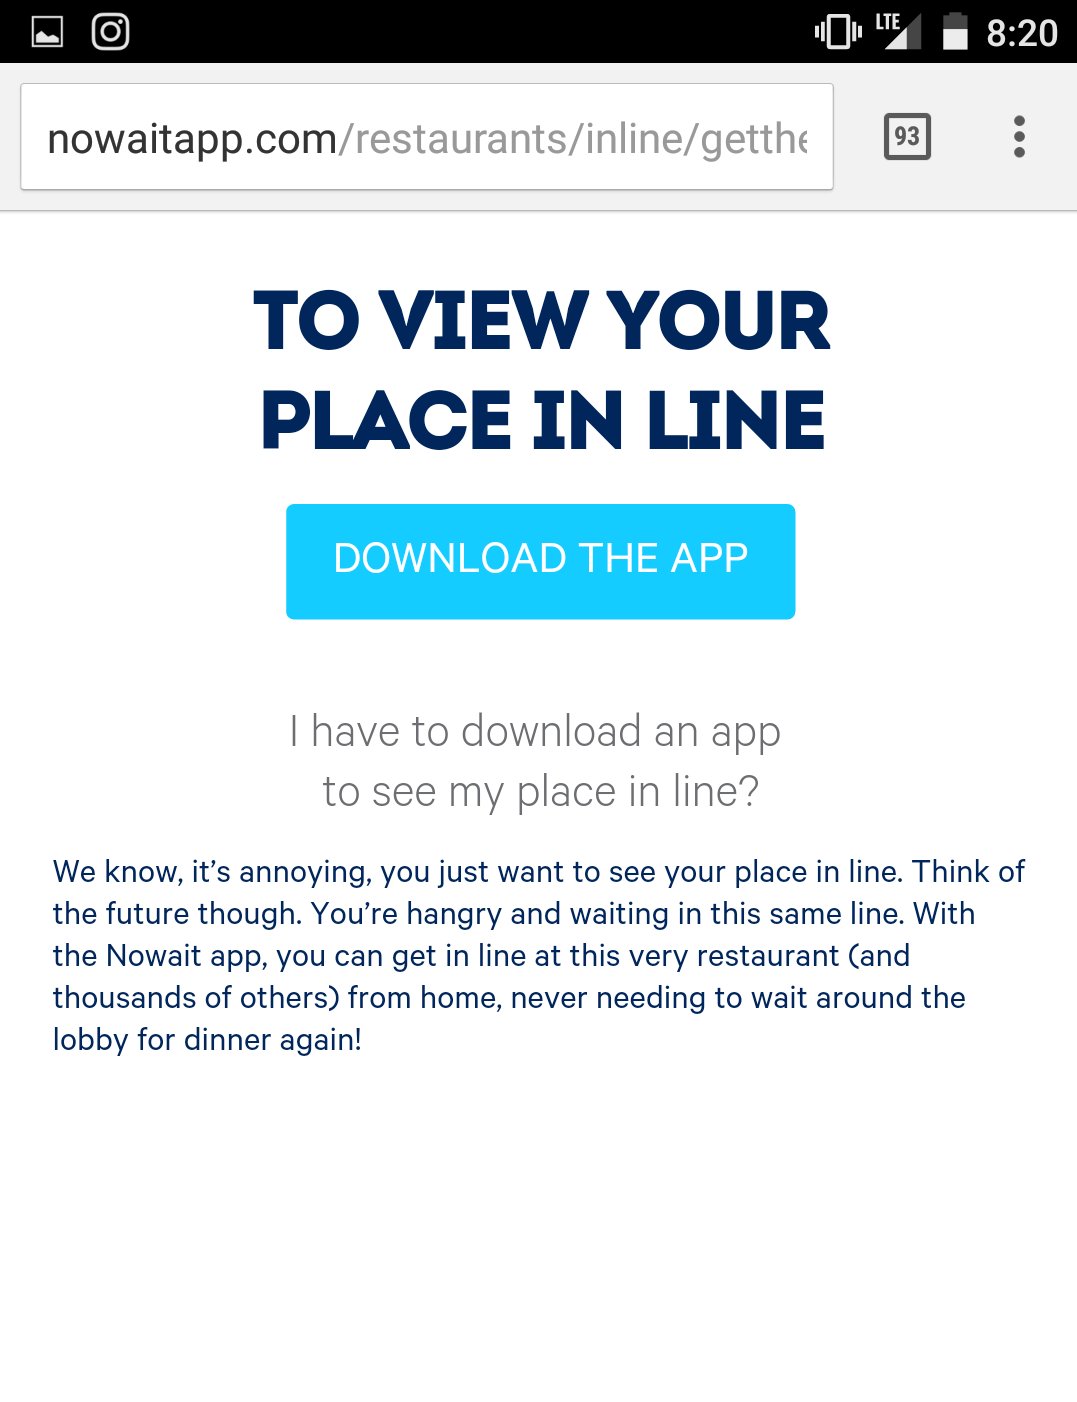
The open web is my platform of choice, and the technology is finally there. Progressive Web Apps[1] offer the features of native but are instantly-available, without downloading or installing. So yes, I very much want that as a developer.
OK, fine. I'll concede devs want more interactiveness. I have yet to see evidence that users want more interactiveness. I think that points to the arrogance of devs "who totally know better than the user".
This had traditionally happened through POST/GET requests and having all the logic server-side. Yes it's possible to build interaction without Javascript, but it's not a great effect. Imagine if you had to wait for a page load every time you voted on a post on reddit.
Now extend that to modern webapps. Take Google's Voice Memos demo[1]. It loads instantly. It supports any device. You can even add it to your homescreen and you won't be able to tell it from a native app. Everything about it just works. Why would a user not want such an experience?
Javascript interaction is the natural evolution of the web. If it wasn't JS it would have been something else. This growth has been driven by users, devs, and browser vendors alike. There's nothing "arrogant" about it.
I don't know of anyone, besides programmers, who doesn't like the current interactive-web-app web more than the decade-ago full-page-load web. They don't like ads and popups and things being slow either, but they love Gmail and AirBnB and Facebook and on and on. We should solve the problems without throwing away all the good stuff.
The reason is, that JS is enabled by default, nothing else.
If users had the possibility to actively decide before any remote code will execute on their computer, how many would like to enable it?
We are just one default checkbox setting away from what you call "utopia" here - a word that should be used for much bigger things.
Of utopic naivity in deed is the expectation that such powerful features will not be misused - delivering browsers with code execution enabled by default will be looked at as one of the most funny things of the first internet in a few decades.
Web application development paradigms that enforce JavaScript usage as an absolute necessity are examples of "naive utopian deadends". It is totally anti-avantgarde and anti-progressive, we should not waste so many young talents on that.
None of that changes that js adds incredible power to what webpages can do and there is zero chance of rolling back browser-delivered applications at this point.
I also don't understand why you think html+css doesn't have the same fundamental 'code execution' flaw - you're accepting unseen input from a remote source and feeding it into an execution engine which will have exploits - whether that's css or html or js or xml or *.
Back to your question though: yes, 98% of web users want remote code execution on because they want spotify, facebook, and youtube to work. They would be upset if they even had to manually go in and enable it. And I'm not even sure you could make a quality version of those sites without js.
It might be convenient and powerful - but secure? With our current huge (in code and complexity) browsers? With the series of bugs in font rendering, image libraries etc?
[ed: autocorrect. Apologies for seemingly calling algolia "third-rate" for a while there!]
"same origin" is about the source of that code, only of minor relevance here as long as no working signed code distribution mechanism and infrastructure exists - why not, btw, after all these years?
For communications and general information transmission we do not need remote code execution.
Yes, browsers try to do that in a "safe way" - the "sandboxing" approach has been exercised for many years now, mostly without success. Maybe Qubes OS can be a successful approach to this problem, but we still have too many non-technical problems to solve, as reality shows, so enough time to do more research. Until then: css only should be the default.
CSS gives us a very good way to stop going on with that inacceptable defaults while we fix the first version of the internet.
My impression is that Javascript has basically been the most successful sandbox ever deployed on a large scale. All vulnerabilities I've seen that escape the sandbox are due to things like Flash.
Does anybody know of any "JS-only" exploits that have happened?
This was used to win a contest: https://securityevaluators.com/knowledge/papers/engineeringh...
Then there's this: http://arstechnica.com/security/2015/08/dram-bitflipping-exp...
And this looks to execute some shellcode (but maybe it doesn't work): http://stackoverflow.com/questions/381171/help-me-understand...
Regardless, the bottom line is clear: if you value security and privacy, you disable JavaScript.
Even with the same-origin policy, the default behaviour of a web browser is to execute code it downloads from a remote site (i.e., remote to your computer); as it turns out, this is an utter disaster for security and privacy, turning what is a relatively securable platform (HTML+CSS) into a nightmare.
It is not, today, possible to be secure and private while allowing JavaScript. That's a problem.
CSS only design is an important piece of a future web with reduced security and privacy threads.
The (interesting) model of allowing remote code execution per default was a beautiful, but naive vision. We have to make big advances in technology, politics and society to make this model work in a way that does not make internet users victims by default. We are not there yet. Reality is: the crooks destroyed that vision and are advantaged by the current situation, while all internet users are being trapped in their first moment of browser usage without their consent or knowledge.
For many use cases, (e.g. government websites, banking, anything where you type in your name) css-only design should become a requirement by law to protect the user until we figured out how to write secure software that respects user privacy and how to form governments that will respect their citizens (possibly will take longer). Until then browser vendors should implement more and better possibilities for CSS that help to avoid JavaScript whenever possible.
I very much like JS animations and stuff happening in the browser window, also there are some edge cases where JS brings some important advancements to a UI, but we have to face that privacy and security are much more important issues than having a nice UI and we have to change the current situation, as we, as programmers, are responsible for it.
The "remote-execution-by-default" experiment has failed, we need to change that, and CSS is a great way to go on with a web that might be less problematic for everyone, but still offers very nice usage experiences.