News for hackers. Stuff that matters.

yashap

Re:GitHub Actions Is Down on Thursday August 06, 2026 @06:30PM (#49203516)
We use other runners (Blacksmith), and it hasn't helped, still hard down all day long. Brutal outage.

As a side note, I started getting these symptoms (actions staying queued forever or not running at all) at 5pm PDT yesterday, intermittently. And definitely full outage by 8:30pm PDT. So for sure full outage for 7 hours and counting, even if you use other runners, and I strongly believe partial outage for ~15.5+ hrs before that, even if it hasn't been acknowledged by GitHub yet.

Re:GitHub Actions Is Down on Thursday August 06, 2026 @02:37PM (#49200564)
Yeah who knows, would be interesting to hear an inside take if any readers here are also GH devs!

They're at 93.91% uptime over the past 90 days, according to https://mrshu.github.io/github-statuses/ , and that doesn't even include today's outage yet.

A glorious one nine of reliability.

Re:GitHub Actions Is Down on Thursday August 06, 2026 @02:30PM (#49200490)
It's honestly insane how terrible their reliability is. Over the past 4 weeks, 8 days with GitHub Actions outages, many of them multi-hour outages: >3 hours on each of July 9th, July 20th and today, and 1.5 hrs on July 23rd.

Outages happen, but this many outages so close together, and so many of them so major/long lasting, something is systematically wrong for sure. It's been seriously hamstringing our ability to ship code at my company.

Re:People are just as bad as my LLMs on Monday March 10, 2025 @06:10PM (#43326689)
Hmm really? Even on the Wikipedia page for 7 (https://en.m.wikipedia.org/wiki/7), one of the first things it says is “7 is often considered lucky in Western culture and is often seen as highly symbolic.” And FWIW you can see the Wikipedia edit history, that isn’t a recent edit, nobody here is messing with it :)

“Lucky Number 7” is a common phrase, there was even a popular movie that played on this, “Lucky Number Slevin” (https://m.imdb.com/title/tt0425210/). It’s one of the first numbers I’d think of as a “lucky number.”

Re:A Marriage Proposal Spoken in Office Jargon on Wednesday January 15, 2025 @06:06PM (#42718482)
This is great :) Also if anyone else is hitting New Yorker paywalls and can't read this, just disable JavaScript and reload.
Re:Shortest times between train stations in Europe on Sunday December 29, 2024 @12:24PM (#42541312)
Ah brutal. Has it got worse recently? Been years since I’ve taken the train in Germany, but they used to be pretty good IMO.
Re:Shortest times between train stations in Europe on Saturday December 28, 2024 @01:49PM (#42533398)
Huh really? Whenever I’ve taken the train in Germany it’s been pretty punctual, and looking at the board that’s been the case for most trains. But maybe I just got lucky and/or it’s changed over time.

Flakiest trains I’ve experienced anywhere in Europe were in Italy - rolling strikes among train workers are crazy frequent and cause so many delays and cancellations.
Re:Does current AI represent a dead end? on Friday December 27, 2024 @01:38PM (#42524720)
I hope so, but for different reasons. Agreed they spit out plenty of gibberish at the moment, but they’ve also progressed so far so fast it’s pretty scary. If we get to a legitimate artificial general super intelligence, I’m about 95% sure that will be terrible for the vast, vast majority of humans, we'll be obsolete. Crossing my fingers that the current AI surge stops well short of that, and the push that eventually does get there is way, way off into the future.
Re:JSON5 – JSON for Humans on Monday December 09, 2024 @04:05PM (#42370546)
I want to be able to easily read and understand configuration without having to pop it into a converter. The YAML I encounter in the wild is ~80% pure block style, ~20% mixed (within a single file, mostly block style with some flow style). And I just find the block style hard to read, I have to either spend significant mental effort trying to understand where the objects vs. arrays are, or I have to pop it into a converter (to either JSON or flow style) to understand. Whereas JSON/JSON5, it’s immediately clear without any mental overhead.
Re:JSON5 – JSON for Humans on Monday December 09, 2024 @10:44AM (#42367246)
Don’t have any experience with them.
Re:JSON5 – JSON for Humans on Monday December 09, 2024 @02:26AM (#42363757)
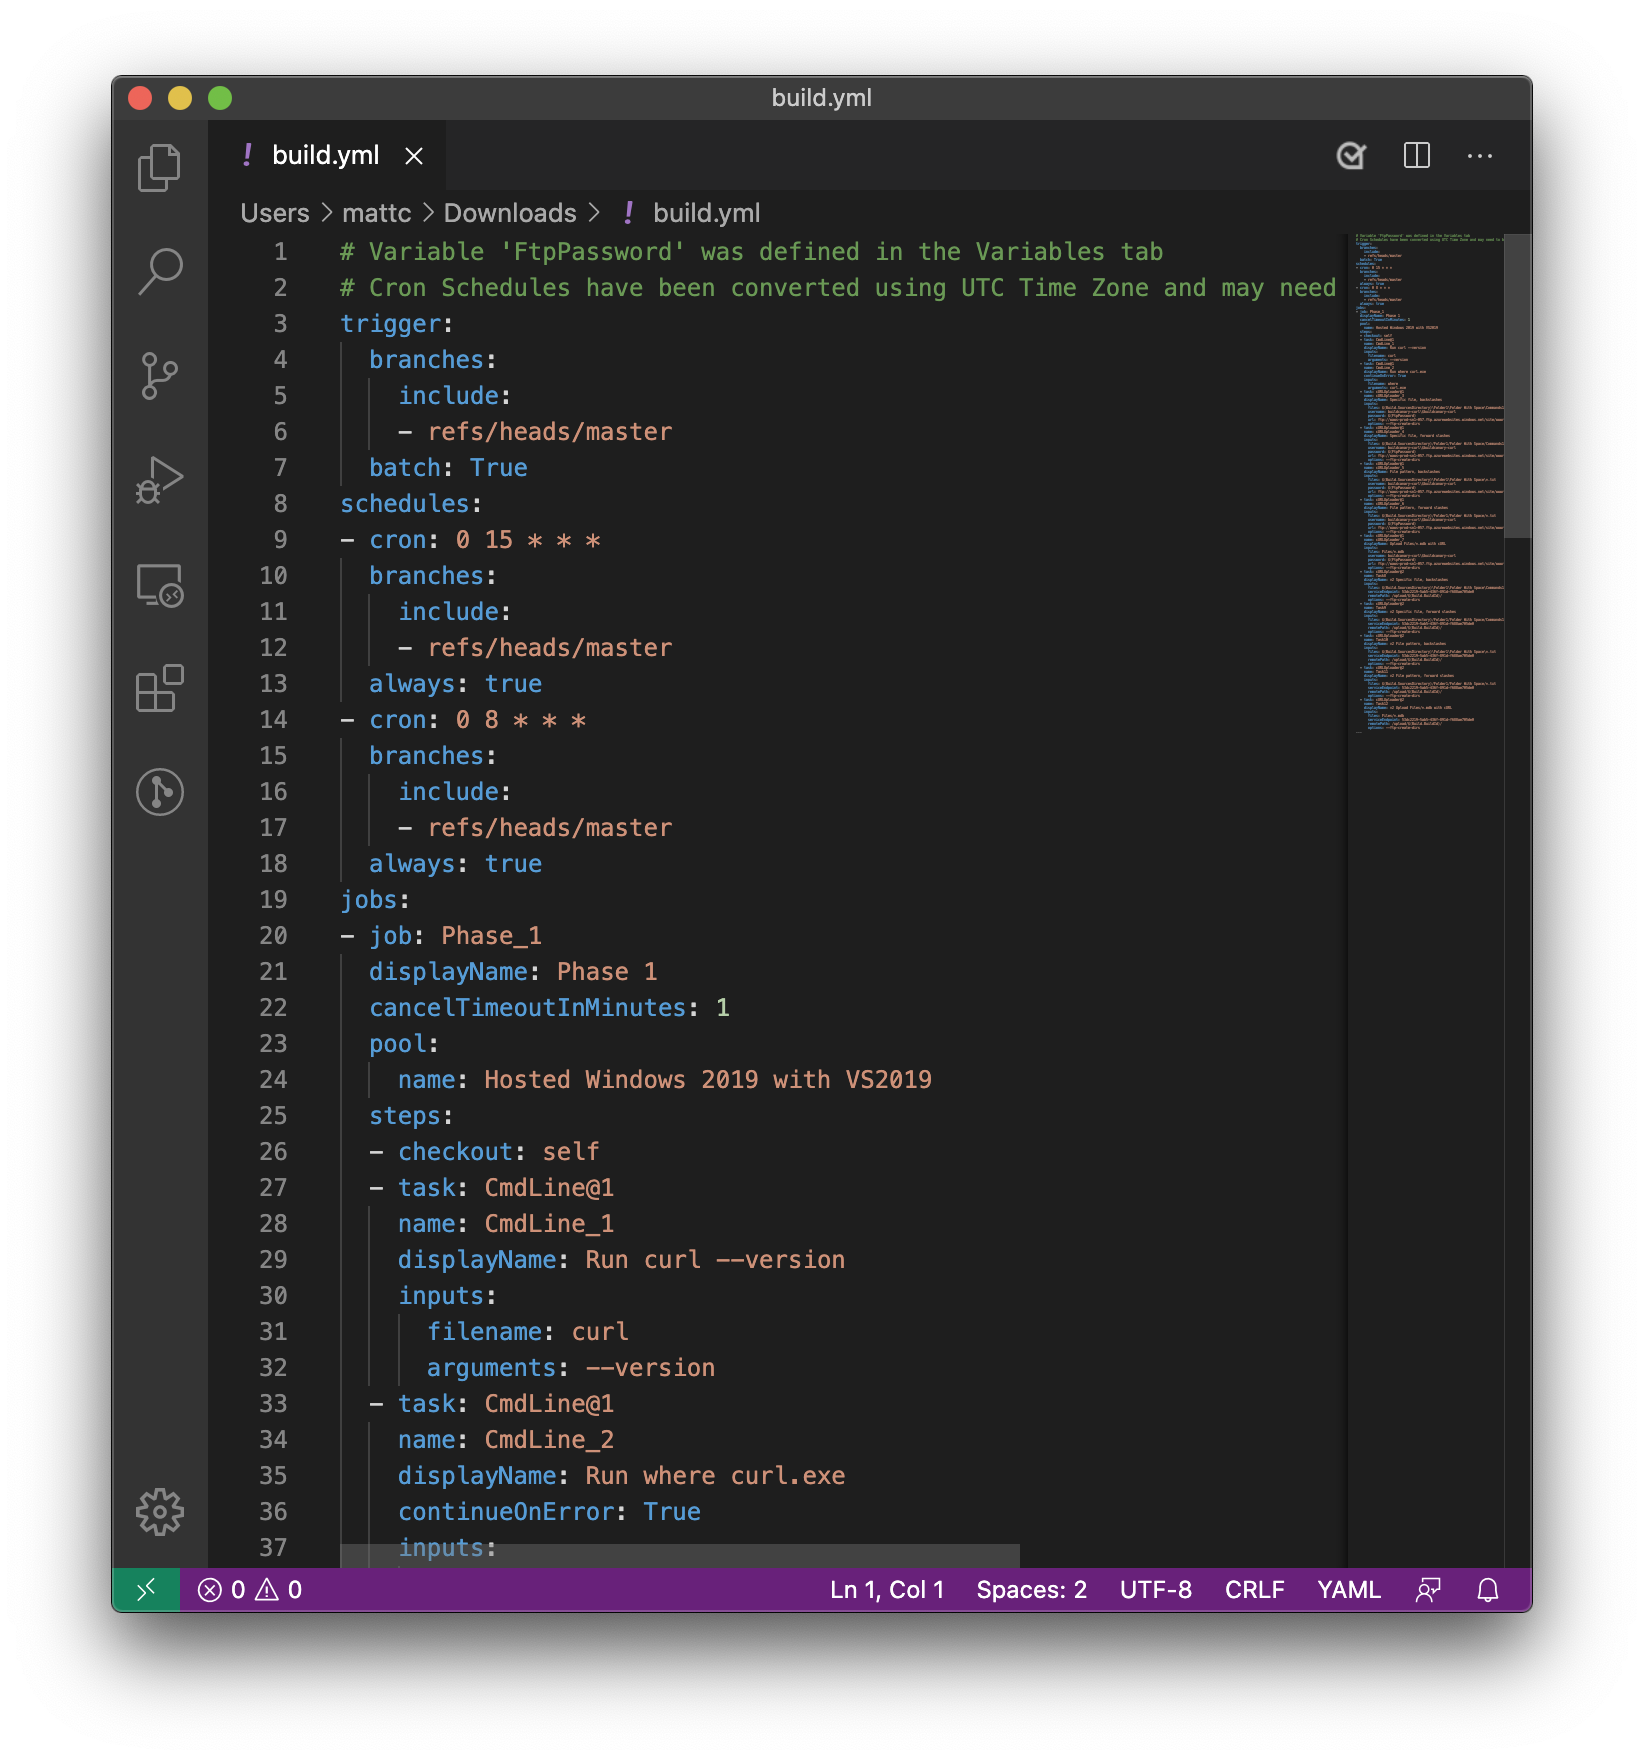
For sure, but most YAML you actually encounter does not use much in the way of JSON syntax, it looks a lot more like this: https://devblogs.microsoft.com/devops/wp-content/uploads/sit...

Where arrays and objects just look too similar (IMO), white space is significant, most strings are unquoted, etc. And personally I find it quite difficult to really understand what’s going on there, at a glance, compared to JSON (or JSON5).

Re:JSON5 – JSON for Humans on Sunday December 08, 2024 @05:21PM (#42361188)
Fair, YAML has a lot of usability warts, and those suck too. Although personally I really do hate how tough it is to tell apart arrays and objects, at least with the most common YAML array/object style.
Re:JSON5 – JSON for Humans on Sunday December 08, 2024 @05:13PM (#42361119)
I’m a fan of JSON5. A common criticism is “we’ve already got YAML for human readable config with comments,” but IMO YAML’s readability sucks, it’s too hard to tell what’s an object and what’s an array at a glance (at least, with the way it’s often written).

When dealing with large YAML files, I find myself frequently popping them into online “YAML to JSON” tools to actually figure out WTF is going on. JSON5 is much easier to read, at least for me.

Re:Shrunked JavaScript monorepo Git size by 94% on Sunday October 27, 2024 @02:50AM (#41960363)
They’re probably downloading from a server in the states, being much further away makes a big difference with a massive download.
I think you’re reading way, way too much into this. Read the piece and it seems like just a goofy little oddball story, makes for a light and enjoyable read, I’m really not picking up any political angle in this piece.

The Guardian are certainly a left-leaning, frequently political paper, but that doesn’t mean every story is political, and IMO this one isn’t.

Agreed, it’s a lose-lose situation really. But the reason most companies just settle is that going to trial is so expensive, and the American legal system allows these frivolous lawsuits while generally awarding either no compensatory damages, or damages far below the cost of the defence.
You can see why, though. Even in this case where they thoroughly won, and got damages, the damages were just $225K, and they probably spent millions on legal fees, employee/founder time, etc.

Ultimately, the American legal system is pretty broken. If someone brings a frivolous lawsuit against you, and you defend yourself in court, nearly 100% of the time you’ll be losing money, often a lot of money. This is the core reason why patent trolls exist, why companies normally settle out of court - it’s cheaper to do so.

Re:How to avoid a BSOD on your 2B dollar spacecraft on Thursday September 26, 2024 @11:57PM (#41666112)
Ah fair, definitely a very different environment than what I’ve worked in! Have only worked on SaaS, where all forms of testing (automated and manual) are a thing we do internally, without customer involvement. We’ll do things like turn features on/off for customers, have them provide feedback, but that’s more product feedback than them being part of the testing/QA process.

I have worked on software where individual customers pay millions for it, but not billions, and it’s also not a physical thing that can literally crash into earth or fly off into space if something goes wrong!

Re:How to avoid a BSOD on your 2B dollar spacecraft on Wednesday September 25, 2024 @08:21PM (#41653230)
I enjoyed the humour, and the content. Personally I wouldn’t change it - it’s kind of a click-bait title, but I never would have read the article if it had a boring title, and I am glad I read it.
Re:How to avoid a BSOD on your 2B dollar spacecraft on Wednesday September 25, 2024 @08:04PM (#41653151)
Indeed, and it’s clearly stated in the article:

> Safemode is the satellite equivalent of a blue screen of death.

It’s about avoiding safemode, and more generally about the end-to-end QA/testing process for satellites before they’re sent up into orbit. It’s very clearly not about actual Windows BSODs, it’s just written in a tongue-in-cheek style. Those commenting about “wtf windows on a spacecraft” clearly didn’t read the article, just read the title.

FWIW I found the writing style engaging and the content interesting. I guess the title is a little click-bait-y, but not in a way that I minded much, and I probably wouldn’t have read an article titled “How to avoid safemode on a satellite.”

I did think it was pretty wild that customers have to be informed of every incident where a satellite flips into safemode in TESTING! In normal operations, sure, but in testing, that’s wild. Feels like having to report bugs caught in my local dev environment, that were never deployed to prod.

Re:Drift towards danger and the normalization of deviance (2017) on Thursday September 19, 2024 @03:45PM (#41595621)
> I have not found an answer for testing React components that seems like a good use of resources > … > I'd really love to have a system that would give me a heads up that some CSS I changed has a spooky effect on a distance on part of the UI because of the complexity of selectors but that's asking a lot

I would’ve agreed until recently. I always found basically all other forms of testing valuable (unit tests of almost everything on the BE, unit tests of FE business logic, BE integration tests, E2E tests), but not testing of the visual elements of the FE.

But the company I work at, ~6 months ago we gave this product a try, and honestly it’s pretty incredible: https://www.meticulous.ai/

They basically record sessions of real usage in our staging environment, and then replay them against your branch, like taking all the same interactions, and mocking responses to all network calls. It records tonnes of these sessions and is very smart about which ones it uses for a given change. It flags any visual differences, and you can OK them (or not). There’s a bit of work to initially integrate, but then you don’t write any tests, and you get pretty amazing coverage. It has the odd false positives, but not many, and they’re easy to review/approve in their web UI. They’re also a small startup willing to work super closely with you (we share a Slack chat with them, they’re very open to feedback and iterating quickly on it).

I swear I’m not a paid shill or affiliated with them in any way, just a user who really loves the product. I was skeptical it’d work well at first, but it’s honestly been great, has caught many potential regressions, I feel we’re getting much better coverage than we would with handwritten UI tests. It’s very worth a look IMO if you’re not satisfied with your visual tests. It’s not an E2E testing tool, because the network requests are recorded/replayed (so it can’t stop BE changes that break the FE), but it’s amazing for testing so many elements of the FE.

Yeah, it’s a clickbait title. Reading the article:

- Until 2010 US submarines had exclusively male crews

- Since then more and more subs have had both male and female crew members, but the subs themselves were still designed for men

- This sub was designed to have a mix of male and female crew, which in practice means things like design tweaks around washrooms, sleeping areas, and making overhead valves easier to reach

Re:How economical is your local Taco Bell? on Wednesday September 11, 2024 @12:11PM (#41512737)
I’ve never used it, but I’ve used the Starbucks app a bunch. Order on the app when I’m 5-10 mins away, and can just roll up and grab my food/drink, vs waiting in line, ordering/paying, then waiting for prep. Useful when you’re tight on time or just don’t feel like waiting. I assume the Taco Bell app is similar.
Re:Ilya Sutskever's SSI Inc raises $1B on Wednesday September 04, 2024 @11:50AM (#41447202)
The successful companies that came out of the dot com bubble era actually proved their business viability before getting investment, though.

Amazon is one of the most famous successes of the era. Bezos quit his job, launched the business out of his garage, with seed money being $10K of his own savings, and was doing $20K/week in sales just 30 days later. And I believe their only VC round before going public was an $8 investment from Kleiner Perkins. But they were a company who proved their viability early on, had a real product with rapid revenue growth before getting any VC $$.

I’d say this SSI round is more similar to Webvan, who went public with a valuation of $4.8 billion, and at that time had done a grand total of $395K in sales, with losses over $50 million.

I’m sure there are good investments out there for AI companies that are doing R&D and advancing the state of the art. However, a $1 billion investment at a $5 billion valuation, for a company with zero product or revenue, just an idea, that’s nuts, and extremely similar to the type of insanity we saw during the dot com bubble. Even more so given that SSI seemingly don’t even want to be a business, they’re saying “we aren’t releasing any sort of product until we develop safe artificial general super-intelligence.” So their plan is to be a total non-business unless they become the first people to hit an incredibly, incredibly difficult milestone.

Re:Ilya Sutskever's SSI Inc raises $1B on Wednesday September 04, 2024 @11:08AM (#41446682)
Agreed, the AI bubble is very, very real. Not that LLMs are all hype, they’re certainly impressive with useful applications, but AI companies are getting insane valuations with zero proof that they’re viable businesses.
Re:Defenders think in lists, attackers think in graphs (2015) on Saturday August 24, 2024 @08:14PM (#41343081)
Hackers are global, though, and no matter what country you’re in, almost certainly the vast majority of hackers attempting to attack you are doing so from outside your country. Enforcing laws on a global scale is extremely difficult and almost impossible to do effectively.
The platform is absolutely overrun with bots and extreme racism and sexism (as well as extremely racist/sexist bots). It’s a complete tire fire, advertisers are pulling out en-masse because they don’t want to be associated with this cesspool, non-bot users are fleeing, the company is outright tanking.

Musk bought it for $44 billion in October 2022. Over the first 13 months under Musk, we saw X internal memos marking themselves down to $19 billion, then Fidelity marked down their investment to a level implying a $15-16 billion valuation, then in November 2023 they marked it down again to $12.5 billion. All signs point to it losing even more value since.

I’d be surprised if X doesn’t declare bankruptcy within the next few years, Musk has rapidly taken it from social media giant to poor man’s 4chan.

Hmm fair, I’ve mostly just compared it to Ory Keto, Keycloak and FusionAuth, and it was my favourite so far, was the easiest to use/quickest to integrate for me. But it’s definitely personal, and it’s also a space with a tonne of players, have only tried a handful!
I think the “developer friendly” critique is a fair one for Ory, especially Ory Keto, which I found to be an absolute nightmare to use. But as a dev I found SuperTokens really easy/nice to use.

Open core vs. full open source, fair.

How would you compare yourselves to SuperTokens (https://supertokens.com/)? I ask because they’re another open source, YC backed auth system, and one that I’ve quite enjoyed using on a side project. There seem to be a lot of similarities between you two, would be interested to hear your take on the differences!

Older »