dns_snek
If you have to specify everything in text and you don't intend to actually communicate anything through graphics and if you only focus on pure, sterile mathematical functions which don't have an ideological component that could be biased to begin with... then surely you can see that your statement is the trivial one.
> The graph still shows the function in that domain neutrally
The key word being "in that domain". You can use the same excuse every time you mislead people with statistics. The fact that your choices can mislead people proves that they're not neutral.
> Our [new] approach to containment starts with a paramount requirement: the limits on what an agent can access must hold even when the agent tries to circumvent them. We define a strict security boundary around the resources the agent is authorized to use and design the surrounding infrastructure to enforce that boundary—even when agents make sustained, sophisticated attempts to breach it.
https://openai.com/index/securing-our-frontier-model-trainin...
https://news.ycombinator.com/item?id=50173902
https://news.ycombinator.com/item?id=49355370
https://news.ycombinator.com/item?id=49363163
https://hn.algolia.com/?dateRange=all&page=0&prefix=true&que...
The founder of Murena strongly implies that the difference between /e/ and GrapheneOS is that GrapheneOS is designed to protect pedos, for example. I think that explains a lot.
https://www.clubic.com/actualite-604786-murena-e-os-intervie...
You can run wireguard in userspace with something like wireproxy which connects to a wireguard peer and acts as a proxy for your subprocess.
It's not like those horrible synthetic THC analogues we see in Europe that can kill people.
I think this has been misreported and it's even worse, EU register of infrastructure says that maximum permitted speed for this section is 270km/h and the sections before it are even higher.
https://rinf.data.era.europa.eu/unified-search?view=map&q=JT...
What do you mean? Here's one published last year:
> This study does not provide evidence to support the use of school policies that prohibit phone use during the school day in their current form, given that no differences were observed in mental, physical, and academic outcomes for adolescents attending schools that permit, versus restrict phone use. However, the negative associations found between increasing time spent on phones/social media and worsened mental health and wellbeing do provide evidence on the need to address phone and social media use in adolescents, and school policies should be developed as part a more holistic approach. [...]
https://www.thelancet.com/journals/lanepe/article/PIIS2666-7...
This study doesn't say anything about the effects of social media on students.
It finds that phone bans in schools are not associated with measurable improvements in mental health. This is not the same as saying that social media and phone use aren't harmful, it only means that phone bans in school don't independently improve mental health outcomes.
A similar study from a couple of years ago [1] reached the same conclusion, however they had more data which exposed the hidden correlation (emphasis mine):
> Implications of all the available evidence
> This study does not provide evidence to support the use of school policies that prohibit phone use during the school day in their current form, given that no differences were observed in mental, physical, and academic outcomes for adolescents attending schools that permit, versus restrict phone use. However, the negative associations found between increasing time spent on phones/social media and worsened mental health and wellbeing do provide evidence on the need to address phone and social media use in adolescents, and school policies should be developed as part a more holistic approach. Preventative efforts should also consider how other behaviours that influence mental health and wellbeing are influenced by increased phone/media use, such as sleep, physical activity, attainment, classroom behaviour and problematic use.
[1] https://www.thelancet.com/journals/lanepe/article/PIIS2666-7...
The author has provided an APK that claims to do just that. Hacking tools aren't allowed on app stores, no, but that has no bearing on the severity of vulnerabilities they exploit.
> And do any carriers actually let it go through their network and to a device like a normal message? It's entirely possible the malformed message would crash some software in the carrier's processing stack first and so never be delivered.
Apparently, unless you're accusing the author of lying.
> And if it doesn't, they could easily add a check to block such messages.
Your ISP could block RDP but that doesn't lessen the severity of RDP vulnerabilities, shift responsibility, or lessen the need for the vendor to respond in any way, that's not how this works.
This is an Android vulnerability and it should be assumed that the carrier is indifferent, actively hostile, cooperating with law enforcement to carry out this attack, or someone might carry out this attack using an IMSI catcher.
> It's difficult to believe they don't already have some sort of protection against spamming tons of messages to any device.
20? I doubt it. Do you think the author is lying?
> It's also entirely possible it works differently on different carriers, and some but not others might add blocks for this
Indeed. What's indefensible is Google's classification that this isn't a security vulnerability.
Are there systems that can warn drivers and prevent collisions without external signaling, like ACAS?
If signaling worked properly then it wouldn't matter whether the train was driven autonomously or not, the "problem" becomes trivial. Establishing and continuously verifying that signaling is working properly is the hard part.
Without signaling you're limited to crawling speed just like humans are when they don't have any signalling .
Most notably agents like Claude Code and Codex? Easy to check if you ask it to run:
    $ curl 'https://dv-g3b-emudhra.we-have-a-problem.com/'

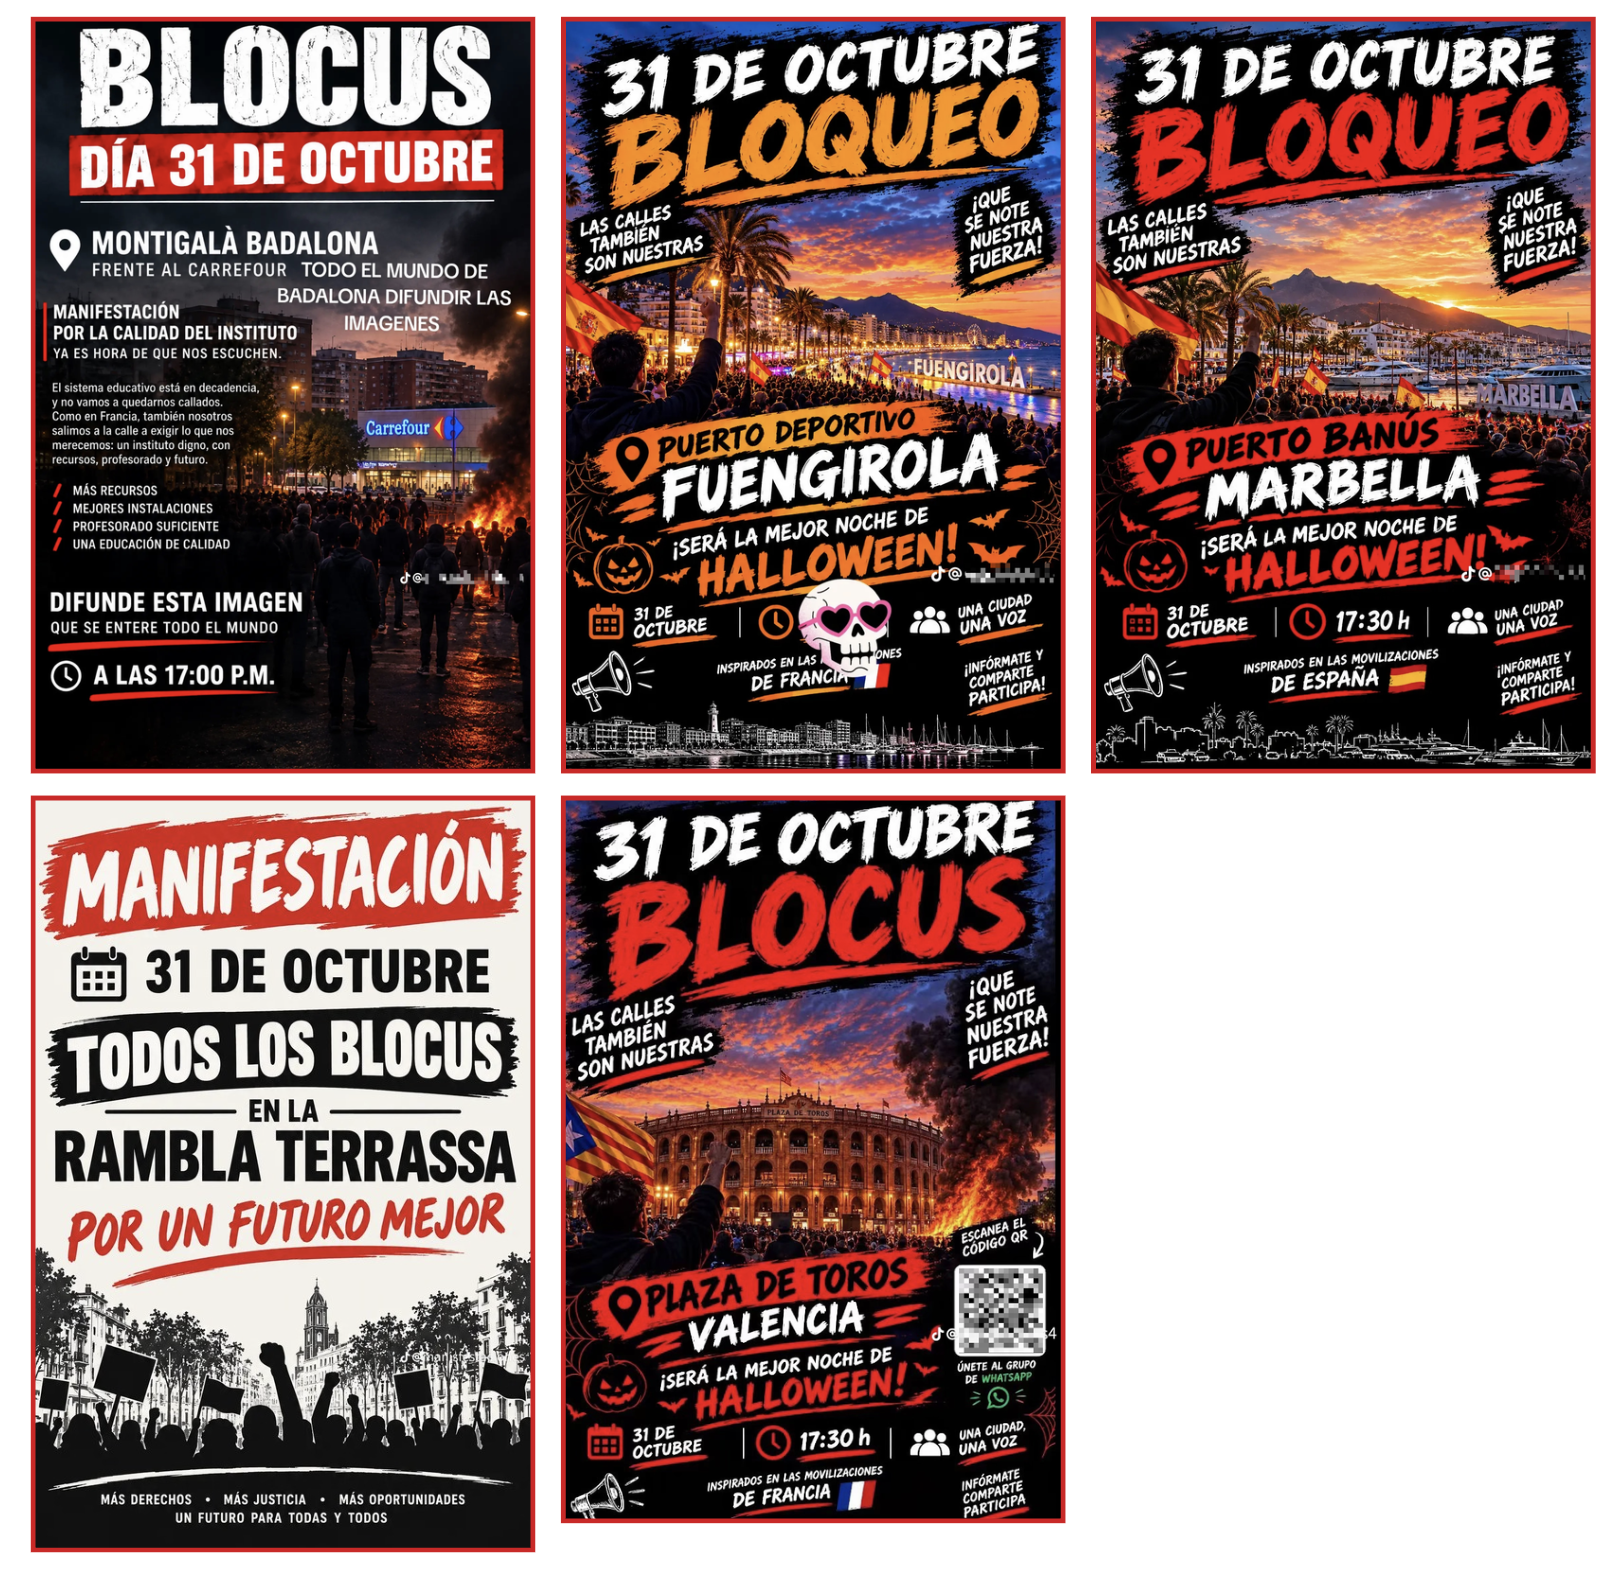
Your client successfully connected to the site. That's bad!Spain: https://files.maldita.es/uploads/2026/10/6adf4cb02eb11captur...
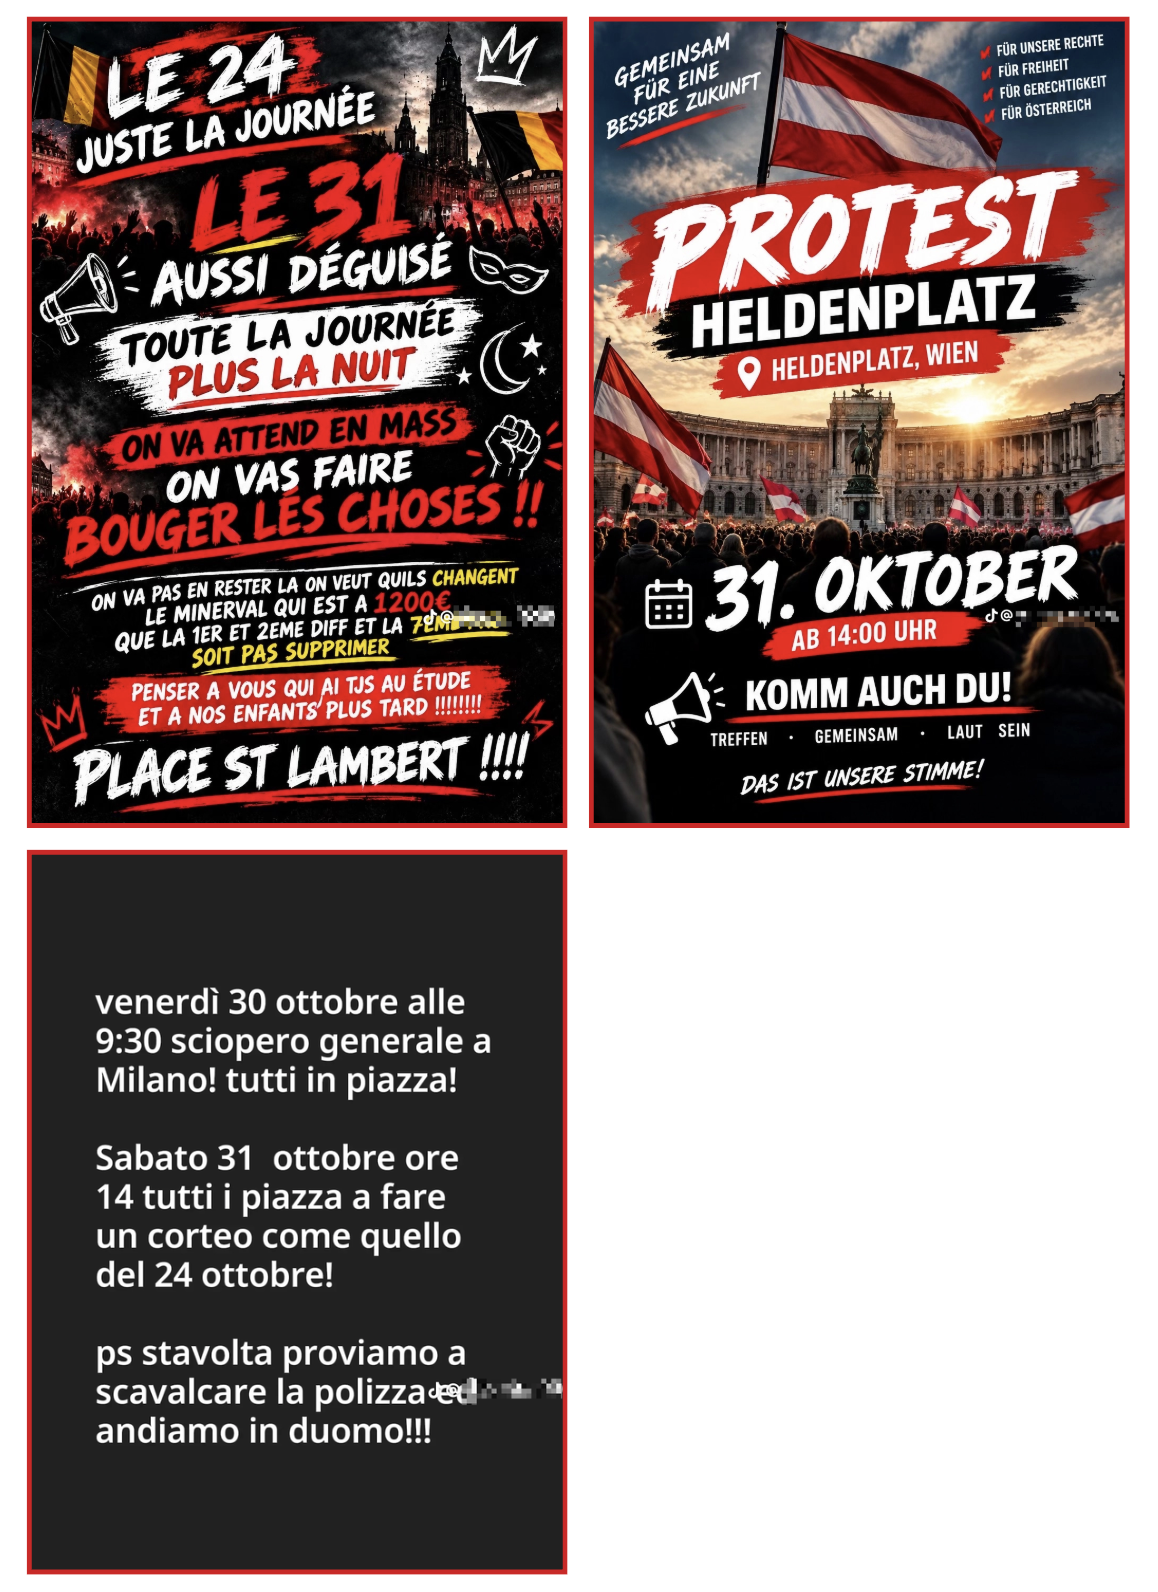
Belgium and Austria: https://files.maldita.es/uploads/2026/10/6adf4cdc68db4captur...
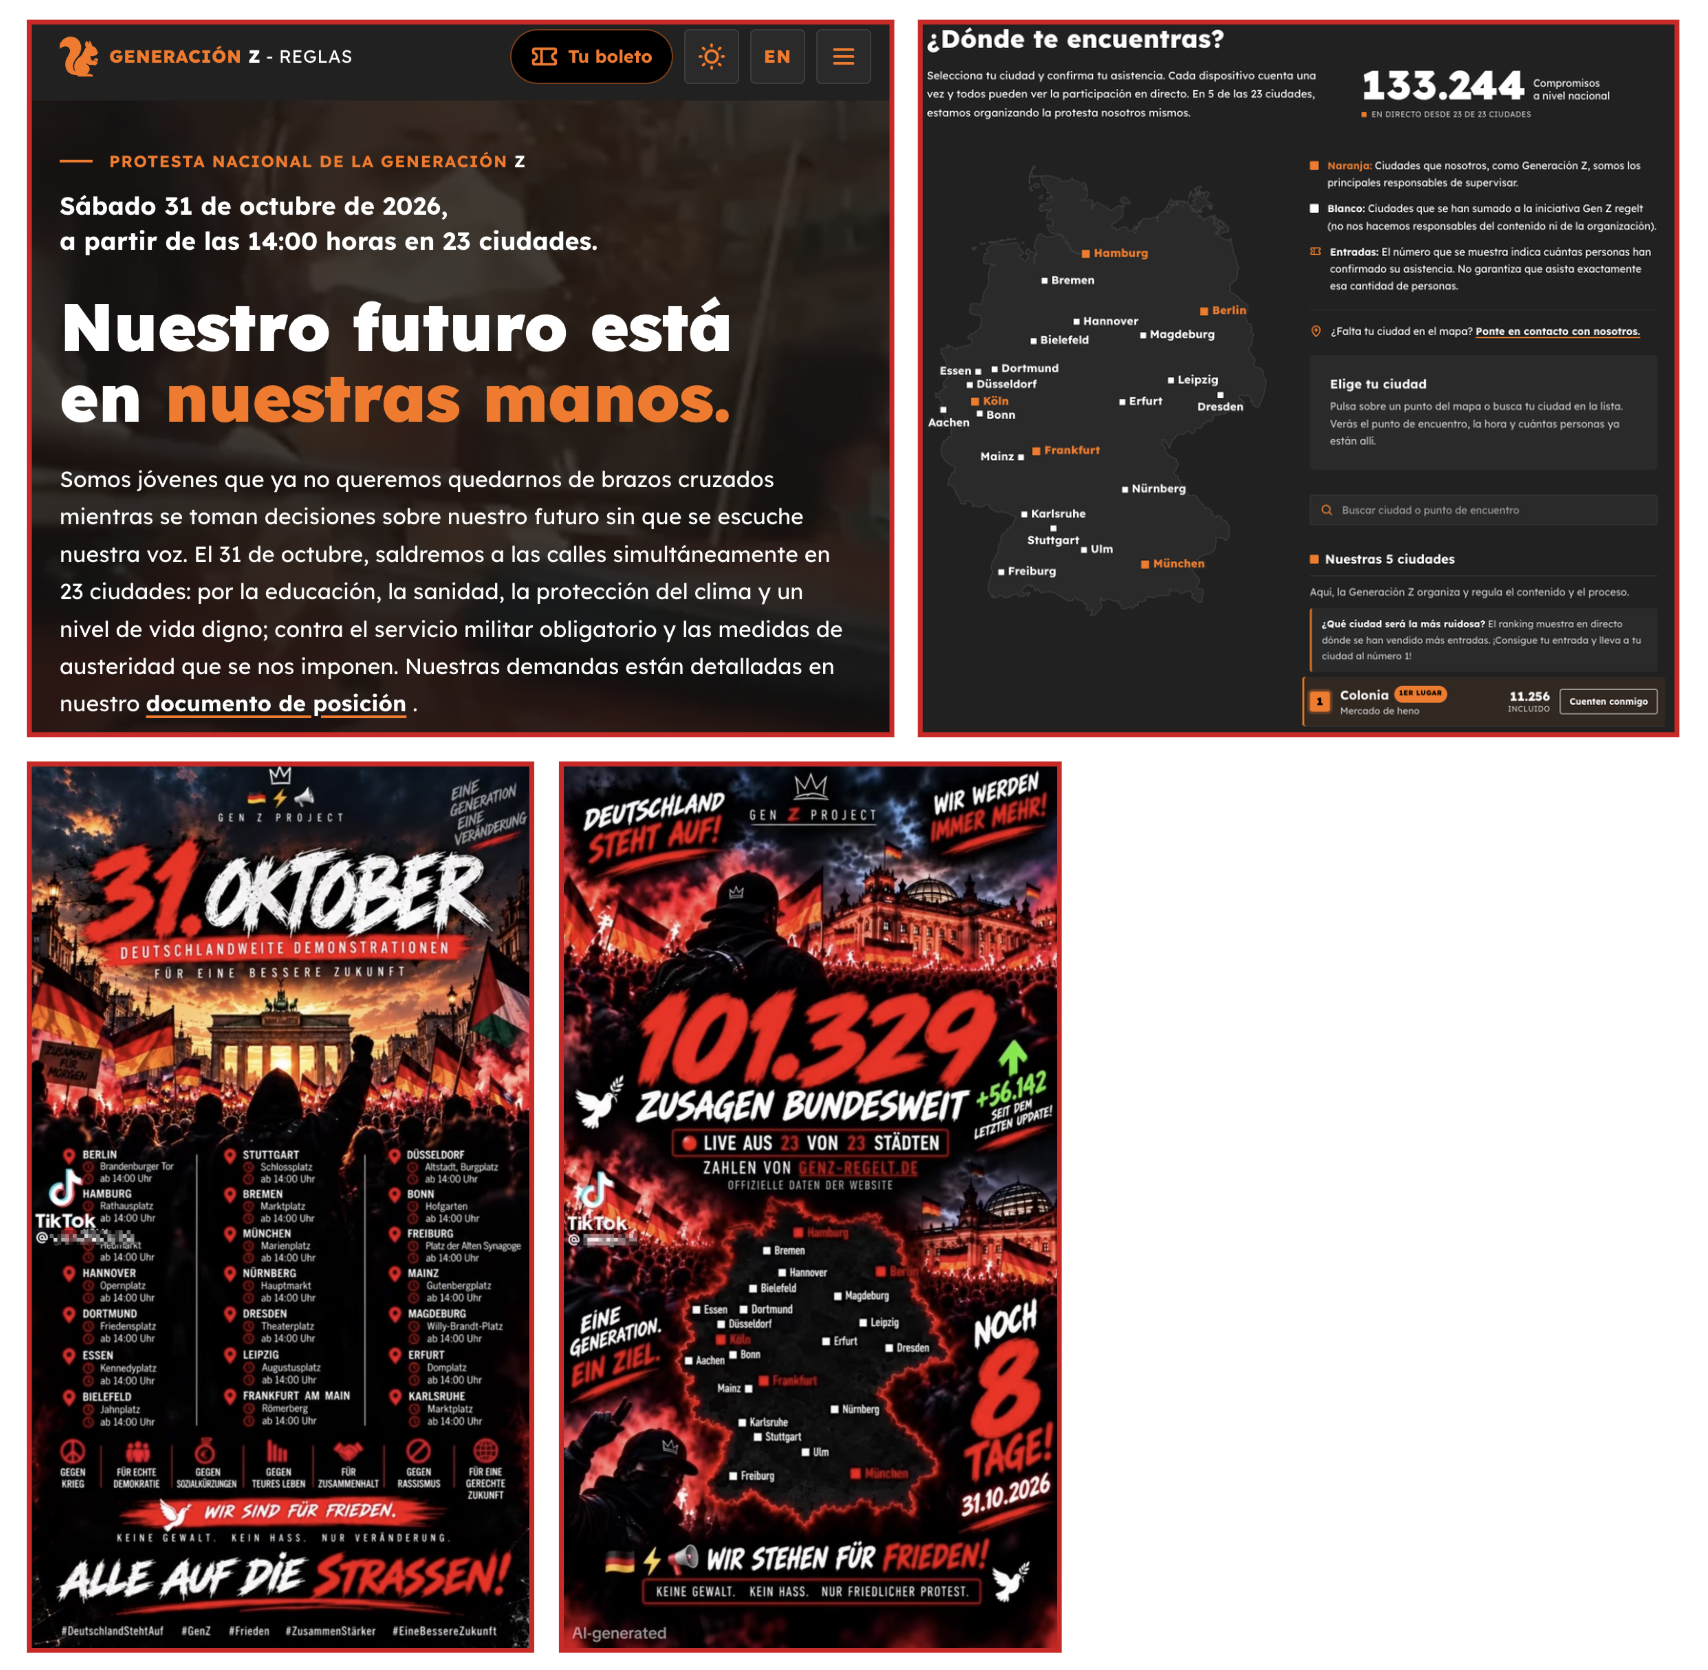
Germany: https://files.maldita.es/uploads/2026/10/6adf4ccfdee54captur...
France and Germany (inciting violence): https://files.maldita.es/uploads/2026/10/6adf6524f4131pasted...
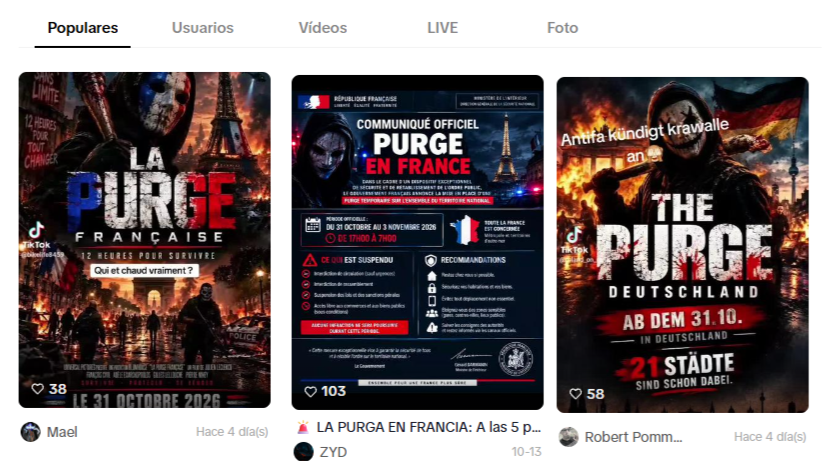
^Source: https://maldita.es/investigaciones/20261026/tiktok-manifesta...
There are more of these posters circulating and calling for protests in every European country that locals know nothing about and never actually happened (i.e. Oct 17): https://www.tiktok.com/@genz.rights/photo/769540155445459688...
I jest, but you're describing authentication protocol which uses the UDP destination port field to carry each character of the "one time password" in a roundabout way. You could simply send 1 packet containing the password to the daemon.
I've never seen it used in the wild but apparently, it exists: https://github.com/mrash/fwknop
Throwing out food that was at 6 °C for 2 hours without tasting it is really paranoid, the answer should be "it depends". If not following government advice/requirements on safe storage conditions (which is tailored to high risk populations) meant certain illness then I would be seriously ill at least once a week, but I've never been.
I would be waaaay more worried about catching a norovirus from someone who didn't wash their hands than raw meat being kept at 4-8C for 12h.
Either way the comparisons here are unfair. An LLM that runs off a backpack-sized solar panel and a laptop might be a substitute for a broad, low quality, surface-level encyclopedia but it's many orders of magnitude worse than a library of books.
I would argue that in a survival situation the accuracy of information becomes even more important. If an LLM to misidentifies a plant (or a medical condition, its treatment, etc.) it could put you in an ER, but in a survival situation that could kill you.
> Specific configurations should not impact any attribute contributing to the CVSS Base metric assessment , i.e., if a specific configuration is required for an attack to succeed, the vulnerable system should be assessed assuming it is in that configuration. [1]
For a vulnerability to score a 10 its Attack Complexity must be 'Low' (broadly speaking: it doesn't require target-specific customizations or mitigations [1]), which isn't the case with php2shell.
Here's a breakdown of that 9.2: https://www.first.org/cvss/calculator/4.0#CVSS:4.0/AV:N/AC:H...
[1] https://www.first.org/cvss/v4.0/specification-document#Attac...
First you incorrectly claimed that multi-line RUN commands aren't supported still require that ugly legacy syntax. When that was proven wrong, instead of saying "good, I wasn't aware", you went on a tangent about its adoption and wanted to interrogate my knowledge -- Yes, obviously I know that running all commands in one RUN block is beneficial because it reduces layer count and image size.
Your revolutionary idea of "transactions" is already implemented through multi-stage builds. Except those are even better than transactions because individual steps are still cached, independent components can be built in parallel and they don't invalidate each other's cache. Finally the artifacts are copied into the final image, leaving behind unnecessary layers.
It is all but certain there are exploitable memory issues in Chrome, Firefox, Node.js, Linux kernel, Nginx, etc.
Can we expect CVEs in a few hours? I'm sorry I ruined everyone's weekend.