MiWDesktopHack
Thank for following this up. I think you are right. RH SWS was EOL before the Dual_EC default switch was made. If the only public banners for this product are from before this time, I will conceed that DUAL_EC likely never saw use on the Public Internet.
Pls unblock me on twitter ;-)
Dual_EC was default PRNG in BSAFE-SSL-C for almost a decade. Shodan matched 1700 banners from this time, online now. The chance that a person interacted with a https service in that time is quite high I would think.
This seems somewhat related to some work I did last year on using blockchain to 'register' and provide distributed revocation of certs. I called it UTXOC or Unspent Transaction Output based Certificates
https://github.com/MiWCryptoCurrency/UTXOC/ Specifically, I called 'self-signed' certs 'Cryptocurrency Bonds' and could be revoked by spending the funds associated with a public key (bitcoin-like address), and others could verify this by inspection of the blockchain.
The difference here is that I was using the cert privkey as as the bitcoin privkey; Problem being that modern browsers don't and likely never will support the secp256k1 curve for EC keys in TLS. I did built a custom NSS+Firefox that did, and it worked, so it is possible. In fact, NSS used to support the full range of EC curves until 2005. https://raw.githubusercontent.com/MiWCryptoCurrency/Certific...
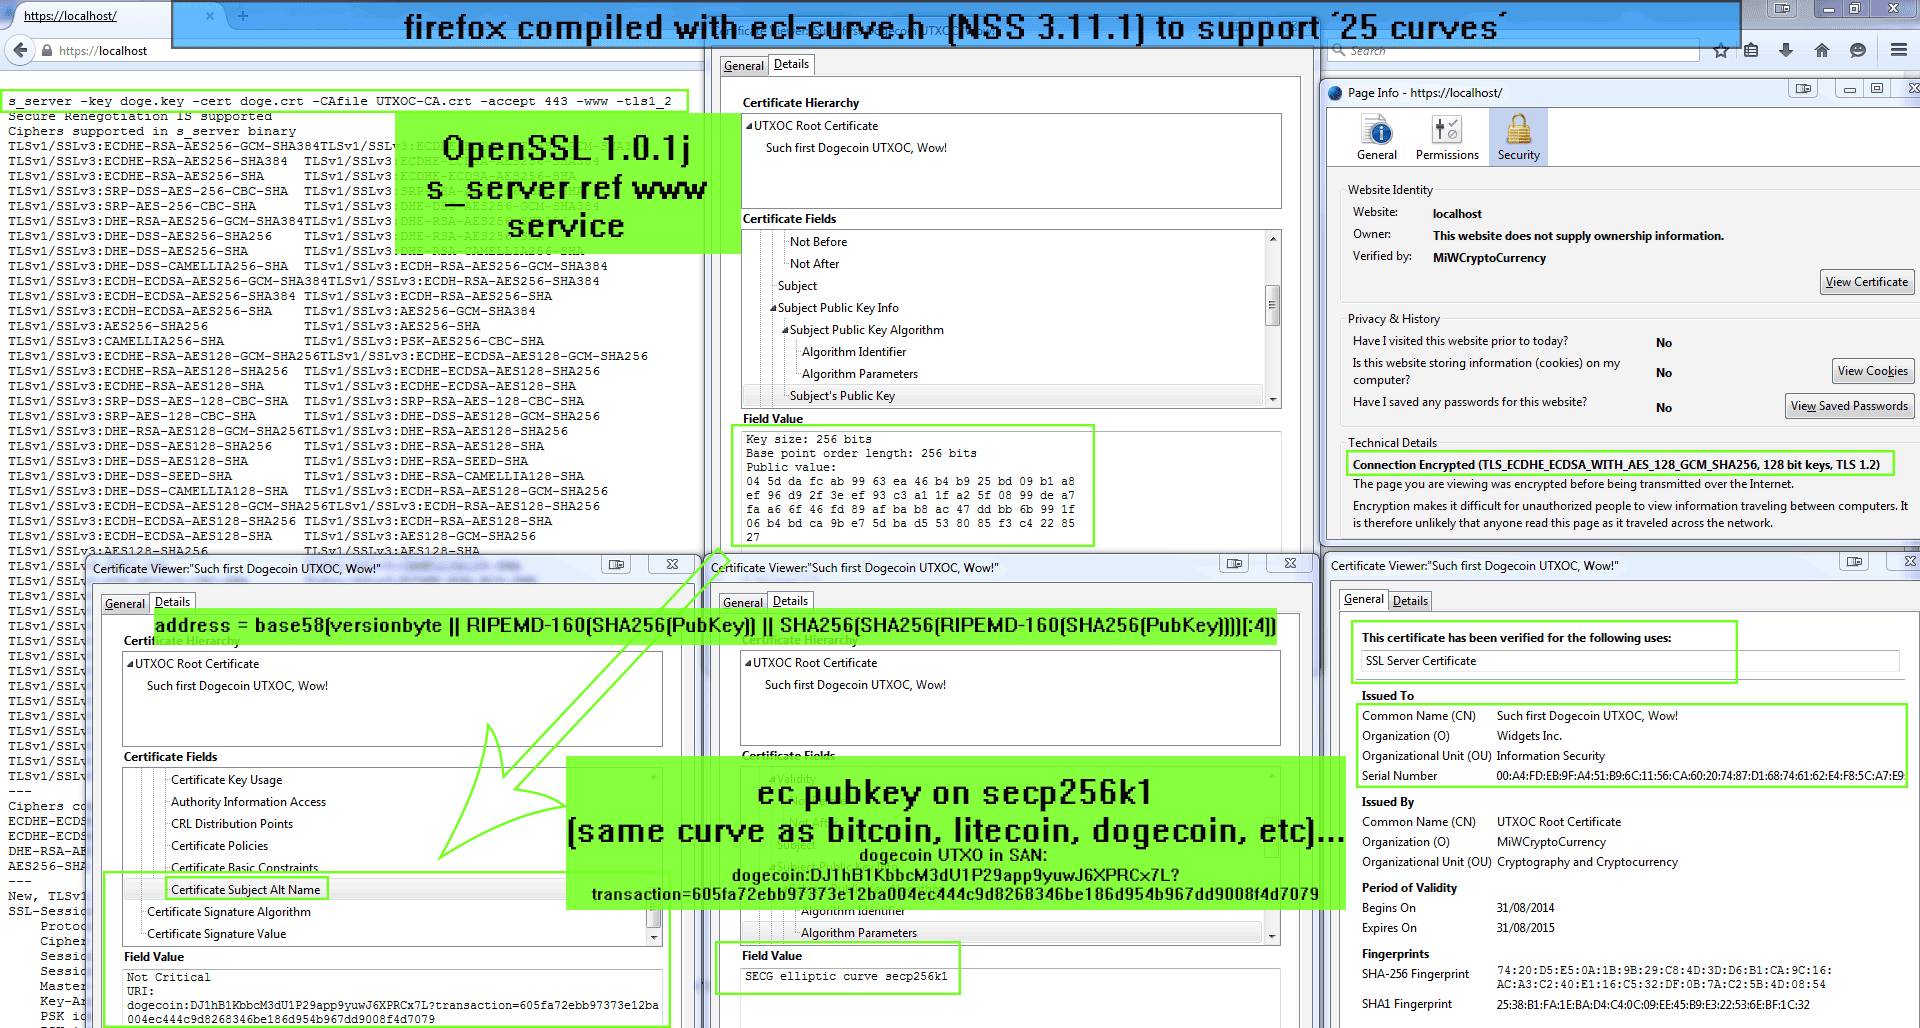
Would be great to discuss your thoughts on using blockchain for x509 and trusts.
A <$1000 bitcoin (SHA-256) mining ASIC appliance is likely to be doing 1TH/s. Makes 2^16 rounds look kinda weak.
This paper was written in 2011, and a lot has changed since then. Today, we have an infrastructure similar to what Certificate Transparency is said to produce -- without collusion or support from the CAs. Bitcoin and other blockchain based technologies have an economic incentive to continue to propagate. I fail to see why anyone other than the CA's would have an incentive for the Certificate Transparency blockchain to propagate.
I proposed an alternative model which i called 'UTXOC'. I wrote a paper and published some python scripts to generate certificates based on a prior bitcoin transaction. A certificate validity can be determined by some bitcoin-like value left unspent. If the value is spent, the cert if invalid. If the private key is compromised, the attacker has an economic advantage in 'cashing out' the value; thus invalidating the certificate. I propose that also adds to the cost of key substitution attacks on TLS; an active MiTM would need to spend at least as much cryptocurrency in order to successfully fake a certificate, even with a trusted root in the client.
It could go either way -- with CA support for such things, or a self-signed 'cryptocurrency bond' style model where TLS operators hold cryptocurrency in order to maintain the validity of their certs.
This is published here: https://github.com/MiWCryptoCurrency/UTXOC
Very interested to hear opinions on this, its a work in progress. Yes, support for secp256k1 is limited in mainstream OS's -- it only works with openssl s_client and s_server currently. Given time I hope that the secp256k1 curve is added to browsers and operating systems, and this or similar blockchain based record architectures are adopted.
thanks all ;-)
Very impressive example of the richness in todays web. Well done loth!
Whomever this is, and they are likely associated with the project as have an associated email, is gathering funds from the projects premined wallets for distribution. Like ripple, they are handing these out to people interested in the technology. I received part of the initial distribution of ripple by posting on the bitcoin forums. I encourage you to make an account, nothing to lose here; the initial distribution of the currency helps with its decentralization.
Paypal used to pay people to make new accounts too!
I had to use this mirror recently as there are already bad copies floating about; it is a trusted hosting for the last ungimped version for windows and linux. check the hashes n' sigs!
  * screenshot of the back office application
  * OSX and Windows back office application binaries
  * btc_xfer_total_summary.txt
  * CV-Mark_Karpeles_20100325.pdf
  * home_addresses.txt
  * trades_summary.txt
  * btc_xfer_report.csv containing every deposit and withdraw
  * mtgox_balances containing the balances of all user wallets
  * trades.zip containing monthly csv files of all trades within mtgox & coinlab between 2011-04 to 2013-11
  * trades csvs have fields:
  Trade_Id	Date	User_Id	User	User_Id_Hash
  Japan	Type	Currency  Bitcoins	Money
  Money_Rate	Money_JPY
  Money_Fee	Money_Fee_Rate	Money_Fee_JPY
  Bitcoin_Fee	Bitcoin_Fee_JPY	User_Country	User_State
This dataset could lead to loss of anonymity to a significant number of people in the cryptocurrency world.
This would not show on any external chain monitors like the story source as most of the trading is occurring within reddit; only when a client cashed out to their wallet would the transaction actually touch the blockchain.
If this cryptocurrency survives, it will be uneconomical to mine by the commoners sometime this year.
They have already got $1USD for this. https://blockchain.info/address/1M7rREovDkdEh4mZrYNgcj1FECRk...
When i first read your post smtddr i got worried we had a collision! Ive found the quality of blockchain auditing in 2013 highly inaccurate. I recently bring attention to the case recently on reddit where someone 'chased' the SMP thief through a tumbler and found... the 96k wallet allegedly owned by btc-e. Its a shame if a non published address of yours has been tainted in someones inaccurate blockchain analysis.
At best you can drop all transactions that are broadcast to the network and generate blank blocks, thus freezing all future transactions.
The greater the hashrate of your miners, the greater probability that your miners will find a valid nonce that satisfies the difficulty equation; it doesn't magically give you the ability to find a valid nonce before any other party. As long as there is one other party mining, there is a non-zero chance that their block will be accepted before yours.
What ratio of malicious/non-useful blocks vs valid, legitimate BTC transaction containing blocks would be required before the economy fails, that is an open question.
Actual youtube link just in case you don't want to visit news corp www's. http://youtu.be/ojIz5Mai2Rw
When my phone finally dies, and I get another one, I won't be able to have the same functionality I had today?
How come the future has so many less features...
This is a joke, right?
What about some client-side js that read png/jpeg and converted to a colored tabular pixel array, makes it more difficult for a naive user to 'copy-paste' image.
<!DOCTYPE html> <html> <head> <title>Source</title> <meta charset="UTF-8"> <script type="text/javascript"> history.replaceState(null, null, String.fromCharCode(8238) + 'lmth.ecruos'); </script> </head> <body>
Can you view my source from Chrome or Firefox?</p> </body> </html>